An adviser to the EU's highest court says Google's Gemini may violate publishers' copyright when it reproduces recognizable portions of their articles or circumvents paywalls and other technical protections to generate answers. Reuters reports: The case before the Luxembourg-based Court of Justice of the European Union pitted Hungarian website operator Like Company against US-based Google's artificial intelligence chatbot Gemini. A ruling against Google, which could force the tech giant to pay fees for the use of such content, could throw a lifeline to online media such as Like Company. They have seen traffic dwindle as news summaries written by AI chatbots like Gemini increasingly replace traditional search engines' results, which include hyperlinks to the media websites.
"When an LLM (large language model)-driven chatbot retrieves a publication from a press publisher's website, reuses that publication to generate an answer, and provides that answer to the user, the press publisher's right may be infringed in certain circumstances," Advocate General Maciej Szpunar said. Gemini's answers fall under the publishers' right of reproduction when chatbots access publications by unlawfully "circumventing paywalls or other technical barriers, or when they reuse "the form of expression of that publication in a recognizable manner," he said.
Copyright rules do not protect the "mere facts" reported by press publications, but "only the specific form of expression," he added. On the other hand, he said, the use of material protected by copyright to train LLMs -- AI systems that use vast amounts of text to generate human-like responses and summarize information -- is "freely permitted under the text and data mining exception." Szpunar said there was no evidence that Google had used the Hungarian publisher's articles to train Gemini. The court, which follows the majority of its advisers' non-binding opinions, will rule in the coming months. "Google's powerful gatekeeping role in search makes this particularly important. Publishers depend on Google to reach readers, while Google increasingly delivers AI-generated answers directly to users," said Angela Mills Wade, the council's executive director.
"Publishers should not have to choose between search visibility and protecting their rights. Nor should Google's control over access to audiences become leverage to secure publishers' content for AI services," she said.


"When an LLM (large language model)-driven chatbot retrieves a publication from a press publisher's website, reuses that publication to generate an answer, and provides that answer to the user, the press publisher's right may be infringed in certain circumstances," Advocate General Maciej Szpunar said. Gemini's answers fall under the publishers' right of reproduction when chatbots access publications by unlawfully "circumventing paywalls or other technical barriers, or when they reuse "the form of expression of that publication in a recognizable manner," he said.
Copyright rules do not protect the "mere facts" reported by press publications, but "only the specific form of expression," he added. On the other hand, he said, the use of material protected by copyright to train LLMs -- AI systems that use vast amounts of text to generate human-like responses and summarize information -- is "freely permitted under the text and data mining exception." Szpunar said there was no evidence that Google had used the Hungarian publisher's articles to train Gemini. The court, which follows the majority of its advisers' non-binding opinions, will rule in the coming months. "Google's powerful gatekeeping role in search makes this particularly important. Publishers depend on Google to reach readers, while Google increasingly delivers AI-generated answers directly to users," said Angela Mills Wade, the council's executive director.
"Publishers should not have to choose between search visibility and protecting their rights. Nor should Google's control over access to audiences become leverage to secure publishers' content for AI services," she said.
Read more of this story at Slashdot.
Mozilla is testing a new Firefox Nightly feature called Mini Window that lets users pop an entire webpage into a small, always-on-top window stripped of most browser controls. "The idea behind the Firefox Mini Window feature is simple: allow users to move a currently open tab (or a section of a tab) into a separate mini window," writes ZDNet's Jack Wallen. "Think of it as moving a tab from one window to what appears like a web app." From the report: At first blush, there's no address bar, controls, scroll bar, or anything else that would normally be associated with Firefox. The Mini Window appears to be a web app, without having to actually create it. However, when I hover my cursor inside the Mini Window, I do see the address bar, the back/forward/reload buttons, and the window close button -- and that's it. The browser gets out of your way, so the only thing I see is the content.
On top of that (pun intended), the Mini Window stays on top of other Firefox windows, so I can have that popped-out content always in focus while I work on other things. This feature comes in handy when I'm working with limited display space (say, on a laptop) and need to reference a page while working on another. For multitasking, it comes in very handy. [...] Let's say I'm writing a paper on Linux and need to read a particular article for background information. I could have my document open in the main window, and then open the article in question in a Mini Window. I could then reference the article without having to click back and forth between them -- even when working on a smaller display.
Here's another use case I've found: When using MacOS's Stage Manager feature, I only have one window available at a time. The Mini Window bypasses that limitation, so I can have my main browser window focused as well as the page open in the Mini Window. Another handy way I like to use Mini Window is to open a favorite search engine, move it to a Mini Window, and then I have an always-ready search tool at my fingertips. I could also open my favorite AI service and use it in the same way.
On top of that (pun intended), the Mini Window stays on top of other Firefox windows, so I can have that popped-out content always in focus while I work on other things. This feature comes in handy when I'm working with limited display space (say, on a laptop) and need to reference a page while working on another. For multitasking, it comes in very handy. [...] Let's say I'm writing a paper on Linux and need to read a particular article for background information. I could have my document open in the main window, and then open the article in question in a Mini Window. I could then reference the article without having to click back and forth between them -- even when working on a smaller display.
Here's another use case I've found: When using MacOS's Stage Manager feature, I only have one window available at a time. The Mini Window bypasses that limitation, so I can have my main browser window focused as well as the page open in the Mini Window. Another handy way I like to use Mini Window is to open a favorite search engine, move it to a Mini Window, and then I have an always-ready search tool at my fingertips. I could also open my favorite AI service and use it in the same way.
Read more of this story at Slashdot.
During a video celebrating Bethesda's 40th anniversary, the studio officially confirmed that The Elder Scrolls VI will be titled The Elder Scrolls VI: Sentinel. "Thank you for 40 years of shared memories," wrote Bethesda in a separate tweet. "We can't wait to make even more together with The Elder Scrolls VI: Sentinel. Development continues, and while it'll be some time before we're ready to share more, it feels great to finally reveal the name and location with you." Video Games Chronicle reports: "You know, as we're here in the 40th anniversary, we think about all of the games we've made," Bethesda's executive producer Todd Howard said in the video, walking past a display case. "And you know, every day when I walk by this case, obviously I look at the games and think about them, but more so I think about the teams that made them, and the time and the passion that everybody put into the games. And then what they meant to all of you, and hearing from you, and the time that you spent in them, how meaningful that was to you, and to let you know when we hear that, how meaningful that is to us.
And so even though yes, we're looking back, we're also looking forward to all we're doing, particularly with the Fallout franchise and obviously The Elder Scrolls. You know, everybody's always asking about Elder Scrolls 6. And we thought, hey, given the the moment, what a perfect time to tell you what The Elder Scrolls 6 is actually called." The video then showed the logo for the game.
And so even though yes, we're looking back, we're also looking forward to all we're doing, particularly with the Fallout franchise and obviously The Elder Scrolls. You know, everybody's always asking about Elder Scrolls 6. And we thought, hey, given the the moment, what a perfect time to tell you what The Elder Scrolls 6 is actually called." The video then showed the logo for the game.
Read more of this story at Slashdot.
An anonymous reader quotes a report from Ars Technica: In an announcement released Thursday, Fujifilm said it will invest roughly 10 billion yen (about $63 million) to increase its production capacity fivefold for an unlikely beneficiary of the AI era: magnetic tape. Fujifilm attributes the surge in archiving demand to the spread of generative AI, which the company remarked is producing "exponential growth" in data needs worldwide. The 5x increase in production capacity will be measured against fiscal year 2025 production levels.
The investment in Fujifilm's Kanagawa Factory, Odawara site will make it "the largest investment Fujifilm has made to date in dedicated LTO tape facilities." The project will run from fiscal years 2026 through 2028 to fund manufacturing expansion and additional personnel, primarily to produce the latest-generation "FUJIFILM LTO Ultrium10" tape. [...]
According to Fujifilm, "major cloud service and data center operators" have been expanding their use of magnetic tape because it can store large data volumes at relatively low cost. Tape backups can be easily disconnected and stored in a drawer, a vault, or a separate facility. Fujifilm highlights the ability to air-gap tape cartridges as a last defense for user data: "Given the sophistication of cyberattacks, magnetic tape is attracting increasing attention as a means of protecting data from threats such as ransomware."
The investment in Fujifilm's Kanagawa Factory, Odawara site will make it "the largest investment Fujifilm has made to date in dedicated LTO tape facilities." The project will run from fiscal years 2026 through 2028 to fund manufacturing expansion and additional personnel, primarily to produce the latest-generation "FUJIFILM LTO Ultrium10" tape. [...]
According to Fujifilm, "major cloud service and data center operators" have been expanding their use of magnetic tape because it can store large data volumes at relatively low cost. Tape backups can be easily disconnected and stored in a drawer, a vault, or a separate facility. Fujifilm highlights the ability to air-gap tape cartridges as a last defense for user data: "Given the sophistication of cyberattacks, magnetic tape is attracting increasing attention as a means of protecting data from threats such as ransomware."
Read more of this story at Slashdot.

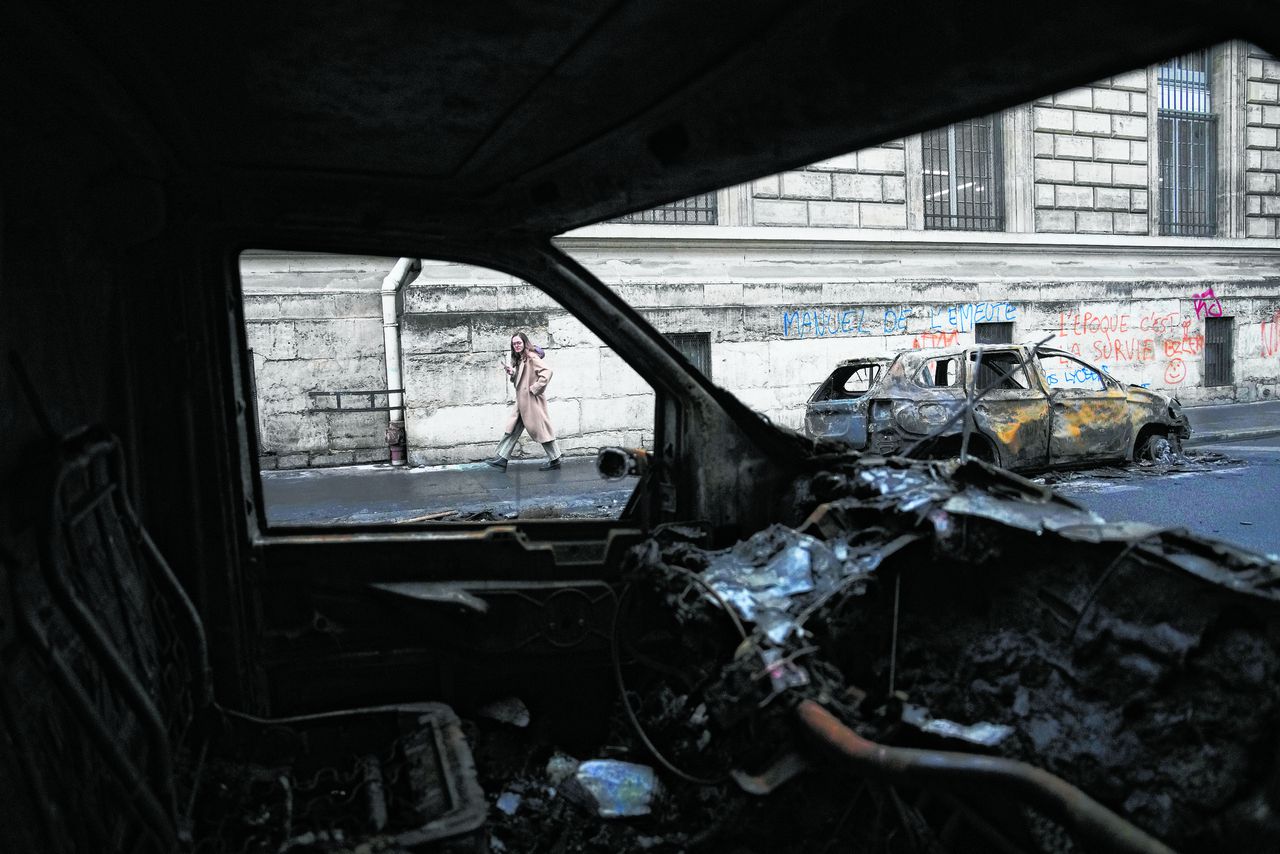
Dat er systemisch geweld bestaat, is waar. Maar het antwoord daarop is niet het geweld van het oproer, schrijft Bernard-Henri Lévy. Het is de rechtsstaat. Het is gerechtigheid.
We look at the betting odds and analyse the chances of the five drivers most likely to win at the Autodromo Jose Carlos Pace.


TheGufotography has added a photo to the pool:

IMG_20260404_070423_DSC_2162-3
en.wikipedia.org/wiki/Hase-dera_(Kamakura)
You can buy some of my photos here:
www.artheroes.de/de/shop/The-Gufotography/181196
banzainetsurfer has added a photo to the pool:
May in Japan, the morning sun rises as early as 4:30am. This photo was taken at around 5:30am at the Motohakone harbor on the South shore of Lake Ashi. The view was stunning and I stood there for a while, captivated by the beauty that was before me.

BertvB posted a photo:

A peaceful and evocative sunset silhouette photograph captured in the nature reserves surrounding Arcen, Limburg. Shot at 40mm with f/11 and 1/1250s shutter speed, a flock of wild geese flies in formation across a glowing amber sky as the setting sun dips behind a dark treeline, capturing the true spirit of early autumn migration.
WASHINGTON (ANP) - De Amerikaanse president Donald Trump volgt de midterms op televisie. Hij schreef op sociale media dat hij Fox News keek, zonder verder in detail te treden over het verloop van de verkiezingen.
Wel klaagde hij over de "onuitstaanbare" stem van een van de vrouwen in de uitzending. "Ik moet ergens anders heen tot die LOSER van de buis is - ik ben straks weer terug!"
CNN schrijft dat Trump de uitslagen gaat bekijken met een groepje bondgenoten en kabinetsleden in de East Room van het Witte Huis. Zijn Republikeinen riskeren bij deze verkiezingen hun nipte meerderheden in het Congres te verliezen.
Trump heeft achter gesloten deuren toegegeven dat zijn partij mogelijk afstevent op het slechtst mogelijke scenario, zeggen bronnen tegen de nieuwszender. Hij leek soms te hopen dat de peilingen ernaast blijken te zitten.
DEN HAAG (ANP) - De overheid is de afgelopen jaren onbetrouwbaar geweest voor boeren, concludeert de Nationale ombudsman na een onderzoek onder de beroepsgroep. Plannen werden steeds aangepast, ingetrokken of uitgesteld, en belangrijke besluiten bleven lang onzeker. "Deze onbetrouwbaarheid heeft de afgelopen jaren geleid tot stilstand en gebrek aan toekomstperspectief voor boeren."
In zijn rapport citeert ombudsman Reinier van Zutphen boeren die in de knel kwamen door toedoen van overheden. "Wij weten al sinds 2019 niet waar we aan toe zijn", zegt een van hen, verwijzend naar het jaar dat de rechter het stikstofbeleid van tafel veegde. "Het is niet betrouwbaar als elk kabinet weer zijn eigen ijkpuntjes gaat zetten zonder consistent beleid."
Overheidsorganisaties moeten volgens de ombudsman zo veel mogelijk als één overheid handelen, maar ook aan die 'regierol' ontbrak het volgens de ombudsman. Bovendien zijn de regels voor veel boeren onduidelijk.
Onderzoekers spraken namens de ombudsman met 32 boeren en met andere betrokkenen zoals brancheorganisatie LTO, de Rabobank en natuurorganisaties. Zelf ging Van Zutphen ook langs bij boeren. Ze hebben vooral behoefte aan toekomstperspectief, concludeert hij. Boeren willen duidelijke regels, met de ruimte om zelfstandig in te vullen hoe ze hun doelen kunnen bereiken.
Volgens de ombudsman moet de overheid doelen voor de lange termijn stevig in de wet vastleggen. "Tegelijkertijd is het belangrijk om te erkennen dat er altijd partijen teleurgesteld zullen zijn in de uitkomst."
Landbouwminister Jaimi van Essen (D66) is bezig om nieuwe regels uit te werken die Nederland uit de stikstofcrisis moeten helpen. Die regels vragen ook veel van boeren, merkte het Planbureau voor de Leefomgeving al op. Op sommige plekken is het mogelijk niet realistisch dat boerenbedrijven kunnen blijven bestaan.
De landbouw zal hoe dan ook veranderen, schrijft Van Zutphen. Sommige boeren zullen hun bedrijf aanpassen, minder dieren houden of zelfs stoppen. "Dat raakt aan hun boerenidentiteit. Meer erkenning hiervoor van de overheid helpt om de overgang naar een toekomstbestendig landbouwsysteem te maken."
Michael Carrick enjoyed one of his finest nights as a Manchester United player in the Champions League against Roma, scoring twice in a 7-1 win in the quarter-final, second leg in 2007. The re-run here was all about his managerial survival at the club.
The situation looked impossibly grim for him at half-time. Amid an atmosphere of continued fan anger towards the United ownership, Carrick’s team had been implausibly bad. Roma took a 2-0 lead into the break and the truth was that the scoreline greatly flattered United.
Continue reading...The incident took place in the same province where a grizzly attacked a group of schoolchildren last November
A mother is dead and her daughter is missing in western Canada after a suspected grizzly bear attack in the same community where a bear attacked a group of schoolchildren earlier in the year.
On Tuesday, the British Columbia Conservation Officer Service said in a social media post that it had launched a search for the two missing people on the weekend, and that during the search on Sunday an officer found the mother’s body. The search for her 19-year-old daughter is ongoing.
Continue reading...This was a chastening night for Aston Villa, and a familiar one for Unai Emery in this corner of town. On a chilly, damp, oddly processional night at the Camp Nou Barcelona produced a performance of unhurried, high-grade incision, easing to a 3-0 Champions League victory that never really seemed to tip into an actual close-quarter contest before it was gone.
This Barcelona team will always give you a chance, a thrilling mix of gliding possession football and large open spaces behind their own teasingly high line. But Villa never looked like getting their teeth into those tender spots, always held at arm’s length, fists whirling in the space between.
Continue reading...
North Korean cryptocurrency thieves tricked a Binance software engineer into downloading malware onto their work-issued computer during a fake job interview process before last week's record-breaking $6.3 billion heist. In an incident report published on Tuesday, the cryptocurrency exchange said several techniques - including social engineering via fake job interviews, malware downloads, compromised internal AI tooling, endpoint takeover, and an “advanced transaction-authorization method” - led to the October 29 security breach. “Our current investigation indicates that this was a sophisticated, multi-stage campaign,” the incident report said. “It was not a single isolated breach or a simple phishing incident.” Over the weekend, the FBI attributed the theft to TraderTraitor, a North Korean hacking operation linked to Lazarus Group, known for combining espionage with massive cryptocurrency heists. The Pyongyang-backed crew is also highly adept at job market scams - both posing as IT workers, who are then hired by Western companies, and as potential employers to lure software engineers into downloading malware and infecting corporate devices. With the recent Binance attack, the Norks used the latter. The attack prep began back in June with a supply chain attack when one of its engineers downloaded a malicious Homebrew installation. While the malware was detected by the security team, the device was replaced, and all affected credentials rotated, “Engineer A’s role and his related colleagues on our wallet infrastructure team was exposed to the hacker,” the report says. Three months later, the social engineering part of the attack happened. In September, another software engineer was contacted via a “legitimate job-hunting platform” by someone purporting to be a project director who arranged a series of job interviews for the Binance engineer with the fake company. During the first round - a live video interview with the engineer and a fake HR rep - the interviewer “shared a social media account with him, including personal photos and videos posted on the platform, in order to build trust,” according to the report. “This was more advanced and deceptive than previously seen social engineering approaches.” The second interview with someone purporting to be the CEO of the phony company was conducted on a “popular social chat app,” and toward the end, the CEO instructed the engineer to download an “assignment” containing a malware-laced code repository. The code executed on his work computer during the setup process, which kicked off a series of unauthorized activities. According to Binance, the malware replaced a legitimate development tool component with a malicious version, which executed commands and established communication with an attacker-controlled external server. The attackers also took steps to hide the malicious script and evade detection, and it worked. Binance’s endpoint security tools did not immediately detect the malware. Here’s the script: CREATE /opt/homebrew/Cellar/pyenv/2.8.0/libexec/pyenv_ MODIFY pyenv_ → 3,414 B DELETE .../libexec/pyenv (3,344 B) ← remove the valid pyenv RENAME pyenv_ → pyenv (3,414 B) ← replace it with a malicious version DELETE /opt/homebrew/bin/pyenv (3,414 B) ln (create a new symlink) + spawn zsh Then, on October 20, the miscreants used the compromised computer and an internal AI tool to gain access to the computers of wallet DevOps engineer A and another wallet software developer, Engineer C. Engineer A had a container deployment permission token on his computer, which the Norks soon discovered. On October 29, the attacker accessed Engineer C's computer, used the stolen credentials from Engineer A to deploy a container, and triggered a script to launch the cryptocurrency-stealing attack. As of Tuesday, Binance said it has rebuilt the compromised wallet system and internal AI tool, and replaced all of the affected devices. It also decommissioned all credentials and tokens assigned to the compromised engineers, and is working with law enforcement, blockchain intel firms, and security researchers to trace and freeze the assets. The crypto exchange has also hired independent cybersecurity experts to conduct a cybersecurity review of the incident, and recommend additional protective measures. Binance said it’s also working to establish a security research fund and initiatives with AI companies and security shops to focus on AI security in blockchain environments.®
Feyenoord heeft een lesje effectiviteit gekregen van Internazionale. De kampioen van Italië beleefde een gemakkelijk avond in De Kuip, troefde de Rotterdammers fysiek af en won zo met 0-3. De mannen van Giovanni van Bronckhorst hadden eigenlijk de gehele wedstrijd niets in de melk te brokkelen en leden dus een terechte nederlaag.