
Three hours and 15 minutes into the 4 hour long documentary Musk, a video game avatar of the titular billionaire picks up a chainsaw off the Resolute Desk in the Oval Office. Shot like a first-person shooter, the audience watches as Musk wields the chainsaw to destroy various government buildings. Walking through a farm, Musk aims the chainsaw at grain silos labeled ‘USDA’ and lightning arcs from its spinning blades. The silo explodes and cows moo in distress.
In my experience, the purpose of a video game chainsaw is to viscerally rend through objects. I have never seen one shoot lightning. It’s a small detail that speaks to my overall problem with Alex Gibney’s Musk: it’s cringe.
Elon Musk is one of the most powerful men alive on the planet and Gibney’s Musk does a decent job of giving the overall arc of the man’s many faults. The director takes us from Zip2 to DOGE while highlighting the billionaire’s pathology, and it hits more than it misses.
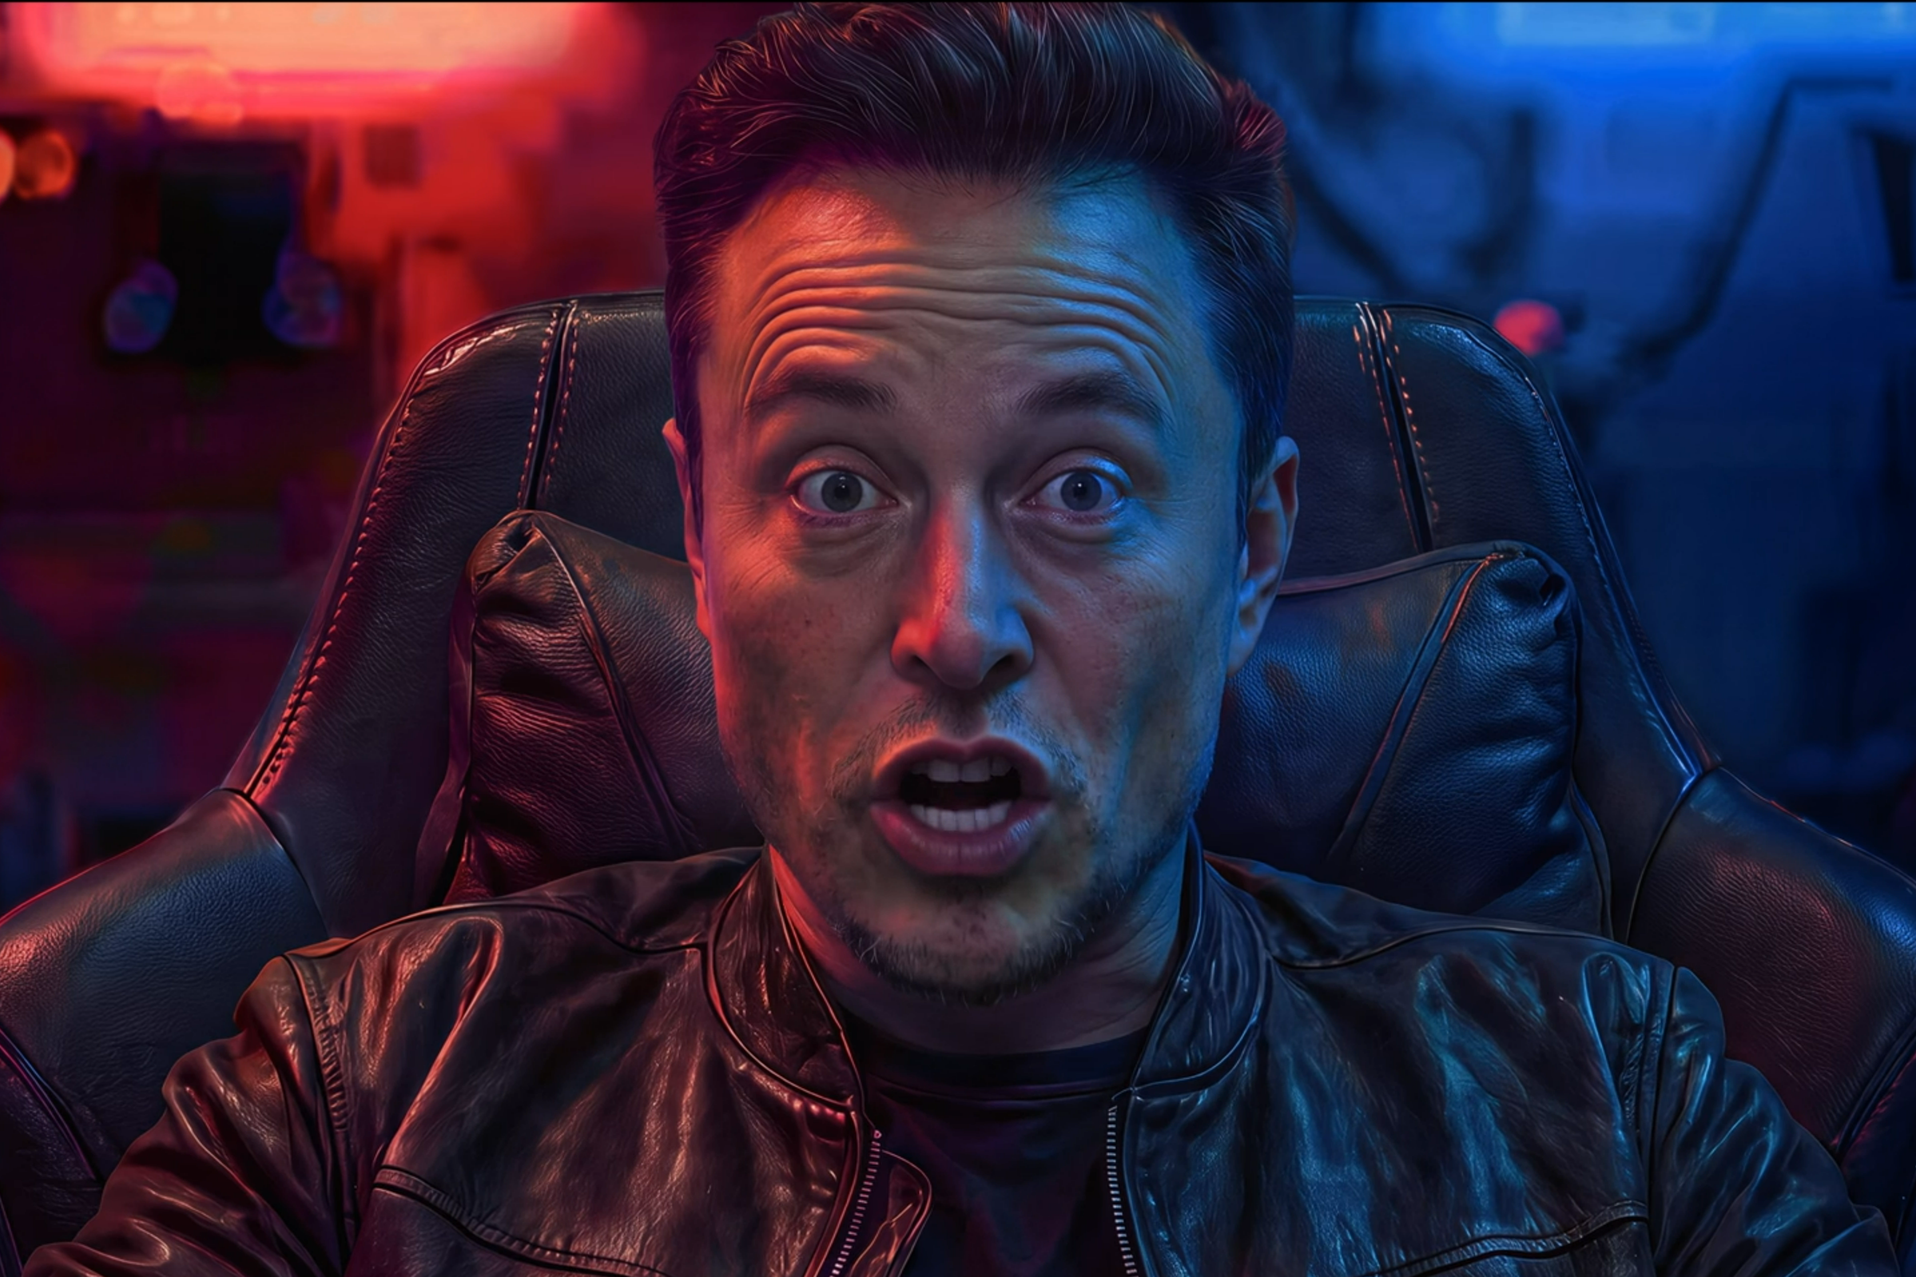
Musk is a good overview of the general arc of Elon Musk, the man. But there have been other Elon Musk documentaries told in much the same way (we made one at VICE several years ago, that is similar in tone and vibe). And so, at a laborious four hours long, it’s not clear who Musk is for, and the weird video game interstitials and ghoulish AI avatar of Musk himself are genuinely distracting. Musk would not talk to Gibney so the director generated an AI avatar of the billionaire to act as a stand-in. Throughout Musk, this hyperreal grotesque lends color commentary as if the billionaire is actually in the room.
The director cites Musk’s oft-stated belief that we’re living in a simulation as a justification for the AI Musk. “He believed it likely that an artificial intelligence of the future had exfiltrated all knowledge and life experiences from planet Earth and was now running an ancestor simulation in which our past lives had become the training data for a kind of sim world,” Gibney says as the AI musk coalesces before the audience. “In honor of that idea, we decided to edit together recordings of his actual words to create a simulated interview at the heart of a kind of documentary video game.
I understand what Musk is going for here, and it’s funny to watch Musk’s likeness and spirit rendered through the lens of AI and video games. But, on the whole, the AI Elon doesn’t work. Its head is too big, its features are exaggerated, and it sits in a stereotypical gamer chair while bathed in the kind of blue and red lighting popular on Twitch streams ten years ago. The things the bot says aren’t fabricated, they’re direct quotes from the man himself, though some are lightly edited.
In every instance, the quotes are more interesting and more informative when shown in their actual context, in the video interviews the real Musk gave.
“I lost my son, essentially. They call it dead naming because, uh, your son is dead. So my son is dead. Killed by the woke mind virus,” AI Elon says in the film.
This was part of an interview with Jordan Peterson for The Daily Wire. Learning that enriches the quote. There’s crosstalk with Peterson. You see Musk’s real face when he talks about Vivian. It is a real video interview that you can actually watch. There is no need to use an AI avatar to do this.
In another clip the AI Elon explains the Twitter Files. “On Twitter, there was a lot of censorship. We sort of uncovered a lot of that with the Twitter Files,” it says. “Free speech is meaningless unless you allow people you don’t like to say things you don’t like.” The real clip comes from a Real Time With Bill Maher interview.
There’s a lot of this in the film. “What is the most entertaining outcome for the election? That’s probably what’s going to happen,” the Musk bot grins evilly while paraphrasing a Musk catchphrase. Musk talking to Kara Swisher, Musk at a Vanity Fair conference, Musk delivering missives at CPAC, and Musk speaking to Joe Rogan are all condensed into an AI approximation of the real person. In every instance, the original quote in its context is more powerful and more illuminating about its subject.
And then there’s the video game sequences. Musk uses Elon’s obsession with video games as an extended visual metaphor throughout. Under a pink filter that looks like it’s designed to capitalize on the release of Grand Theft Auto VI, Musk picks different classes — shifting from gamer to founder to Kublai Khan. He drives a sports car along a digital track while Tesla’s stock pieces rises like a video game score, and uses Iron Man-style gloves to vaporize Twitter employees.
If the man believes we’re living in a video game then this is what it might look like. His DOGE -fueled chainsaw rampage across DC ends with him dropping a nuke on the National Nuclear Safety Administration and his inauguration Nazi salute turned into a pixel-art version score screen.
Again, this is a four-hour long documentary. It has an intermission, even when you stream it. The video game sequences and AI Elon feel like a baby boomer grasping the aesthetics of a younger generation and misusing them. It’s Steve Buscemi holding a skateboard in the hallway of a high school asking how his fellow kids are doing. It detracts from the overall message here, which is that Musk is a destructive force in our businesses and politics.
“Bederf wat je hebt niet door te verlangen naar wat je niet hebt.” Dat schreef de Griekse filosoof Epicurus ruim tweeduizend jaar geleden over het topic dankbaarheid. "Ook dat wat je nu hebt, wilde je ooit graag", voegde hij eraan toe.
Dankbaarheid betekent niet dat je doet alsof alles prima gaat, schrijft het Engelse filosofieplatform Philosophy Basics. Het gaat erom dat je duidelijk op je netvlies hebt wat al goed is. Filosofen en psychologen hebben acht oefeningen bedacht om dit gevoel op te roepen.
Kijk eerst naar wat je al hebt
Je baan, je huis, die vriend die je nu vanzelfsprekend vindt: ooit hoopte je erop zonder te weten of het zou lukken. Kies één gewoon onderdeel van je leven en vraag je af of je er ooit naar verlangde. Vaak is het antwoord ja.
De Romeinse keizer Marcus Aurelius ging een stap verder. Denk aan het beste wat je hebt, schreef hij in zijn Overpeinzingen, “en bedenk hoe vurig je ernaar zou zoeken als je het niet had”. Neem iets kleins, zoals warm water uit de kraan of een fijne stoel. Hoeveel zou je ervoor overhebben als het er niet was?
Hij waarschuwde er wel bij: hecht er niet zo aan dat het je van streek maakt als je het kwijtraakt. Je moet het beter zien, niet steviger vasthouden.
Dank heeft een naam en een stem
Het hele eerste boek van de Overpeinzingen is een lijst van schulden. Marcus noemt zijn grootvader, vader en moeder en zegt wat hij van elk leerde. Doe hetzelfde in een paar regels: welke leraar, oma, oud-baas of vriend leerde je iets wat je nog steeds gebruikt? Dankbaarheid voelt echter met een naam erbij.
Zeg het daarna ook. Seneca schreef er een heel boek over, Over weldaden.
Wie een weldaad met dankbaarheid ontvangt, betaalt de eerste termijn al terug.
De collega die voor je inviel, de buurman die je pakketje aannam: stuur deze week één kort bericht en zeg precies wat het voor je betekende. Seneca vond dat je je dank niet alleen moest laten horen aan de gever, “maar overal”.
Een vroeg boeddhistisch geschrift noemt twee soorten mensen zeldzaam: wie als eerste iets goeds doet en wie dankbaar is en iets terug wil doen. Kun je iemand niet terugbetalen, omdat hij er niet meer is of de hulp te groot was, help dan iemand die nu in dezelfde situatie zit.
Een dagboek helpt, maar niet voor alles
Het bekendste onderzoek komt van de Amerikaanse psychologen Robert Emmons en Michael McCullough, in 2003 gepubliceerd. Proefpersonen hielden wekelijks of dagelijks bij waar ze dankbaar voor waren. Andere groepen schreven ergernissen, neutrale gebeurtenissen of vergelijkingen met anderen op.
In cijfers
- 3 experimenten met studenten en mensen met een spierziekte, in 2003
- 10 weken duurde de wekelijkse versie
- dagelijks: de duidelijkste verbetering van de stemming
- wekelijks: geen betere stemming, wel een positiever oordeel over het leven als geheel
De dankbare groepen voelden zich beter “op meerdere, maar niet alle” metingen, schreven de onderzoekers. Een behandeling voor een ziekte is het dus niet. Wil je beginnen, schrijf dan op zondagavond drie specifieke dingen op uit de afgelopen dagen: het gesprek waar je om moest lachen, de maaltijd die iemand voor je kookte. Niet elke week “mijn gezin”.
Genoeg is ook een antwoord
“Wie tevreden is met zijn lot, is rijk”, staat in de Daodejing van de Chinese denker Laozi. Dat betekent niet dat je geen doelen meer hebt of onrecht accepteert. Vraag je af op welk terrein meer weinig verschil zou maken en waar je kunt stoppen met jagen.
Je hoeft ook niet alles op te schrijven. De eerste slok koffie, een liedje dat je vergeten was, de kleine routines die je gelukkiger maken: sta er vandaag een paar seconden bij stil.
Dankbaar zijn is geen zwijgplicht
Dankbaarheid is geen reden om echte problemen te negeren of oneerlijke behandeling te slikken. Je kunt blij zijn met je baan en toch om opslag vragen. Je kunt van je familie houden en ze toch vermoeiend vinden.
Iemand die het zwaar heeft voorhouden dat hij “dankbaar moet zijn”, helpt zelden, schrijft Philosophy Basics. Dankbaarheid groeit als je haar zelf opmerkt, niet als een ander haar oplegt. Ook dat hoort bij gelukkig ouder worden: zien wat goed is, zonder te ontkennen wat moeilijk is.
Zo bedoelde Epicurus het ook. Wat je nu hebt, was ooit iets waar je op hoopte.
Meer weten?
Bronnen: Philosophy Basics, Journal of Personality and Social Psychology
NEW YORK (ANP) - De Nederlandse Bregje de Best wordt de nieuwe financieel directeur van de grote Amerikaanse bank JPMorgan Chase. Zij neemt die rol op zich na de publicatie van de cijfers over het eerste kwartaal van volgend jaar.
JPMorgan Chase is de grootste bank van de Verenigde Staten, met bezittingen van 5,1 biljoen dollar onder beheer. De Best neemt de functie van Chief Financial Officer (CFO) over van Jeremy Barnum, die vicevoorzitter wordt. De Best is nu nog financieel directeur van de tak Commercial & Investment Bank (CIB) van JPMorgan Chase.
Topman Jamie Dimon van JPMorgan Chase zegt dat De Best een "buitengewoon" leider is met grote ervaring. Ze werkt al ruim twintig jaar bij de bank en heeft gestudeerd aan de Erasmus Universiteit in Rotterdam.


Mr Mikage (ミスター御影) posted a photo:

Overwrought and boring, this nadir of a prequel to the Games’ death match saga is nothing but a cash grab for an exhausted franchise
Here is yet another iteration of the utterly exhausted, unbearably extended and now surreally boring Hunger Games franchise, based on the YA bestsellers by Suzanne Collins. This one has another of the series’ convoluted faux-mythic subtitles: Sunrise on the Reaping. What, “harvest dawn” not old-timey enough?
Well, “reaping” in fact refers to an annual process by which ordinary smudgy faced, raggedy clothed people are chosen at random for compulsory participation in this futurist dystopia’s brutal, televised survival contest to the death: a bread-and-circuses nightmare with which the rulers keep the populace in a cowed and pacified state. In this Darwinian process, competitors strategically team up with (and then betray) some players against others in the short term, to stay in the game.
Continue reading...International investigation using trove of leaked internal data allegedly shows German bank overlooked compliance concerns to safeguard profits
Deutsche Bank reportedly dismissed warnings about its dealings with risky clients, including high-profile Russian oligarchs, to protect profits, the findings of an investigation into a trove of leaked bank documents indicate.
A leak of 15m internal files is reported to show that the troubled German bank repeatedly ignored concerns by its compliance officers about its risk-taking, despite having already been caught being used to launder billions of dollars for Russian criminals, spies and oligarchs between 2010 and 2015.
Continue reading...I am at Cop 31 – concerned about the crisis around the world, but mindful that voters want jobs, warmer homes and cheaper prices
Miatta Fahnbulleh is the UK secretary of state for energy security and net zero
In this cold weather, it is easy to forget that Britain has just been through its hottest summer on record, part of our new reality as the climate crisis reaches our doorstep. For millions around the world, the consequences have already been more devastating for the communities that did the least to cause this crisis.
That is the backdrop to Cop31 in Antalya, Turkey, where I arrive on Tuesday as the UK’s chief negotiator. As I have prepared for these negotiations, I’ve been reflecting on the gap between the science and the political debate in Britain. Early predictions by the Met Office indicate that 2027 will surpass 2024 as the hottest year on record globally as El Niño rips through the Pacific. This is a sobering reality. And yet, the Conservatives and Reform UK want to bury their heads in the sand and break the consensus on delivering net zero. But we know sustained climate action can work.
Continue reading...
Some of the world's most popular websites spent Monday serving malware to visitors after crooks found a way into a piece of software used to A/B test web pages. Scott Helme, a security researcher at Report URI, identified malicious JavaScript being served by websites belonging to at least 178 organizations, including the BBC, CNN, Zoom, IKEA, Salesforce, HSB, and TalkTalk. All have one thing in common: they use Optimizely's Web Experimentation software. Optimizely allows businesses to tweak the content and layout of their websites without changing the underlying site code. Unfortunately, someone other than its paying customers figured out how to do just that. The attackers abused a feature that allows Optimizely customers to add their own JavaScript to web pages. The malicious code was distributed alongside the legitimate stuff from Optimizely's own content delivery network, giving customers little reason to suspect anything was amiss. Optimizely has since confirmed that the criminals exploited a vulnerability, dubbed "OPTIMJACK" by researchers, in the sign-up process for its experimentation software, adding that it had patched the hole, removed the offending code, revoked tokens, and notified affected customers. "Earlier today, Optimizely identified a security incident in which an unauthorized party exploited a vulnerability in Experimentation and used it to add malicious JavaScript to some customer projects,” the company said. “We've fixed the vulnerability and removed the injected code from affected projects. We've also taken steps to secure affected user accounts and put additional protections in place to prevent unauthorized code from being delivered." Of the 1,611 Optimizely scripts examined by Helme and his team, 188 contained malicious code, including those used by Optimizely's own website and login portal. Given the researchers examined only a subset of the scripts, the number of affected businesses could be higher. The malware underwent several revisions over the course of Monday, with cryptocurrency theft among the crooks' money-making schemes. Copy a wallet address to your clipboard and the malware could quietly swap it out for one belonging to the attackers, diverting any funds sent to that address. A card skimmer added later in the day grabbed card numbers, expiration dates, and security codes from payment forms. However, according to a separate analysis by StepSecurity, card details entered into an iframe hosted by a third-party payment processor were beyond the malware's reach. There was something nasty in store for Apple users, too. The malware attempted to deploy the Coruna and DarkSword exploit kits on iPhones and iPads running older versions of iOS, though how many devices the criminals managed to compromise is anyone's guess. Helme traced roughly $7,000 in cryptocurrency to the attackers' wallets on Monday, though there’s no telling how much more the crooks stand to make from stolen payment card details. By 2152 UTC on Monday, TalkTalk was the only organization remaining on Report URI's list whose Optimizely code still contained the malware. All that money spent securing corporate websites, and the attackers found their way onto them via a bit of software the marketing department uses to tinker with web pages. ®
A Dutch cybersecurity researcher claims he found six zero-days in Danfoss refrigeration controller firmware in under an hour, then delivered a withering assessment of the vendor's defenses against memory corruption. The Centre for Cybersecurity Belgium (CCB) warns that the flaws could let attackers take control without credentials, potentially retain access after resets, or disable controllers altogether. Carlo Meijer of cyber consultancy Midnight Blue examined the latest AK-SM800A firmware, version 5.3.2, manually – no AI required. He said that he went looking in random places where strcpy() is invoked, given the vendor's "extremely liberal use" of the function (which doesn't check whether the destination buffer is large enough), and swiftly found five cases in which he said he could trigger a segfault with a one-line cURL command. "Of course, remotely triggering a crash is bad in itself, but being able to leverage the buffer overflow to obtain remote code execution is much worse," he wrote. Meijer added: "Any reasonably experienced exploit developer will agree exploiting straightforward stack-based buffer overflows on ARM Linux without exploit mitigations is very straightforward. And if they don't, there's probably a frontier or open-weight model out there willing to help them agree." He noted that before achieving RCE, an attacker would need to overcome the limitation of strcpy() where it stops copying bytes after hitting a null byte, but said "it's not exactly rocket surgery." He went on to claim: "Also, the exploited application runs as root (because of course it does)." Later firmware adds "session control," an authentication mechanism whose strict setting blocks unauthenticated access to most web interfaces. But Meijer found a memory corruption flaw in that protective layer too. He described the final zero-day as a "trivial" pre-auth memory corruption bug which again starts with a segfault but can be wangled into an RCE "with some additional effort." Meijer also considered whether attackers could maintain access after a reset, as seen with implants such as Saltwater and Firestarter. He considered this feasible because the controllers do not use their processor's secure boot features. "In such a scenario, an attacker could either retain remote access or leave a time-triggered payload for a 2nd (or 3rd...) strike – increasing damage by spoiling new batches of food," said Meijer. "Alternatively, attackers could simply wipe flash memory and/or push a malformed firmware update to brick the controllers and render them permanently inoperable – requiring costly and time-consuming replacement similar to the TTPs deployed during the December 2025 attack on the Polish electric grid." Meijer's priority for operators was to remove the controllers' direct internet exposure, rather than spend scarce resources on piecemeal patching. He said the vendor's advice following the attacks on European supermarkets and blood banks in recent weeks – rotating creds, applying patches, enabling strict session control – was insufficient given the flaws in the controllers' codebase. "This is insufficient and asset owners need to remove internet exposure as soon as possible," said Meijer. "We recommend against allocating scarce security resources to patching efforts and instead focus on reducing exposure." The CCB likewise urged operators to remove direct internet exposure immediately, but also recommended applying patches when they become available. Beyond the liberal use of strcpy(), Meijer criticized the absence of standard exploit mitigations, including stack canaries and position-independent executables. "These mechanisms have been staples of memory corruption defenses for decades and enabling these features... requires no engineering work at all," he said. "It is simply a matter of setting the right compiler flag. Enabling these features became the default in Ubuntu 17.10 and there is simply no excuse for a network-facing application that was last updated a few months ago to not have them enabled." The Register asked Danfoss to respond to the findings, but it did not reply. Danfoss has consistently blanked our requests for information since being implicated in at least some of the attacks that affected European supermarkets recently, alongside rival controller vendors Copeland and Dixell. It also did not respond when we asked about its involvement in the attacks on US commissary appliances over the summer, after some alleged that its controllers were targeted. ®

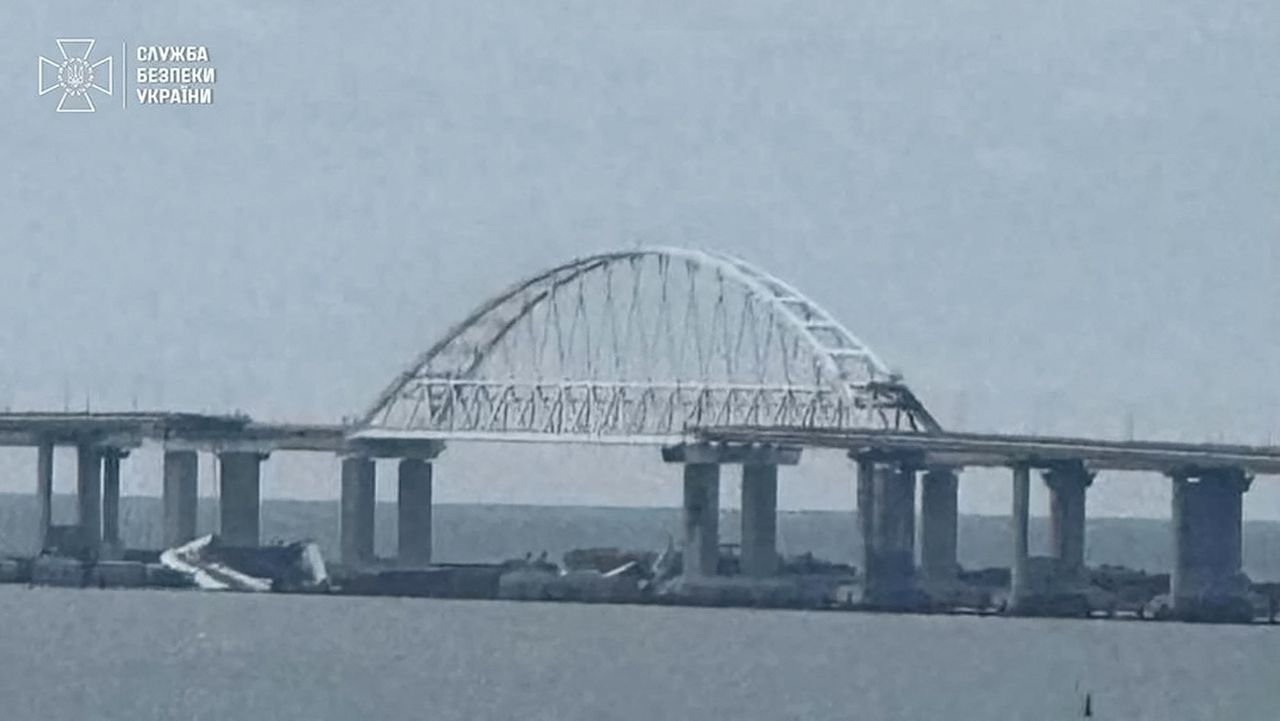
Met elf verschillende wapensystemen viel Oekraïne de Kertsjbrug naar de Krim aan. De autoweg is deels ingestort. De logistieke en symbolische verkeersader was een topdoelwit voor Kyiv. De aanval slaagde mede met gebruik van een Nederlands wapen.
The chocolate brand is one of the most famous confectionery items produced in Russia.


