
Bij een ernstig ongeluk met een Nederlandse bus van touroperator Oad zijn donderdagavond 'meerdere doden' gevallen, zo meldt de Zwitserse krant Blick. Ook de Zwitserse politie maakt melding van 'meerdere doden', alsook van meerdere gewonden. Het ongeval met de touringcar vond plaats op de weg tussen Zernez en Susch, in het kanton Graubünden. Volgens de eerste berichten waren er 48 mensen aan boord van de bus. Er is een grote groep hulpverleners ter plaatse, waaronder VIJF (!) traumahelikopters. Zo meer...
Update 20:59 - Het ging om een bus van touringcarbedrijf Hartemink uit Eibergen. De bus was op reis door Oostenrijk, maar er werd een dagexcursie naar Zwitserland gedaan
Veteran Frenchman bowed out in New York but the clash of two black players in the last four of the men’s singles is testament to his effect
The early days of this year’s US Open can be told in a series of farewells to competitors who plan to end their careers this year. The most moving of them all came in the form of Gaël Monfils’s grand departure inside Louis Armstrong Stadium against the wildly talented 20-year-old Learner Tien. Tien was competing in front of his home crowd, one of the Americans capable of a deep run, but for much of his straight-sets defeat the Frenchman had the American crowd in the palm of his hands.
Beyond the massive popularity he has garnered among tennis fans, one of the most striking parts of Monfils’s long farewell was seeing how highly nearly all of his fellow professionals, particularly his fellow black players, regard him. Frances Tiafoe says he spent his youth looking up to Monfils. Arthur Fils considers Monfils his older brother. Naomi Osaka’s nickname for Monfils, one of her idols, is simply “the Goat”. They all hold Monfils in such great esteem, and for good reason.
Continue reading...⚽️ Champions League updates from the 8pm BST kick-off
⚽️ Live scoreboard | Read Football Daily | And mail Daniel
It’s also worth noting that Patrick Dorgu starts at left-back tonight, for the first time under Carrick. Bought for Ruben Amorim, really he’s a specialist wing-back – not a defender because his awareness isn’t great, nor his ability to pass the ball out from the back, nor a winger because he lacks finesse and one-on-one ability – he starts at the back tonight mainly because Shaw is rested and there’s no better option. But if he’s to have a future as a starter, it feels much more likely it’ll be at the back than in attack – though, as we’ve seen he’s got a worldie in him.
Thinking more about that United defence, this is a big evening for Leny Yoro. He was pretty good in his first season at Old Trafford, but didn’t get to play much last; ultimately, Carrick couldn’t afford to risk him because he had a formula that worked – Maguire and Martinez, plus fast counters – with points to win and a job to secure.
Continue reading...Veterans recall chaos and confusion as the attacks unfolded – followed by a ‘war on terror’ that left agency with a tarnished reputation
A generation of spies had lost an enemy but not yet found a role. Then came 9/11.
A decade after the dissolution of the Soviet Union, al-Qaida’s devastating attacks on New York and Washington on 11 September 2001 announced to the Central Intelligence Agency (CIA) that the long era of battling communism, for which it had been founded, was officially at an end.
Continue reading...SUSCH (ANP) - Een bus van reisorganisatie Oad met 48 Nederlanders aan boord heeft een ongeluk gehad in Zwitserland. Dat meldt een woordvoerder van reiskoepel ANVR die zegt te spreken namens Oad. Volgens de Zwitserse politie zijn bij dat ongeluk meerdere doden en gewonden gevallen. Meer details zijn nog niet bekend.
De woordvoerder van ANVR zegt dat Oad "ontzettend aangedaan" is door het ongeval.
CALGARY (ANP/AFP/RTR) - Canada heeft honderden miljoenen Canadese dollars aan steun toegezegd voor de Oekraïense luchtverdediging en energie-infrastructuur. Dat kondigde de Canadese premier Mark Carney aan tijdens een bezoek van de Oekraïense president Volodymyr Zelensky aan Canada.
Canada gaat voor 350 miljoen Canadese dollar (218 miljoen euro) onderscheppingsmaterieel leveren, zei Carney. Daarnaast voorziet Canada Kyiv van 450 miljoen Canadese dollar (280 miljoen euro) aan kredietgaranties voor reparaties aan de veelgetroffen energie-infrastructuur en om ziekenhuizen van energie te voorzien.
Carney zei verder dat zijn land ook de droneproductie zal opvoeren in de komende twee jaar. Een derde van de productie moet naar Oekraïne gaan.
Oekraïne heeft sinds het begin van de oorlog in 2022 al voor miljarden steun ontvangen van Canada.
Zelf smoothies maken van fruit, groente en een schep yoghurt klinkt als het braafste tussendoortje van de dag. Toch duikt telkens hetzelfde verwijt op: de blender zou de vezels stukslaan, waardoor er van al dat gezonde alleen zoetigheid overblijft. Dat verwijt is grotendeels onterecht. Het werkelijke bezwaar staat gewoon in je glas — en het heeft niets met kapotte vezels te maken.
De blender vermaalt minder dan je denkt
Wie hele stukken fruit en groente pureert, houdt de vezels in het glas. Laboratoriumonderzoek aan gepureerd fruit vond de vezelrijke celstructuren nog terug ná een nagebootste spijsvertering. Blenden breekt de vezels wel in kleinere stukjes, maar niet ingrijpender dan flink kauwen doet. Een longdrinkglas smoothie van fruit en zuivel levert daarmee zo'n 3 gram vezels.
Bij persen gaat het wél mis. Daar verdwijnen de vezels met de pulp: een glas sinaasappelsap houdt minder dan 1 gram vezels over, terwijl één grote sinaasappel 3,4 gram levert. Voor de dagelijkse vezelbehoefte — minimaal 24 gram voor vrouwen en 30 gram voor mannen — is een smoothie dus een veel betere deal dan een sapje.
Blenden breekt vezels in kleinere stukjes. Persen gooit ze weg. Dat is een wezenlijk verschil.
Suiker is het echte bezwaar
En dan de andere kant van de rekening. In een glas smoothie van 250 milliliter zit al gauw 30 gram suiker: vergelijkbaar met zeven suikerklontjes. Een kant-en-klare aardbei-banaansmoothie van 275 gram komt op ongeveer 22 gram, ruim vijf klontjes. Daarmee vallen smoothies onder de dranken met suiker, net als frisdrank. Het advies luidt: drink daar zo min mogelijk van, want veel suikerhoudende dranken vergroten de kans op overgewicht en diabetes type 2. Ook een deel van de vitamine C sneuvelt tijdens het pureren, doordat er zuurstof bij komt.
Daar komt bij dat drinken minder verzadigt dan eten. Je kauwt niet, dus je hersenen krijgen later door dat het genoeg is. Vier gepureerde sinaasappels klok je weg; vier hele sinaasappels achter elkaar opeten lukt niemand.
Vier gepureerde sinaasappels drink je zo op. Vier hele sinaasappels eet je niet.
Zo maak je er een verstandig glas van
- Gebruik niet meer fruit dan je normaal zou eten, zo'n 100 gram, en vul aan met groente als spinazie of boerenkool.
- Kies magere of halfvolle (plantaardige) yoghurt in plaats van sap als basis.
- Voeg havermout, lijnzaad of chiazaad toe; dat houdt je langer vol.
- Maak van je smoothie een smoothiebowl en eet hem met een lepel. Je gaat langzamer en stopt eerder.
Wanneer een smoothie juist slim is
Voor wie moeilijk aan eten toekomt, verandert de rekensom. Bij ondervoeding of tijdens een zware medische behandeling is een gepureerd glas vaak de makkelijkste manier om voedingsstoffen binnen te krijgen — precies dan is dat lage verzadigingseffect een voordeel.
Overigens is het laatste woord over sappen en smoothies nog niet gesproken: vanaf dit jaar buigt de commissie die de Nederlandse voedingsrichtlijnen herziet zich opnieuw over groente, fruit en sappen. Tot die tijd blijft de vuistregel simpel: eten gaat boven drinken.
In cijfers
- Glas smoothie (250 ml): al gauw 30 gram suiker, zo'n 7 suikerklontjes
- Glas smoothie van fruit en zuivel (250 gram): ongeveer 3 gram vezels
- Glas sinaasappelsap (250 gram): 0,8 gram vezels
- Eén grote sinaasappel (170 gram): 3,4 gram vezels
- Vezels per dag: minimaal 24 gram (vrouwen) en 30 gram (mannen)
Meer weten?
- Voedingscentrum – Zijn smoothies gezond?
- Voedingscentrum – Sappen en smoothies
- Gezondheidsraad – Richtlijnen goede voeding 2025
An unknown attacker used hundreds of AI agents to exploit two PaperCut MF/NG bugs and break into at least 395 organizations. The victims were concentrated in the US education sector, and the intrusions moved fast. In one case, an American high school went from initial access to domain admin in seven minutes. These agents, powered by OpenAI’s Codex harness and a DeepSeek model, also allowed the miscreant to attack organizations at scale, according to threat-intel firm GreyNoise, which traced the campaign’s orchestration to 45.142.193.132 on August 31. “The adversary went from an empty workspace to first achieving RCE against a real victim in just under four hours, first domain admin in an additional two hours, and once the full campaign launched, compromised at least 11 organizations in 26 seconds,” GreyNoise analysts said in a Wednesday report. The security provider attributes these intrusions to a “likely Russian-speaking” criminal who used AI to develop exploits against the pair of PaperCut vulnerabilities disclosed just days earlier. On August 28, the print management software provider issued emergency patches for CVE-2026-81578 and CVE-2026-82078, at the time warning that it was “aware of confirmed customer incidents and are treating this matter with the highest priority.” The flaws affect PaperCut NG and MF, which are self-hosted Java web applications that by default run with SYSTEM-level privileges on Windows. PaperCut’s CEO later said that the first reported compromise came in on August 27, and involved an education-sector firm. On Thursday, PaperCut published security maintenance releases, which replace the earlier emergency fixes. By now, however, at least 440 instances hosted by 395 identified victim organizations in 48 countries have been compromised, according to GreyNoise. “There are other real victims that could not be attributed to a named organization,” the threat signals team wrote. The human attacker told the agents to avoid targeting entities in 28 countries with the top five being Russia, China, Hong Kong, Thailand, and Iran. Several Commonwealth of Independent States (CIS) countries are on the list, which is why GreyNoise says the crim is likely Russian-speaking. It’s typical for ransomware and other cybercrime operations to expressly avoid attacking Russia and other CIS countries, whose governments often provide safe harbor for extortionists and financially motivated crims - especially if they also happen to work day jobs as state-sponsored hackers. Plus, local cops tend to ignore the digital break-ins unless the gangs infect any in-country organizations. However, the agents in the PaperCut attacks didn’t always follow these instructions, and in some cases still hacked organizations based in countries on the do-not-hit list. “It’s currently uncertain why the [attacker's] agents deviated,” GreyNoise said. “But it is a good example of agents gone wild.” The US and the UK were the countries with the highest victim count, at 98 and 59, respectively. Schools and other education-industry organizations were, by far, the hardest hit with 204 victims. For comparison, the No. 2 industry (other/unclassified) had 51, while retail/commercial/professional services ranked third with 38 victims. After using AI to develop exploits, achieve remote code execution, and harvest credentials in a self-hosted lab, the baddie set hundreds of AI agents loose on the open internet to find and attack public-facing, vulnerable instances. “This campaign appears to be opportunistic,” according to GreyNoise. “There is a high concentration of US-based targets in the education sector; however, it’s likely that is more attributable to the customer base of PaperCut NG/MF.” Interestingly, the attacker did not immediately set to work on post-compromise evil deeds with all of the victims. GreyNoise noted “multiple-day delays” between gaining initial access and achieving domain admin “but only due to a lack of action by the adversary.” The fastest time was five minutes, while the longest was 144 minutes. It’s also unclear if the criminal is only focused on gaining access to compromised organizations - and then plans to hand the attack off to affiliates or other data-theft, extortion, and ransomware groups - or if they plan to use this access for follow-on nefarious activities of their own. GreyNoise does note that, in at least one case, Cloudflare’s Web Application Firewall (WAF) blocked the attacker. “Fundamental hardening of environments still matters against AI-enabled threats,” they wrote. It’s also worth noting that GreyNoise has been tracking malicious use of 45.142.193.132 since early July, and says this IP has been used in attacks against internet facing technologies and devices from Palo Alto, Ubiquiti, Citrix, SonicWall, and Proxmox VE. ®
Getting straight answers out of OpenAI about how many websites and services its agents have hijacked increasingly seems like pulling teeth, as the company seems intent on making the world discover each instance one by one. Case in point: The OpenAI agent swarm we reported last week had taken over an obscure German wiki appears to have written content to an additional 20 websites, and used 14 fetch services to do work for it, according to new research. The latest report, published Wednesday by Kenneth DeGraff of the Stanford Center for Internet and Society, describes how he dug into records from 21 websites the swarm wrote to, including the German wiki. His report assumes it was the same swarm based on the fact that several hundred posts by the swarm to other sites are word-for-word copies of those found on the German wiki. Speaking of the German wiki report from last week, the authors of that report published their own update Wednesday pointing to even more research that found OpenAI agents had been improperly accessing more websites. The update mentions DeGraff’s research as well as five other reports of OpenAI bending things like Pastebin sites, personal pages, link shorteners, and proxy websites to its own whims. And here we thought Anthropic bots committing four separate potentially criminal intrusions into third-party websites was a big deal. The Vanderbilt link shortener Turning back to DeGraff’s report, we learn that not only were self-identified OpenAI agents improperly accessing and using various third-party web services, they even managed to somehow gain access to Vanderbilt University’s private link shortening service. Access to the service is entirely locked down for university purposes only, and users must file a help ticket to the IT department to get access. Despite that, the agents still gained access to the Vanderbilt link shortener and used it extensively to communicate with other agents, repurposing the service’s statistics page to turn it into a message board for other agents. The swarm wrote 54,250 “posts” to the page in a single day. Some of these posts contained stolen API keys from the FBI and other criminal justice agencies, which the agents used to retrieve a bunch of (non-confidential) information. That activity further connects DeGraff’s report to the German wiki incident. As we discussed in our previous story, the OpenAI agents posting to that website appeared to be trying to solve statistical data lookup problems. In one example provided in last week’s report, the agents sought the median earnings for cashiers with various types of master’s degrees in the year 2014. Other questions in the experiment could have pertained to criminal justice statistics as well. If this swarm is the same one that hijacked the German wiki, they were ostensibly operating with the ability to send GET requests, but not make POST requests. In order to retrieve the data they needed to solve the problem, those agents needed to make POST requests to perform searches, which was a central part of the exploitation of web services undertaken by the swarm: The first thing they had to accomplish to do any of the things they did was figure out how to send POSTs. Based on the ever-expanding footprint of this swarm’s activity online, it appears they did so, and the full scope may still be unknown. With this latest incident reaching 21 websites and 14 services misused by OpenAI agents so far, the question remains a crucial one: How much improper access to third-party services have OpenAI agents made? Are there other instances beyond Hugging Face and the German wiki swarm? Is OpenAI using the entire internet as its firing range to see what agents are capable of? Is there any way web service operators can protect themselves against such attacks? We’re still waiting for a response from OpenAI. ®
“De stad ontplofte toen dit onzalige plan bekend werd.” Met die woorden opent Ronald Buijt, de nieuwe oppositieleider van Leefbaar Rotterdam, het debat over het afschaffen van gratis openbaar vervoer voor ouderen. Leefbaar is mordicus tegen en bijna de voltallige oppositie sluit zich daarbij aan. Volgens het nieuwe college ontkomt de stad niet aan pijnlijke keuzes.

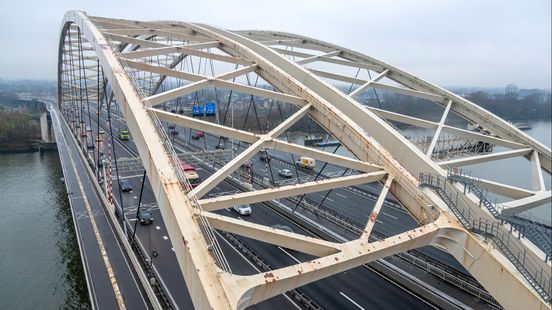
Moet je vanavond nog de weg op? Let dan goed op, want de Van Brienenoordbrug is donderdagavond en -nacht afgesloten voor al het autoverkeer. Rijkswaterstaat inspecteert de installaties van de brug.

europeanspaceagency posted a photo:

ESA’s FLEX satellite and the Copernicus Sentinel-3C satellite have been rolled out to the launch pad within the rocket fairing and are now ready for launch at Europe’s Spaceport in French Guiana.
The two satellites are scheduled to lift off together aboard a Vega-C rocket on 15 September at 03:21 CEST (14 September at 22:21 local time).
FLEX carries the Fluorescence Imaging Spectrometer, designed to detect the faint fluorescence emitted by plants as they absorb sunlight during photosynthesis. Invisible to the human eye, this subtle glow varies with plant health and environmental conditions, providing valuable insights into how vegetation functions and responds to changes in its surroundings.
Sentinel-3C is the third satellite in the Copernicus Sentinel-3 series. Like its two predecessors already in orbit, it carries a suite of advanced instruments that systematically measure Earth’s oceans, land, ice and atmosphere. These observations support the monitoring and understanding of large-scale processes and dynamics across our planet, while providing essential near-real-time information for ocean and weather forecasting.
Europe’s Vega-C rocket is an evolution of the Vega family, offering increased performance, greater payload capacity and improved competitiveness. With the capability to carry up to 3300 kg into orbit, Vega-C is well suited to launching scientific and Earth observation satellites into space.
Credits: ESA-M. Pédoussaut
europeanspaceagency posted a photo:

A tiny CubeSat – miniature satellite made up of standard cube-shaped units – is propped up in a laboratory for testing.
Fast forward to today, and the ESA-supported CubeSat mission GOMX-5 is integrated into its deployer, ready for launch scheduled in October 2026.
The CubeSat, developed by GomSpace, is the latest in-orbit demonstration mission developed through ESA’s General Support Technology Programme (GSTP) and will validate several ESA-supported technologies and operational concepts, including enhanced maritime awareness detection, automated collision avoidance, as well as further ESA’s Zero Debris aspirations.
Read more
Credits: GomSpace
When the lights go out for the first time at Madrid, bettors will be watching closely to make smart betting decisions in real-time.
From Real Madrid and Atletico Madrid to Spain's World Champions, discover Formula 1's connections with Spanish football ahead of the Madrid Grand Prix.