Eén datacenter slurpt evenveel stroom als heel Eindhoven. Wat betekent dat voor Nederland?

Eén Microsoft-datacenter in Noord-Holland gebruikt één procent van alle elektriciteit op het Nederlandse net. En de komende jaren komen er nog meer van dit soort hyperscalers bij. Wat betekent dat voor ons stroomverbruik? En waren dit soort megadatacenters niet verboden?


Niet eerder in zijn leven had Gustav von Aschenbach zo’n mooie jongen gezien

Onstuimige, verboden, onuitgesproken verliefdheid. Deze zomer zoekt NRC de beste boeken over zomerse liefde. Deze aflevering: De dood in Venetië.

Eindelijk is dit afgrijselijke WK bijna ten einde

Het begon al met ONS voetbalelftal dat in de aanloop al door het oog van de naald kroop tegen Oezbekistan, daarna op het WK zelf nog best aardig voetbalde en toen na tactische aanpassingen van voetbalwetenschappelijk meesterbrein Ronald Koeman van het veld werd gekoemanbald door het toch wel vrij magere ploegje Marokko, dat zelf weer helemaal van de mat werd getikt door Frankrijk, een ploeg met minder goede middenvelders dan Nederland, maar met in ieder geval een middenveld. Met het oeverloze gedoe dat we nu niet droomkandidaat Arne Slot, maar Sarina Wiegman als coach zouden moeten hebben. Niet omdat Sarina Wiegman zoveel prijzen heeft gewonnen (dat heeft ze namelijk gedaan), maar alleen maar omdat ze een vrouw is. Met al die Marokkanen die op tv zaten te janken dat het sloopgedrag van Marokkanen niet komt door Marokkanen, maar dat het eigenlijk de schuld is van Nederlanders, en dat slopende Marokkanen weliswaar erg zijn, maar wat te denken van de Slag bij Beverwijk in 1997?? Met de achterkamertjescamorra van de FIFA, de op twee na meest maffioze club ter wereld slechts na de 'ndrangheta en de VVD, met die totaaaaaale idioot van een Gianni Infantino, die kale eikel die vroeger altijd als laatste werd gekozen met gym, een paar keer achter de goede mamagans aan is gewaggeld en nu in het centrum van de macht staat, terwijl hij opgepakt zou moeten worden omdat hij een nepotist en een halve crimineel is. Maar daar zit hij weer, met alle staatshoofden te jubelen, heeee Wimpie-Alexander, ja met mij ook alles goed, en daar staat-ie weer met iemand anders met een zak geld te knuffelen, met z'n gore met Zwitserse franken gladgetrokken glimlachkop. Met ónze KNVB die wel een grote belerende snuit heeft over fairplay en respectbandjes en wat dies meer zij, maar aan de corrupte boevenzooi bij de FIFA niets durft te doen, gelaten en gedwee tekent bij het kruisje als Infantino weer verkozen moet worden, zelfs jubelt dat het WK weer zo'n waanzinnig groot succes is, wat is het toch een succes. Wat een succes! Die volslagen achterlijke ticketprijzen, waardoor normale fans eigenlijk niet naar het stadion kunnen, tenzij ze hun huis verkopen of toevallig ergens een ingang hebben bij een of ander bedrijf. Met hospitalityarrangementen en VIP-tickets die zo veel belangrijker zijn dan normale tribunekaarten voor de gewone supporter: het WK was altijd al commercieel, maar dit gaat echt alle perken te buiten. Met de volstrekt debiele inmenging van Donald Trump, die met zijn corrupte vriendje belde en een rode kaart ongedaan gemaakt kreeg. Met straks in de finale een achterlijke halftimeshow van een halfuur, die hydratation breaks waar de Belgen dan nog een beetje bij gaan lullen, maar die de NOS helemaal volpompt met reclames over gokken bij de Staatsloterij. Met die roeiende vikingen, met speciale aandacht voor die ene viking, want het klopte allemaal niet ofzo. Met 100.000 wedstrijden in een maand tijd, waarvan de helft het aanzien totaal niet waard was, al zaten we in het begin nog wel voor de tv voort Kiribati - Mongolië (2-1), tot we er diarree van kregen. Met minutenlange shots van allerlei hotemetoten op de tribune en dan was het Leonardo di Caprio en dan zei Jan 'seleçao' Roelfs weer dat het een sterbasketballer van de NY Knicks was. Sowieso, JAN ROELFS, de Robert Mugabe van de NOS. En en dan moet het ergste nog komen: dat die door de FIFA voorgetrokken en op het veld volledig doorgesnoven Argentijnen straks de beker in de lucht mogen tillen, na penalty's, tijdens de Schande van New Jersey. Zijn álle Argentijnen zo debiel, of zijn het alleen die 11 idioten op het veld? Nee, snel vergeten, dit toernooi.

Liveblog wapenstilstand. Gisteren twee Amerikaanse aanvalsgolven, 'Amerikaanse vrouw bevrijd uit Iran'

Social

Trump schrijft bovenstaand dat er een 'Amerikaanse vrouw' die sinds 2024 'onwettig' vastzat in Iran het land veilig heeft verlaten. Hij noemt haar identiteit niet, maar de New York Times sprak in augustus 2025 van een vrouw met een Iraans en Amerikaans paspoort die in december 2024 in Iran gearresteerd was, maar vervolgens werd vrijgelaten nadat haar paspoorten waren afgenomen, waardoor ze het land niet kon verlaten. De New York Times beschreef haar destijds als volgt: "De vrouw werkt voor een Amerikaans technologiebedrijf en leidt een liefdadigheidsorganisatie voor kansarme kinderen in Iran. Maar na de recente oorlog heeft de Iraanse rechterlijke macht haar zaak opgeschaald en haar aangeklaagd wegens spionage, aldus haar advocaat – een ernstig misdrijf waarop jarenlange gevangenisstraf en zelfs de doodstraf kan staan."

Dan even over de Amerikaanse aanvalsgolven van gisteren. Dat waren er twee, maar die daarvoor eindigde pas om 22:00 de vorige avond, dus het zat erg dicht op elkaar allemaal. CENTCOM schrijft:

"CENTCOM beëindigde op 15 juli om 21.00 uur (Eastern Time) een reeks aanvallen op Iran die in de avonduren plaatsvond. Amerikaanse strijdkrachten vielen Iraanse commandocentra, luchtverdedigingslocaties, faciliteiten voor raketten en drones, en kustbewakingsposten aan. Hiermee werd beoogd het vermogen van Iran verder te ondermijnen om een ​​bedreiging te vormen voor onschuldige zeevarenden aan boord van commerciële schepen die door de Straat van Hormuz varen. CENTCOM zette precisiewapens in om doelen op meerdere locaties, waaronder Bandar Abbas, te raken. Eerder die ochtend hadden Amerikaanse strijdkrachten tijdens een aanvalsgolf van 90 minuten al installaties voor kustverdediging en kruisvluchtwapens op het eiland Greater Tunb bestookt."

Ook heeft CENTCOM als onderdeel van de opnieuw ingevoerde maritieme blokkade van Iraanse havens een olietanker uitgeschakeld die weigerde om te keren: "Strijdkrachten namen waar dat de onder de vlag van Curaçao varende tanker M/T Belma door internationale wateren richting Kharg-eiland voer. Het commerciële schip negeerde herhaalde waarschuwingen toen het probeerde de Amerikaanse blokkade te doorbreken. Een Amerikaans toestel schakelde het schip uit door Hellfire-raketten op de schoorsteen af ​​te vuren. Het schip is niet langer onderweg naar Iran."

Iran reageerde met de traditionele aanvallen op Amerikaanse doelen in Golfstaten. Benieuwd wat vandaag brengt, wij gaan weer live!

CENTCOM sfeerbeeld

Social

CENTCOM schakelt olietanker uit die weigerde om te keren

SocialSocial

Unauthorized low passes will continue until morale improves

Social

Rijnmond - Nieuws

Het laatste nieuws van vandaag over Rotterdam, Feyenoord, het verkeer en het weer in de regio Rijnmond

Hennie van der Most vraagt eigen faillissement aan na miljoenenstrop met Rotterdams pretpark

Het moederbedrijf van ondernemer Hennie van der Most, Van der Most Top Holding, is door de rechtbank in Overijssel failliet verklaard. Dat komt niet als een verrassing. Vorige maand werd al bekend dat de schulden van zijn failliete pretpark waren opgelopen tot 50 miljoen euro.

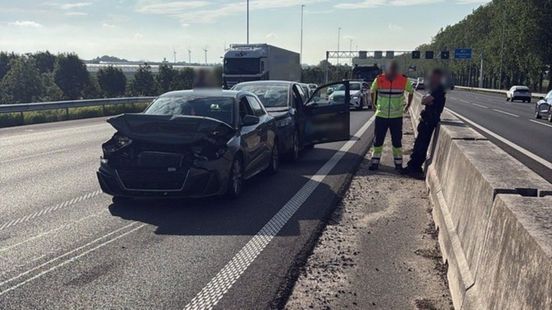
Nog meer verkeersellende: Ongeval op A12 zorgt voor uur vertraging

Een ongeval op de A12 bij Bleiswijk zorgde donderdagochtend voor flinke verkeershinder. Automobilisten richting Den Haag moesten rekening houden met een vertraging van ongeveer een uur. Inmiddels is de weg weer vrij.

After the Strain of a Slow Hard End

Thomas Hawk posted a photo:

After the Strain of a Slow Hard End

Someone Like You

Thomas Hawk posted a photo:

Someone Like You

Vale Sam Neil

Popplio728 has added a photo to the pool:

Vale Sam Neil

The Courier Mail - Tuesday July 14 2026.

Vale Sam Neil

Popplio728 has added a photo to the pool:

Vale Sam Neil

The Advertiser - Tuesday July 14 2026.

Vale Sam Neil

Popplio728 has added a photo to the pool:

Vale Sam Neil

The Advertiser - Tuesday July 14 2026.

Vale Sam Neil

Popplio728 has added a photo to the pool:

Vale Sam Neil

Herald Sun - Tuesday July 14 2026.

Vale Sam Neil

Popplio728 has added a photo to the pool:

Vale Sam Neil

The Daily Telegraph - Tuesday July 14 2026.

Vale Sam Neil

Popplio728 has added a photo to the pool:

Vale Sam Neil

The Advertiser - Tuesday July 14 2026.

The Guardian

Latest news, sport, business, comment, analysis and reviews from the Guardian, the world's leading liberal voice

Fleabag at 10: did Phoebe Waller-Bridge usher in a wave of female-fronted series – or straitjacket them?

The confessional classic opened the floodgates for a generation of brilliant female showrunners. But as risk-averse streamers tighten their purse strings, is the industry forcing women’s stories back into a box?

Ten years ago, Phoebe Waller-Bridge locked eyes with the camera and asked her audience: “Do I have a massive arsehole?” An unexpected punchline to a monologue about a booty call that went surprisingly – and literally – south, it announced Waller-Bridge as a new star of British telly. The half-hour comedy series Fleabag broke the fourth wall, and the internet. Its second season was even bigger, spawning countless thinkpieces discussing Andrew Scott as the “hot priest” and the sold-out Topshop jumpsuit worn by Waller-Bridge, which had a keyhole cutout revealing an aspirational slice of boob.

Both Fleabag and Waller-Bridge were praised for blazing a path that female showrunners and their feminist creations could later stomp down. It secured Waller-Bridge an exclusive deal with Amazon worth a reported $20m (£16m) a year. The show’s success certainly changed Waller-Bridge’s life. But, a decade on, as the British television industry has been reshaped by the rise of streamers, budget cuts and dwindling opportunities for new talent, how did it change TV?

Continue reading...

Behance Featured Projects

The latest projects featured on the Behance

Gauchos


The Register

Biting the hand that feeds IT — Enterprise Technology News and Analysis

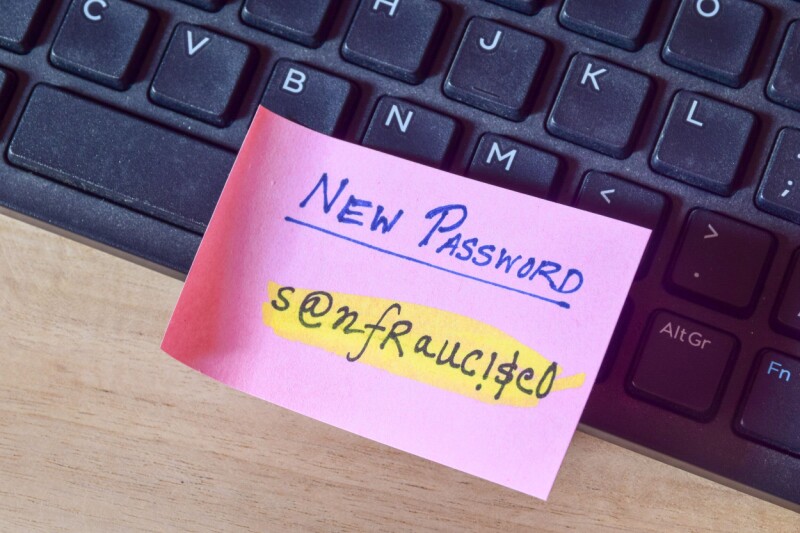
Law firm insisted on one password to rule them all

PWNED Welcome back to PWNED, the weekly column where we gather lessons from organizations that didn’t take security seriously enough. This week’s tale of woe comes from a company that left a door wide open for miscreants, but was lucky it didn't have to pay the price. Have a story about someone leaving a gaping hole in their network? Share it with us at pwned@sitpub.com. Anonymity is available upon request. Our story comes courtesy of a reader we’ll Regomize as Manny. A few years ago, Manny got a job working at a law firm. The firm used him to replace an entire team, making him the de facto IT department all by himself. He soon discovered that all of the company’s data and applications lived in one large web-based interface, which was divided up based on the type of client. So there were areas in the UI for personal injury cases and others for travel refunds, for example. There was just one big, gaping security hole: a master password that allowed you to log in as any user in the system. If you had this password, which many people in the law firm did, you could grab detailed personal information about any client, even their health records. “I immediately raised this as a huge security risk,” Manny told us. “But I was told, 'Oh that's the admin password, everyone uses it. Don't touch it.'” As long as you had the person’s email address that you wanted to impersonate, this password would allow you to impersonate them. This applied to both staff and clients. “Colleague is off sick? Sign in as them and reassign their work to someone else to complete. Client forgot to fill in a field? Log in as them and complete it for them,” Manny said. The system itself was 15 years old, ancient in tech terms, and it desperately needed replacing. So Manny was asked to build a whole new system. Naturally, he refused to add a back door, even though that’s what the boss wanted. “I point blank refused to add any back doors to it,” Manny recalled. “So they promoted every user to a system admin and carried on, business as usual.” What we can take away from Manny’s experience is that sometimes even the best IT people who know security basics can still be hindered by clueless management. We also know that sometimes in order to pay the bills, IT people have to go along with security practices they strongly disagree with. In the end, the boss will have the final word, even if that word is “ignorance.” ®

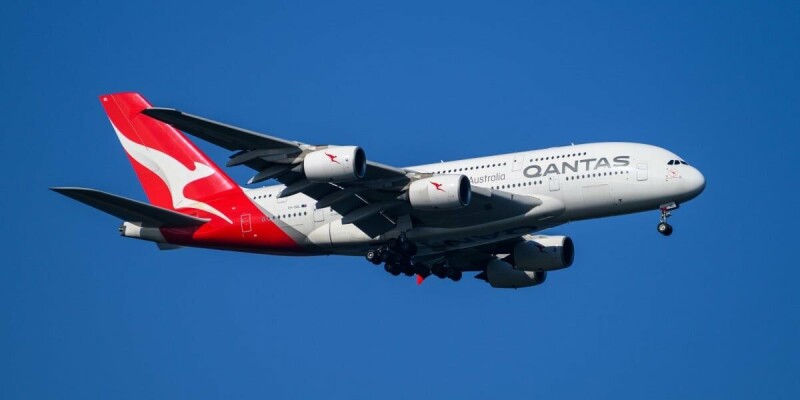
Tech support scam caused massive data breach at Australian airline Qantas

Australia’s Privacy Commissioner has revealed a tech support scam was the cause of the massive 2025 data breach at Australian airline Qantas and found the carrier didn’t breach its privacy obligations despite leaking personally identifiable information for 5.7 million customers. The Commissioner reached that conclusion, and a decision not to open a formal privacy probe, in a report published today. Qantas has previously admitted the incident was the result of a social engineering attack on a contact center. The Commissioner’s report goes deeper, explaining a crook who claimed to represent “Qantas IT help” made the call and told a contact center agent to access a CRM system and perform certain actions needed to close a support ticket. Those actions instead connected the CRM to a data extraction tool which the crooks used to siphon off customer records. The Commissioner considered whether Qantas observed the Australian Privacy Principles (APPs), the binding rules that govern how businesses safeguard PII, and found the airline did the right thing. The report found that Qantas audited the operator of the contact center and tested the security awareness of its employees – and had done so in the months before the incident. Qantas also conducted mandatory and recurring training on how to handle PII. The Commissioner was therefore satisfied Qantas took adequate steps to ensure the contact center observed the APPs and didn’t fail in its obligations. The regulator made a similar finding regarding the airline’s cross-border data-sharing practices. “Our inquiries did not identify any omissions in the steps Qantas took that, if addressed, would have prevented the breach that occurred in this incident,” the report states. The APPs include a requirement to take reasonable steps to protect personal information from unauthorized access. Again, the Commissioner decided Qantas complied because it used role-based access controls, among other techniques to protect data. Another issue the regulator considered was whether Qantas took reasonable steps to destroy or de-identify the personal information it didn’t need. The carrier told the Privacy Commissioner that it scheduled annual data removal runs from its CRM, and that no records that deserved deletion or removal were present at the time of the attack. That clean record saw the Commissioner decide not to launch a deeper investigation. “I have a broad discretion to commence an investigation of an act or practice where it may be a contravention of the APPs and where it is desirable to do so,” the report states. The first-person pronoun is presumably the work of Commissioner Carly Kind, who observed “it does not appear that Qantas could have reasonably foreseen and prevented the breach in the manner that it occurred. The way in which the threat actor gained access was through a vishing attack which could not have been prevented by a strengthening of Qantas’ current role-based access controls.” It’s possible the Commissioner will revisit the matter at another time, and class-action lawsuits are also in train regarding the incident. Qantas may therefore still have to fight through plenty of turbulence before this matter lands. One thing the report doesn’t address is the identity of the attackers. Pundits have suggested the Scattered Spider gang did the deed after it started attacking the aviation industry in the weeks before the Qantas incident. ®

The Daily WTF

Curious Perversions in Information Technology

CodeSOD: Wait Longer

Karen was maintaining some specification tests that were flaky. Not extremely flaky, but three or four times out of a thousand, the tests would just fail. The tests were complicated, and some of the operations were timing sensitive, so it wasn't precisely surprising- but the problem was that they were actually generous with their timing windows. The unit tests passed consistently, it was only these functional, specification-based tests that failed.

So, for example, there were sections in the tests where they wanted to wait at least 2ms. Since the code and tests were in TypeScript, they used the setTimeout function, which per standard JavaScript documentation warns that it may wait longer. But again, Karen was fine with longer.

Unfortunately for Karen, the documentation for NodeJS is less specific, as it makes no guarantees about when the timeout function gets invoked. This means that it can fire the timeout before the time has elapsed.

After many, many hours of debugging, that was exactly the situation that Karen found herself in. Which is why her very simple wait function went from:

export const wait = (ms:number) => new Promise((complete) => setTimeout(complete, ms));

To the much more awkward:

export const wait = (ms: number) {
    const target = performance.now() + ms;
    return new Promise((complete) => {
        const checkReady = () => {
            if (performance.now() > target) {
                complete();
            } else {
                setTimeout(checkReady, 1);
            }
        }
        setTimeout(checkReady, 1);
    });
}

This version of the function checks the time every millisecond, and only completes the operation if we've waited at least as long as our target duration. This ensures that the timeout never fires too soon and it fixes the janky tests. But it's also terrible. Terrible that it exists. Terrible that this is the best solution. Terrible that our functional tests need to be so time sensitive. And terrible that the Node runtime actually breaks the one consistent scheduling guarantee that pretty much every other scheduler does: that it'll wait at least as long as you asked, but might wait much longer.

At best, we can say, "at least it's only testing code."

[Advertisement] Picking up NuGet is easy. Getting good at it takes time. Download our guide to learn the best practice of NuGet for the Enterprise.

Ius Mentis

Internetrecht door Arnoud Engelfriet

Wat als een Vinted-verkoop misgaat? ‘Ineens had ik 817 euro verlies gemaakt’

Vinted is een van de populairste platforms voor tweedehands kleding, maar niet iedereen houdt daar een positieve ervaring aan over. Dat meldde TROS Radar onlangs. Ze onderzochten de uiteindelijk toch juridische vraag: hoe goed zijn verkopers op Vinted eigenlijk beschermd als er iets misgaat?

Kern van het probleem is dat het platform (net als diverse andere) met kopersbescherming werkt, waarbij verkopers eigenlijk met lege handen staan als het platform meent dat de koper een punt heeft:

Radar ontving de afgelopen tijd meerdere klachten over Vinted. Gebruikers vertellen onder meer dat zij onterecht worden geblokkeerd, dat zij namaak- of beschadigde artikelen ontvangen, en dat betalingen soms niet worden vrijgegeven of juist wel terwijl dat niet zou moeten. Ook wordt vaak genoemd dat contact met Vinted lastig is en dat besluiten niet goed worden uitgelegd of besproken.
Het idee van kopersbescherming is even sympathiek als eenvoudig. De betaling van de consument wordt in depot (escrow) gehouden tot je je producten hebt. Blijkt de zending kwijt, dan lost Vinted dat op door je geld terug te geven. Ook bemiddelen zij bij een geschil, en omdat de winkel het geld dan nog niet heeft, zal die sneller meewerken aan een oplossing.

Het probleem is even eenvoudig: als verkoper heb je nu geen enkele kans meer als de koper (te) makkelijk gelijk krijgt. Bezwaar is moeilijk, bewijslast torenhoog en contact krijgen wil vaak ook niet lukken. Al sinds 2022 zijn klachten van deze aard te lezen.

Juridisch is hier weinig over geregeld. De Digitaledienstenverordening (DSA) kent wel regels over online marktplaatsen, maar die gaan vooral over de consument meer informatie en waarborgen bieden. De wat minder bekende platform-to-business verordening (P2B) kent wél een beschermende regel voor bedrijven:

Onlinetussenhandelsdienstverleners zorgen voor een intern systeem voor het afhandelen van de klachten van zakelijke gebruikers.
Alleen gaat dat dan weer niet over klachten voortvloeiend uit de koopovereenkomst met de consument op het online platform. (Het is meer bedoeld voor zaken als je account dat zomaar gesloten wordt, of onduidelijkheden bij je app in de store geplaatst te krijgen.)

Arnoud


Het bericht Wat als een Vinted-verkoop misgaat? ‘Ineens had ik 817 euro verlies gemaakt’ verscheen eerst op Ius Mentis.