


Evgeny Drokov has added a photo to the pool:

Travelers traverse the sacred grounds of Fushimi Inari-taisha in Kyoto, Japan, passing through thousands of vibrant vermilion torii gates. Each gate represents a votive offering from individuals and businesses seeking prosperity, growth, and divine favor from the Shinto deity Inari. This winding path creates a physical journey into the heart of Japanese spiritual tradition, marking a history of dedication that spans centuries.
Visit my webshop shop.drokov.com for high quality photo prints that fit Ikea frames.
Half a year after Iranian drone strikes knocked out multiple Amazon data centers, the US tech company has acknowledged the permanent loss of some customer data that was hosted in Bahrain and the United Arab Emirates.
Amazon Web Services was "unable to restore access to the resources and data" hosted in some of the war-damaged data centers, according to an AWS dashboard update posted on September 15. The development was first reported by Reuters and suggests that the Iranian strikes inflicted catastrophic damage on the data centers.
Customer data was irretrievably lost in one of three AWS availability zones in the United Arab Emirates region, specifically the mec1-az2 availability zone.
Each availability zone is serviced by one or more Amazon data centers. The company is still working on "recovering regional resources" and restoring resources hosted in the other two availability zones in the United Arab Emirates... But the destruction was apparently even more widespread for the data centers in the Bahrain region, because Amazon said it was unable to restore access to resources and data across all three availability zones there. "The damage to our infrastructure spanned multiple Availability Zones and exceeded what our regional and multi-AZ services are designed to withstand," the AWS update said.
The company had already suspended customer billing in the affected AWS regions in Bahrain and the United Arab Emirates and has spent the past six months attempting to restore normal operations... [When the war began] AWS immediately urged customers to migrate resources to other cloud regions and use remote backups to restore any "inaccessible resources." The cloud service also reportedly issued $150 million in customer credits following the initial Iranian strikes in March.


Read more of this story at Slashdot.
In één oogopslag:
• 15.6°C · Bewolkt ☁️ | Min 14.9°C / Max 16.2°C | Kans op neerslag 57%
Verwachting voor vandaag:
• Min 14.9°C, Max 16.2°C (Lichte regen) 🌧️, Neerslag 5.0 mm, Kans op neerslag 57%, 🧭 1013.2 hPa ↗️ +3.4 hPa/24h, Windsnelheid: 27.4 km/u (7.6 m/s), richting: ↗ 210°
Uurlijkse voorspelling voor de komende 12 uur:
• 02:00: 15.7°C (Helder) 🌕, 🧭 1009.8 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 12.6 km/u (3.5 m/s), richting: ↗ 230°
• 03:00: 16.0°C (Bewolkt) ☁️, 🧭 1010.1 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 11.2 km/u (3.1 m/s), richting: → 259°
• 04:00: 15.4°C (Helder) 🌕, 🧭 1010.5 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 10.4 km/u (2.9 m/s), richting: → 265°
• 05:00: 14.9°C (Helder) 🌕, 🧭 1010.7 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 9.0 km/u (2.5 m/s), richting: → 262°
• 06:00: 15.1°C (Bewolkt) ☁️, 🧭 1011.0 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 10.4 km/u (2.9 m/s), richting: → 257°
• 07:00: 15.5°C (Bewolkt) ☁️, Kans op neerslag 1%, 🧭 1011.4 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 9.7 km/u (2.7 m/s), richting: → 253°
• 08:00: 15.9°C (Bewolkt) ☁️, Kans op neerslag 2%, 🧭 1011.8 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 10.4 km/u (2.9 m/s), richting: → 264°
• 09:00: 16.1°C (Bewolkt) ☁️, Kans op neerslag 3%, 🧭 1012.3 hPa ↗️ +0.5 hPa/1h, Windsnelheid: 13.3 km/u (3.7 m/s), richting: → 266°
• 10:00: 16.5°C (Bewolkt) ☁️, Kans op neerslag 5%, 🧭 1013.2 hPa ↗️ +0.9 hPa/1h, Windsnelheid: 14.0 km/u (3.9 m/s), richting: → 268°
• 11:00: 16.9°C (Bewolkt) ☁️, Kans op neerslag 6%, 🧭 1013.7 hPa ↗️ +0.5 hPa/1h, Windsnelheid: 15.1 km/u (4.2 m/s), richting: → 258°
• 12:00: 17.3°C (Bewolkt) ☁️, Kans op neerslag 6%, 🧭 1014.1 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 15.1 km/u (4.2 m/s), richting: → 254°
• 13:00: 17.6°C (Bewolkt) ☁️, Kans op neerslag 5%, 🧭 1014.2 hPa ➡️ 0.0 hPa/1h, Windsnelheid: 16.6 km/u (4.6 m/s), richting: → 255°
Voorspelling voor de komende dagen:
• zaterdag 19 september: Min 14.9°C, Max 18.3°C (Bewolkt) ☁️, Kans op neerslag 2%, 🧭 1016.0 hPa ↗️ +2.8 hPa/24h, Windsnelheid: 23.0 km/u (6.4 m/s), richting: ↗ 242°
• zondag 20 september: Min 16.4°C, Max 19.7°C (Lichte motregen) 🌦️, Neerslag 0.5 mm, Kans op neerslag 22%, 🧭 1022.2 hPa ↗️ +6.2 hPa/24h, Windsnelheid: 27.0 km/u (7.5 m/s), richting: ↗ 226°
• maandag 21 september: Min 13.9°C, Max 18.6°C (Matige motregen) 🌦️, Neerslag 0.8 mm, Kans op neerslag 22%, 🧭 1030.1 hPa ↗️ +7.9 hPa/24h, Windsnelheid: 22.3 km/u (6.2 m/s), richting: → 274°
• dinsdag 22 september: Min 13.1°C, Max 17.6°C (Bewolkt) ☁️, Kans op neerslag 2%, 🧭 1029.0 hPa ↘️ -1.1 hPa/24h, Windsnelheid: 11.6 km/u (3.2 m/s), richting: → 283°
• woensdag 23 september: Min 13.2°C, Max 20.7°C (Lichte motregen) 🌦️, Neerslag 0.6 mm, Kans op neerslag 8%, 🧭 1025.1 hPa ↘️ -3.9 hPa/24h, Windsnelheid: 8.0 km/u (2.2 m/s), richting: ↘ 294°
• donderdag 24 september: Min 14.3°C, Max 20.5°C (Bewolkt) ☁️, Kans op neerslag 3%, 🧭 1019.9 hPa ↘️ -5.2 hPa/24h, Windsnelheid: 10.9 km/u (3.0 m/s), richting: ↖ 121°
Details:
• 🌡️ Huidige temperatuur (om 01:15): 15.6°C (Bewolkt)
• 🤚 Gevoelstemperatuur: 15.2°C (-0.4°C)
• 💨 Windsnelheid: 13.7 km/u (3.8 m/s), richting: ↗ 222°
• 🌬️ Windstoten: 27.4 km/h (7.6 m/s)
• 💧 Luchtvochtigheid: 91%
• 🧭 Luchtdruk: 1009.8 hPa ↗️ +0.7 hPa/3h
• 👁️ Zichtbaarheid: 8.3 km
• ☀️ UV-index: 0.0
• 🌅 Zonsopgang: 07:19 · 🌇 Zonsondergang: 19:52
Luchtkwaliteit:
• AQI: 35 🟢 (Goed)
• PM2.5: 6.6 μg/m³
• PM10: 11.4 μg/m³
Gegevens geleverd door Open-Meteo
#Rotterdam #Meteo #MeteoBot #MeteoNetherlands #OpenMeteo #FediMeteo
Spurs and Villa meet in desperation derby and Andoni Iraola faces test on south-coast return
Chelsea have not won this west London derby since Brentford’s first Premier League season. Each visit since October 2021’s 1-0 win, Ben Chilwell the scorer, has been a draw. This season has continued the divergence between the clubs’ respective approaches, Brentford’s solidity and continuity compared to Chelsea attempting their latest reboot. Kevin Schade, after two well-taken goals at Bournemouth, will fancy facing a defence not yet attuned to Xabi Alonso’s configurations. Only one team has won a Premier League title with a defensive trio: Chelsea’s last title team, in 2016-17 under Antonio Conte. Alonso’s attack has been rather more successful, presenting another challenge for Jannik Schuster. Replacing Nathan Collins, the 20-year-old central defender had a tough examination from Bournemouth’s Evanilson on his first Premier League start, emerging with credit. For Chelsea, João Pedro has registered three goals and three assists, but doubts surrounding his fitness could lead to Danny Welbeck’s first league start. John Brewin
Brentford v Chelsea, Friday 8pm (all times BST)
Tottenham v Aston Villa, Saturday 3pm
Continue reading...Government spending watchdog warns of price of keeping publicly owned firm in business
Labour has been urged to lay out a credible plan for the future of British Steel, as the government spending watchdog warned of the “startling” costs of keeping the struggling manufacturer in business with no end in sight.
British Steel was taken into public ownership in July to protect “the future of steel production”, 15 months after the government stepped in to prevent the closure of its steelworks in Scunthorpe and the loss of 4,000 jobs.
Continue reading...Shabana Mahmood says she wants to distinguish between far-right extremism and legitimate local concerns over asylum sites
Shabana Mahmood has described the anti-asylum activist Daniel Thomas as “a far-right and outright racist” who will feel “the full force of the law” if his organisation commits crimes near contested asylum sites such as Piddington.
In an interview with the Guardian, the home secretary also “wanted to reassure” concerned villagers that asylum seekers due to move in to a neighbouring former defence site would not “put pressure” on local resources because they would be given “self-contained facilities”.
Continue reading...Educator talks of ‘moral obligation’ and urges ‘every wealthy white celebrity’ to make similar donation
YouTube star Ms Rachel has said she is matching rapper Macklemore’s $1m donation to organizations supporting Palestinians, calling on other public figures to follow suit.
Macklemore, who was fired as the opening act on Ed Sheeran’s tour after saying “Free Palestine” on stage at New Jersey’s MetLife Stadium, pledged to donate the entirety of his earnings from Sheeran’s tour to several organizations focused on the Palestinian people.
Continue reading...Hoops beaten again after chastening loss to Rangers
Juventus hammer NEC, Besiktas pile woe on Marseille
Celtic suffered another European embarrassment as the Scottish champions were beaten 3-1 at home by Ferencvaros in the Europa League. Just weeks on from crashing out of the Champions League qualifiers to Austrian side Lask, despite at one point holding a four-goal lead, Celtic’s defensive flaws were exposed once more.
Martin O’Neill’s team also suffered a chastening 3-0 defeat to rivals Rangers last weekend and failed to deliver on their manager’s promise to respond. Bamidele Yusuf opened the scoring for the visitors before Mika Baur equalised late in the first half. However Kristoffer Zachariassen quickly put Ferencvaros back in front before Daniel Arzani’s sensational strike, on his return to Celtic Park, capped a fine night for Ferencvaros.
Continue reading...

Cruising, traveling & dive pics. has added a photo to the pool:

Wandering around a farm next to a beautiful waterway is your idea of joy.
Tablelands FNQ

BertvB posted a photo:

A striking and expressive portrait of an American Bald Eagle (Haliaeetus leucocephalus) calling out while perching amidst a colorful bed of wildflowers

Executives working on AI at Microsoft and OpenAI admitted what its critics have been saying all along: Large language models are predatory pieces of technology that have been built on what a Microsoft executive called “an astonishing theft of unprecedented proportions,” and the “largest theft of labor in human history.” An internal Microsoft document said generative AI products have created a “doom loop” that is killing “the entire web.”
Those statements and a series of other mask-off moments feature heavily in an unredacted court filing that was unsealed Thursday in the behemoth New York Times vs OpenAI copyright lawsuit that has been winding its way through the court system for years. In a filing asking for summary judgment (basically, a filing with the court asking it to rule), lawyers for the New York Times laid out a series of admissions made by Microsoft and OpenAI executives in documents and depositions that until now had remained either sealed or redacted at the request of Microsoft and OpenAI.
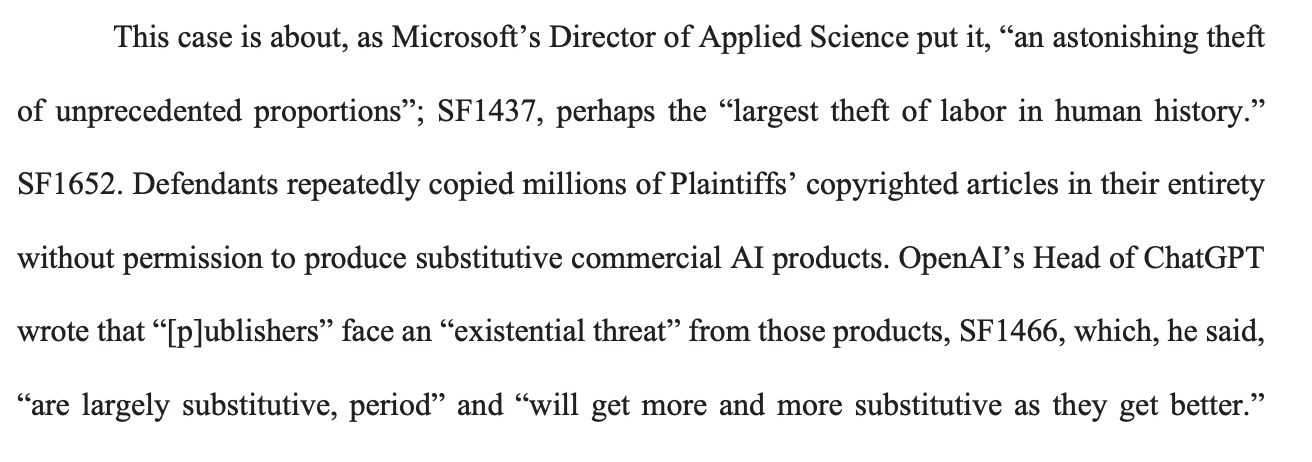
It’s easy to see why the AI companies wanted to hide this from the public. The statements, taken together, are some of the most damning indictments of the ways LLMs were trained, how they worked, and the immediate threat they pose to human labor. It is a reminder that even as AI becomes more powerful and companies try to shift the narrative to the supposed existential risk of “superintelligent” AI, the tools they have already built were created by stealing from human creativity and labor and are by definition existential threats to the human labor market.
“Millions of people around the world will soon consider large models ‘hoovering up’ all their work to be an astonishing theft of unprecedented proportions,” an internal Microsoft document cited in the case read, adding “almost no one intended for content they created to be used in this fashion, nor are they compensated for its use.”
The filing was written by lawyers for the New York Times but is largely comprised of statements and interviews with big tech executives that admit both that LLMs are largely trained on stolen content, that they represent an existential risk for the human writers, artists, and media companies that they stole from, and that their products have started a “doom loop” that is eating the web and destroying the businesses that these companies stole from.
The unredacted filing was found by Jason Kint, the CEO of Digital Content Next, a trade organization that represents digital media companies. Kint has been closely following and posting about massive AI copyright lawsuits.
The court filing cites an internal Microsoft document that found that AI products steal from human content creators, then cannibalize clicks from the people and websites they’ve stolen from, thereby destroying their business models.
“Our AI content strategy has started a ‘doom loop’ that will hurt the performance of our models and the entire web at the same time: It is highly unusual that an end-product threatens the economic foundations of its essential suppliers, but that is the situation we have created for our LLM business with respect to its ‘content supply chain,’” the document said.
Microsoft executives, including CEO Satya Nadella, testified under oath that after ripping content from the New York Times and other news sites, clicks to those news sites fully cratered, falling by more than 90 percent on Bing.
Documents obtained during the court proceedings found that OpenAI created “a hack to get around nytimes paywall,” to which OpenAI cofounder Greg Brockman said “ah, nice.” Microsoft executive Brent Hecht wrote that LLMs steal content “without ways of distributing economic value down the supply chain, [which] necessarily threatens the economic stability of those who create the content.”
OpenAI’s policy director Jack Clark wrote that the company was “creating systems that substitute for the labor of the people that define the ‘culture’ of society” and Microsoft, in a policy document, wrote that generative AI could “significantly disrupt the employment of the very people who generated the data on which the foundation model was trained […] LLMs are a product that destroys its supply chain.” OpenAI called itself an “existential threat” to news publishers, and an OpenAI software engineer testified that “no matter how prominently we show the links, users won’t click.”
None of this is at all surprising to anyone who has been paying attention to the development of generative artificial intelligence, but the document, taken in whole, is a real they-admit-it situation. OpenAI’s and Microsoft’s lawyers have been trying to argue that their model training is fair use and transformative under copyright law and that they are building something that is fundamentally different from the human labor that it was trained on. But internally, these executives know that what they have built has been built on stolen content and that the products they’ve made are cannibalizing the sources they’ve stolen from and destroying the internet as we know it.