Alisher Usmanov and Mikhail Fridman delisted in what Ireland’s EU presidency called ‘a difficult compromise’ for the bloc
The EU has agreed to remove two Russian billionaires, Alisher Usmanov and Mikhail Fridman, from its sanctions list, while extending restrictions on nearly 3,000 individuals and companies accused of supporting the war on Ukraine for the next three years.
With an end-of-Tuesday deadline looming to preserve the Russia blacklist, the EU’s 27 member states found a compromise that meant delisting the two oligarchs in spite of very few countries wanting this outcome. EU sanctions have to be approved unanimously.
Charity’s head coach ‘shocked’ after Sunderland council leader says it will not support ‘politically charged’ groups
Anti-racism education in some schools will be scrapped after a city council now led by Reform UK ended its 30-year support for the charity Show Racism the Red Card.
Gary Bennett, the former Sunderland AFC captain and the charity’s head coach, said he was “shocked and disappointed” that Nigel Farage’s party had withdrawn vital funding.
Officials say one pilot safely ejected as F-16 believed to have crashed on approach to Spangdahlem after training drill
An F-16 fighter jet assigned to the US air base Spangdahlem in western Germany crashed on Tuesday, the US military said, adding that one pilot had ejected safely and was receiving medical treatment.
The cause of the incident is under investigation, the military said in a statement, with emergency response personnel at the scene of the crash.
It might seem a perfectly natural thing to do. But, on TikTok, a recruiter has expressed her dismay at gen Zs showing up with a takeout drink – and it’s caused a ruckus
Name: Iced coffee.
Age: Colonial troops in Algeria invented a sweetened cold coffee beverage known as Mazagran in around about 1840. However, in Japan, a cold brew was popular among sailors even earlier, in the 17th century.
As diet trends proliferate on social media, it can be hard to work out which are backed by science and which should be ignored. From paleo to keto, raw food to intermittent fasting, each attracts a tribe of ardent followers. Now Daniel Lieberman, professor of biological sciences at Harvard University, has written a book to try to cut through the noise. In Fed Up, he uses his background as an evolutionary anthropologist to scrutinise the evidence, turning himself into a guinea pig in the process and trying various diets. In this podcast, he tells Ian Sample which one has remained part of his routine
2026 is een verschrikkelijk RAMPJAAR voor patat, en dat is niet alleen verschrikkelijk, dat is ook een ramp. Door de Zomer des Doods zijn er minder aardappelen en zijn ze ook nog eens kleiner. Bij de andijviestamppot neemt u gewoon een aardappeltje extra, geen probleem, u bent niet achterlijk, MAAR HOE ZIT HET MET PATAT? Niet best kunnen we u vertellen. Patat wordt namelijk ook kleiner maar niet goedkoper, wat de vraag oproept: is onze patat onze patat nog wel? Spoiler: nee. Zelfs de Franse en Vlaamse frieten zijn niet meer de Franse en Vlaamse frieten. Die lange ranke stengels die we zo smakelijk diep de keel in staken Zijn Niet Meer. Die kleine krengen halen de keel niet eens. Enige, zij het schrale troost: er komen mogelijk wel méér patatjes in uw zak of bak. Ligt aan de (15-jarige) patatbakker van dienst. Bovendien vreet u dan vooral veel neppatat. Friet dus eigenlijk. Nee, even helemáál geen zin in patat nu.
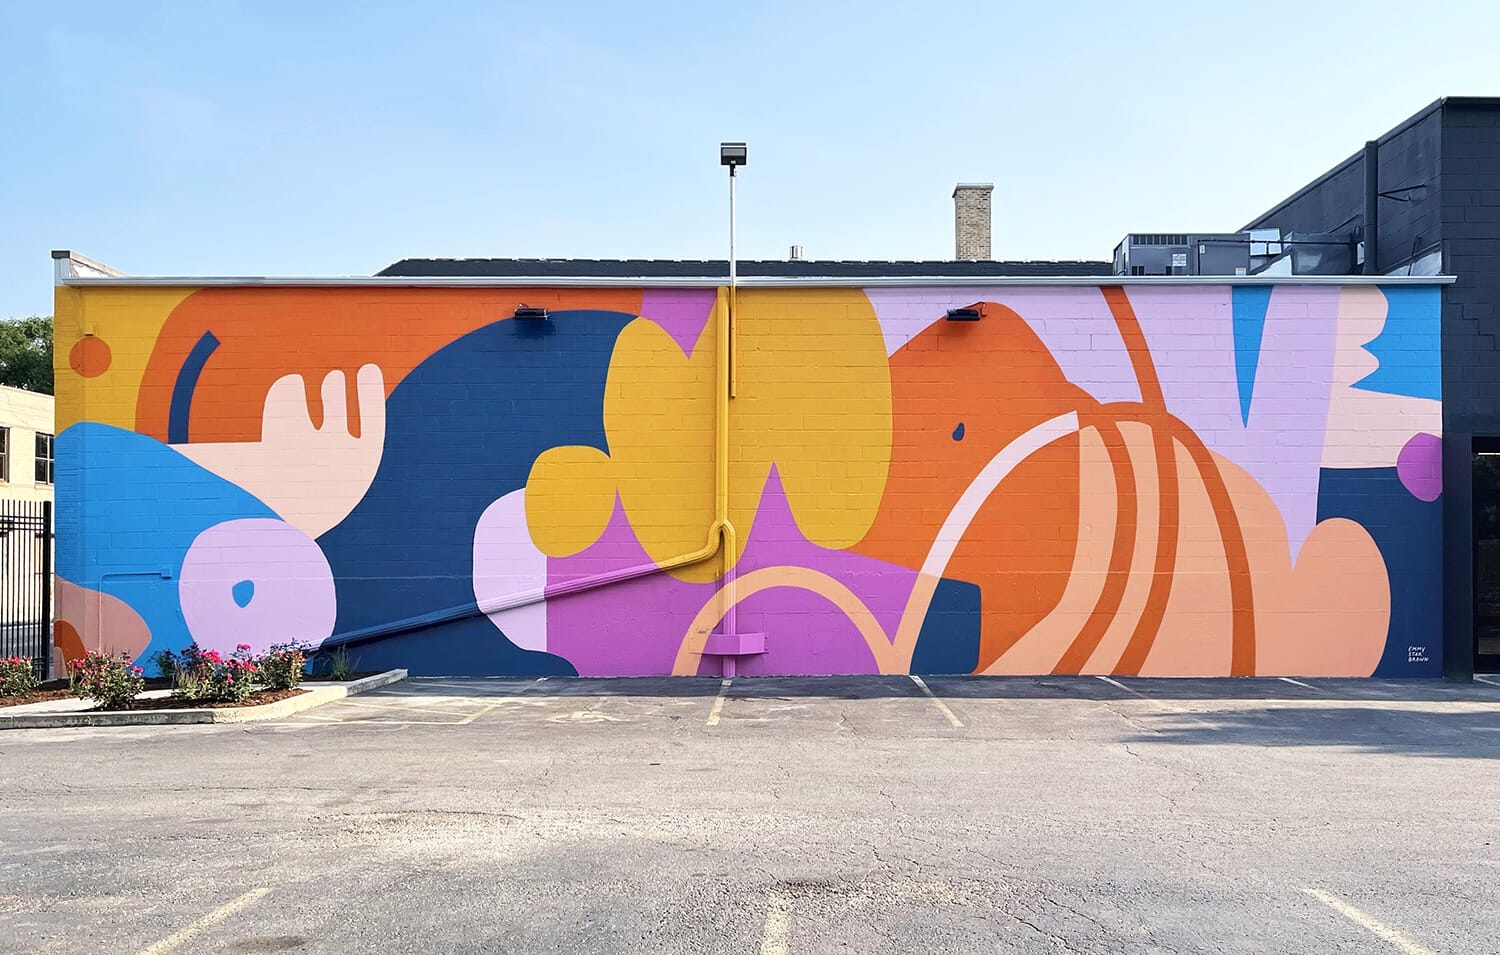
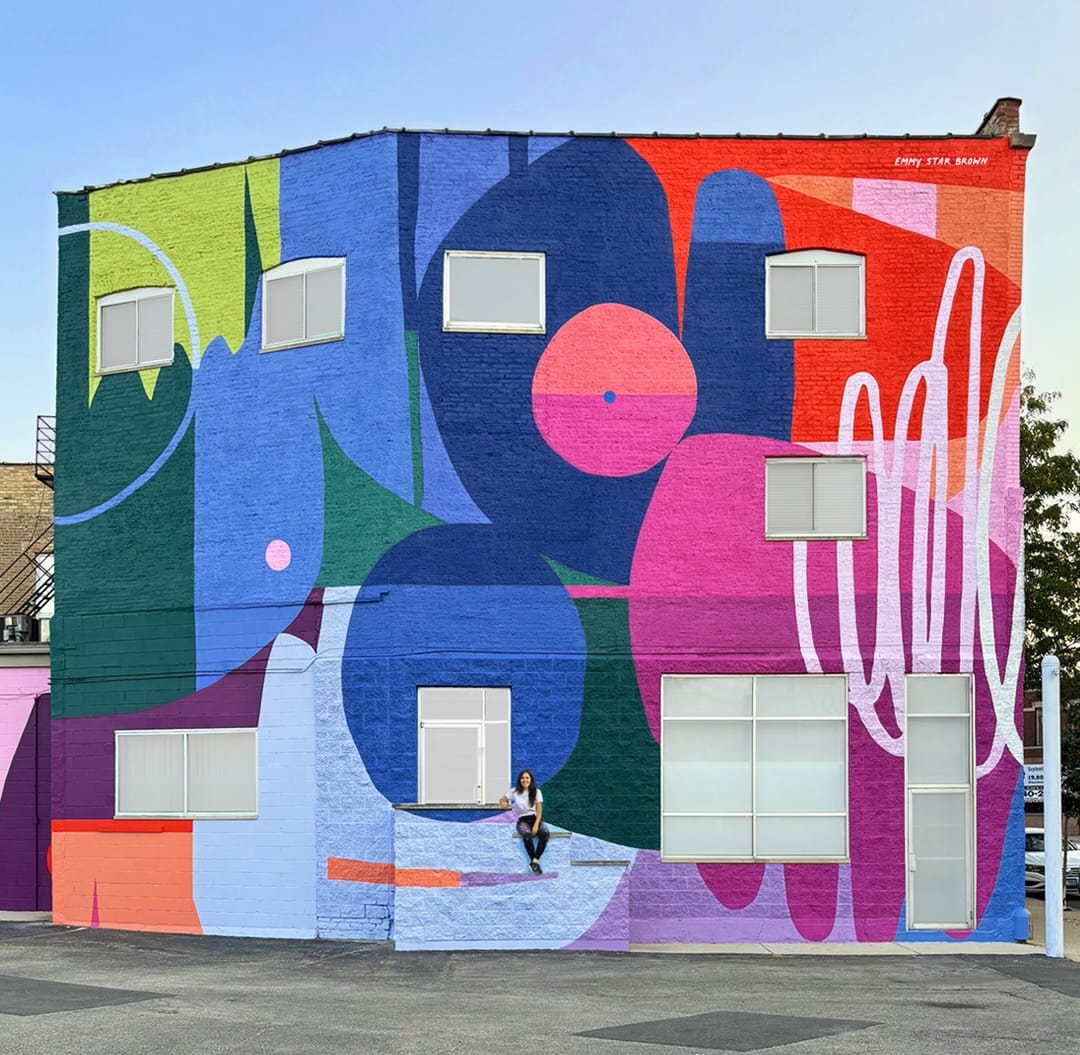
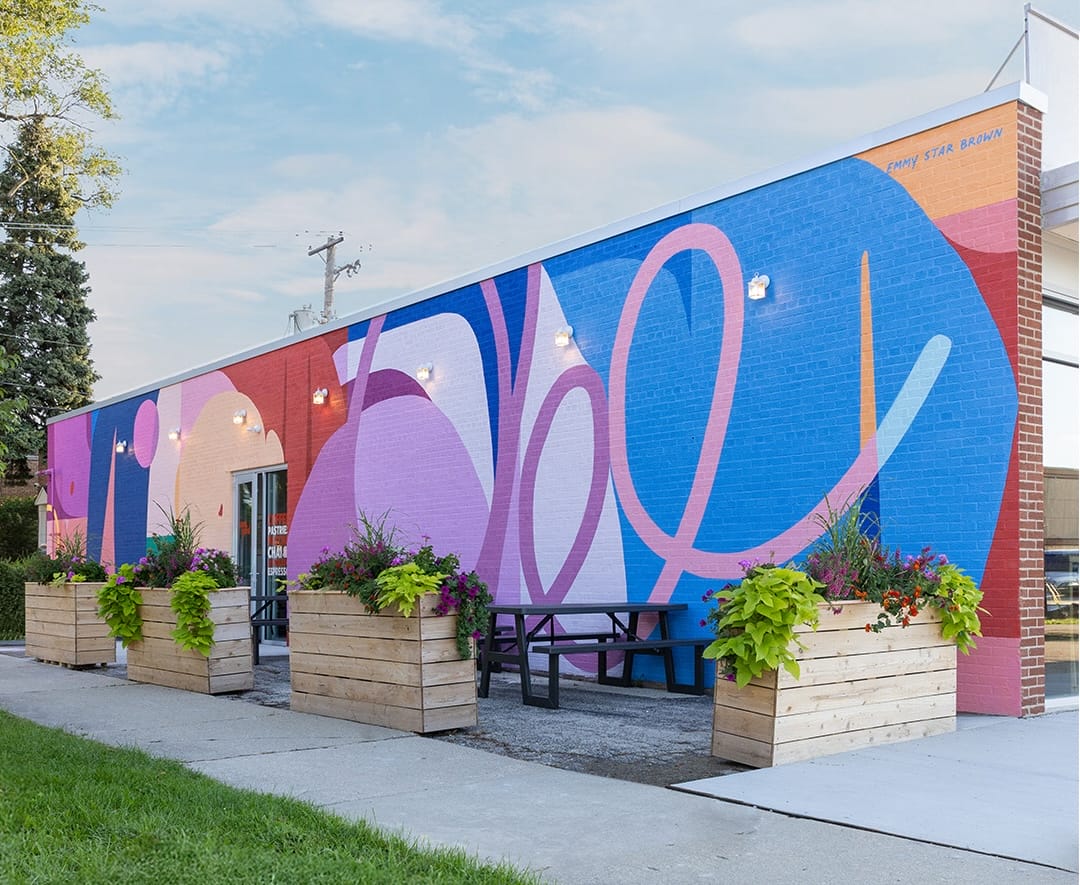
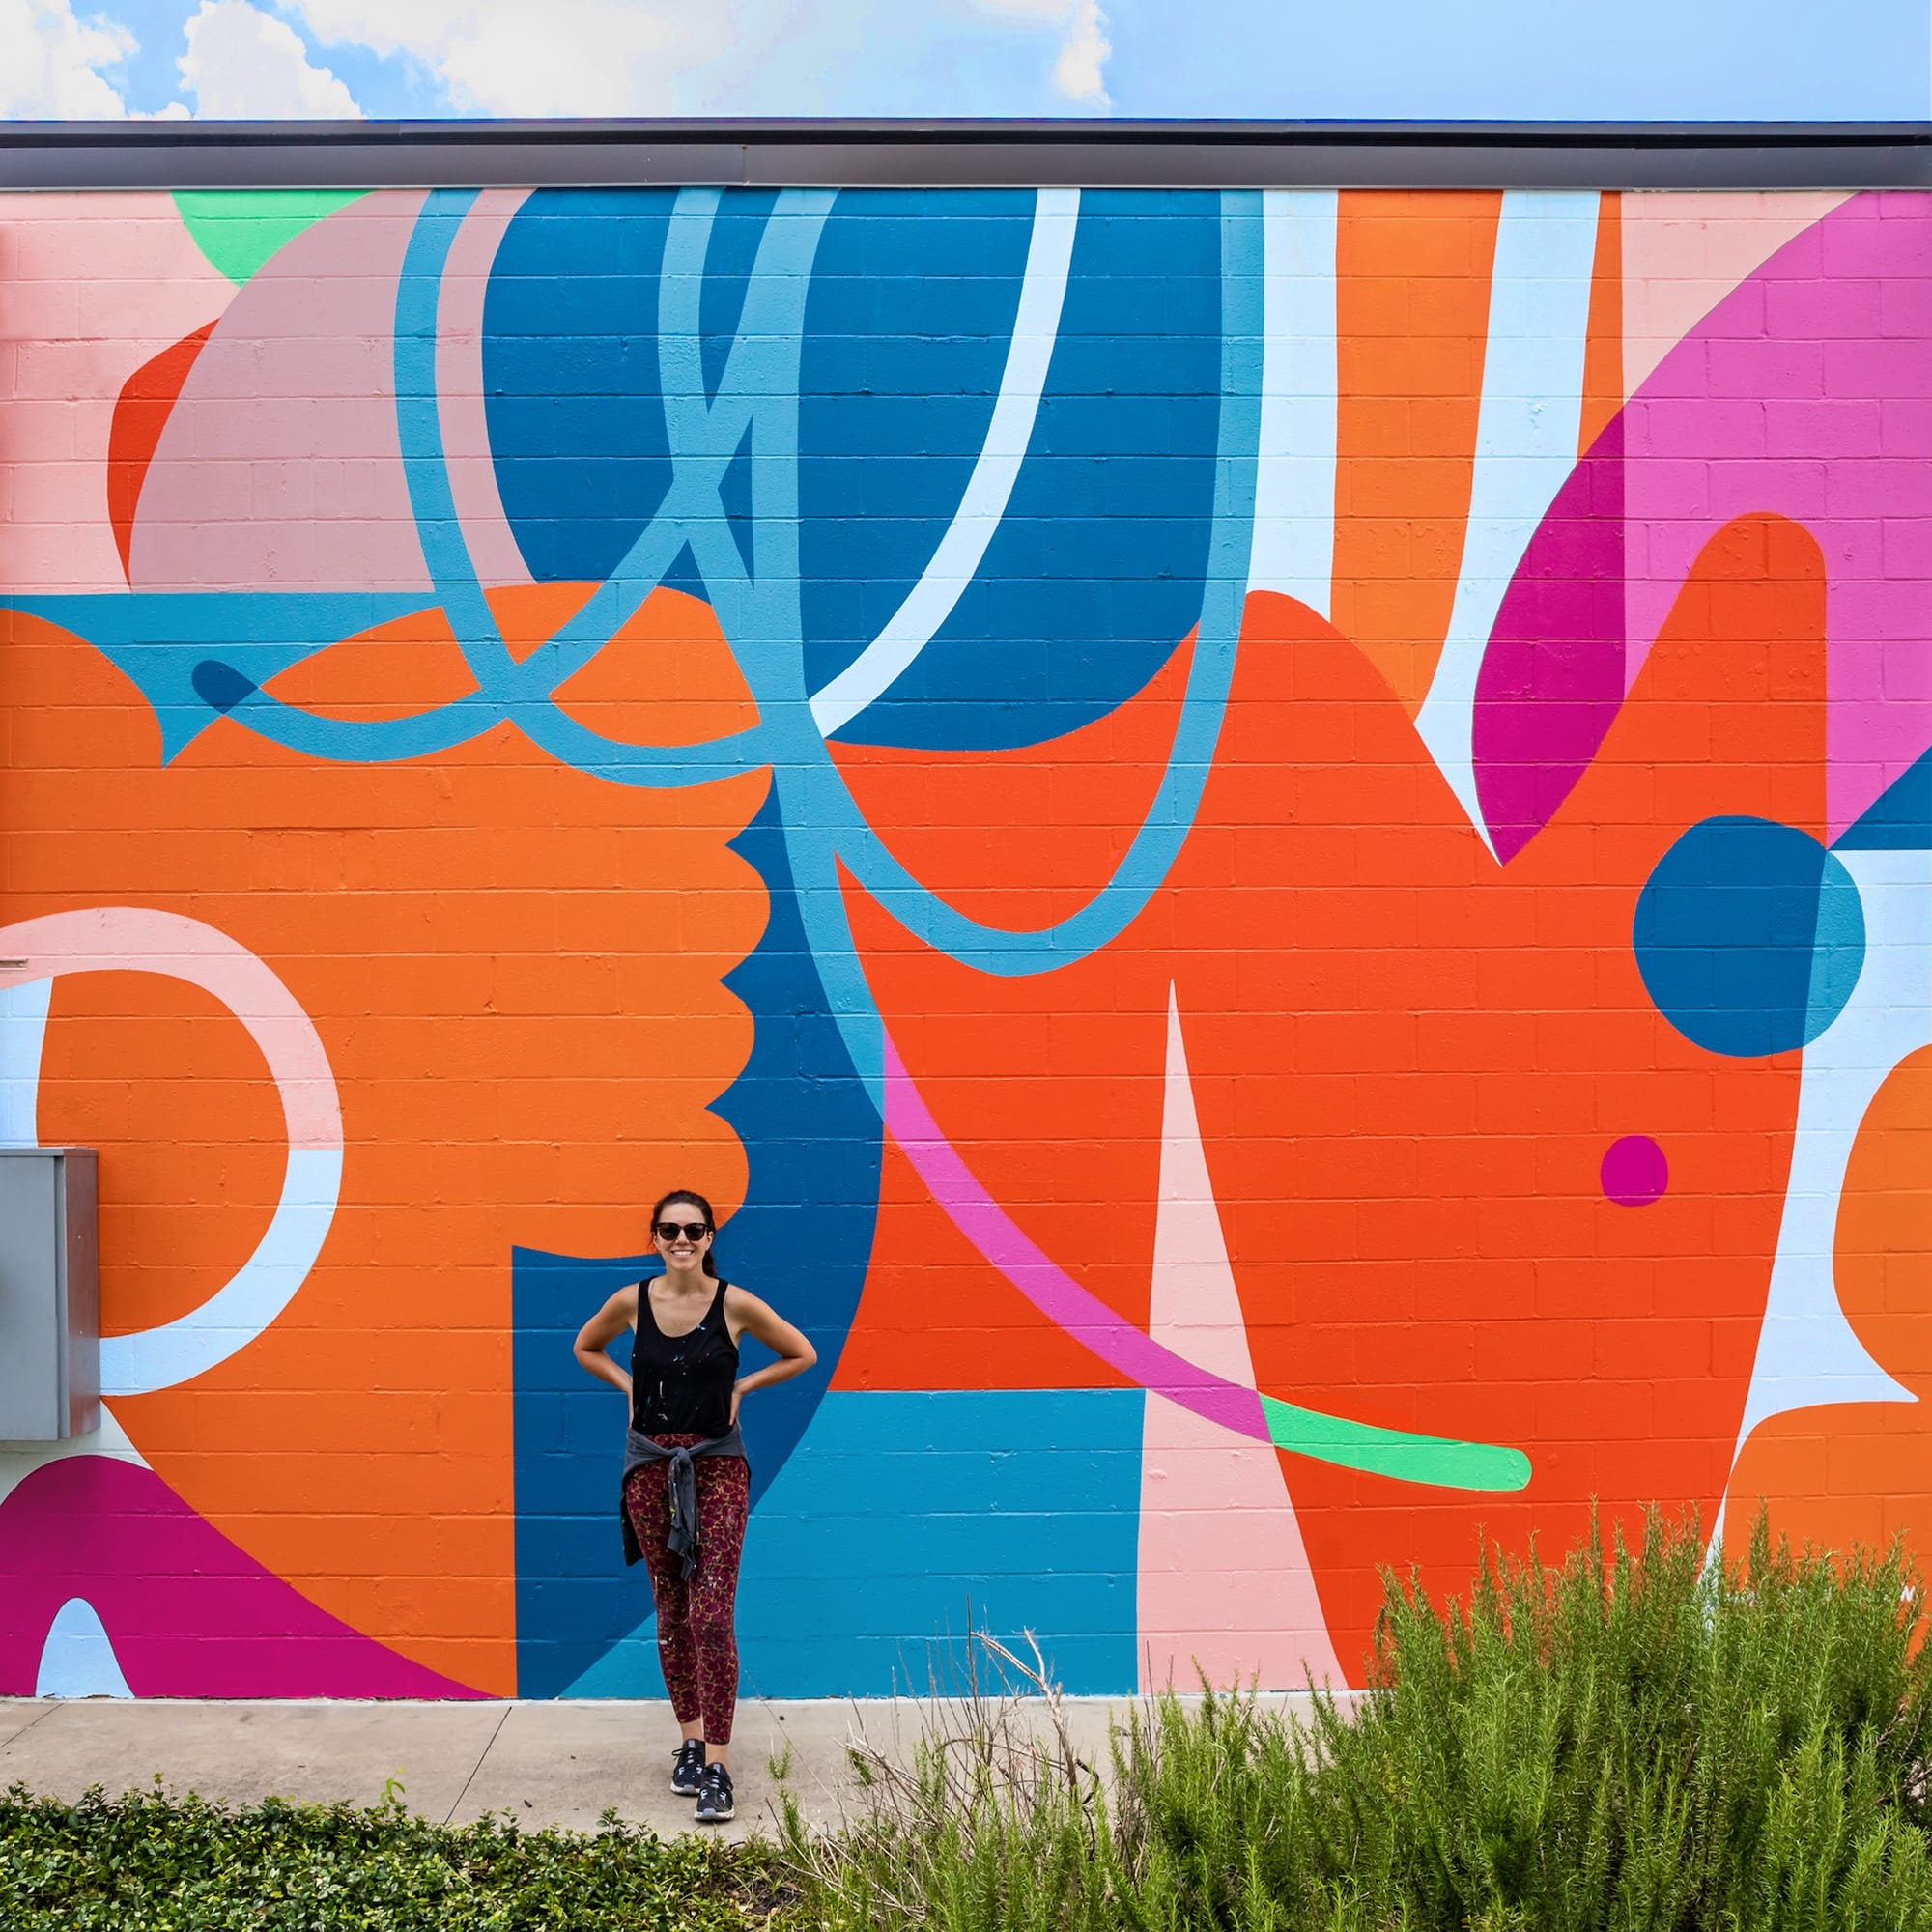
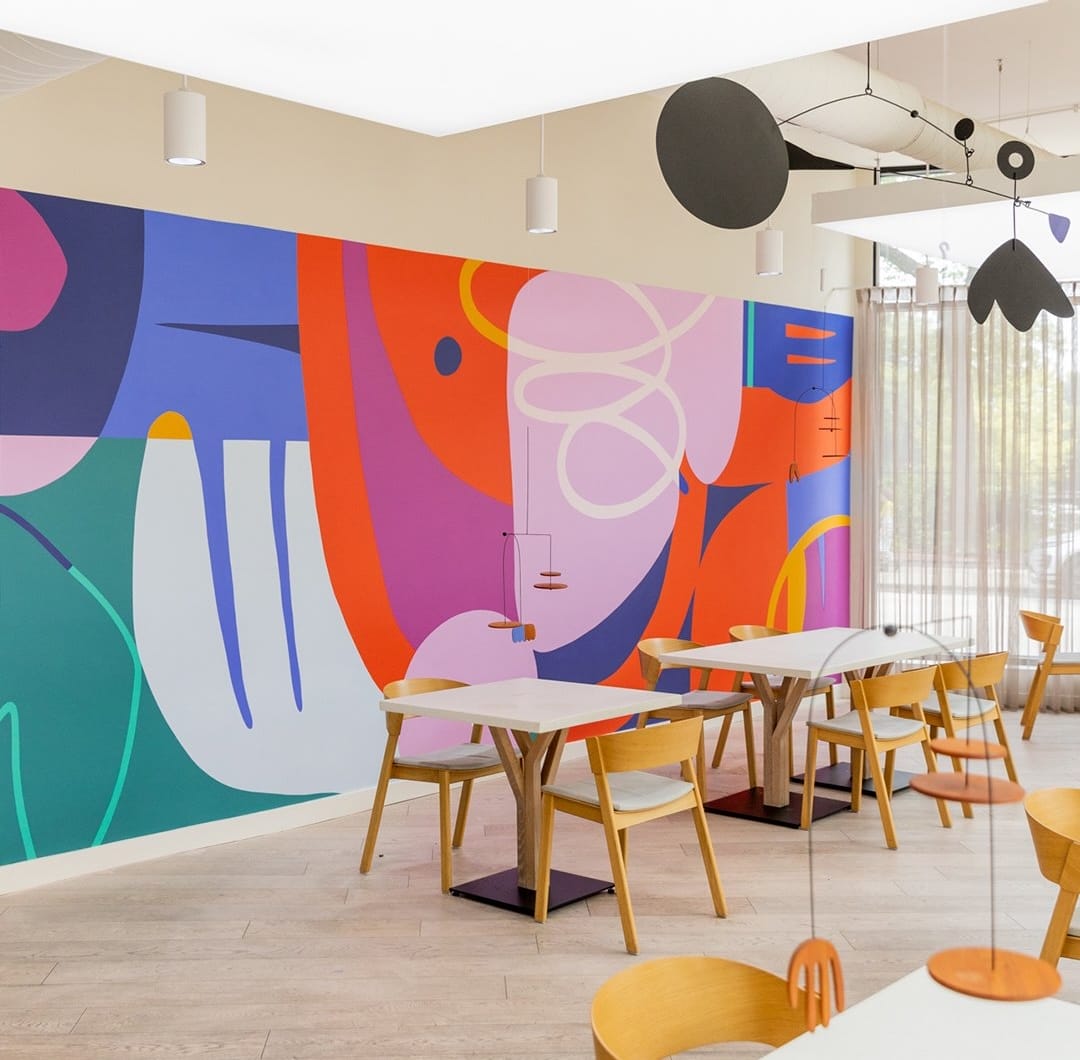
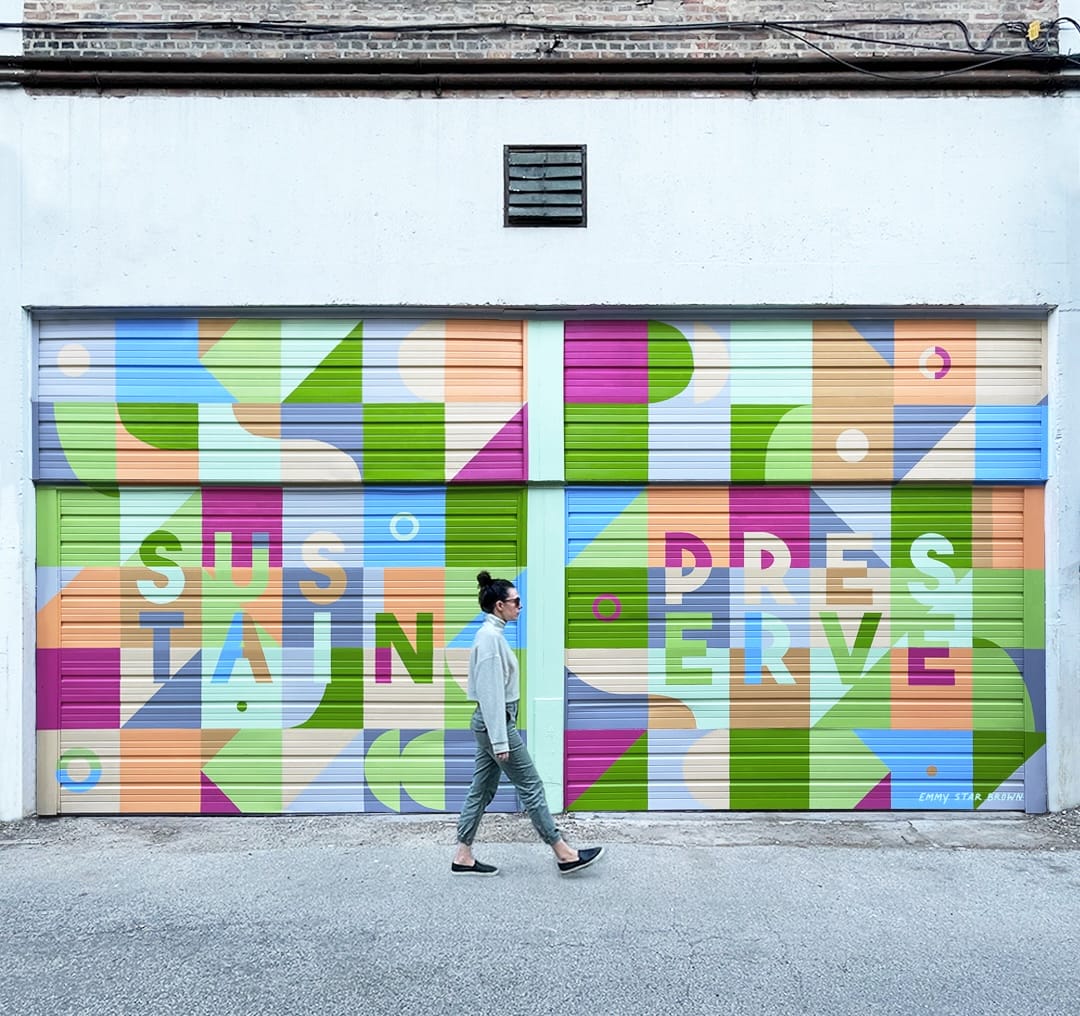
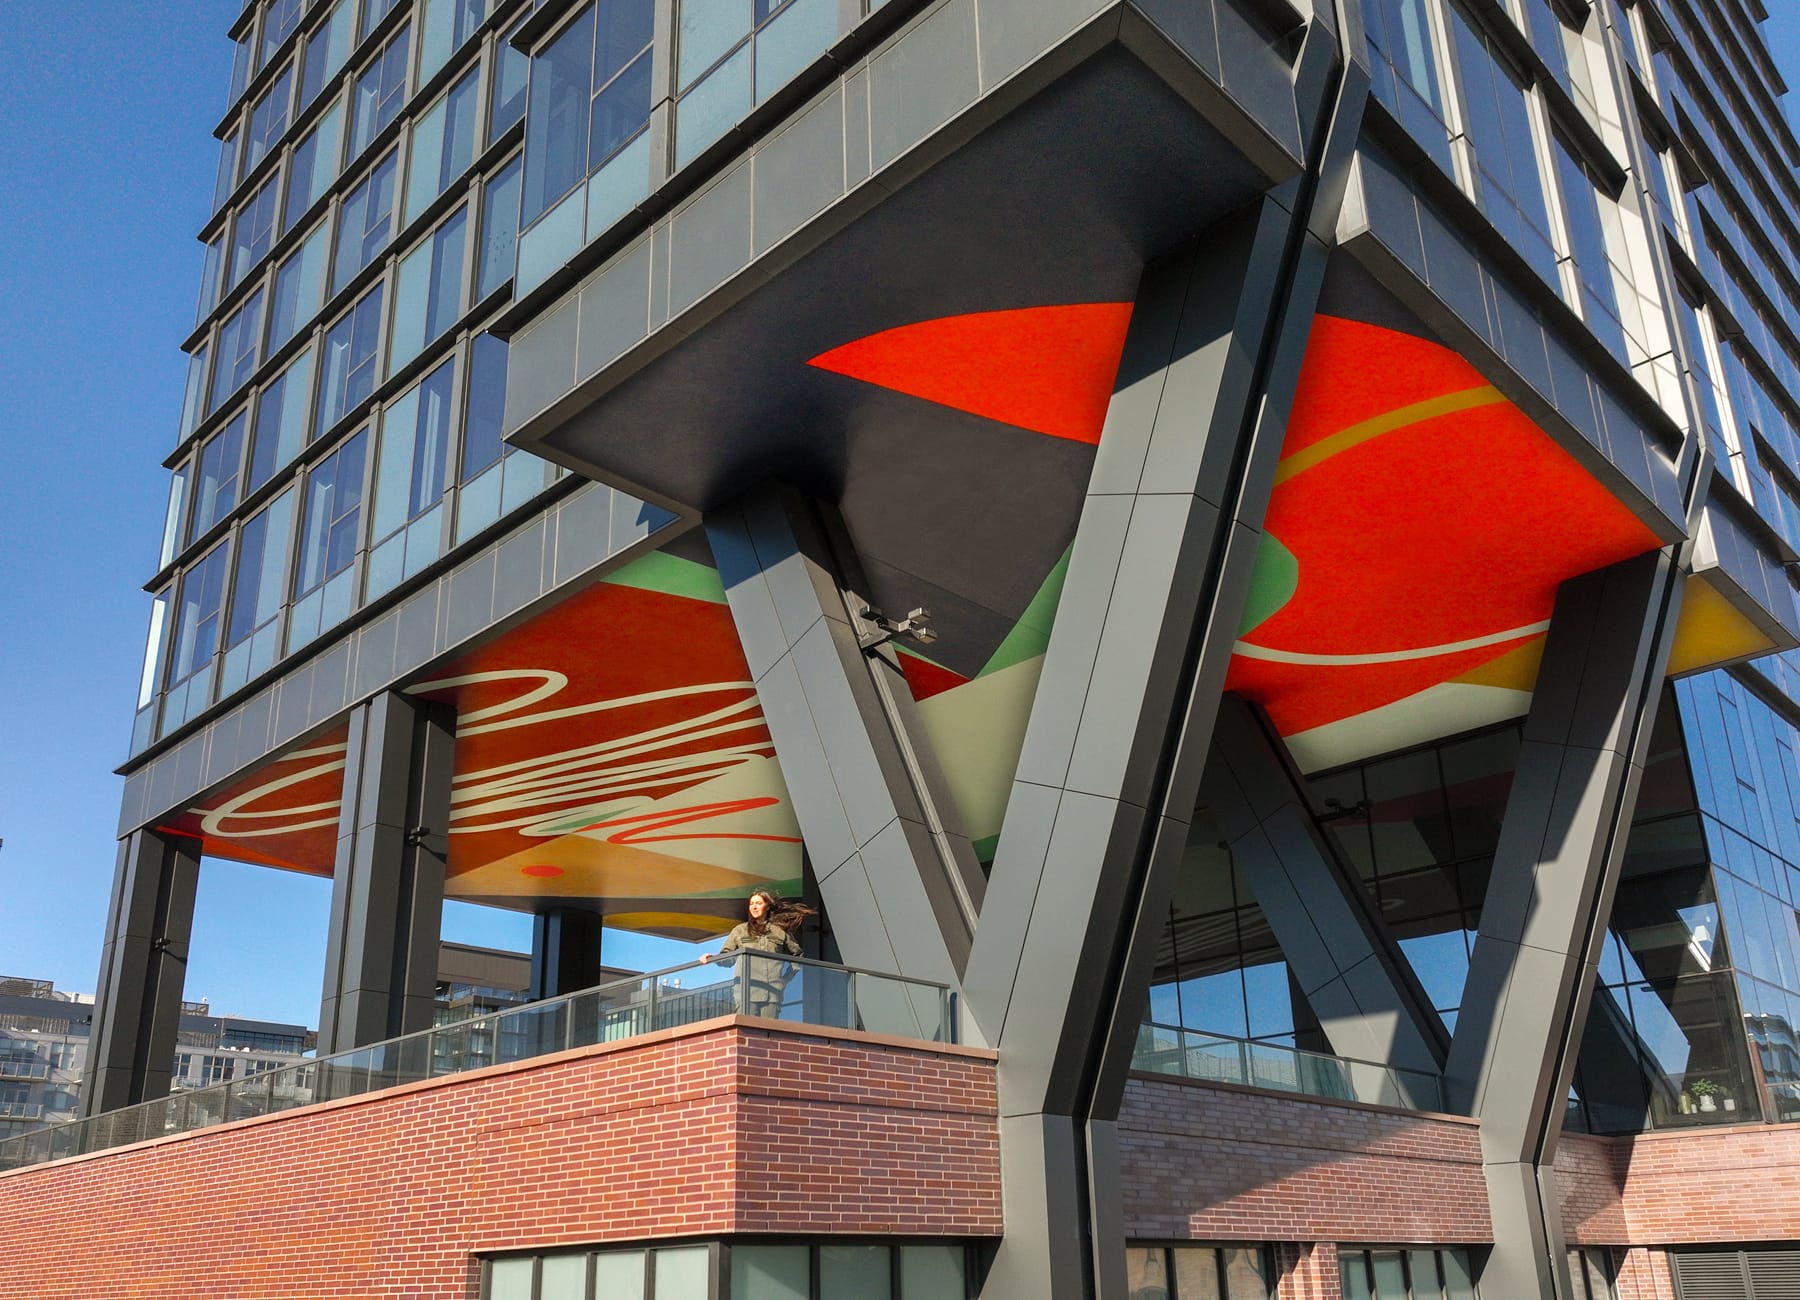
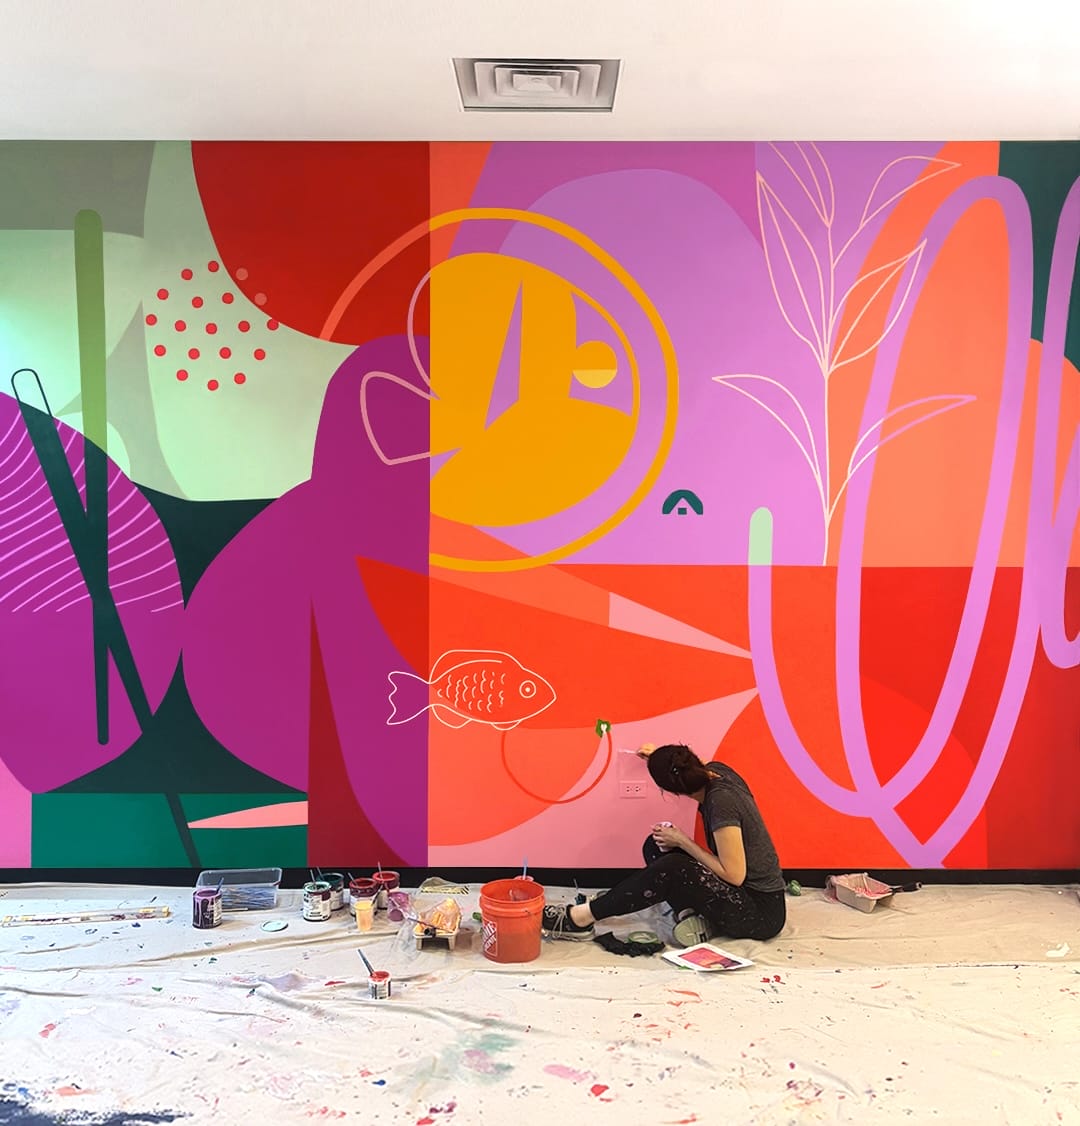
Vibrant, amorphous shapes intersect with squiggles and occasional geometric lettering in the murals of Chicago-based artist Emmy Star Brown. She describes her studio practice as a space where her inner child emerges, paring down her expressions to formal qualities of line, shape, and contrast. In her large-scale installations on urban buildings, which draw on her background in visual communications and advertising, both interior and exterior surfaces transform into energetic, edge-to-edge romps of color.
Brown’s work is currently on view alongside that of Danym Kwon in The Peace of Wild Things at Joy Machine. See more on the artist’s Instagram.
Canyon Groove. What if the grooves on a record were shaped like actual canyons? What would that sound like? “The floor sets the key. The shape of the walls sets the mood. The width sets how long one pass takes, and the depth sets the echo.”
There are folks in macOS/iOS "Contacts" whom I haven't emailed in years. How do I make them stop being the first completion? I would prefer to not have to shitcan their contact info entirely, but I'm sick of almost accidentally emailing the wrong person.
"Remove from previous recipients list" does not fix it. They show up as completions anyway.
UTRECHT (ANP) - Wakker Dier heeft een kort geding aangespannen tegen NS over een geweigerde reclamecampagne. De dierenrechtenorganisatie wilde op stations posters laten ophangen met daarop een koe, een varken, een kip en de vraag: "Zullen we eens een dagje niet 650.000 dieren eten?" Daarmee vraagt Wakker Dier aandacht voor haar jaarlijkse initiatief Eet Geen Dierendag. NS Stations wil de oproep echter niet laten zien.
Over de redenen voor de weigering wil NS nu niet veel kwijt, omdat de zaak woensdag in Utrecht voor de rechter komt. In het algemeen stelt het spoorbedrijf het belangrijk te vinden dat iedereen zich "welkom en prettig voelt" op stations en daarom "zorgvuldige afwegingen" worden gemaakt over welke uitingen wel en niet worden getoond.
Wakker Dier vindt dat het weigeren van de campagne inbreuk maakt op haar vrijheid van meningsuiting en wijst erop dat andere maatschappelijke initiatieven en bijvoorbeeld politieke partijen ook reclame mogen maken op stations.
MADRID (ANP/AFP) - Het Grondwettelijke Hof in Spanje heeft zijn steun uitgesproken voor het opnemen van verduistering onder een amnestie. Hierdoor kan mogelijk de voormalige Catalaanse separatistenleider Carles Puigdemont terugkeren. Hij bevindt zich momenteel in ballingschap.
De amnestie was ingesteld om spanningen na de mislukte poging tot onafhankelijkheid in 2017 te verzachten. Zo'n vierhonderd mensen profiteerden van de maatregel.
Het Spaanse Hooggerechtshof oordeelde dat de amnestiewet niet van toepassing was op personen tegen wie een onderzoek naar verduistering loopt. Hierdoor viel Puigdemont niet onder de amnestie. Puigdemont zou publiek geld hebben gebruikt voor de organisatie van het verboden referendum over de onafhankelijkheid van Catalonië. Hij vluchtte in 2017 naar België.
Tegen het besluit van het Spaanse Hooggerechtshof werd beroep aangetekend bij het Grondwettelijke Hof, dat zijn steun uitsprak voor het toevoegen van verduistering in de amnestiewet.
AMSTERDAM (ANP) - De financieel topman van achterafbetaaldienst Klarna, Niclas Neglen, stapt over naar betaalbedrijf Adyen. Zijn benoeming gaat naar verwachting in op 1 februari, maakte Adyen dinsdag bekend.
Voor zijn overstap naar Klarna was Neglen onder meer financieel directeur voor Europa, het Midden-Oosten en Afrika bij HSBC Private Bank. Eerder werkte hij dertien jaar bij General Electric, waar hij verschillende leidinggevende financiële functies bekleedde binnen meerdere internationale bedrijfsonderdelen.
Eind mei werd bekend dat de toenmalige financieel directeur Ethan Tandowsky zou vertrekken per eind augustus bij Adyen voor een functie buiten de fintechsector. Tandowsky begon in 2016 bij Adyen en was sinds 2023 financieel directeur.
DEN HAAG (ANP) - De Autoriteit Consument en Markt (ACM) mag straks ook overnames en fusies van kleinere bedrijven gaan beoordelen. De Tweede Kamer stemde in met een wet die dat regelt, op initiatief van PRO-Kamerlid Julian Bushoff.
Met de nieuwe wet kan de ACM op eigen initiatief een overname onderzoeken, bijvoorbeeld of een bedrijf niet te veel macht krijgt binnen een sector. Zo krijgt de autoriteit bijvoorbeeld beter zicht op zogenoemde 'killer acquisitions'. Dat zijn overnames van grote bedrijven die kleinere concurrenten overnemen, om de ontwikkeling van een nieuw innovatief idee van een concurrent tegen te houden. Dit gebeurt bijvoorbeeld in de techindustrie door grote spelers.
Nu is het nog zo dat overnames waarbij een van de bedrijven een omzet van 50 miljoen euro per jaar heeft, kunnen worden onderzocht door de autoriteit. Overnames van bedrijven die samen 30 miljoen euro per jaar omzetten, moeten gemeld worden. De drempel van het verplicht melden van een overname wordt met deze wet verhoogd naar 75 miljoen euro omzet voor beide betrokken bedrijven. Een melding is met de nieuwe wet niet per se nodig voor een onderzoek door de ACM.
A high profile hacking group claims it has breached multiple FBI-related services and stolen data “on all FBI employees and applicants.” A representative of the group, called ShinyHunters, told 404 Media the data includes FBI agents’ names, home addresses, phone number, and information on their spouse.
The data breach could be massively significant and may have all sorts of national security and counterintelligence implications. Criminals from the same ecosystem as ShinyHunters have previously used hacked data like phone records to track, intimidate, and harass the FBI agents investigating them. The highly sensitive data could also be a boon to foreign intelligence agencies who want to better understand how one of the most important law enforcement and intelligence agencies in the U.S. operates. And if the data fell into the hands of more criminals, FBI agents and their spouses could face serious threats to their safety.
“We hacked the FBI. We hold data on all FBI employees and applicants,” the representative of the group told 404 Media.
💡
Do you know anything else about this hack? I would love to hear from you. Using a non-work device, you can message me securely on Signal at joseph.404 or send me an email at joseph@404media.co.
The representative provided 404 Media with a sample appearing to contain the personal data of 5,000 FBI employees. That data included an alleged address, phone number, date of birth, and in some cases details on their spouse.
404 Media put some of the sample phone numbers into open source intelligence tool OSINT Industries and found they did correspond to people with the same name as listed in the sample file. 404 Media also searched some of the records through compromised data tool Darkside, made by cybersecurity company District 4. That revealed some of the phone numbers are associated with U.S. Department of Justice personnel.
ShinyHunters also defaced the FBI jobs website on Tuesday. That defacement says, “this site has been seized by ShinyHunters,” which is an obvious nod to the seizure notices the FBI and other law enforcement agencies often put on sites after taking them down. The representative said ShinyHunters carried out the hack on Monday night. At the time of writing, the FBI jobs website says, “Apply.fbijobs.gov and the Special Agent Applicant Portal are currently unavailable.”
The defacement adds, “All FBI data was compromised including PII/PHI [personally identifiable information and protected health information] on incumbent and former FBI employees and all applicant information. We have a lot more than we claim here.”
The announcement ended with another obvious jibe at the administration, this time mocking President Trump’s Truth Social post style: “Thank you for your attention to this matter.”
The FBI did not immediately respond to a request for comment.
The representative said ShinyHunters said the group used a zero day exploit in an Oracle product called PeopleSoft. From there, the group managed to access AWS GovCloud servers and downloaded data. The representative said the exfiltrated data totalled between two and three terabytes.
Typically, ShinyHunters hacks targets and then attempts to extort them. The group threatens to publicly release more compromised data if the victim organization or company doesn’t pay a hefty fee. Obviously, it is unlikely that the FBI would ever pay a ransom like this.
When asked if ShinyHunters was going to attempt to extort the FBI, the representative said, “what we plan to do is not something I’d call extortion, maybe coercion.”
“This is not financially motivated,” they added.
Update: this piece has been updated to include more information from previously compromised data.
Last week, Meta executives announced that its much-hyped AI agent, Muse, had a new feature: It could call businesses for you to do things like make a restaurant reservation or a haircut appointment. But in reality, Meta is testing having these calls being made by human beings in call centers, 404 Media has learned.
“We just expanded the @muse beta for outbound calls to US businesses,” Ryan Fox, the principal engineer on Muse posted on X on Sept. 16. Alexandr Wang, Meta’s chief AI officer, posted “we’re expanding our phone beta for muse!”
Internally, however, the company announced the features to employees and said that it had “added a human agent layer for calls to get completed,” and that “Muse human agent calls [sic] is ready for company dogfooding,” or testing.
“Muse doesn’t just dial a number. It calls a business on your behalf, handles the conversation, completes your request, and reports back with a transcript and a summary,” the internal message board post to employees, seen by 404 Media, reads. “It also no longer works alone. Muse is now able to hand requests to a trained human agent, who places the call and works it through.”
“This is still a confidential, pre-launch product,” the post adds. “Please don’t share it, or anything it producers, with anyone outside the company.”
Once again, a core feature of a major piece of AI technology will actually just be people working in a call center, doing work that a company says AI is doing. It is not clear how often or when a call is routed to a so-called “human agent,” and when a call is done exclusively by AI.
💡
Do you work for Meta or know anything more about Muse? I would love to hear from you. Using a non-work device, you can message me securely on Signal at jason.404. Otherwise, send me an email at jason@404media.co.
The fact that human beings are involved in the call raised questions among employees, who wondered both about the privacy implications of sharing people’s call requests with other human beings as well as the perception that its AI assistant wasn’t advanced enough to do calls on its own.
“Not sure what I am missing here but why is this a ‘feature?,’ one employee wrote on Meta’s internal message board for workers. “This has potential for so much negative PR. It could portray us as ‘their AI is not good enough so they still need humans’ kind of coverage for this launch.”
That Meta is at least sometimes letting human beings read users’ chats and make phone calls on their behalf is part of a time honored tradition in which companies launch an AI product, claim that it is AI, only for it to be later learned that human beings are doing some or all of the work. And it is the latest example of a tech giant passing potentially highly sensitive information to human beings; it is easy to imagine someone asking Muse to make a sensitive doctor’s appointment, for example, and the user not knowing that a human being might make that call.
In internal communications seen by 404 Media, Meta suggested to employees that potentially sensitive information shared by the user with AI — and then passed to human contractors — was still safe because the contractors had undergone “a lot of training to make sure all your data is safe and secure.” An employee commented that the training “is not a [security] mechanism.”
“This is absolutely going to create a ton of outcry if we publicly launch this as default-on. It will kill all the goodwill and organic press we’re getting from early adopters,” they wrote. “Please think about how the headlines will scream ‘Meta uses humans behind the scenes to make calls’ or ‘Muse AI is actually independent contractors’ and result in a ton of bad press about the privacy and security of our data handling […] please PLEASE do not release this as-is and at least make this a user preference if we absolutely must launch this. Please.”
Other employees who had tested the system said that it was a “bad bad idea,” and that they were not made aware that a human being did the call for them until after the call had been made: The tester “was not made aware of the caller being human and was only told after,” one employee wrote. “So they were concerned with information that they shared with the assumption that it is the secure AI which is making the call. Even with clear indication of human calling, I can think of many scenarios where I wouldn’t be comfortable with this and I am not positive about how our users will react to this.”
Various Meta employees and regular users have posted about Muse’s ability to make phone calls, and their experience with it. Ravid Shwartz Ziv, who does AI research at Meta, posted on X that “this week, Muse called customer service on my behalf. It navigated the phone tree, waited on hold, spoke with a human rep, and resolved the issue (worked great!). The crazy thing for me (besides that it works) is that the rep didn’t blink. Talking to a bot was completely natural to them.” Others have posted that the call function didn’t work, or that the person on the other end hung up on the agent (some have said that Muse did what it was supposed to do).
“Internal testing, aka dogfooding, is core to the product development process. While the response from employees has been overwhelmingly positive, the entire point is to get feedback so we can implement safety and privacy protections and improve features before we release them publicly,” a Meta spokesperson told 404 Media. “We’re working with merchants to continue improving this potential calling feature, and will only roll it out when it's ready and with the proper disclosures.”
Frankrijk stelde een voorwaarde voor verlenging van de sancties tegen Rusland, waarover dinsdagavond een besluit moest worden genomen. Letland was het daar niet mee eens. In een „moeilijk compromis” worden twee Russen van de lijst gehaald en wordt de termijn van de sancties verlengd tot drie jaar.
Een 44-jarige man is aangehouden op verdenking van betrokkenheid bij de moord op de 50-jarige Schiedammer die begin april in Frankrijk werd doodgeschoten, dat meldt de Franse krant Le Parisien. De Nederlandse politie kan dit niet bevestigen. De Franse krant meldt daarbij dat, enkele uren na de schietpartij, tien kilometer verderop een tweede slachtoffer werd gevonden in een uitgebrande auto. De twee moorden zouden verband met elkaar houden.
Serial Microsoft zero-day leaker NightmareEclipse has found another way to mess with Windows Defender, this time by stopping the antivirus from updating itself. The security researcher, also known as Abdelhamid Naceri, released a proof-of-concept dubbed “BigDiskBuster” that is designed to prevent Microsoft Defender Antivirus from installing platform and security intelligence updates. “Made a funny tool, completely denies defender from updating so you're stuck with your current version if the tool is running in the background,” NightmareEclipse said. The researcher describes BigDiskBuster as similar to their earlier “UnDefend” tool and claims it works on all supported versions of Windows, although they admit the current PoC is “a bit buggy and needs some rewritting [sic].” That compatibility claim has not been independently verified. The trick doesn't disable Defender. Instead, the PoC waits for an update to start, then tries to fill up the drive so there isn't enough space for it to finish. The code does this by creating hidden temporary files sized to consume the drive's free space, spinning up additional threads as needed to claim more. Once it detects that the Defender update has failed, it closes the files and returns the space. BigDiskBuster also opens Microsoft's Malicious Software Removal Tool executable, MRT.exe, in a way that restricts other processes' access to the file while the handle remains open. The result, according to NightmareEclipse, is that Defender stays stuck on its current platform and security intelligence versions as long as the tool keeps interfering with updates. A screenshot published alongside the PoC shows Windows Security reporting that a protection definition update failed with error 0x80070643. That's a generic installation error, however, and isn't evidence on its own that BigDiskBuster is at work. Leaving Defender stuck on old security intelligence is obviously less than ideal. The antivirus may still be running, but preventing it from receiving Microsoft's latest threat definitions could leave it less able to identify newly detected malware. The steady stream of bugs from NightmareEclipse comes amid a very public spat between the researcher and Microsoft over the company's vulnerability disclosure process. The researcher began dumping Windows zero-days and proof-of-concept code in April, claiming Microsoft had mistreated them and cut off their access to its vulnerability reporting system. Redmond wasn't exactly thrilled. In May, Microsoft criticized NightmareEclipse for releasing vulnerabilities without giving it a chance to fix them first, saying none of the initial bugs had been reported through its official channels. The company also invoked its Digital Crimes Unit, saying it would pursue cases against people engaged in malicious activity or enabling cybercrime – language widely interpreted as a threat of legal action against the researcher. That went down about as well as you'd expect with the security community. Microsoft subsequently walked back the rhetoric, saying it had “no intention to pursue action against individuals conducting or publishing security research.” By then, however, NightmareEclipse's earlier GitHub account had also been taken down, along with access to Microsoft's vulnerability reporting portal. The peace offering didn't end the feud. NightmareEclipse continued releasing Windows exploits, including RoguePlanet in June, LegacyHive in July, ShieldBreak in August, and ShieldCrash in September. Several of the researcher's earlier zero-days have since been patched by Microsoft, while some were exploited in the wild after their public release. BigDiskBuster is a rather different beast. Rather than providing an obvious route to SYSTEM privileges, it interferes with one of the basic things antivirus software needs: updating itself. There’s currently no indication that BigDiskBuster has been used in real-world attacks, and NightmareEclipse's claim that it works across all supported Windows versions remains unverified. Redmond has not responded to The Register's questions. In the meantime, its Nightmare apparently shows no sign of ending.®