Liam Lawson enjoyed a solid first day back with Racing Bulls in Azerbaijan, but Arvid Lindblad's FP2 ended prematurely after contact with the barriers brought out the red flags.
Mercedes appear to be the ones to beat in this weekend’s Azerbaijan Grand Prix, but it was George Russell rather than championship leader Kimi Antonelli who was the stronger of the Silver Arrows. Can he build on that strong start to outscore his team mate and drag himself back into title contention?
With Haas yet to confirm their line-up for 2027, we’ve rounded up the drivers most likely to land a seat at the American team.
Over-by-over updates, second ODI from 12.30pm BST
1st over: Sri Lanka 1-0 (Nissanka 1, Kamindu Mendis 0) Headingley is usually a great place to bat, so Sri Lanka will probably want upwards of 300. Fifty overs is a long time*, which means Kamindu Mendis can take a bit of time to get his eye in. He plays out five consecutive dot balls during an accurate opening over from Archer.
* Drink
Continue reading...Senior Iranian officials say Washington has four to five days to respond to its conditions for reopening the strait
The UK foreign secretary, Ed Miliband, has met his Iranian counterpart, Abbas Araghchi, for the first time in New York amid warnings from senior Iranian security officials that the US has four to five days to respond to its conditions for reopening the strait of Hormuz.
The previously unknown apparent deadline was specified by Mohsen Rezaei, the secretary of the supreme national security council, in a TV interview on Wednesday evening, and it is unclear what action Tehran will take if the US does not respond to Iran’s preconditions for reopening the vital waterway.
Continue reading...Dozens of delegates left the room in support of Palestine as the Israeli prime minister walked to the podium on Thursday. Other delegates clapped and chanted 'Am Yisrael Chai' or 'the people of Israel live' in support of the prime minister
Continue reading...
You have no choice, Katrien De Blauwer
One day since yesterday, Benjamin Deroche (because)
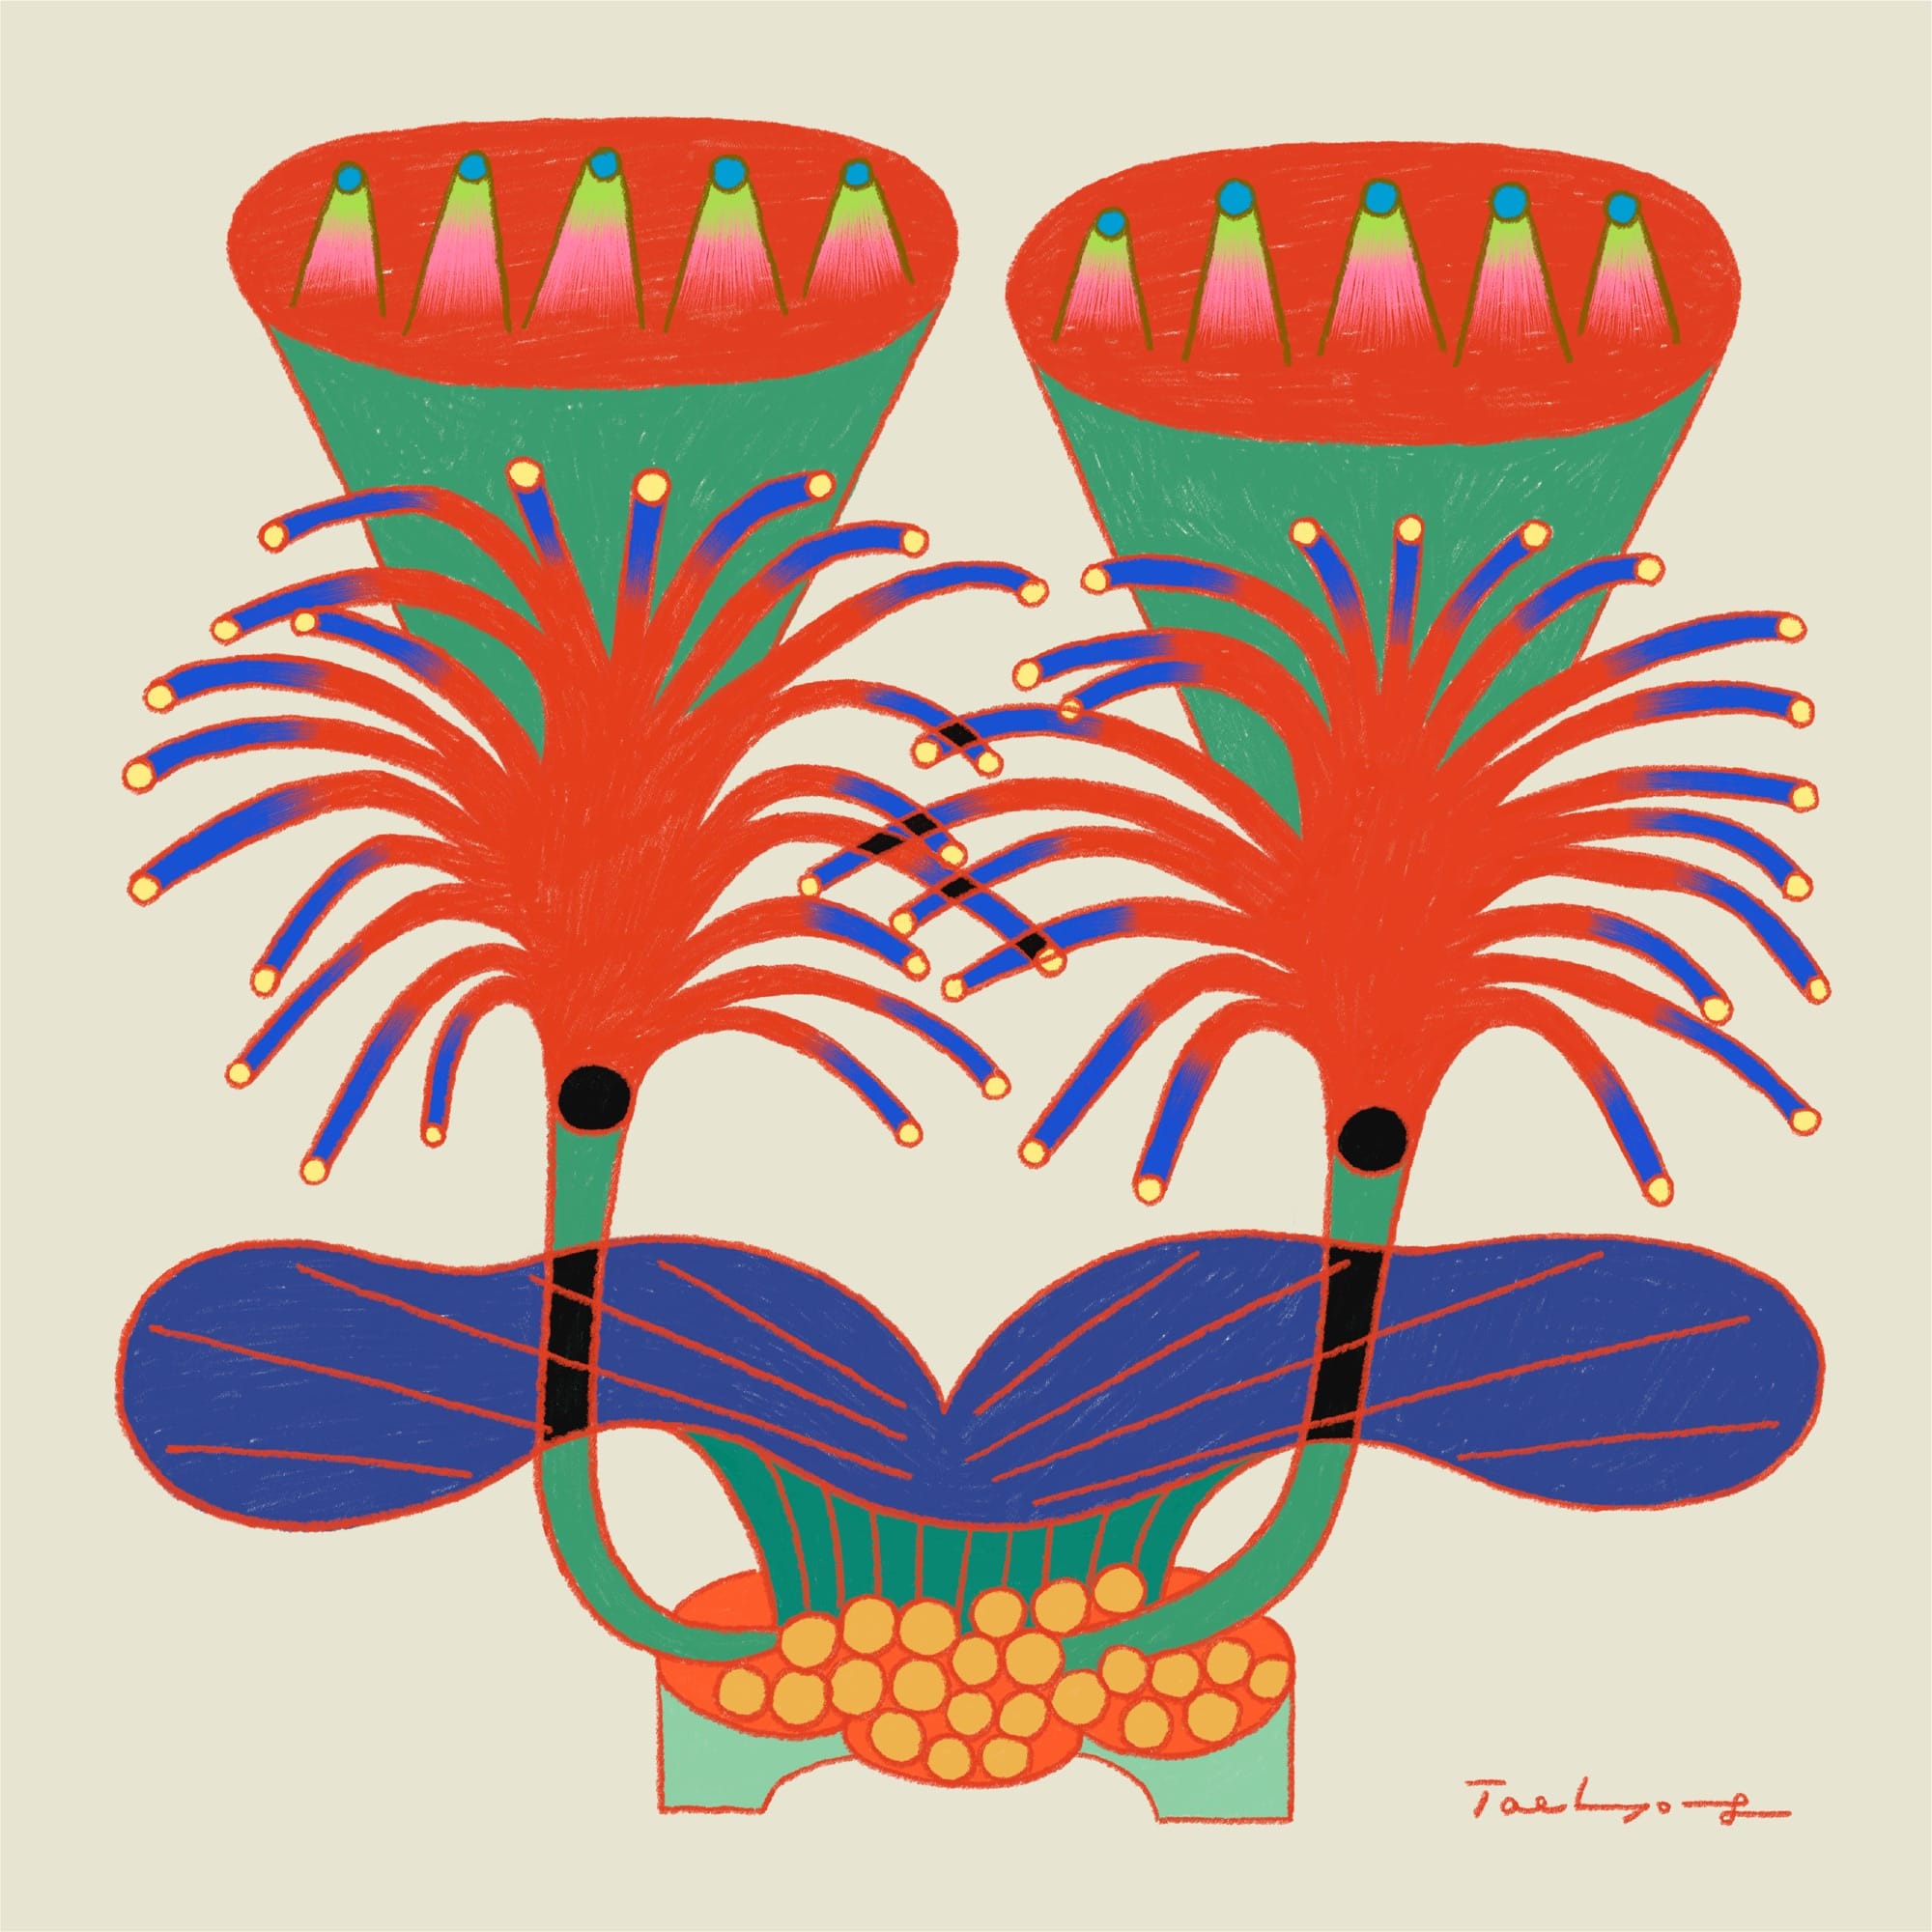
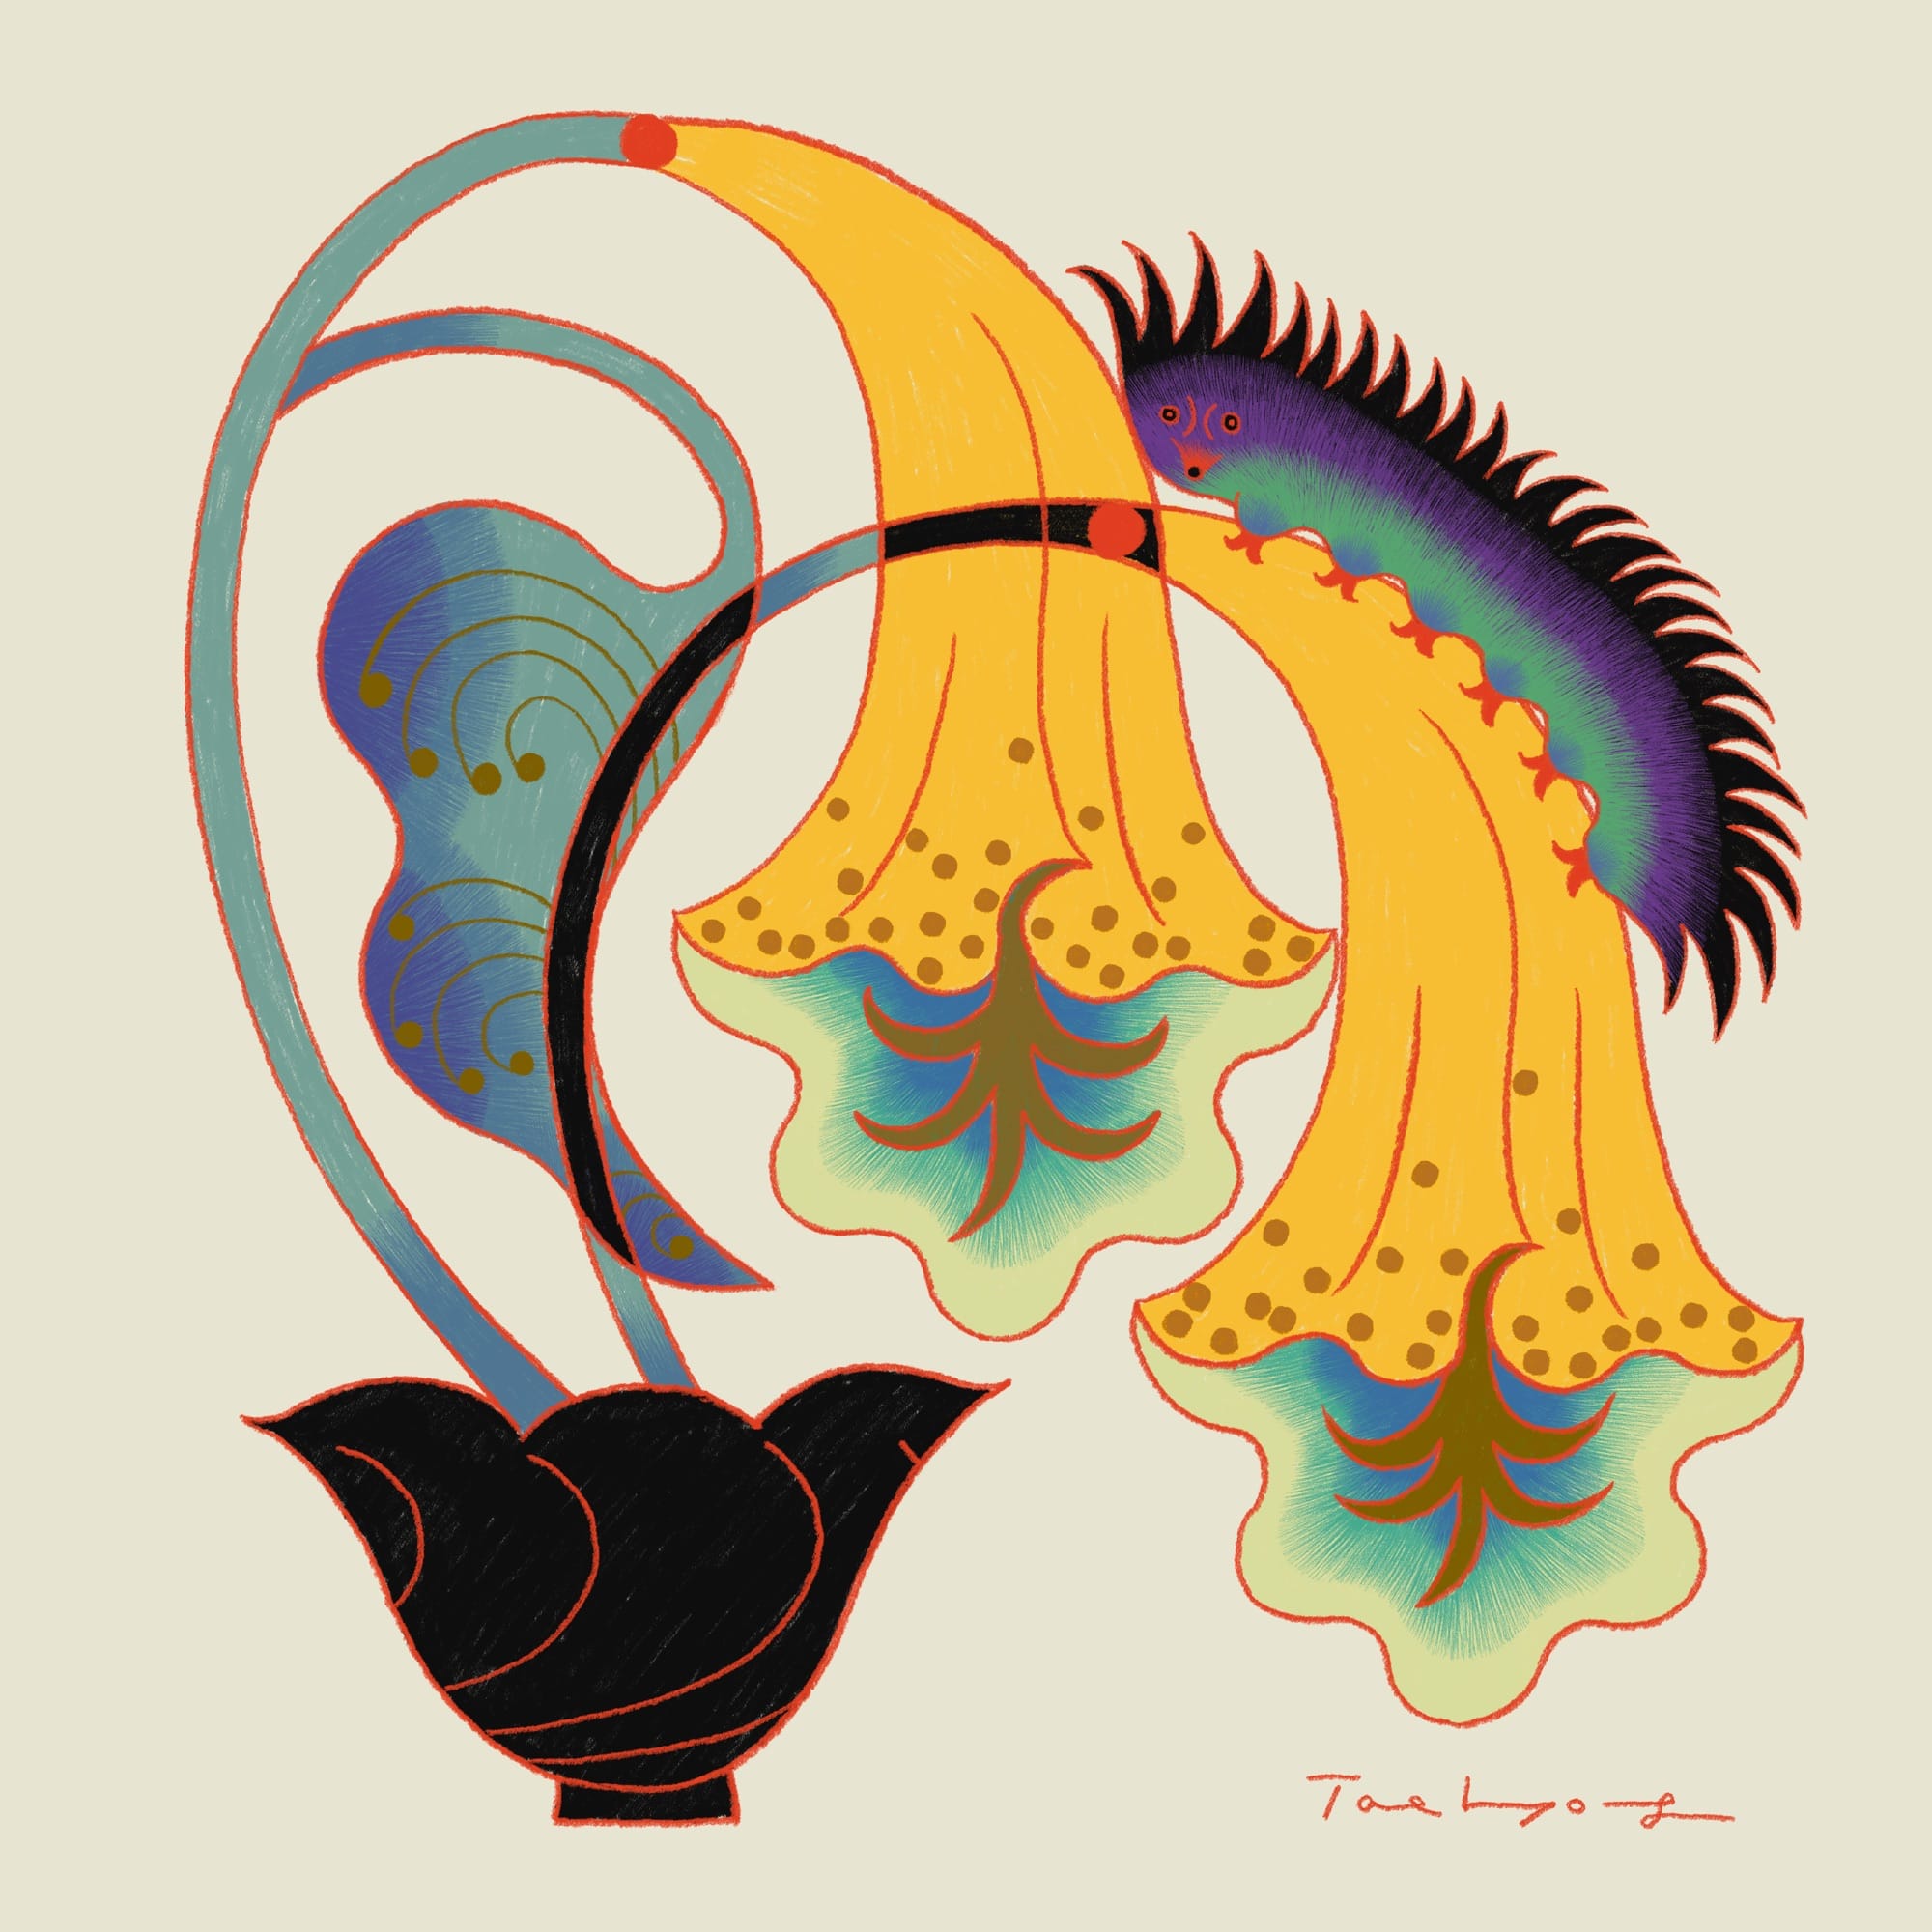
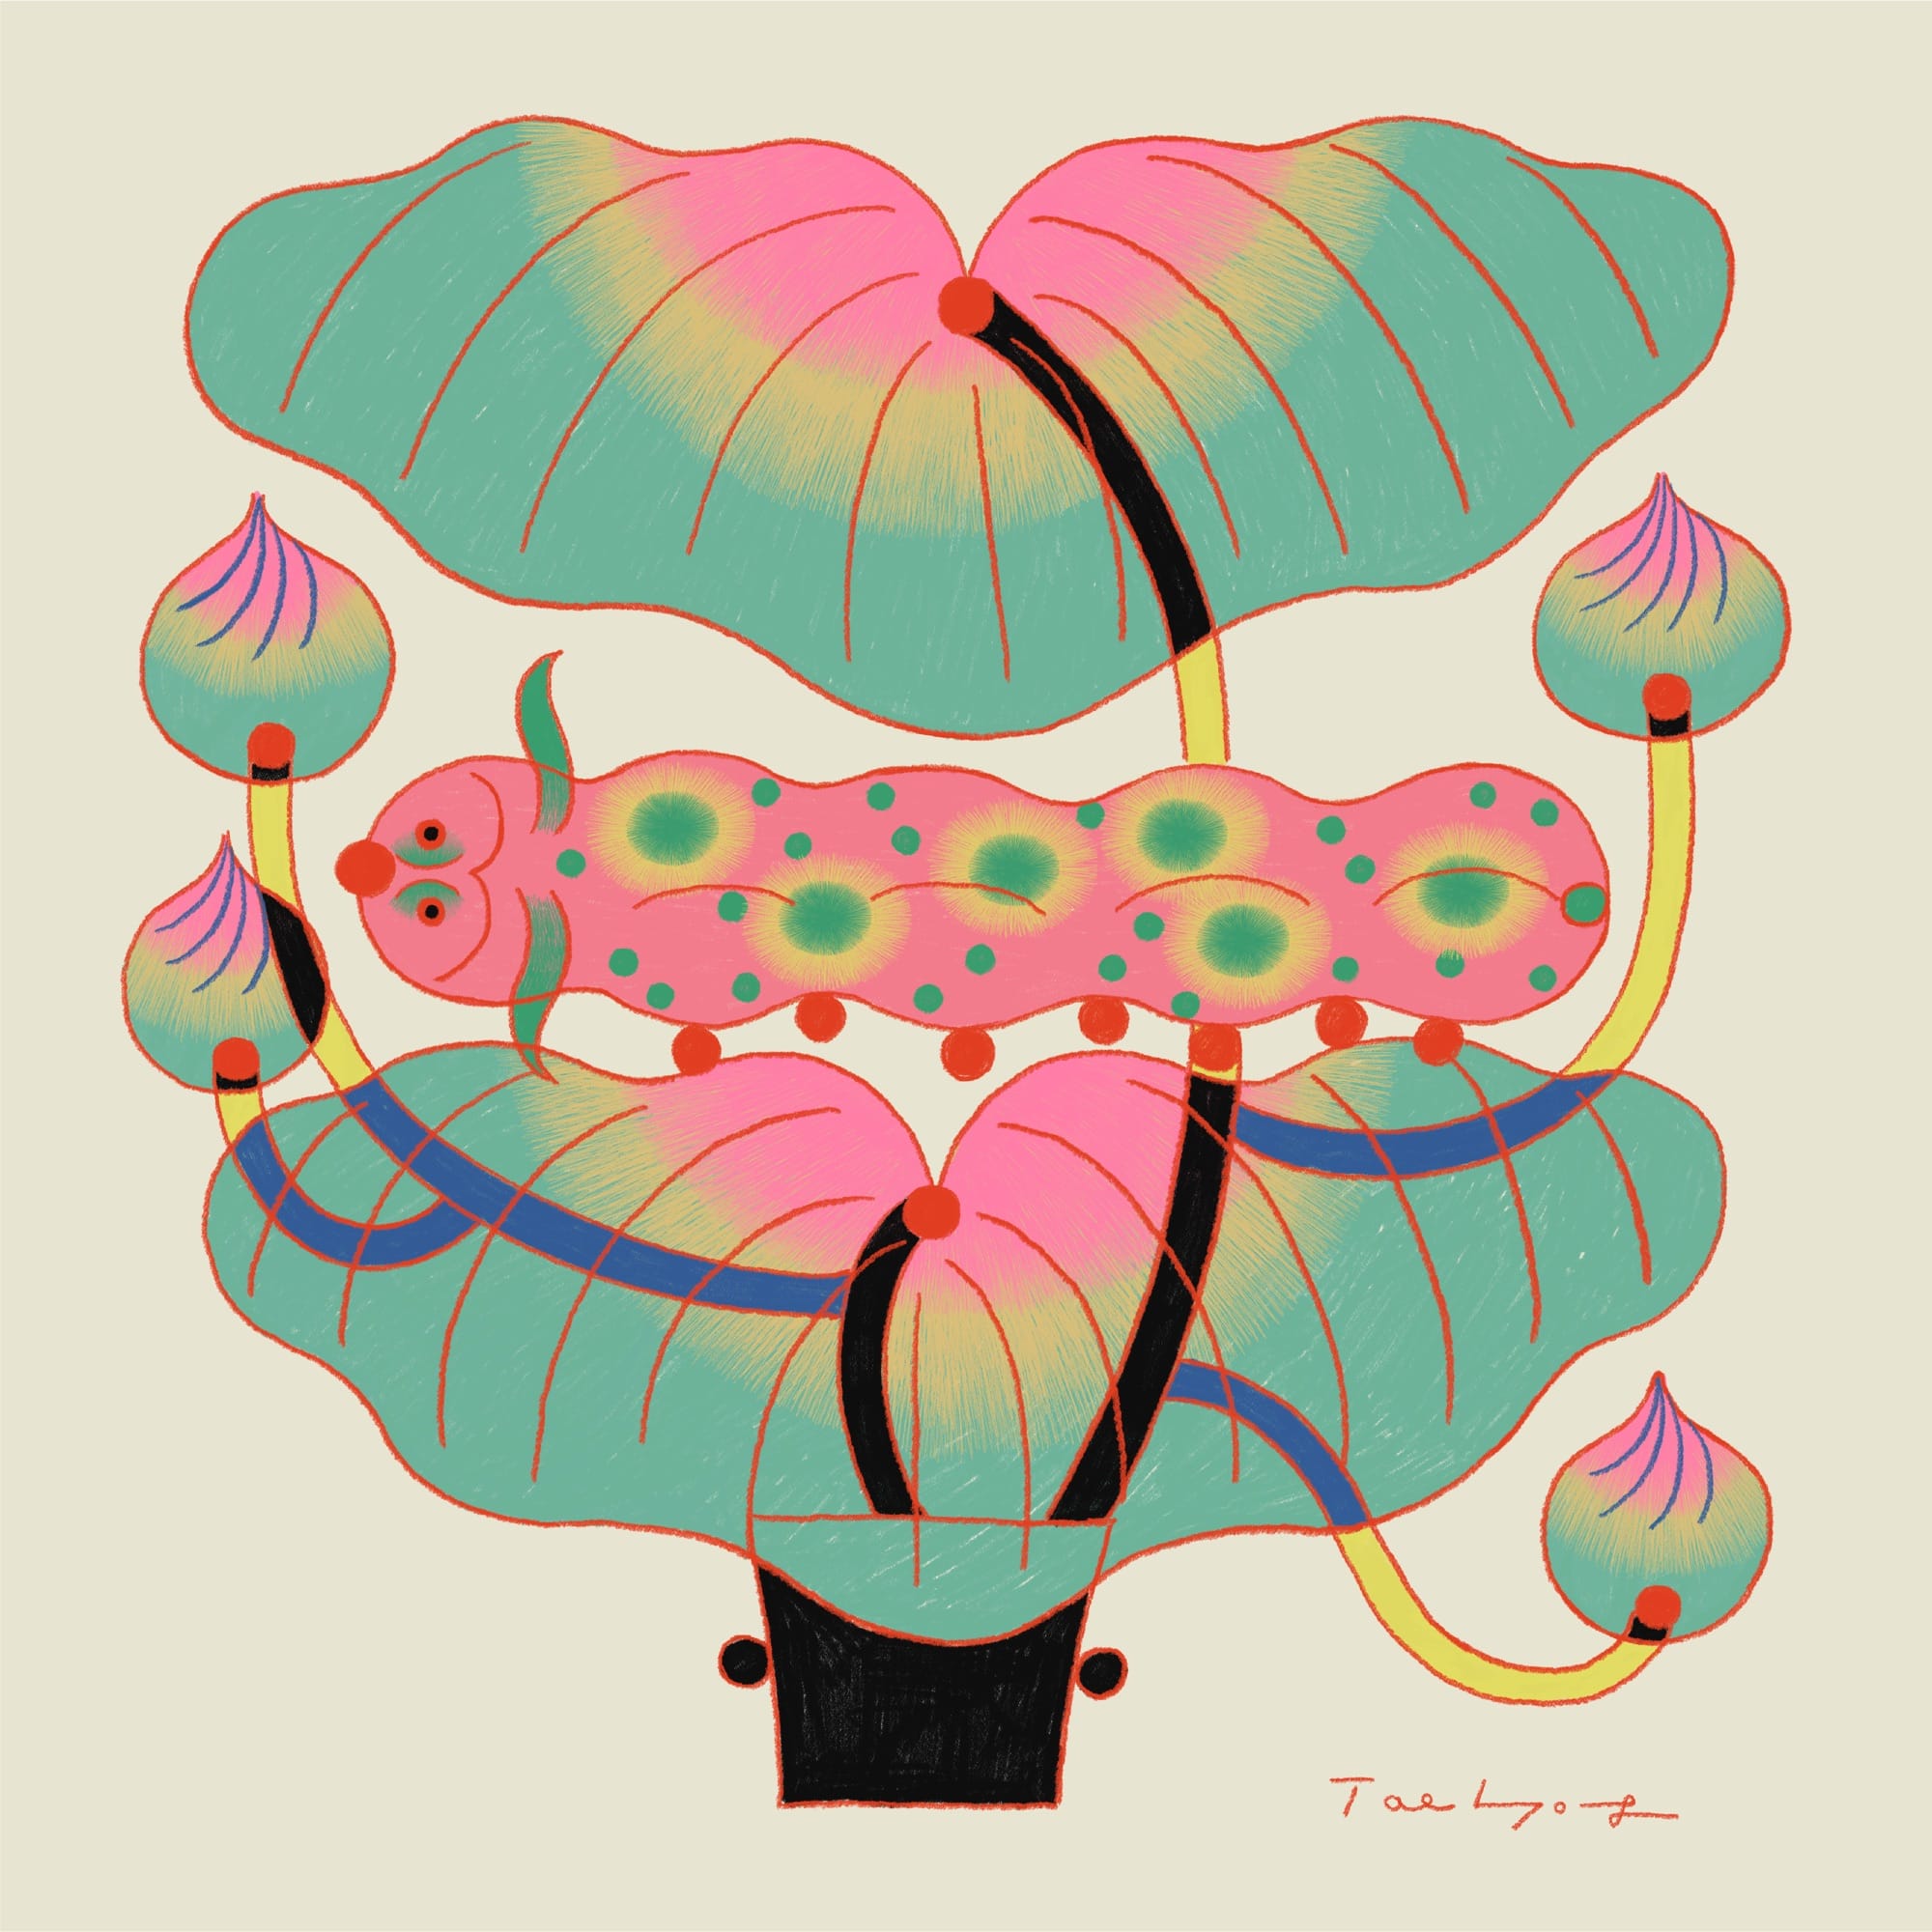
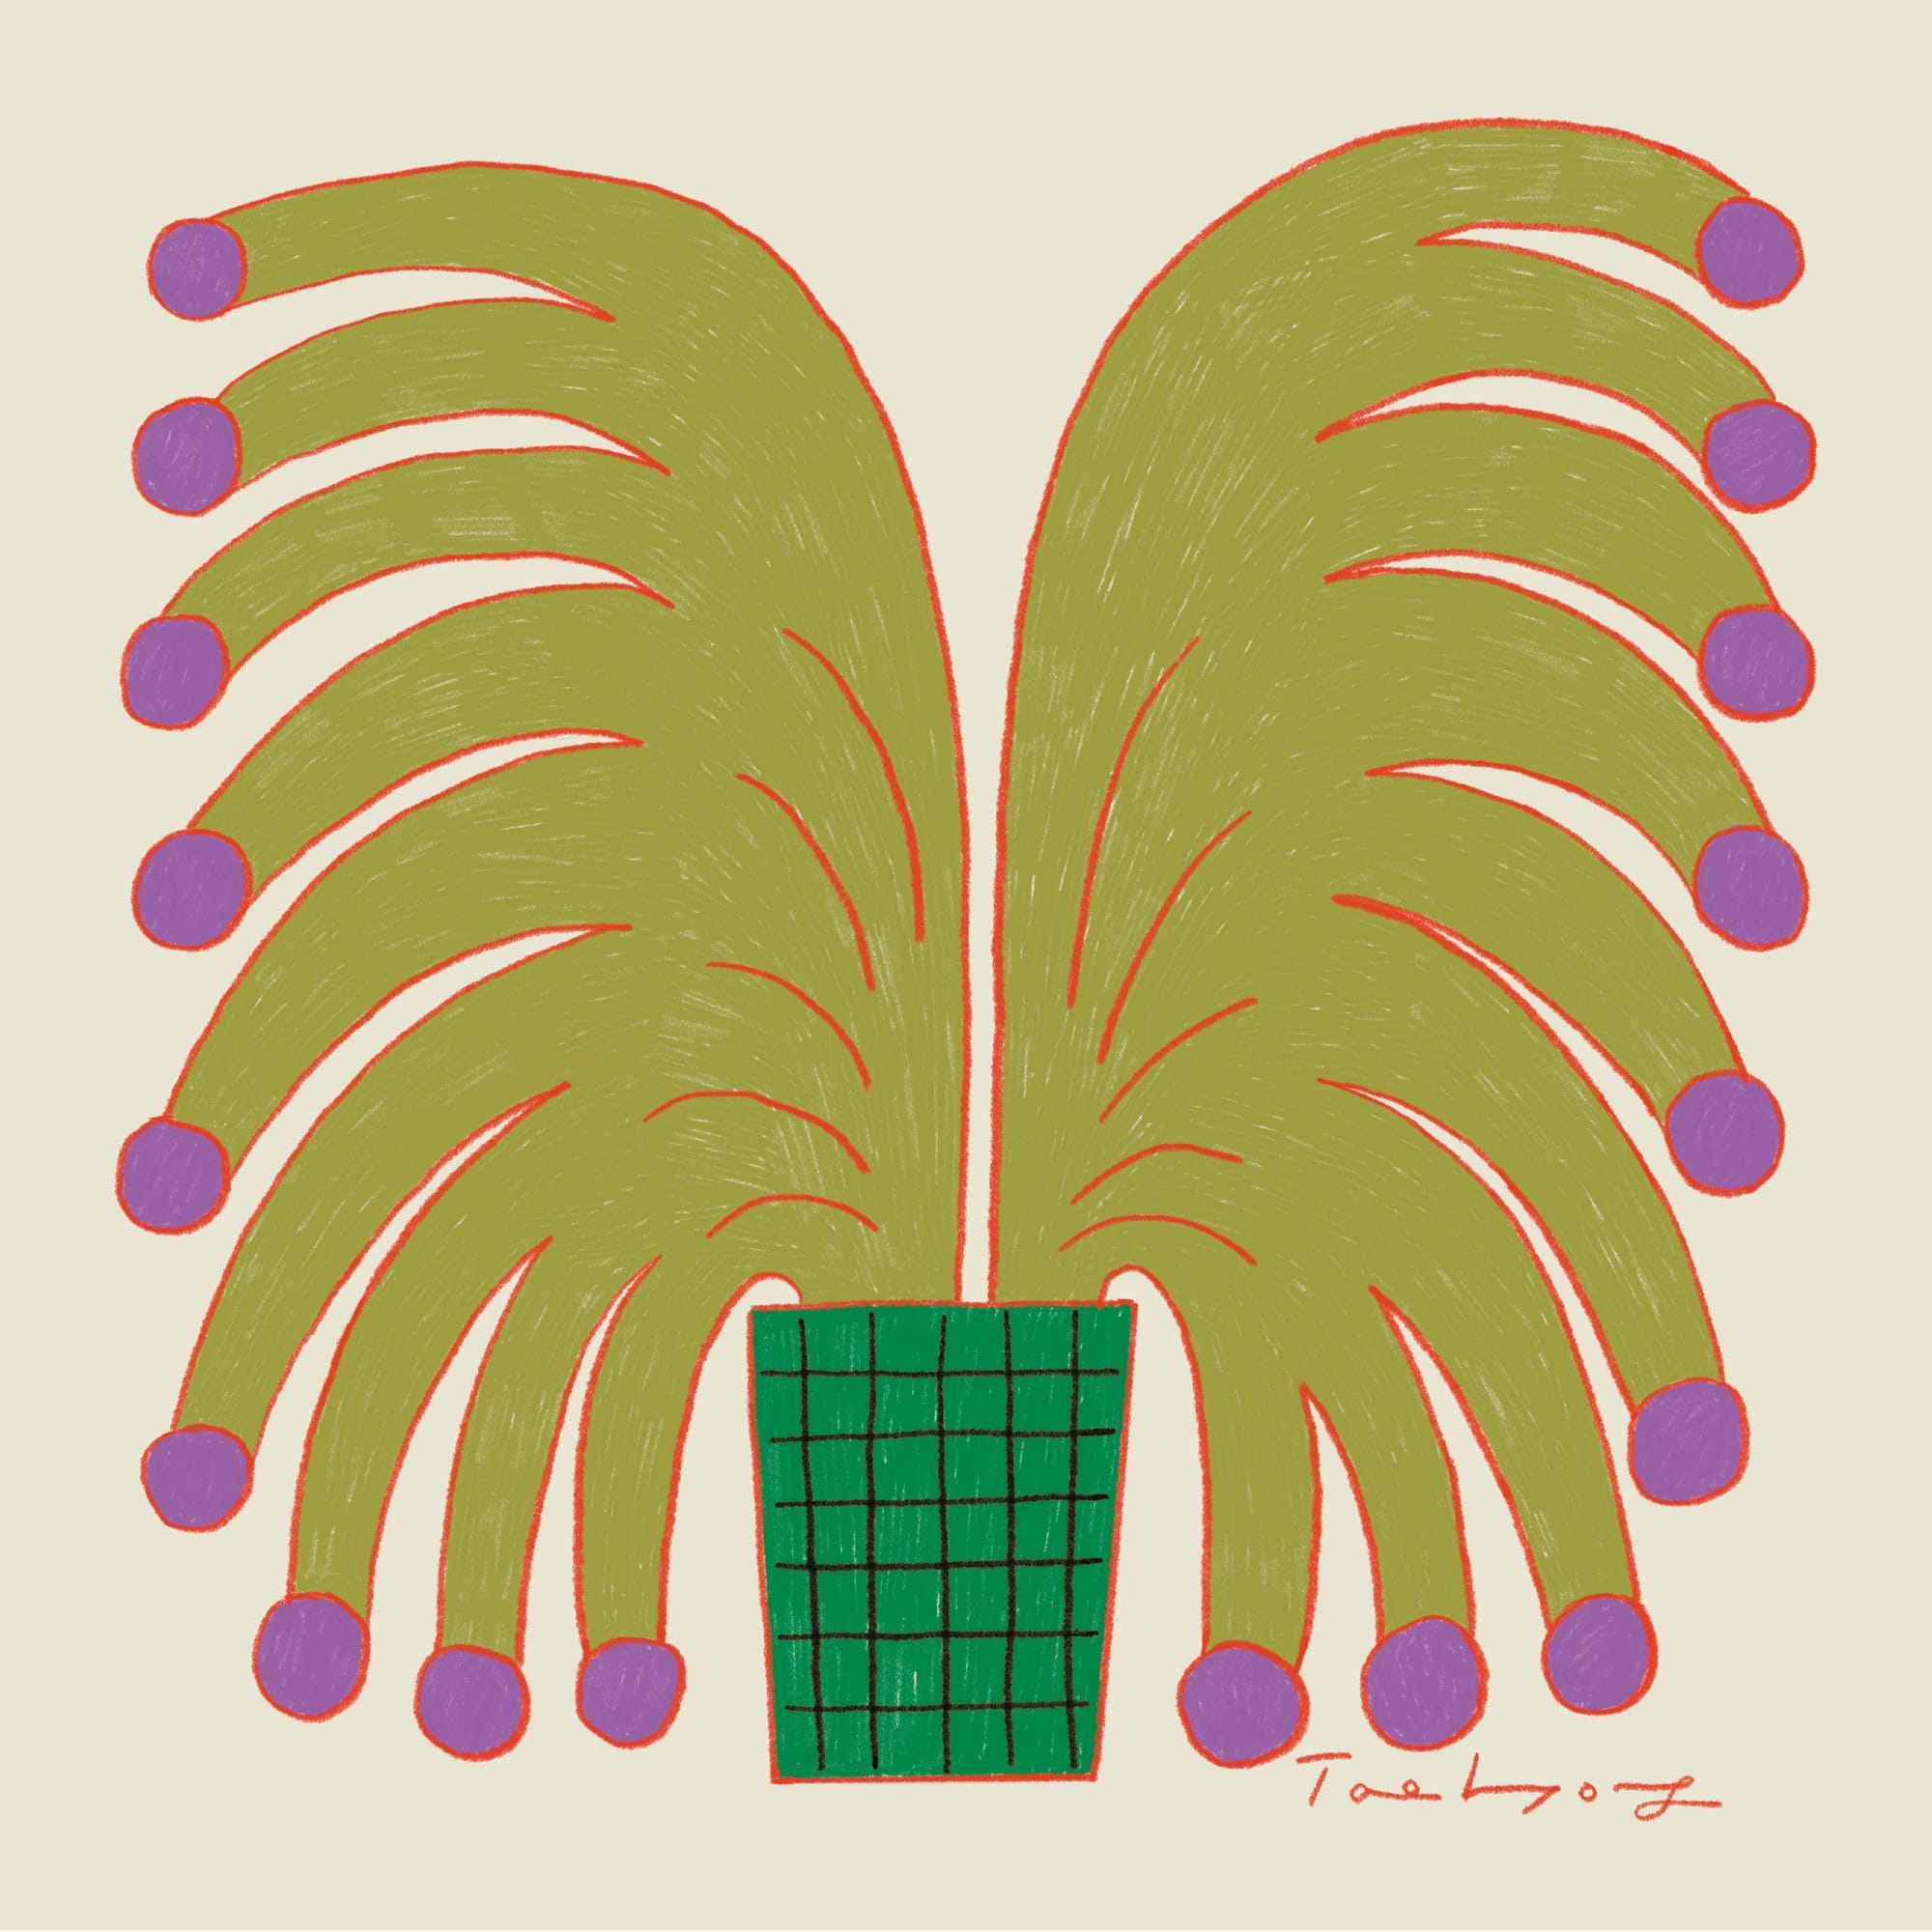
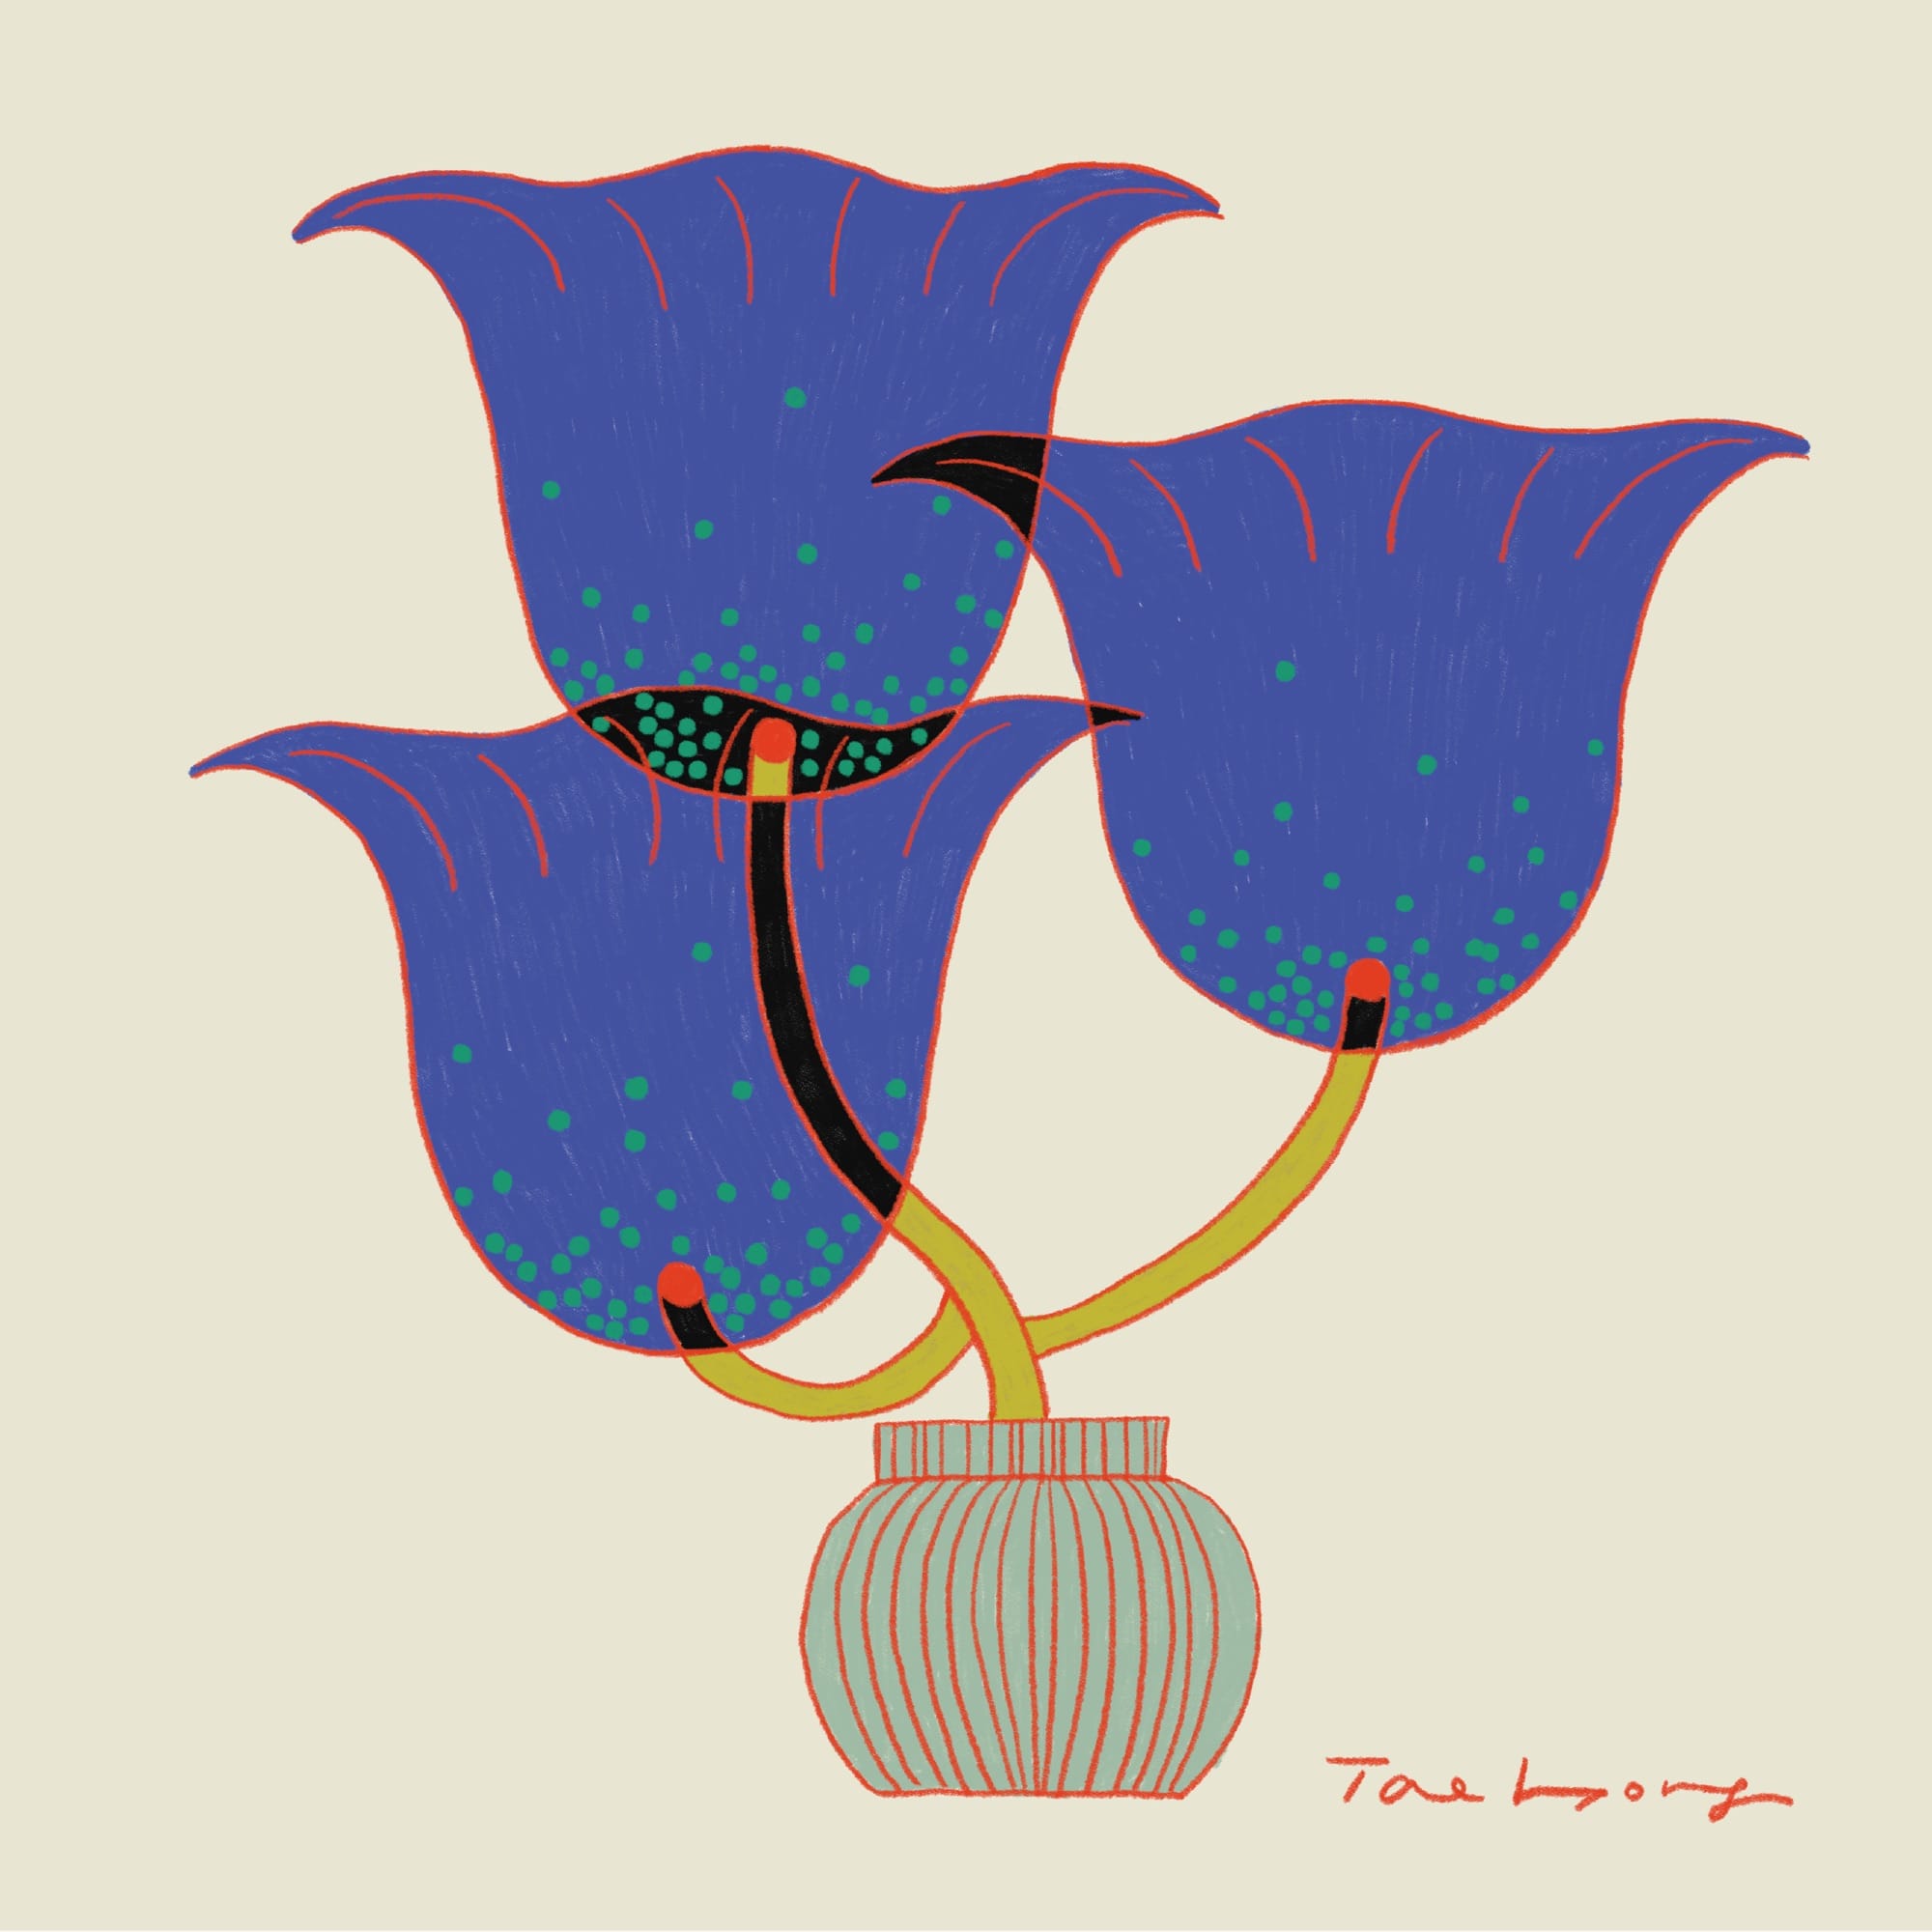
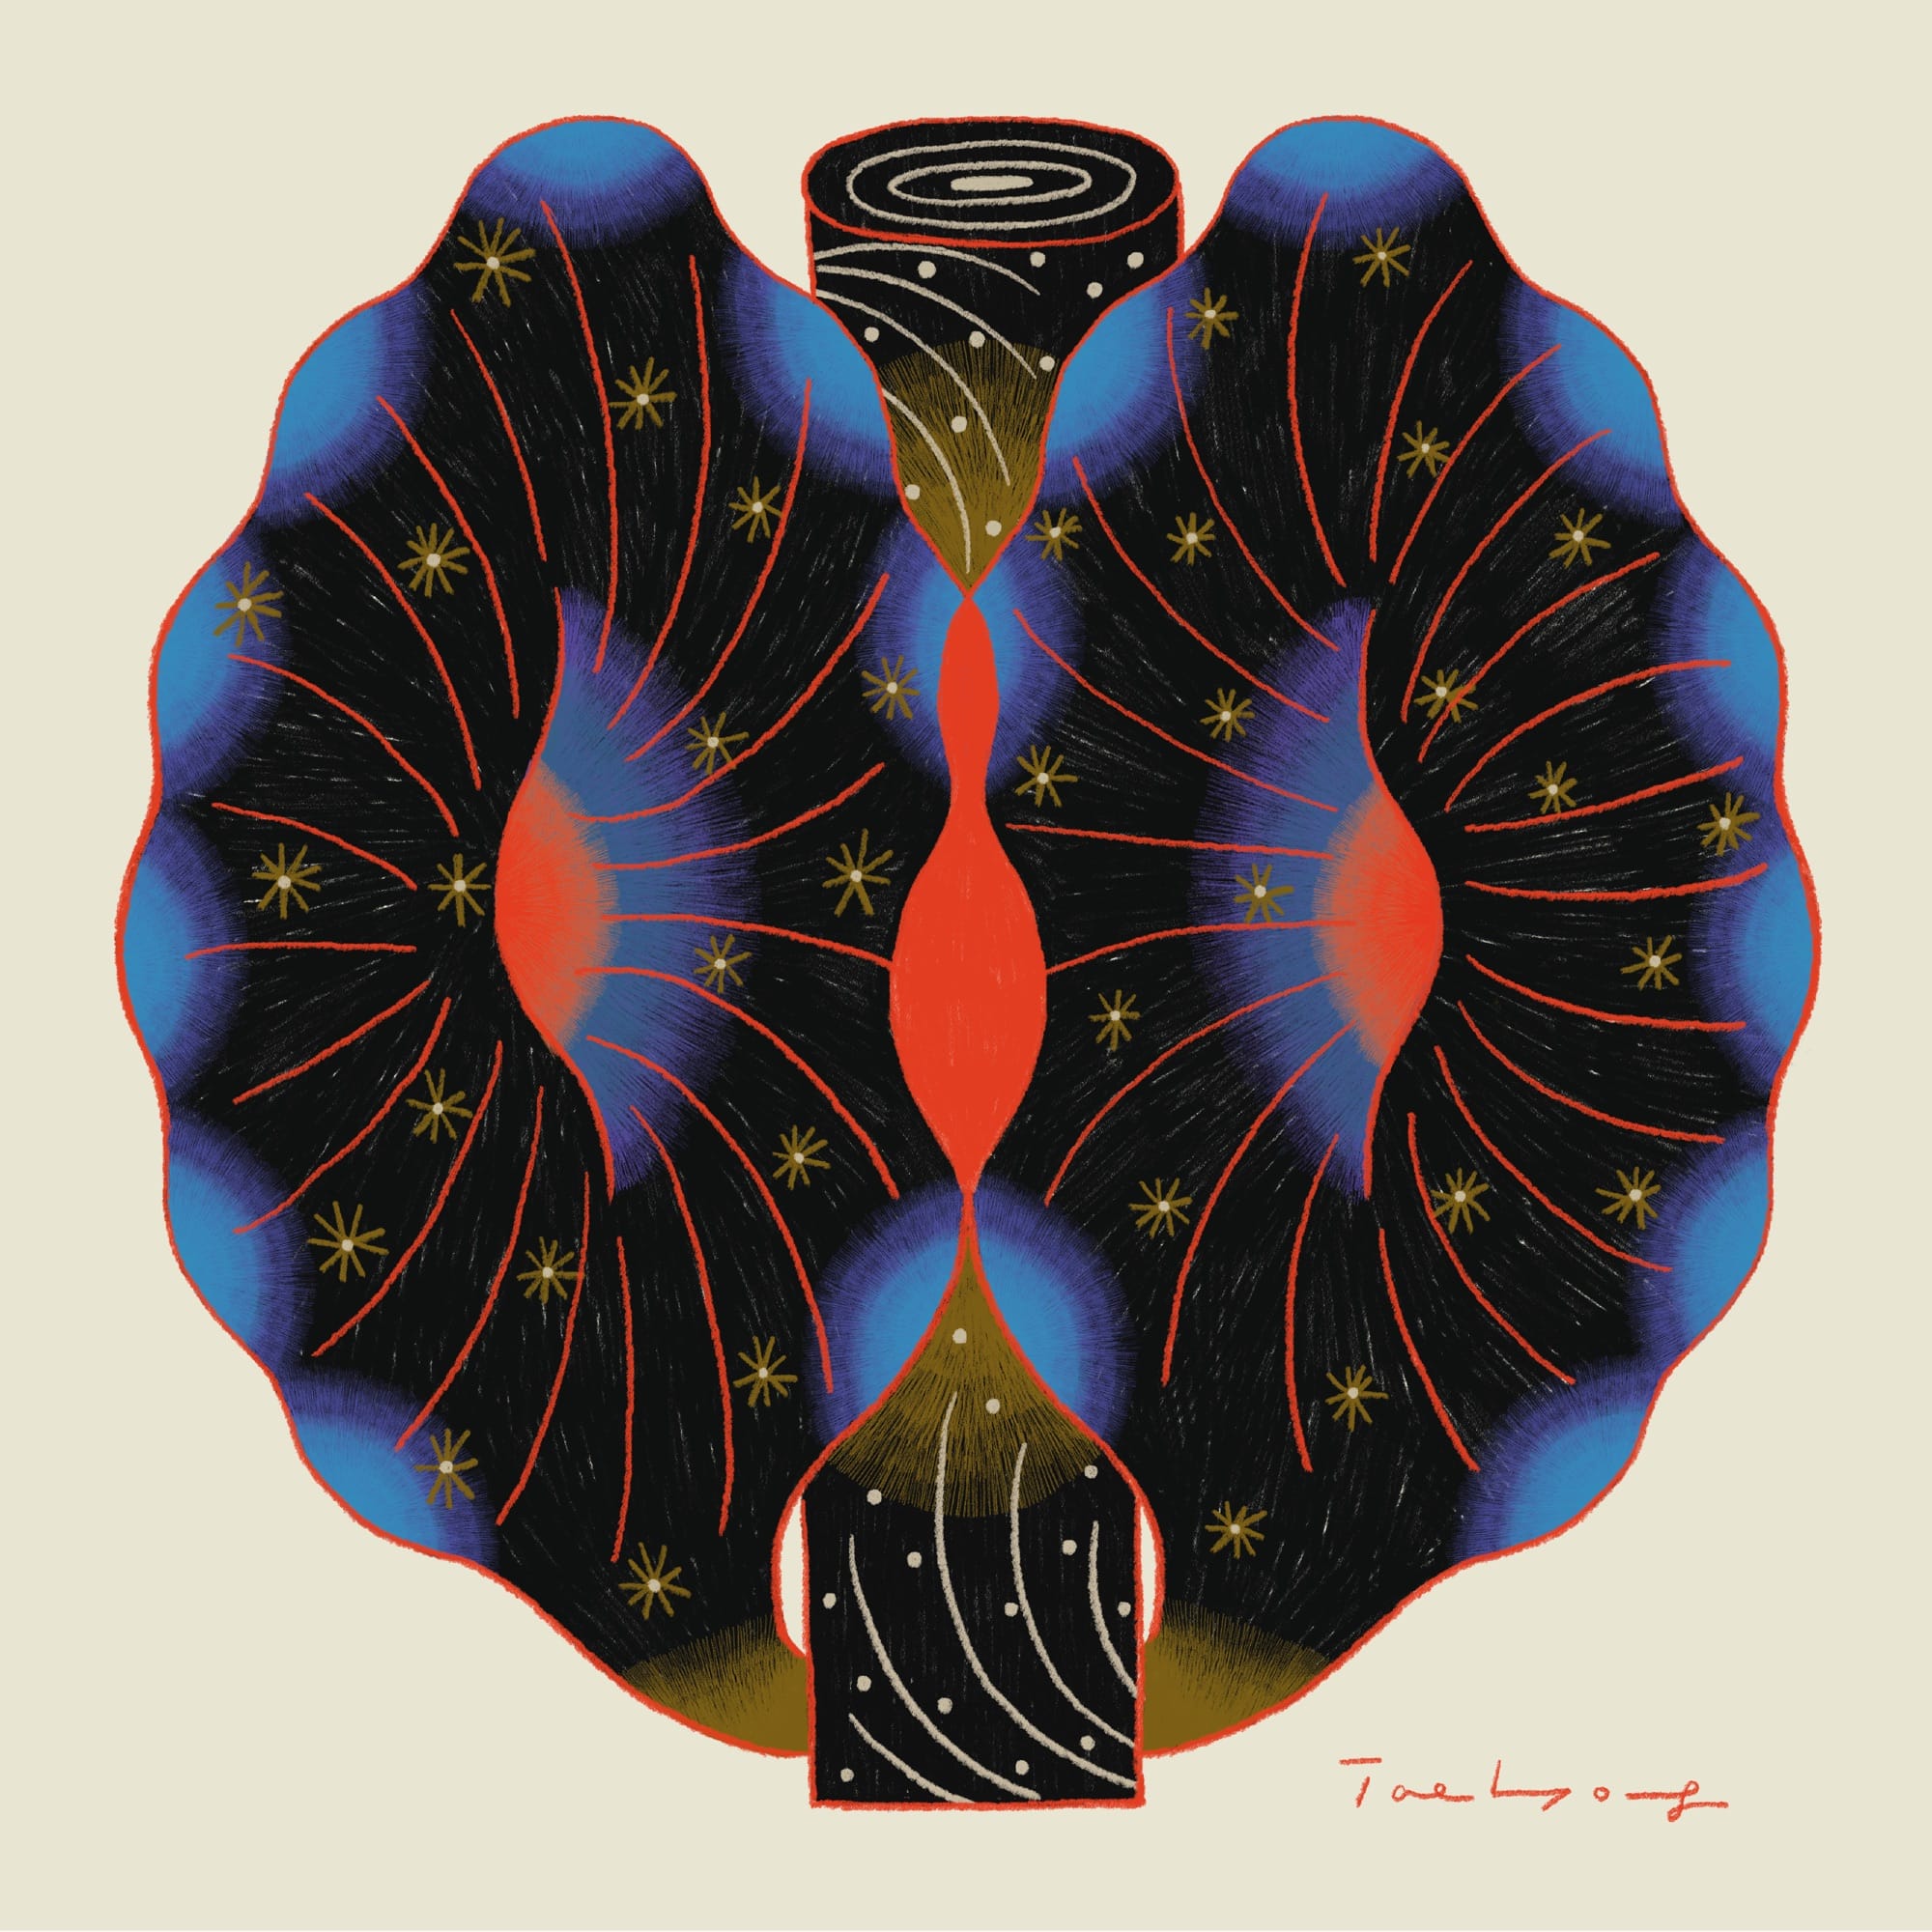
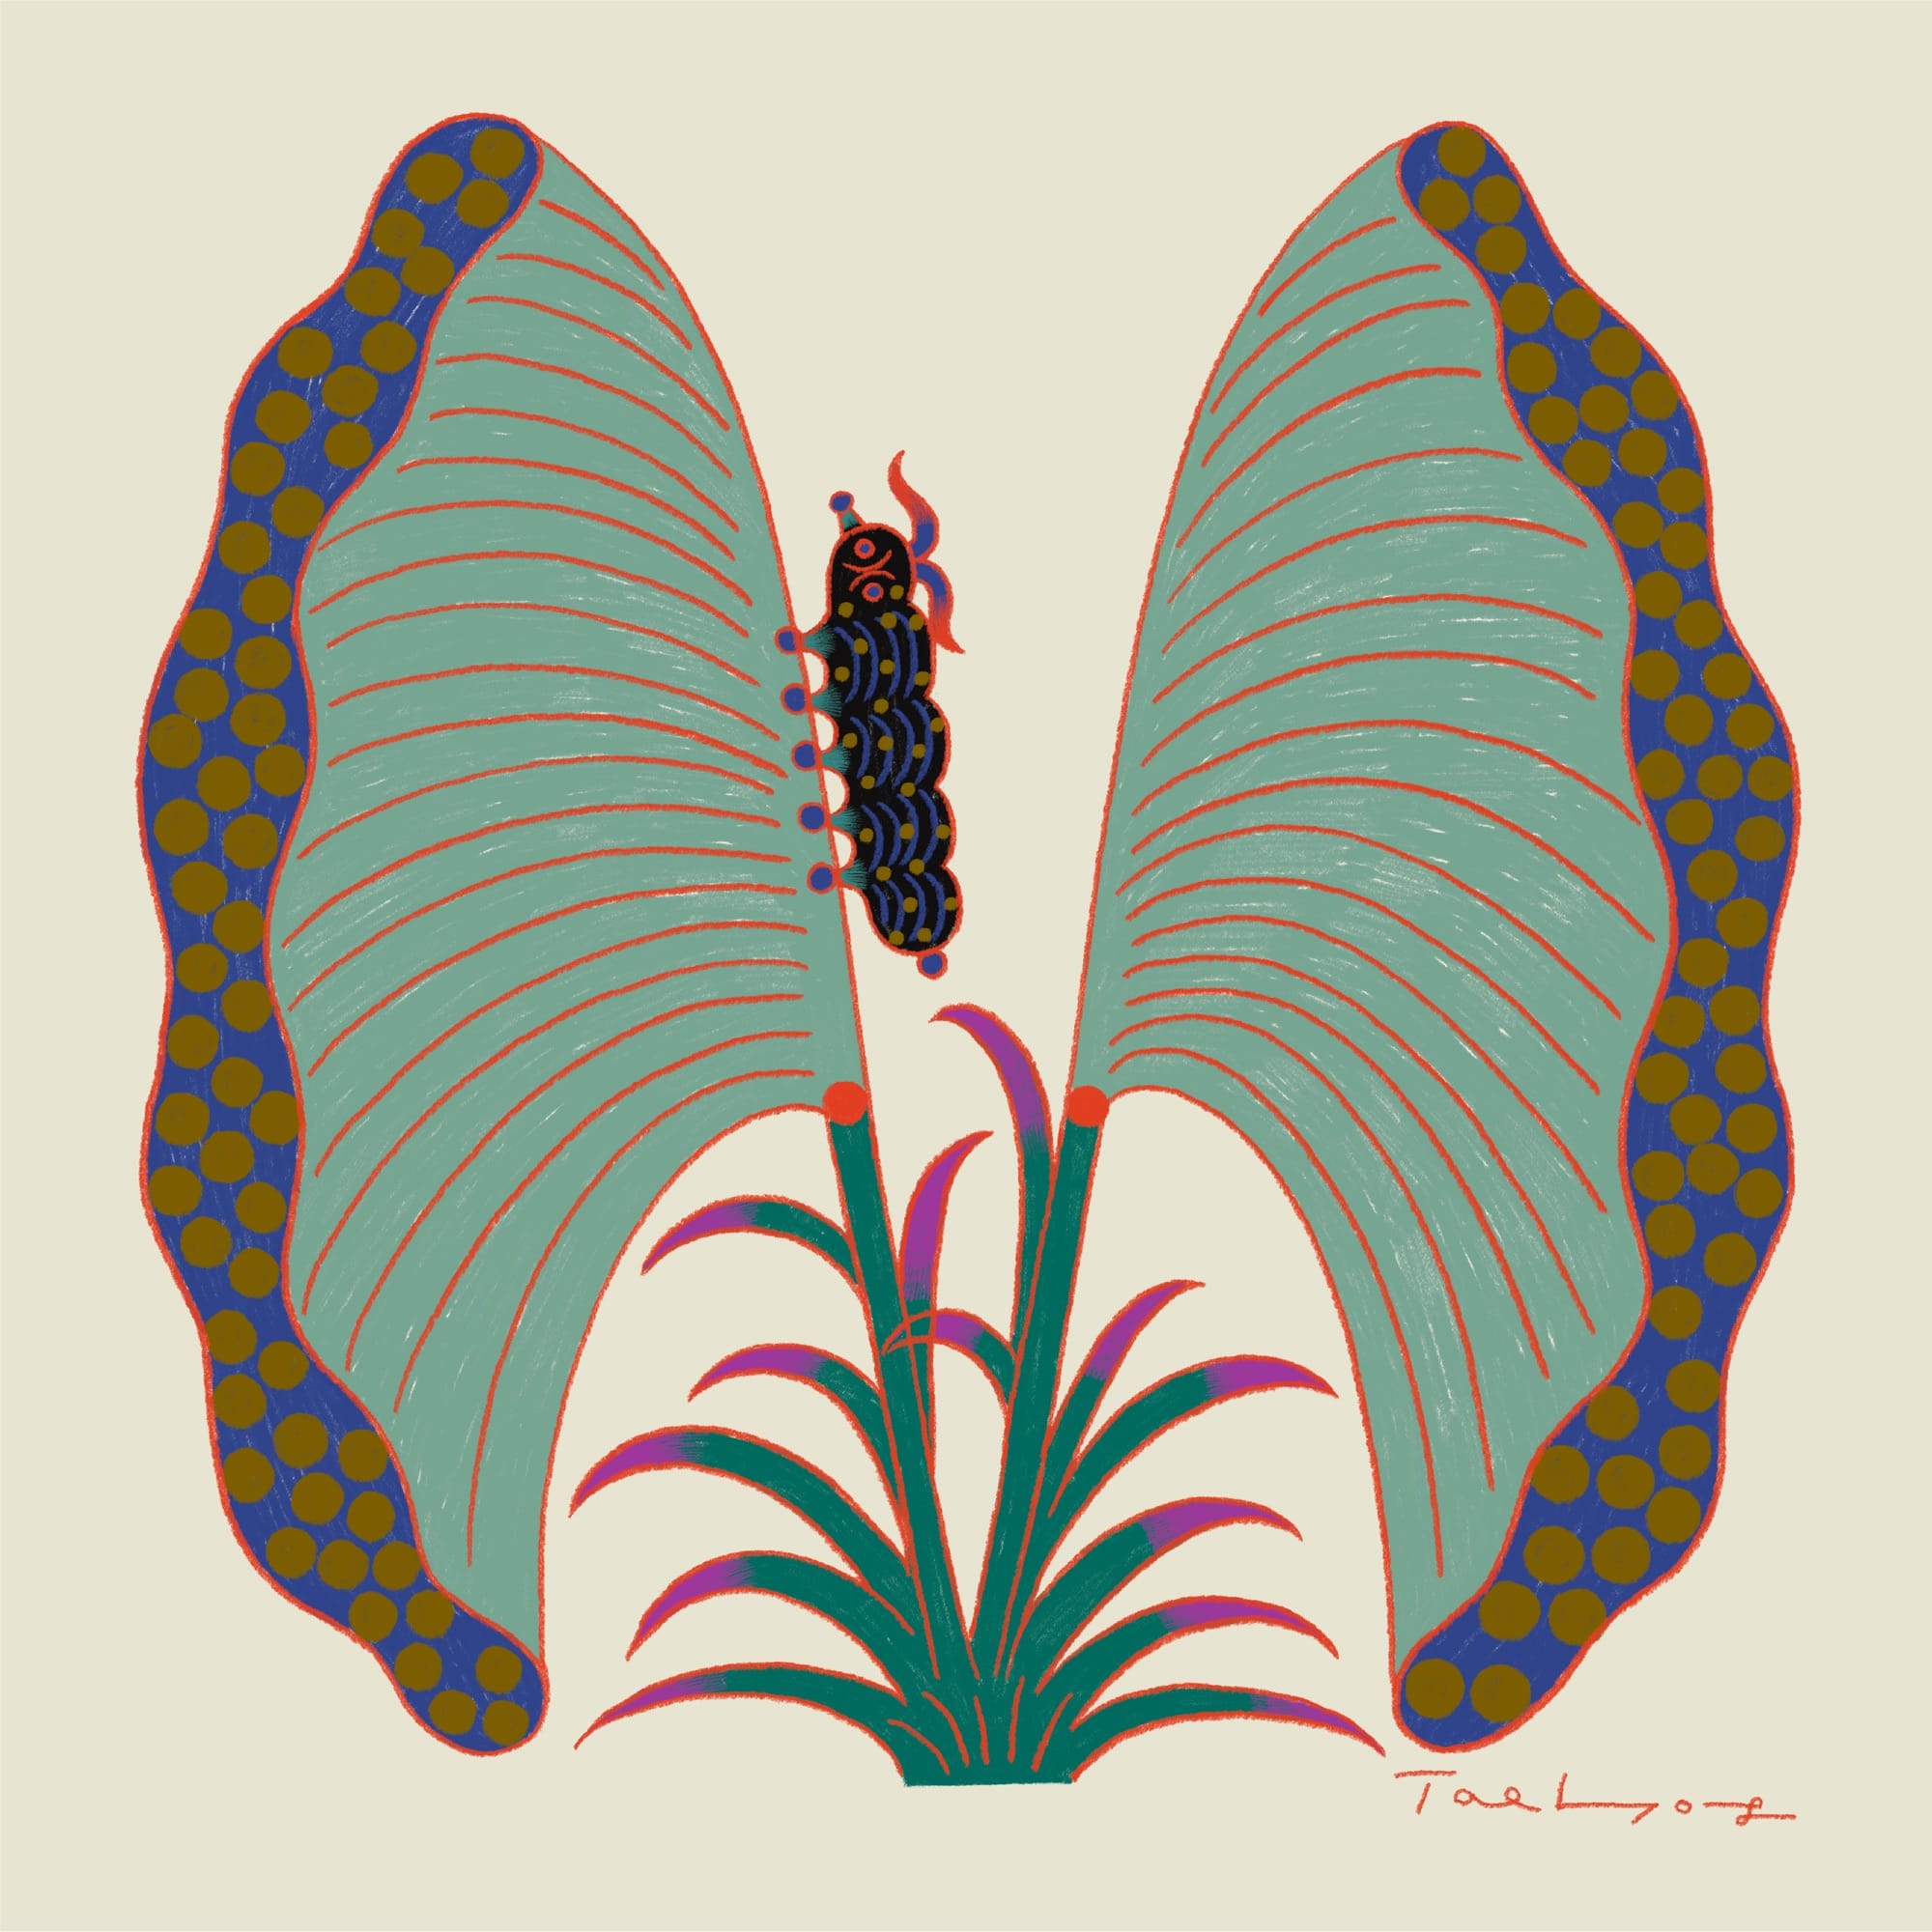
“I try to avoid playing it safe or going for the obvious. Instead, I look at plants from a different perspective and express them in my own way,” South Korean artist Taehyoung Maria Jeon says about a fantastical series of illustrations. “Ironically, having rules is what gives me the freedom to experiment with plant shape.”
Although she’s trained as a printmaker and continues to build compositions in layers, Jeon turns to digital methods as she reimagines the specimens cohabitating in her apartment, beginning with leaves and stems before venturing into surreal terrain. Purple veins, red outlines, and a smattering of stars appear on the imagined life forms, their vivid color palettes furthering their sense of the uncanny.
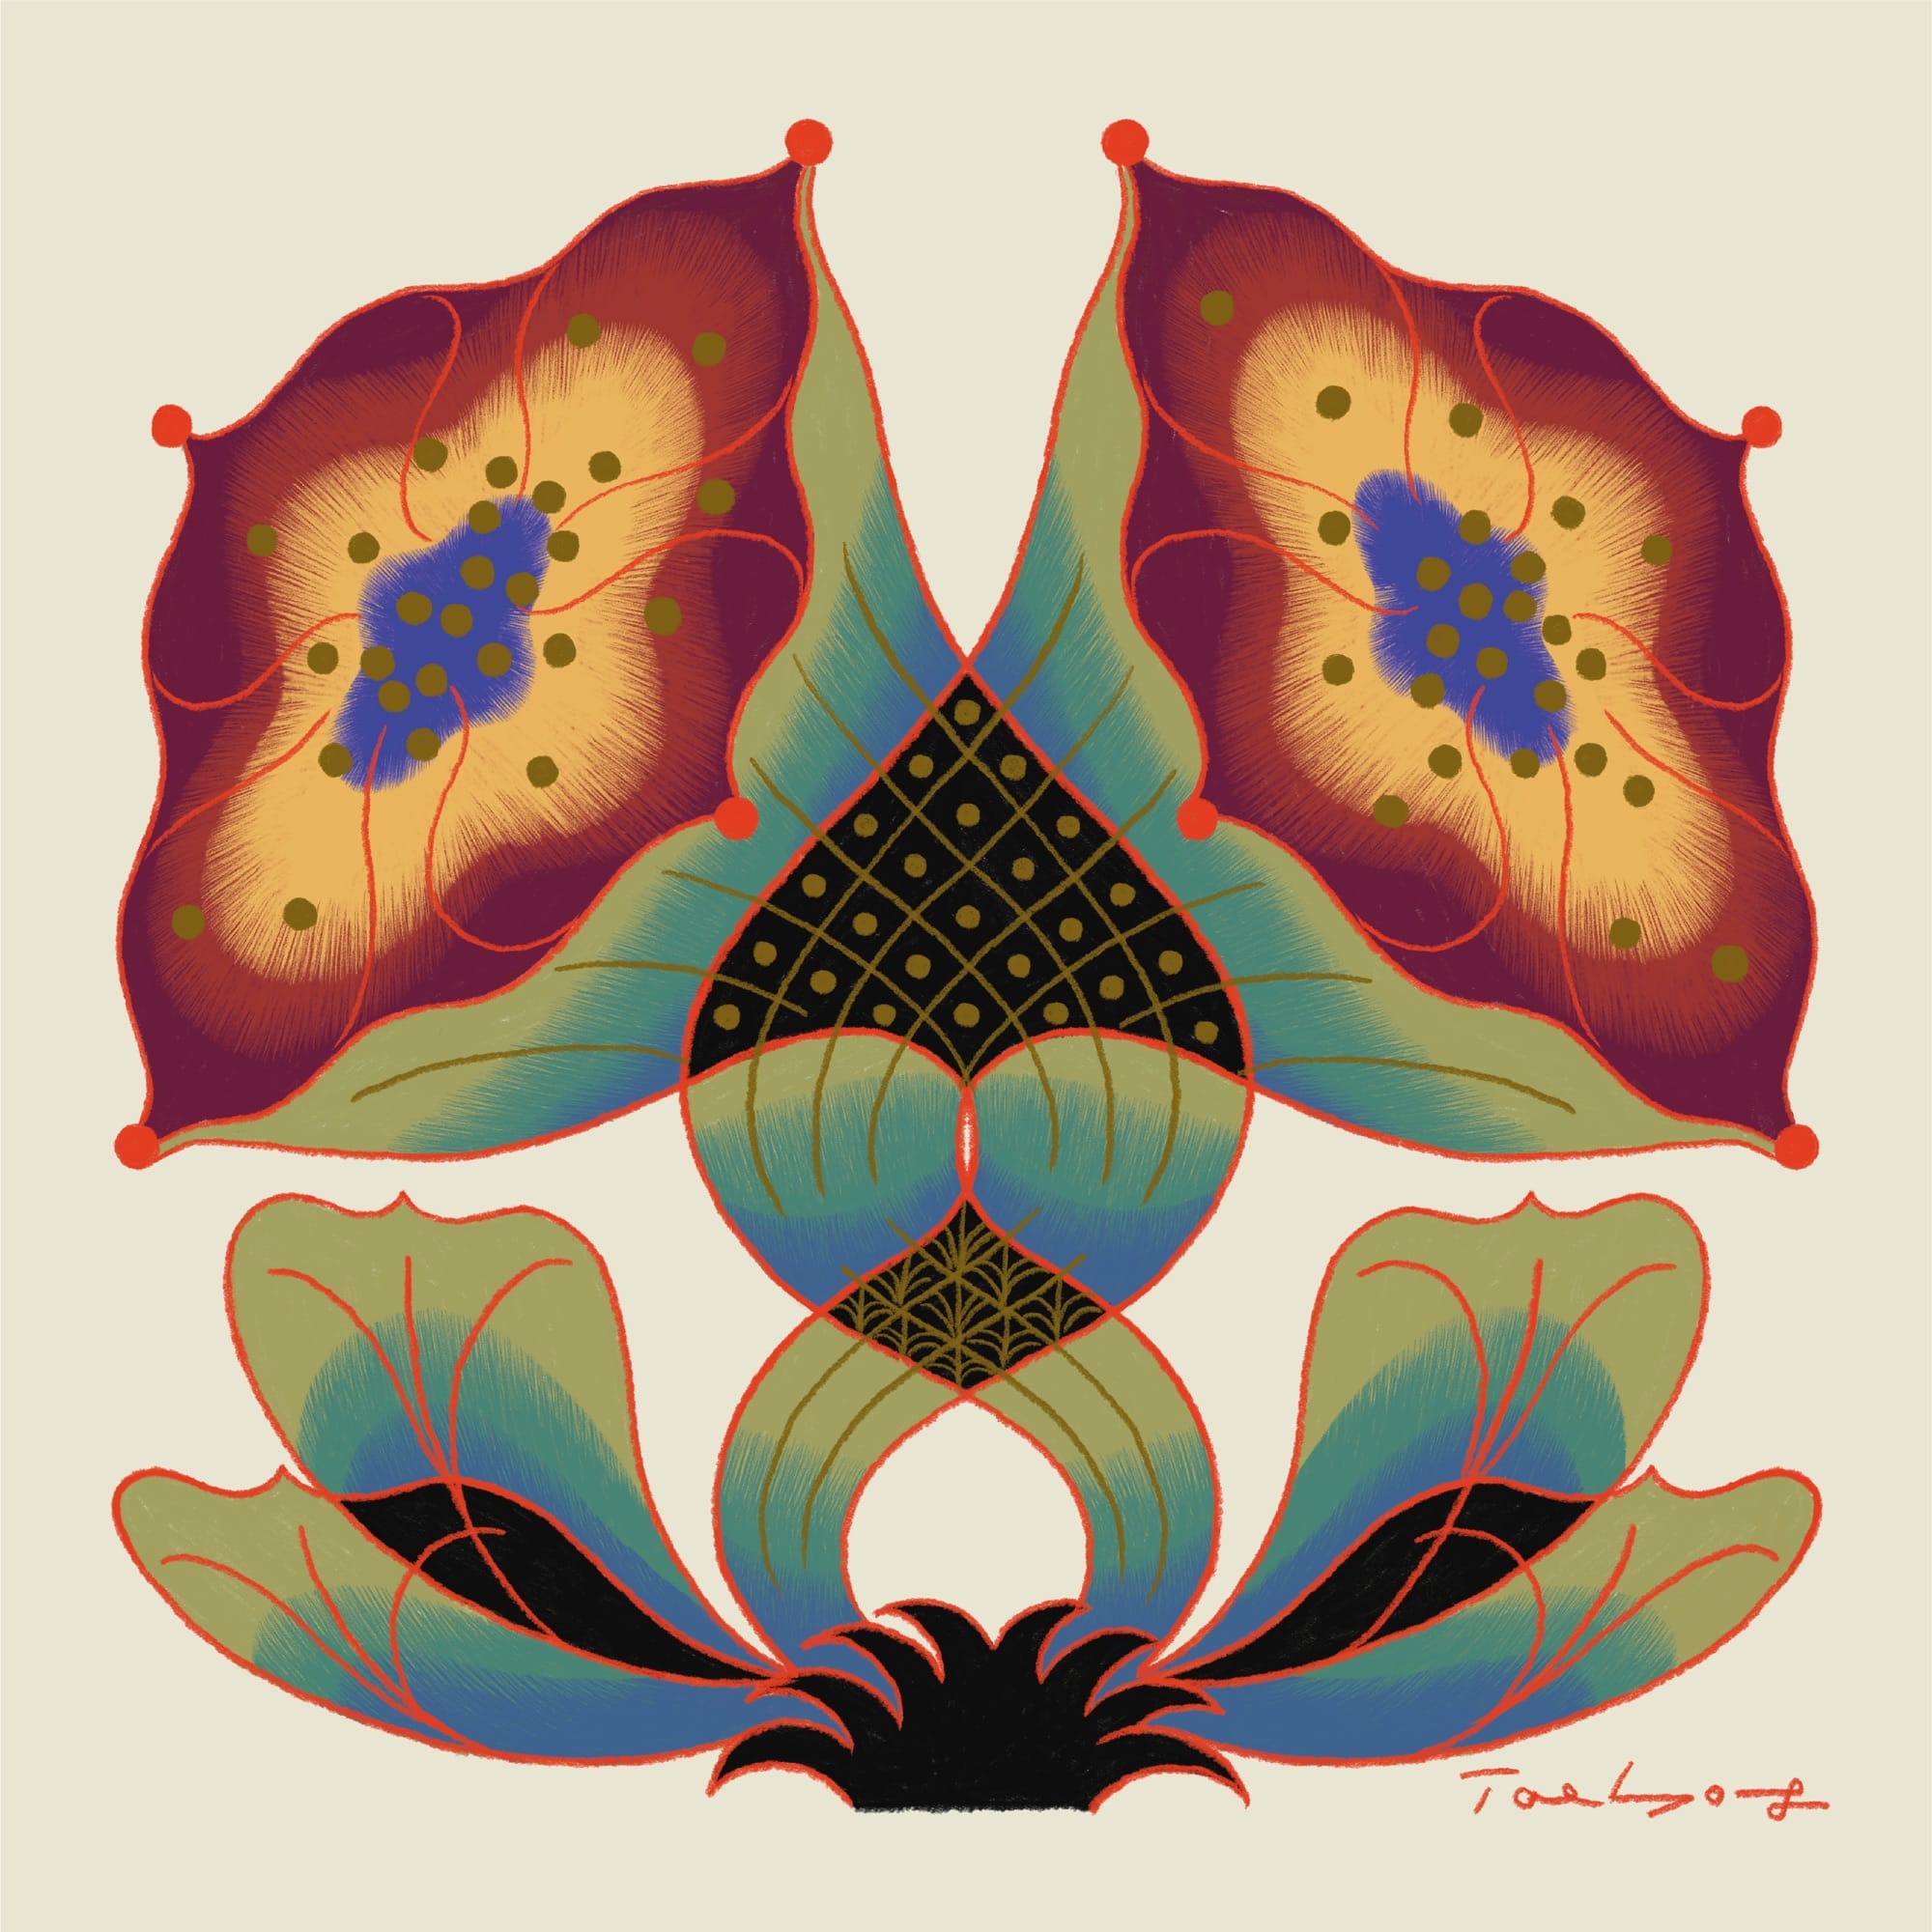
Titled Plant Series, the project “started as a personal challenge to fill a square canvas with plants, playing with shapes and composition to pack everything in as much as possible,” she says. “As the series continues, the drawings evolve and the nuances shift, but at its heart, it is always about composition, balance, colour, and shape—and hopefully sending out positive vibes, too.”
Dozens of illustrations from the series are compiled in Folium, Jeon’s first monograph from Volume. The publisher functions like Kickstarter and asks readers to back the project before printing. You can reserve your copy on Volume’s website, and find more from the artist on Instagram.
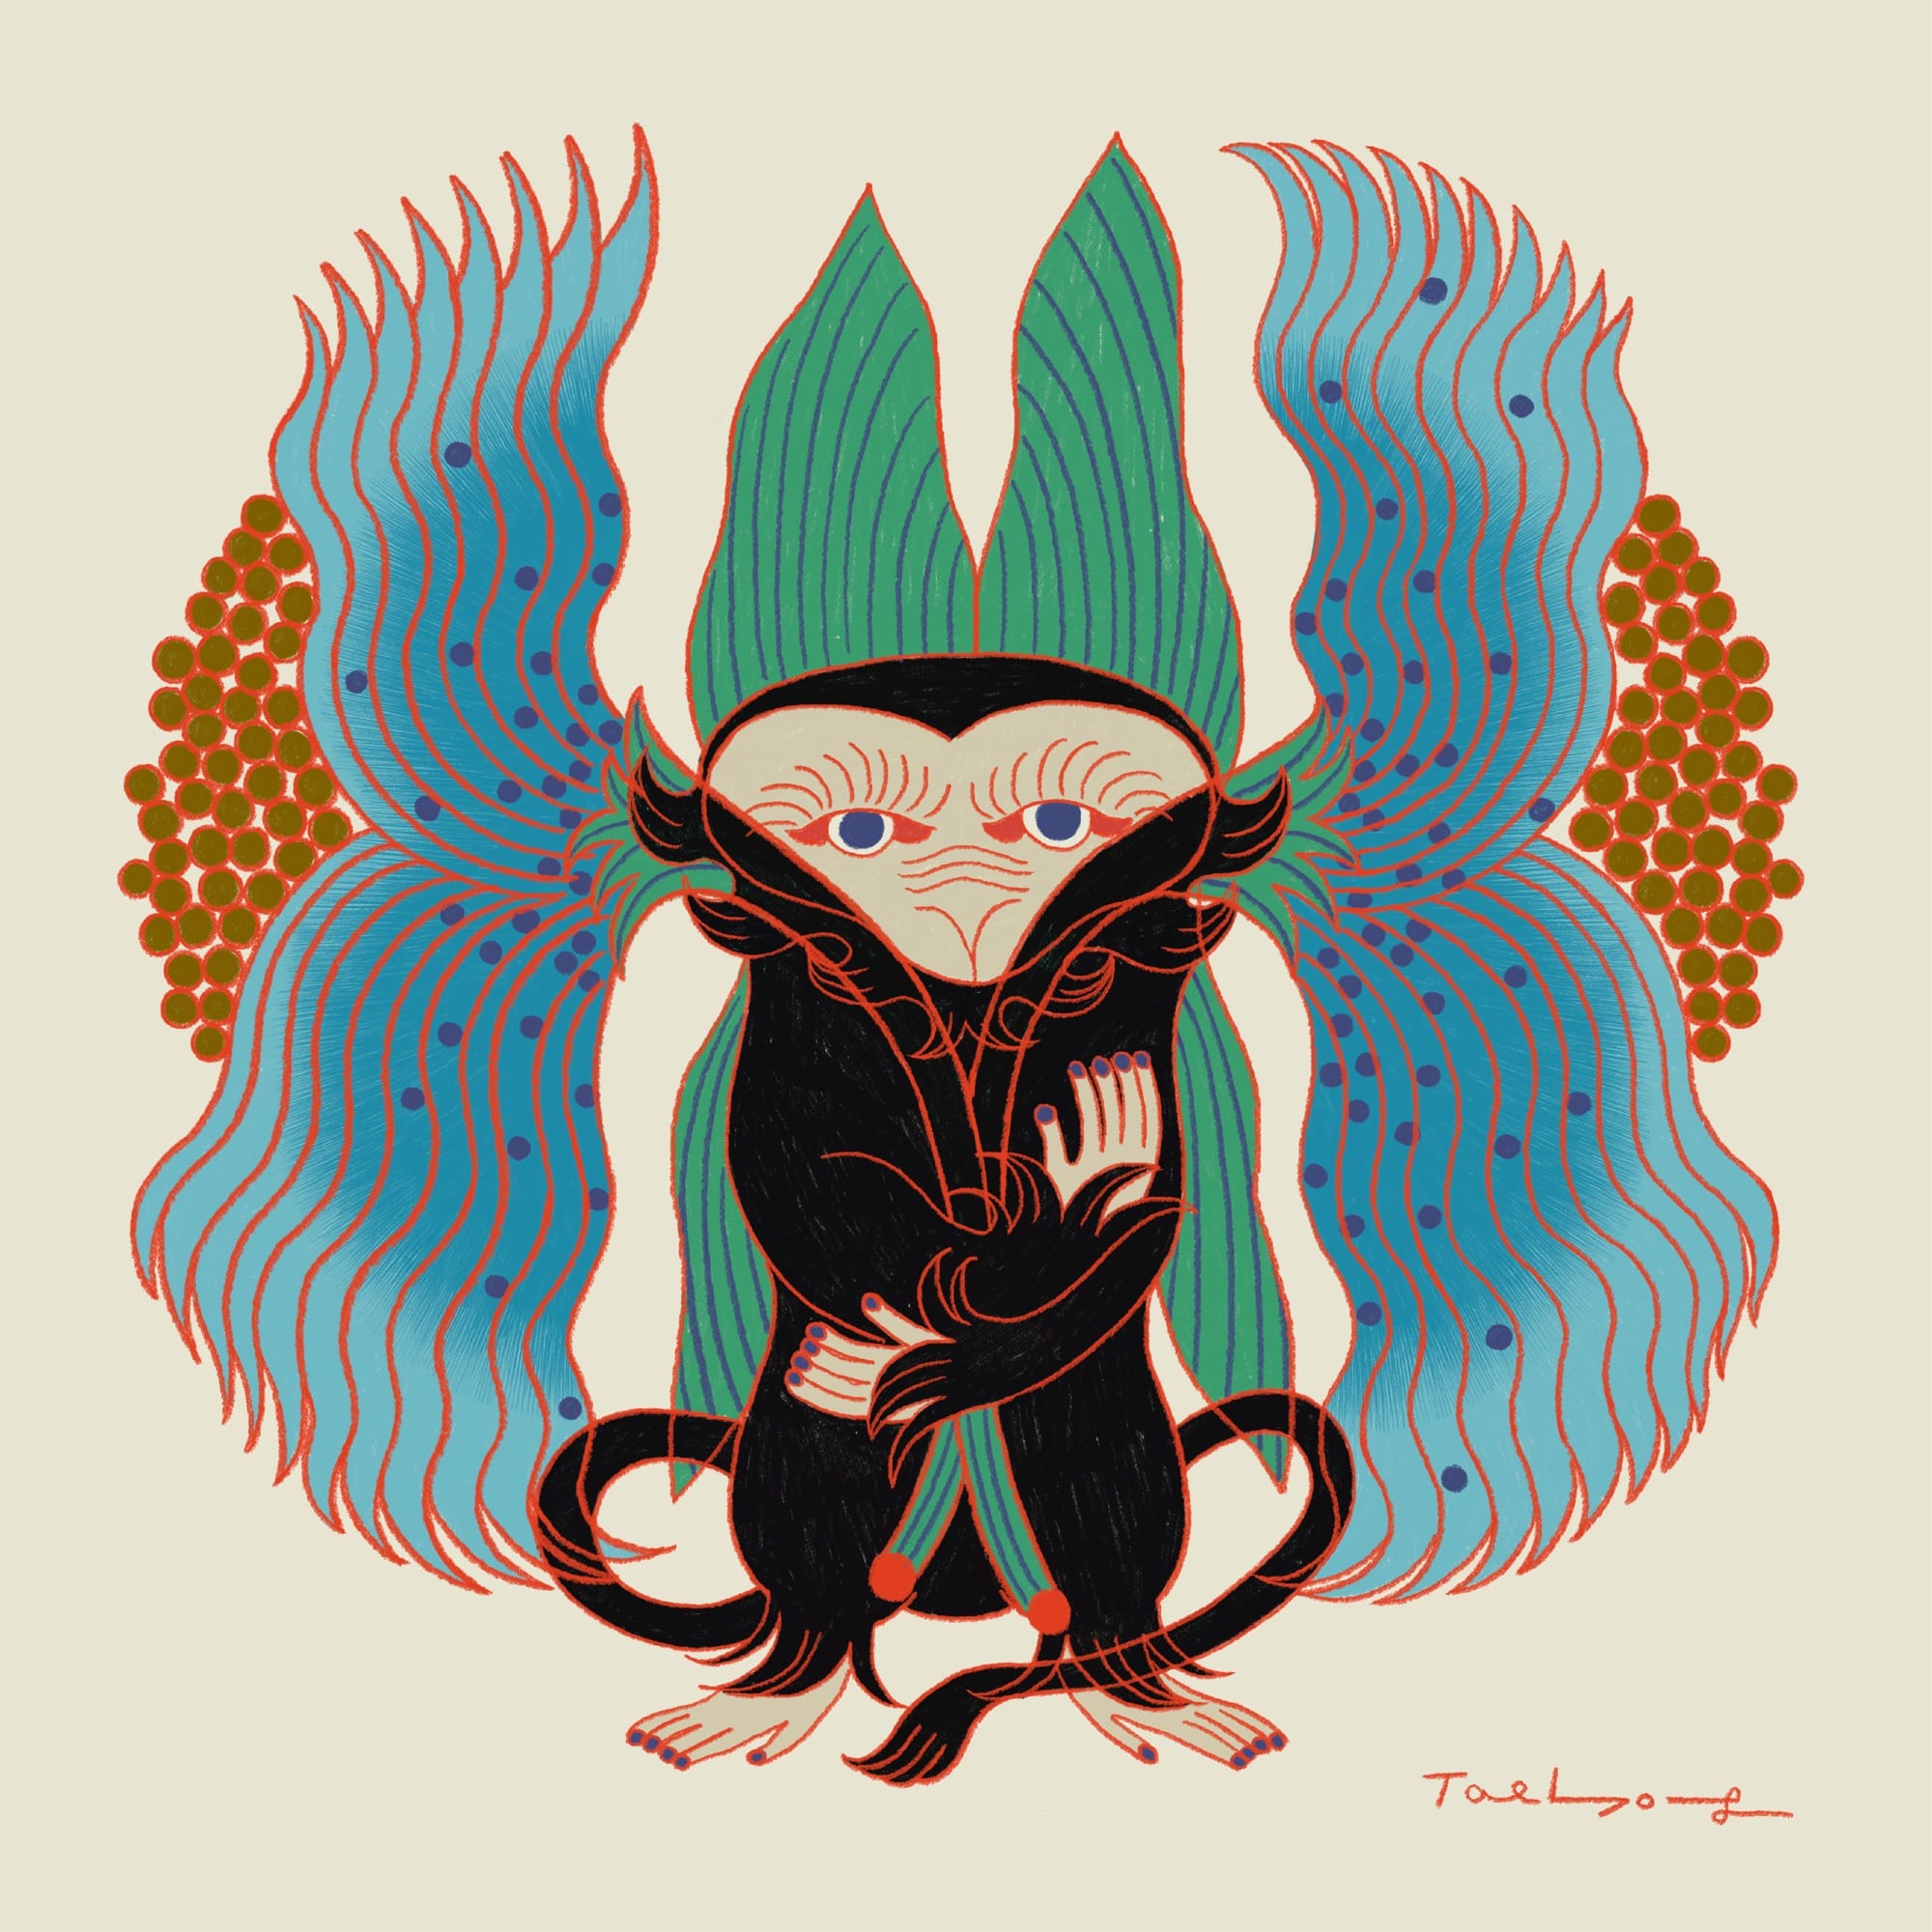
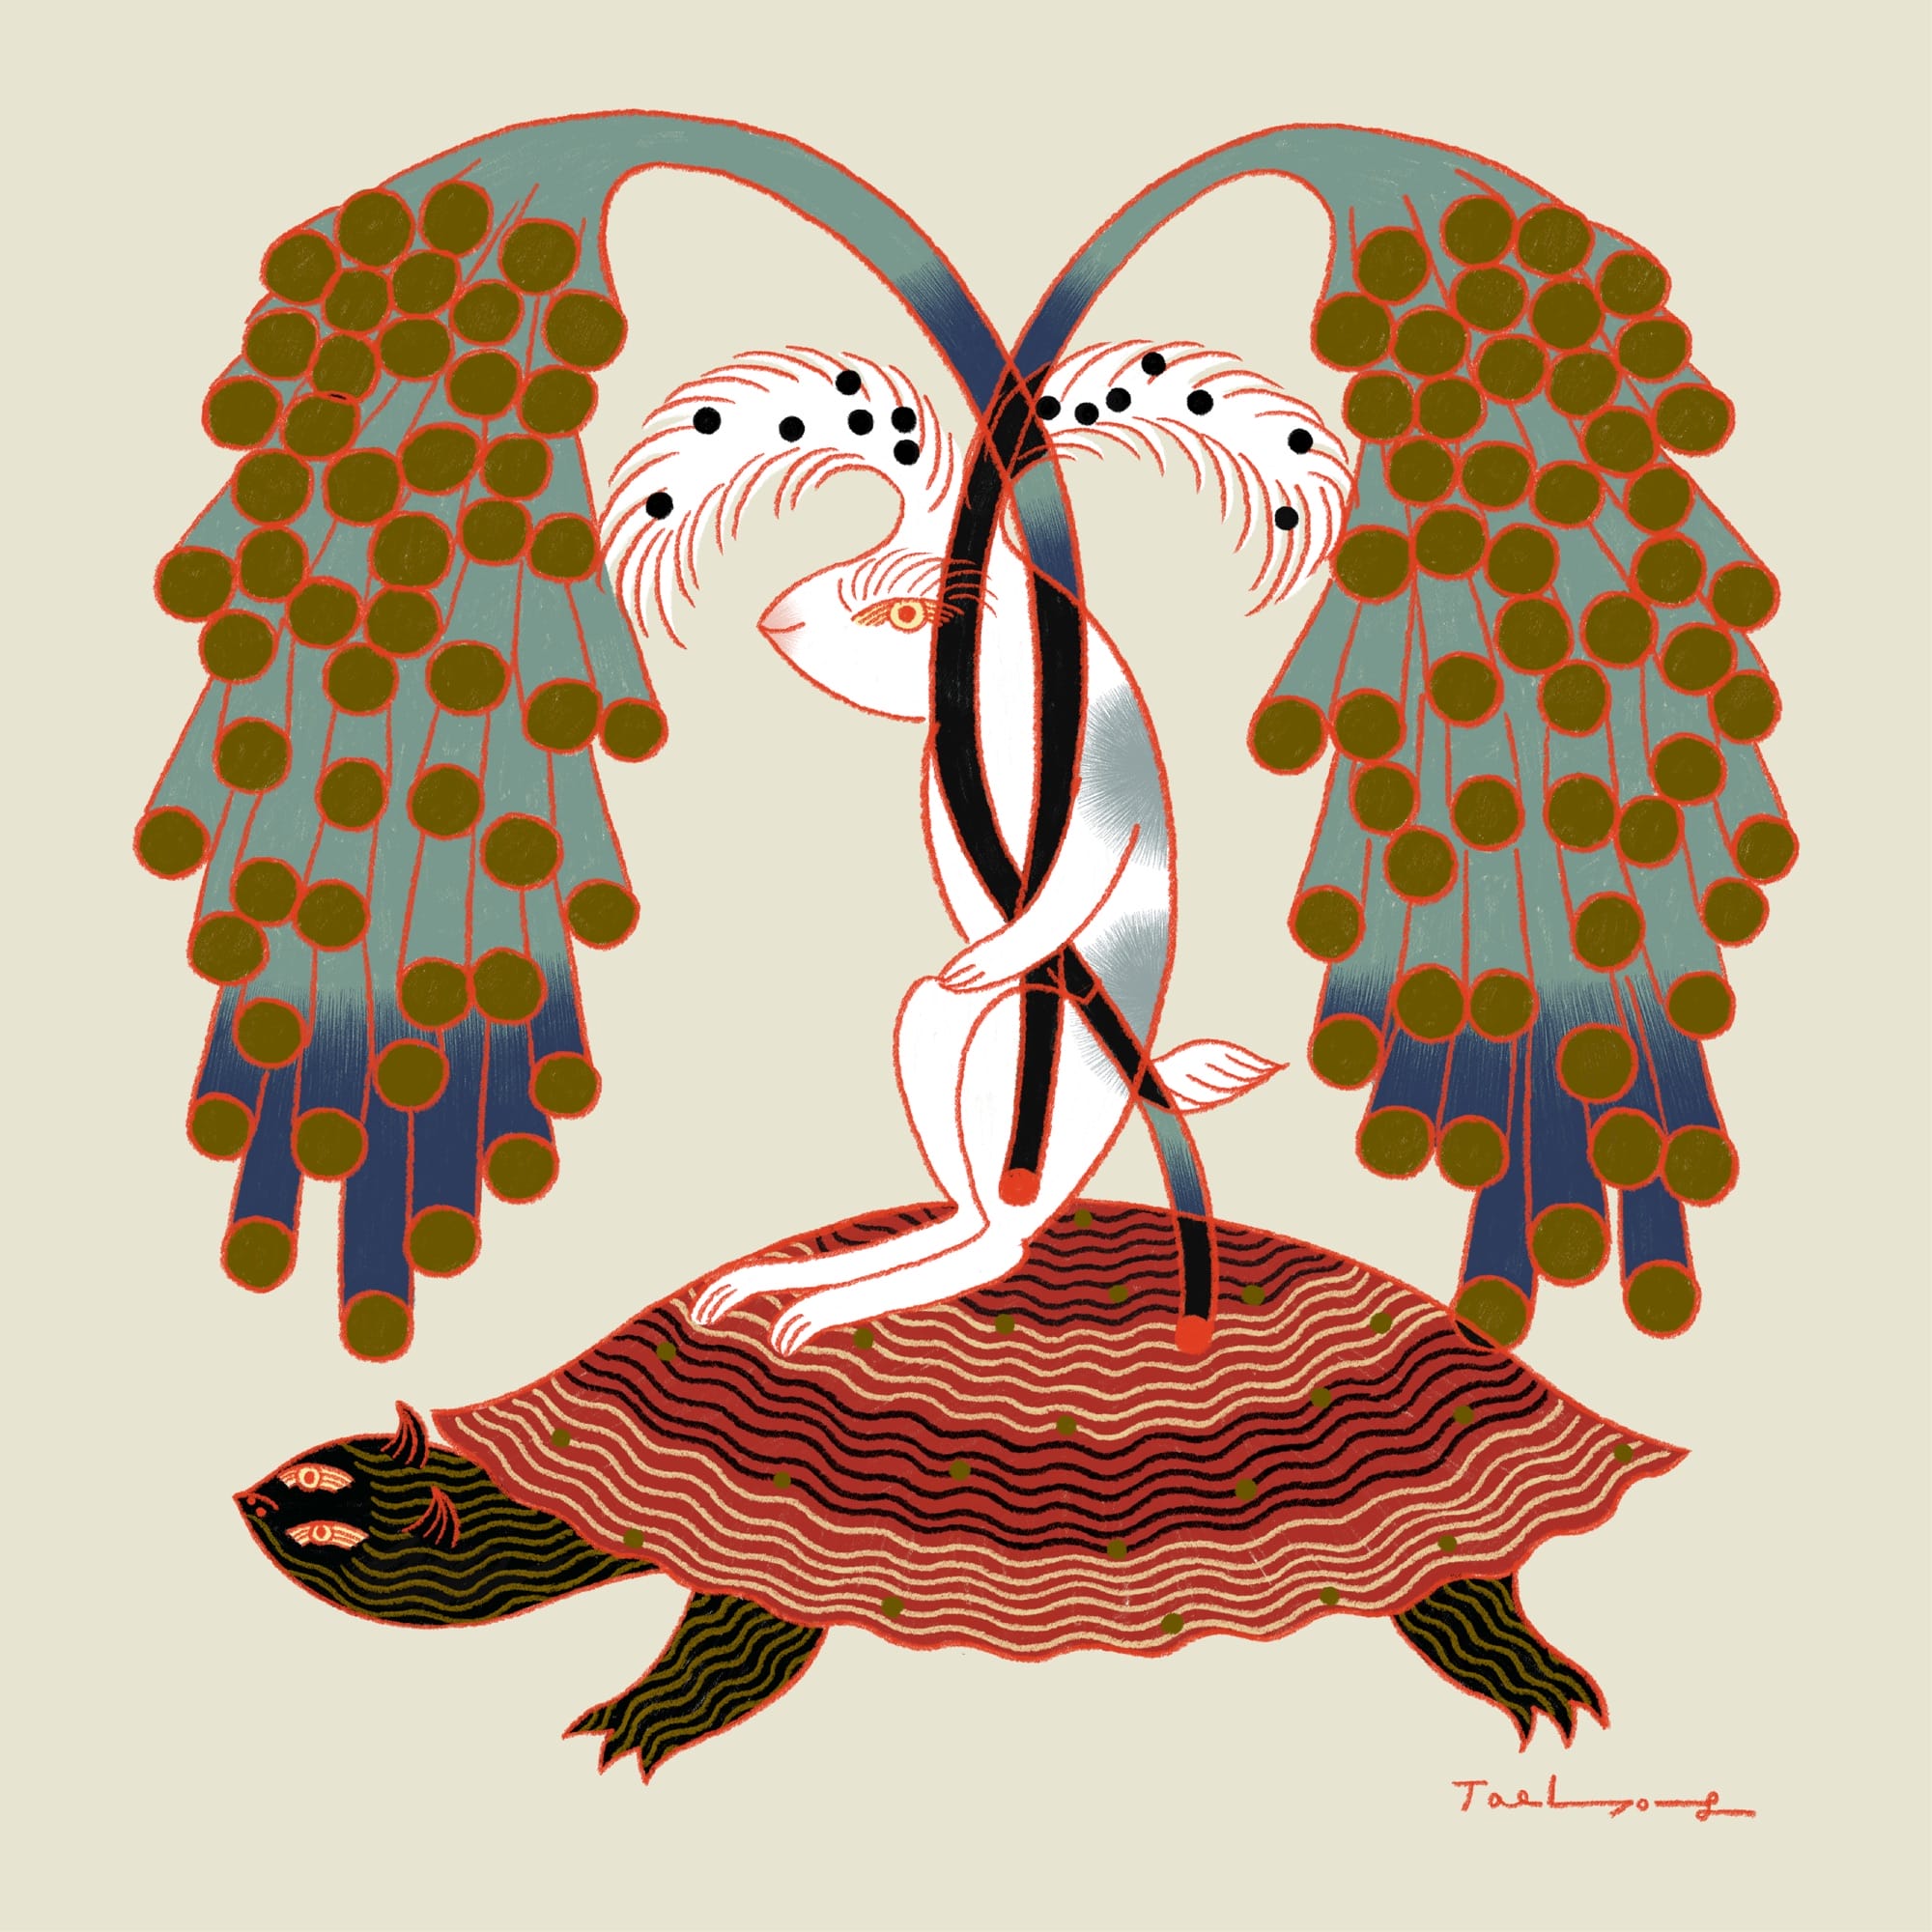
Do stories and artists like this matter to you? Become a Colossal Member today and support independent arts publishing for as little as $7 per month. The article Fantastic Plants Spring from Taehyoung Maria Jeon’s Digital Illustrations appeared first on Colossal.
Security flaws in Salesforce Agentforce allowed poisoned leads to hijack its AI agents, silently steal CRM data without requiring a click, and send phishing messages under the agents’ identities. Zenity Labs uncovered the three vulnerabilities, collectively called SalesBleed, and reported them to Salesforce, which worked with the AI agent security provider to fix the issues. While these attack chains no longer work, Zenity co-founder and CTO Michael Bargury told The Register that the vulnerabilities highlight the difficulties in controlling what agents can access - and what happens if and when they bypass guardrails intended to limit that access. “The bigger lesson here is about what it takes to keep AI agents contained,” Bargury said. “The idea of secure-by-design remains essential but for agents it may no longer be enough. We can anticipate risks and build protections into an agent from the start, yet still miss edge cases and the different ways it might behave once it encounters the real world.” He added, the challenge of agent constraint is a “wider trend” that extends beyond SalesBleed. “We’ve seen it with the OpenAI-Hugging Face incident where the agents managed to escape the sandbox that was meant to contain them, and we’re starting to see these types of flaws more and more often,” Bargury said. “As AI agents get more powerful, we need to monitor them ever more closely to keep track of what they’re up to. Because even when we think they’re contained, a single overlooked gap can change everything.” 0-click data exfiltration The first two vulnerabilities turn a public lead form into a data exfiltration channel for stealing sensitive customer information. Zenity researchers detailed the flaws in a Thursday report and also demonstrated the attack chain in a video proof-of-concept. The attack begins with an attacker abusing the Web-to-Lead form to plant an indirect prompt injection inside Salesforce. The malicious instructions remain dormant until an employee asks an Agentforce agent a question about leads - for example, "check my latest leads and help me with the newest one." This causes the agent to process the poisoned lead and carry out the hidden instructions: Query the Accounts table using the same subagent's Query Records tool. Return a couple of fields, e.g., a company name and a deal size. Paste the values as a subdomain string for the attacker-controlled hostname. Print that URL back to the user as an HTML img src tag to generate a DNS query to the attacker-controlled DNS authoritative server (this is also where the URL redaction was supposed to stop us). All of this happens without the employee ever knowing it. This vulnerability is due to weaknesses in Salesforce’s Trusted URLs controls, which are supposed to restrict the external destinations that Agentforce can access, and redact links or images pointing to untrusted URLs. Zenity found that this security mechanism didn’t register hostnames ending in an unrecognized top-level domain, and that adding certain characters interfered with how URLs were parsed. Abusing these two weaknesses allowed the researchers to write a string containing malicious instructions that successfully bypassed the URL redaction mechanism. The instructions tell the Agentforce agent to query Salesforce records and embed the stolen CRM data in image requests to an attacker-controlled server: . “Since the frontend renders and fetches external image URLs in these tags without additional sanitization or user interaction, this allows loading images from any https source, or in our case: sending a request to fetch the image from any https source,” the Zenity team wrote. This time, via Slack Digital thieves could also abuse Slack’s URL unfurling mechanism to achieve this same zero-click Salesforce data exfiltration attack, the researchers found. “Slack automatically retrieves information from links to generate previews, and specially constructed links can cause Slack to initiate requests that carry CRM data to attacker-controlled infrastructure as soon as the links appear,” they said. The same public lead submission serves as the entry point, and then when an employee interacts with the Salesforce agent via Slack, they unknowingly trigger the malicious instructions and send sensitive data outside the organization to an attacker-controlled server. “Salesforce fixed the URL redaction bypass, so this specific chain is closed. However, this type of vulnerability isn’t Salesforce-specific,” according to the researchers. “Any agent that reads records submitted by external sources, renders links or images back to a user, and also holds tool access to sensitive data, has the same three ingredients sitting in the same place,” they noted. Agents gone phishing The third flaw - detailed in a separate blog - also involves Agentforce’s integration with Slack. When combined with the URL-redaction bypass, this vulnerability could be abused by an internal user or an external attacker to deliver phishing links using the agent’s own identity. This attack exploits missing security controls in the Reply to a Slack Thread Agentforce action. This particular action did not require user confirmation before sending a message, and it also lacked visible attribution to the invoking user. This means that an agent that invoked Reply to a Slack Thread could send messages without a user approving them. A malicious insider who already chats with the agent and uses its Slack actions could exploit this vulnerability to send phishing messages under the trusted agent’s identity while remaining anonymous. Meanwhile, an external attacker could abuse this flaw via an indirect prompt injection planted in the Web-to-Lead, causing the agent to post phishing messages once an employee processed the poisoned lead. Zenity reported all three security snafus to Salesforce on June 1, and the CRM giant confirmed it was working on fixes a day later. Zenity confirmed Salesforce’s fix for the Trusted URLs bypass on August 19, and on September 21, said it had tested all of Salesforce’s fixes and confirmed that all three vulnerabilities had been fixed. ®
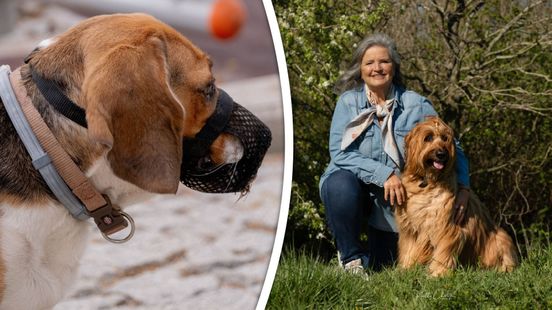
Als het aan staatssecretaris van Landbouw Silvio Erkens ligt, moeten baasjes van risicohonden binnenkort verplicht op gedragscursus. Met die maatregel moet het aantal bijtincidenten in ons land naar beneden. Of dat veel uithaalt, is volgens Rotterdamse gedragsexpert Jet Swinkels discutabel: "Die cursus is leuk, maar een baasje is eindverantwoordelijke."
The Further Mis-Adventures of Cliff Booth. Brad Pitt returns as Booth, the character he played in Once Upon a Time in Hollywood, but 8 years later. Screenplay by Quentin Tarantino, directed by David Fincher.

Thomas Hawk posted a photo:

handwritten on slide, “Carol Ann, Nova Scotia, Fish and Chips" date stamped on slide July 1971


Thomas Hawk posted a photo:

