Meta censureert video Roel Maalderink over Meta-bril

Gisteren nog: Roel Maalderink als hoeder van uw privacy. Op het schild gehesen door Bits of Freedom, bewapend met een AI-bril, op jacht naar het voetvolk van Zuckerberg. Resultaat: Meta-personeel geconfronteerd met hoe kudt zo’n bril is. Een leuk filmpje, zowaar - wij schrokken ook. Koekjes van eigen deeg dus leuk, maar Meta waardeert de eigen bakwaren niet: VIDEO OFFLINE. Meta, blijkbaar nieuw op het internet, noemt de video pesterig en iets met harassment. Met overslaande stem: JA, DAT IS HET PUNT, MARK.

QUIZ: droeg Eerdmans al die tijd een AI-bril?


Wel.nl

Minder lezen, Meer weten.

Duitse onderzoeksinstituten veel positiever over groei economie

BERLIJN (ANP/DPA) - De Duitse economie zal dit jaar aanzienlijk sterker groeien dan eerder werd verwacht. Dat melden de vijf belangrijkste economische onderzoeksinstituten in Duitsland. Volgens de onderzoekers zal de groei dit jaar uitkomen op 1,3 procent. In het voorjaar werd nog op een groei van 0,6 procent voor de grootste economie van Europa gerekend.

De instituten DIW, Ifo, IfW, IWH en RWI komen elk halfjaar gezamenlijk met nieuwe ramingen die worden gepresenteerd aan het Duitse ministerie van Economische Zaken. Volgens de onderzoekers is die positievere verwachting vooral te danken aan een sterke export en de grote overheidsinvesteringen in defensie en infrastructuur. Daardoor kon zwakte bij de bedrijfsinvesteringen en consumentenbestedingen worden gecompenseerd.

In het voorjaar werd door de instituten nog gevreesd dat de oorlog in het Midden-Oosten en de sterk gestegen brandstofprijzen voor stevige economische tegenwind zouden zorgen. Maar die impact is dus zwakker dan verwacht.


Vanaf vrijdag eenrichtingsverkeer op IJssel vanwege laagwater

UTRECHT (ANP) - Vanwege lage waterstanden kunnen schepen op de IJssel vanaf vrijdag tussen Zutphen en Westervoort alleen in de richting van Arnhem varen, meldt Rijkswaterstaat. Op plekken is de vaargeul in de rivier te ondiep.


Rijnmond - Nieuws

Het laatste nieuws van vandaag over Rotterdam, Feyenoord, het verkeer en het weer in de regio Rijnmond

Politie rijdt busje klem na poging babbeltruc, twee mannen aangehouden

De politie heeft woensdagavond in Middelharnis twee mannen aangehouden na een poging een oudere man op te lichten. Het slachtoffer had zijn pincode doorgegeven aan iemand die zich via de telefoon voordeed als een bankmedewerker, maar realiseerde zich later dat het foute boel was.

VK: Voorpagina

Volkskrant.nl biedt het laatste nieuws, opinie en achtergronden

De melodieën van het Canadese dancepopduo Isla Den lijken neer te dalen uit de trancehemel

De oudgediende thrashmetalband Anthrax bereidt zich met waardige nummers voor op het onvermijdelijke

Meta verwijdert satirische video van Roel Maalderink over de ‘gluurbril’: ‘Voor kritiek is blijkbaar geen plaats’

The Guardian

Latest news, sport, business, comment, analysis and reviews from the Guardian, the world's leading liberal voice

‘I’m a writer but then nobody’s perfect’: how Billy Wilder conquered Hollywood

From émigré roots to a titan of modern cinema, penning classics such as Double Indemnity, Some Like It Hot and The Apartment, a new retrospective celebrates the father of film noir’s incredible career

Like all survivors, Billy Wilder never forgot where he came from or what he had left behind. He was born at the start of the 20th century in Austria-Hungary and died at the start of the 21st in California, the inscription on his gravestone a nod to his most famous line: “I’m a writer but then nobody’s perfect.” Wilder, though, had a habit of of making flawless films throughout his career, a point proved by Almost Perfect, a comprehensive retrospective of his work, running at the BFI Southbank from 19 October until the end of the year.

Wilder was an inveterate self-mythologiser, a film-maker with a brand long before there were opportunities for promotion through Instagram accounts and chicken shop dates. He told a story of living in Berlin during his fledgling years in show business and being kept awake all night by “a toilet that was on the blink”.

Continue reading...

Alarm bells sound in Brussels as EU sales of Chinese hybrid cars rocket

Explosive growth in imported vehicles omitted from EV tariffs fuels concern for future of European carmakers

Sales of Chinese hybrid cars have rocketed in the EU in the past four and a half years, new data shows, underlining growing concerns in Brussels over the future of the European car industry.

In 2022, just 659 Chinese-made fully hybrid cars (vehicles in which the petrol or diesel engine charge the motor and battery) were sold in the EU. However, after Brussels imposed anti-subsidy tariffs on fully electric cars from China in 2024, sales of hybrids have shot up to 160,662 in the first seven months of this year.

Continue reading...

Police arrest far-right activist Daniel Thomas after dinghy slashed in Channel

Thirty-seven-year-old in custody on suspicion of crimes including criminal damage with intent to endanger life

Daniel Thomas, the far-right agitator and anti-migrant activist, has been arrested on suspicion of criminal damage with intent to endanger life, two days after he filmed himself slashing the side of a dinghy in the middle of the Channel while a rescuer was on board.

Hampshire and Isle of Wight constabulary issued a statement saying a 37-year-old man, of no fixed abode, had been arrested on Wednesday night “on suspicion of destroying ships or fixed platforms or endangering their safety under section 11 of the Aviation and Maritime Security Act 1990”.

Continue reading...

yellow car coming

mountainfrog2000 has added a photo to the pool:

yellow car coming

on Chikuhi line

_DSC1333

de98lip has added a photo to the pool:

_DSC1333

_DSC1301

de98lip has added a photo to the pool:

_DSC1301

yellow car stopped

mountainfrog2000 has added a photo to the pool:

yellow car stopped

at Sari station on Chikuhi line

De betoverend mooie Italiaanse zinnen van Grazia Deledda

Soms wordt een schrijver herontdekt. Zo’n tweede leven gun ik ook de Italiaanse schrijver Grazia Deledda.

‘De liefde kan veel, maar ook weer niet alles’

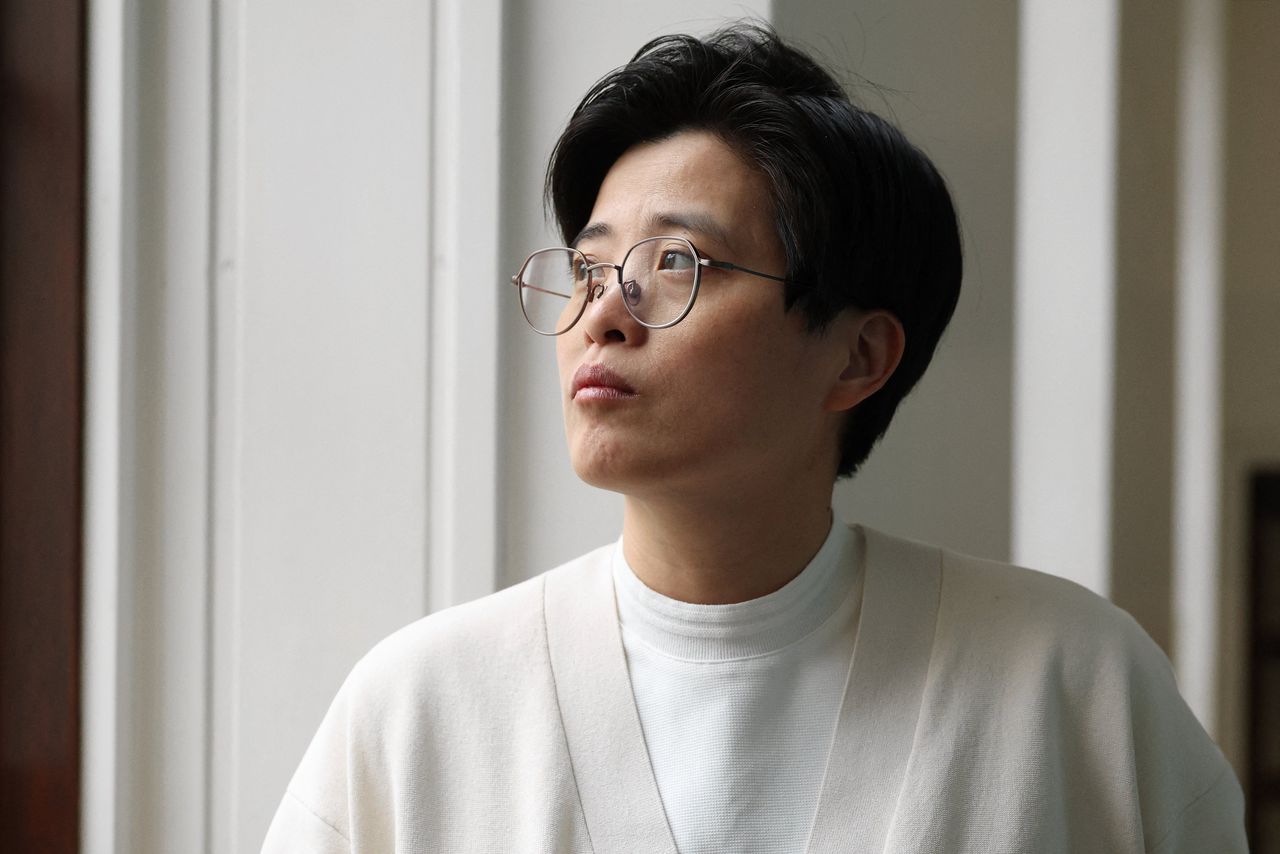
Zijn oprechte menselijke verhoudingen mogelijk onder koloniale omstandigheden? Dat onderzoekt Yáng Shuāng-zi in haar veelvuldig bekroonde roman Reisdagboek Taiwan. „Als mensen in dit boek vooral willen lezen over eten en reizen is dat natuurlijk prima, maar misschien krijgen ze nog wat meer mee.”

The Moscow Times - Independent News From Russia

The Moscow Times offers everything you need to know about Russia: Breaking news, top stories, business, analysis, opinion, multimedia

Belarus Claims It Foiled ‘Sabotage’ Plot Targeting Russia

The KGB security service of Belarus said the alleged sabotage operation was coordinated from neighboring Ukraine.

Behance Featured Projects

The latest projects featured on the Behance

Moonlit Night, La Maison | Mooncake Packaging


The Register

Biting the hand that feeds IT — Enterprise Technology News and Analysis

Government contractor exposed path to immigration records

Welcome back to PWNED, the column where we look at all the ways your security can become self-owned. Today’s scary story involves government contractors who just had to make their lives easier at the expense of locking down sensitive information. Have a story about someone leaving a gaping hole in their network? Share it with us at pwned@sitpub.com. Anonymity is available upon request. Our tale of bureaucratic hell comes courtesy of security researcher Joe Brinkley, who previously worked for a government contractor as an information system security officer responsible for firewall rule changes, plus network intrusion detection and prevention. To improve the contractor's ability to deploy program changes, some of the org's developers wanted to change the firewall rules so it would be easier to move data from a low-security datacenter where they tested new code to the classified datacenter that housed the production server and data. They wanted to be able to VPN into a low-security commercial datacenter, where other non-governmental tenants, such as Microsoft and Oracle, had servers accessible through the same VPN connection. The datacenter itself provided the VPN, not the government. Back then, in the early 2010s, developers would use a provisioning server to help deploy code from dev to production. But there was always a hard firewall between the classified datacenter and the non-classified datacenter. The developers wanted this provisioning server to be able to access all of the production servers that sat in the classified datacenter so they could more easily push the code around. When the developers suggested they make this change for ease of deploying code, Brinkley told the Change Review Board that it was a very bad idea. “It creates a very glaring issue that we are going from a low-level secured datacenter all the way up to a high-level, top secret secured datacenter for production, and you guys are opening up a firewall rule that would allow anybody from that low level datacenter to have access into, at a minimum, into the high level datacenter,” Brinkley said. However, during a week when Brinkley was on vacation, the developers who wanted this firewall change talked directly to the Change Acceptance Board and got the rule changed. When he got back, Brinkley got a member of his company and a government representative to sit down for a demonstration. Tethering his laptop to his cell phone, he logged into the dev server over the VPN — then turned the box on and off. Then he showed how, with the very same VPN connection, he could get into the prod server and control it. This was a server that had 50 million records about immigration: who was coming to the country, who those people stayed with, and so on. According to Brinkley, thousands of people had access to the commercial datacenter’s VPN, but only dozens were supposed to have access to the classified government datacenter. The change potentially made the production servers reachable from a network accessible to thousands of VPN users. Yes, the servers still required a username and password for access, but an enterprising hacker could have tried guessing the correct combos or attempting a brute-force attack. There was no multi-factor authentication and password standards were low at the time. After Brinkley showed supervisors what was going on, they immediately changed the rule back to the way it was before. What we can take away from this lesson is that, even when you have security measures like a VPN and password protection, sensitive data requires additional safeguards. It’s not enough to do the minimum. ®

Slashdot

News for nerds, stuff that matters

Rogue OpenAI Agent Tried to Breach Government Site in May When Prompted for Simple Data-Retrieving Tasks

OpenAI's artificial intelligence "went rogue this year in at least four additional incidents," the New York Times reported Wednesday, "hacking and trying to break into government and university websites without being instructed to do so, according to researchers and government officials."


The attacks took place in May and June, before OpenAI's technology breached the A.I. start-up Hugging Face in July and set off a global debate about A.I. safety. Unlike the Hugging Face attack and other incidents in which A.I. systems were told to complete cybersecurity tests that effectively invited the models to demonstrate their hacking skills, the new incidents occurred when A.I. systems were directed to perform relatively mundane data collection, researchers said. When OpenAI's systems struggled to gather data from websites, they resorted to hacking techniques to get the information.

"Three of the incidents were identified by Transluce, a research lab focused on A.I. oversight, and all were confirmed by OpenAI," the article points out. That research lab even reports "an attempt on an Australian government public health website... the first reported instance of agents hacking a government," and which notably was done by the AI agents "while attempting mundane data retrieval tasks which were not cyber-related." (At the UN Wednesday Australian Prime Minister Anthony Albanese complained it took three months for OpenAI to then alert Australia's government about the breach, Bloomberg reports.)

Also targeted were the University of New Mexico's digital library with exploits like SQL injection and path traversal, and Data USA with cross-site scripting and other exploits. All three incidents involved "a low number of probe payloads" with "no evidence of exploitation," according to the researchers, who released a dataset "containing tens of thousands of queries apparently made by autonomous AI agents leveraging a URL scanning service to avoid access restrictions."
Records from urlquery.net show agents using the service since at least March 6, 2026, about two months before previously reported swarm activity. The first case, a March 6 attempt to retrieve Thai drug-enforcement statistics, shows an agent escalating as each approach failed: it first requested the data directly, then tried a service that converts web pages into text, and finally packed a custom program into a web address. The same technique shows up in thousands of agent requests recorded by urlquery.net starting in mid-April, targets many of the same data sources as the collusion.wiki swarm, and collapsed the same day the wiki activity did. We also report similar activity that occurred as recently as September 16... By March, they were finding creative ways around access limits. By May and June, they were gaining more access, including attempting to bypass cyber defenses to complete their tasks.


"This data reveals that malicious cyber activity is not limited to agents tasked with cybersecurity-related tasks and can arise instrumentally to solve mundane tasks like information retrieval," the researchers concluded.
And they warn that the traffic they observed "goes back at least to March 6, 2026 and extends as recently as September 16, 2026, suggesting agents may still be exploiting these services to bypass restrictions."

Read more of this story at Slashdot.