The Guardian

Latest news, sport, business, comment, analysis and reviews from the Guardian, the world's leading liberal voice

‘You can’t just bet everything on exports’: as its gas runs out, is Bolivia doomed to repeat history?

A fossil gas boom that lifted millions out of poverty has collapsed and inflation is rising – but not everyone believes selling gold and soya is the answer

Once hailed as the “energy heart of South America”, Bolivia’s economy was buoyed up by a fossil gas boom from 2006 to 2014. At its height, then-president Evo Morales commissioned a gleaming presidential skyscraper and installed the world’s longest urban cable car network in La Paz, the seat of government.

Flush with cash, the country grew its GDP, expanded social programmes and halved poverty rates. But then commodity prices plummeted and gas reserves started to dry up, bringing Bolivia’s “economic miracle” crashing down. Inflation – once the region’s lowest – has soared.

Continue reading...

Fury v Joshua fight confirmed for December at Cardiff’s Principality Stadium

  • Fight on 11 December announced by Turki Alalshikh

  • Fury v Joshua to be streamed globally on Netflix

Tyson Fury and Anthony Joshua’s highly-anticipated heavyweight clash will take place at Cardiff’s Principality Stadium on 11 December after a deal was finally agreed.

The details will for the bout, one of the biggest in British boxing history, were announced by Turki Alalshikh, chairman of the General Entertainment Authority and president of the Saudi Boxing Federation, with the tagline: “Years in the making. One night to settle it.”

Continue reading...

George Bush, murder and nautical infidelity: the Chicks’ 20 greatest songs – ranked!

As the country trio once known as Dixie Chicks celebrate 20 years of their album Taking the Long Way, we count down the best of their catchy, sometimes controversial catalogue

One of eight singles released from the album Fly. Amazement at the sheer number should be matched by astonishment at their consistency. If I Fall … is just great. Organ-driven rock lent a Nashville twang by the fiddle, it barrels along, rich with the confidence of a band who know they can’t put a foot wrong.

Continue reading...

Racist abuse of French judo star Teddy Riner investigated after he spoke about rise of far right

Paris public prosecutor opens investigation into online harassment of Riner, one of France’s most popular sportspeople

Paris’s public prosecutor has opened an investigation into the racist abuse and online harassment of the French judo star Teddy Riner after he expressed concern about the rise of the far right.

Riner, who has often been voted France’s most popular sportsperson and is one of the most successful judo competitors of all time, told a TV sports show this month that he felt “anxiety” about the rise of the far right in France. Numerous racist insults and hate messages were subsequently directed at him online, the prosecutor’s office said.

Continue reading...

The Register

Biting the hand that feeds IT — Enterprise Technology News and Analysis

Google to critical infra orgs: Our AI scanners won't be evil, promise

Google has jumped on the AI-defense-for-critical-systems train with its Scan for Good initiative, and says that its threat-hunting models have already autonomously uncovered critical security issues at hospitals, a municipality, a public rail operator, and major technology providers. So don't fear these bots. The initiative, announced on Thursday, uses Google’s Gemini 3.8 Flash Cyber, a version of the model tuned for software bug hunting and remediation, and Wiz’s Red Agent - this is the Google-owned cloud security shop’s pentesting AI agent. The AI systems will uncover public exposures and attack paths across public services, critical infrastructure, and nonprofits, and then hand these off for verification and remediation to human security researchers. “The program has been active over the past several months, and with this official launch, we are scaling it globally,” Gal Nagli, head of offensive security at Wiz, told The Register. “There is no set end date.” It's similar to OpenAI’s Daybreak for Frontline Defenders initiative, announced earlier this month. This program will distribute $1 billion in credits to subsidize access to OpenAI services and training for resource-strapped cyber defenders, including those protecting water and energy systems, community banks, local governments, nonprofits, and open-source projects. And like OpenAI’s new program, the Wiz and Google DeepMind partnership follows disclosures that Google’s AI agents also escaped their sandboxes and hacked other companies’ websites - as did agents developed by OpenAI, Anthropic, and Meta, and those are just the ones we know about. It also comes as existential dread about AI killing all of humanity reaches a fever pitch. AI for good (not evil) Scan for Good aims to put offensive security agents and Gemini 3.8 Flash Cyber to good, not evil, use. When authorized, either explicitly by organizations that apply for an assessment or under applicable bug bounty programs and vulnerability disclosure policies, the AIs will examine publicly facing websites, APIs, and applications for exposures, and then work with organizations to find and fix these. Every potential finding will be reviewed and validated by a human, and Wiz assures that “humans will remain responsible for confirming impact and making disclosure decisions.” When the bots and humans do identify a serious issue, the humans will contact the affected organization and work with them to remediate the security holes. Google’s AI systems have already helped critical organizations and tech providers find serious, internet-facing risks, including a critical GitHub Actions workflow vulnerability in one of Snowflake’s public repositories. In this bug-hunting expedition, conducted through Snowflake’s HackerOne vulnerability disclosure program, Wiz’s Red Agent autonomously identified a script injection vulnerability in snowflakedb/snowflake-connector-net. The flaw allowed an unauthenticated user to execute arbitrary commands within a GitHub Actions runner by opening a GitHub issue with a specially crafted title. Wiz disclosed the issue on June 23, and Snowflake fixed it on the same day, rotated the affected credential, and verified through detailed audit logs that Wiz was the only actor during the exposure window. Real-world examples The Google-owned biz provided several other examples of its AI for good, and said all of these were autonomously discovered by the models before Wiz validated them, but “only far enough to confirm real-world impact.” At that point, they privately notified the affected organization about the issue and helped it remediate the vulnerability. Some of these include: An exposed administrator key enabled read, write, and delete access to 8.8 million files in a “nationally significant archive” belonging to an unnamed Middle Eastern country. Assigning the correct set of permissions fixed the flaw. A public hospital with missing access controls exposed staff contact information and gave anyone online control of a hospital-wide mobile alert channel. A private hospital’s public appointment-booking site used an unsafe upload method that would have allowed attackers to take control of a hospital server and obtain patient identifiers, clinical information, and consent signatures. A municipality’s public data service exposed sensitive personal, health, and financial information belonging to about 5,000 elderly residents. Wiz confirmed the risk without collecting a bulk dataset. A public rail operator had a leaky production database that exposed active administrator sessions. This could have allowed criminals to take control of routes, schedules, service announcements, and administrator accounts - essentially disrupting the entire transportation system. Wiz helped the operator secure the system. The US Cybersecurity and Infrastructure Security Agency (CISA) also gave Scan for Good its stamp of approval, and Wiz told us the American cyber-defense agency provided guidance on the initiative. “At a time of evolving threats, defensive vulnerability discovery helps strengthen the nation’s digital infrastructure,” CISA acting director Nick Andersen said in a statement. ®
City council may be waking from its Oracle nightmare but the accounting hangover continues

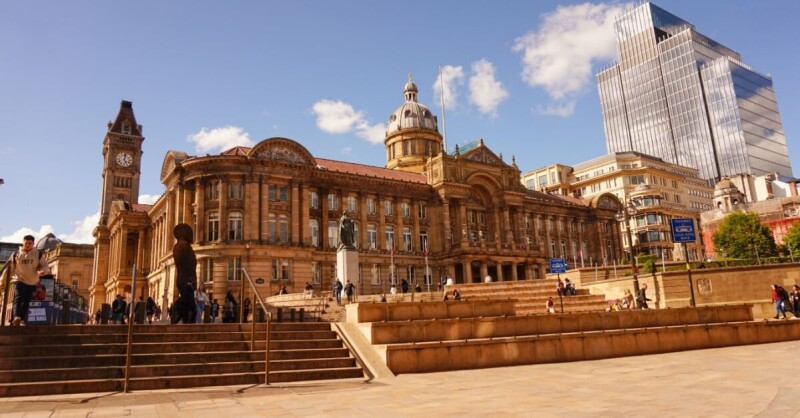
Europe's largest local authority will go at least one more financial year without auditors being able to vouch for its accounts despite finally reimplementing Oracle Fusion. Grant Thornton expects Birmingham City Council to receive "disclaimer opinions" for 2025/26, 2026/27, and 2027/28 due to problems with historic data. A disclaimer opinion means the auditor cannot obtain enough evidence to express an opinion on the financial statements. It does not mean the council failed to produce accounts, but it leaves stakeholders without independent assurance that those accounts are reliable. A report from the auditor said the council's transition to a rebuilt Oracle Fusion-based HR and finance system in August had been largely successful. It added that the "reimplementation appears to have been better managed than the original 2022 implementation." Council taxpayers might hope so. The first implementation of Oracle Fusion left the council unable to reconcile its bank accounts or reliably understand its cash position, and contributed to the crisis that preceded its effective bankruptcy. The total project, including the reimplementation, is set to cost around £144.4 million against an initial estimate of £20 million. Including forgone efficiency savings, researchers have estimated the cost could reach £216 million. Its early performance contrasts sharply with that of the original system, known as 1B, which went live in April 2022. "There are no outstanding business-critical or priority level 1 or 2 tickets or issues. For context, relating to the old 1B Oracle system in September 2025 there were 311 open tickets and 2 major incidents," the report said. Nonetheless, the council is not expected to regain a clean audit opinion before 2028/29 – roughly a decade after the Oracle program began. The council picked Oracle Fusion to replace its legacy R/3 SAP system and initially planned to go live in December 2020 for finance and procurement, and in February 2021 for HR and payroll. A 2021 business case subsequently moved both launches to April 2022. Although the council had planned to implement Oracle "out of the box," it introduced several customizations, including a bank-reconciliation design that failed to function properly. The council struggled to understand its cash position and could not provide auditors with sufficient evidence to verify its accounts. It has spent more than £5 million on manual workarounds. ®

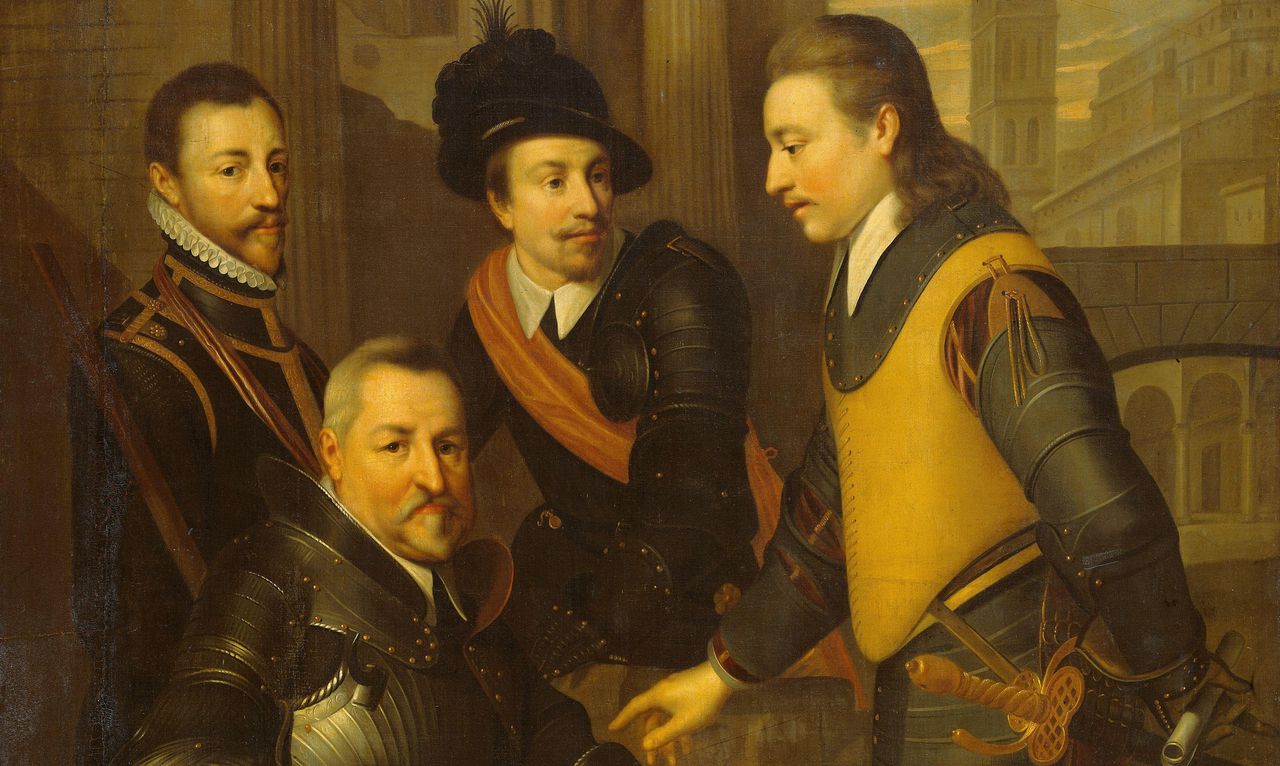
De Nassaus runnen hun dynastie al eeuwen als een familiebedrijf. ‘Voor elke generatie is de opvolging een stresstest’

De geschiedschrijving over vorstenhuizen gaat vaak over staatsvorming. Jasper van der Steen besloot het anders aan te pakken. Hij keek naar de Nassaus als een familiebedrijf.


BNNVARA haalt documentaire Verstoten vaders offline; strafeis van 24 maanden tegen hoofdrolspeler

De film Verstoten vaders is offline gehaald, nadat bekend is geworden dat hoofdrolspeler Armand S. wordt vervolgd voor intieme terreur. Het OM beschrijft een patroon van stalking en dwingende controle over een „heel lange periode”.

‘Uiteindelijk zijn we toch allemaal maar sukkels die het ook niet echt weten’

Als scholier las Sander Heijne (44), hoofdredacteur van Vrij Nederland, Figuranten van Arnon Grunberg. ,,Het cynisme is me op mijn vijftiende eerlijk gezegd een beetje ontgaan.”

De lelijke ingrepen worden steeds urgenter

Het gebeurt veel in Europa: een politicus weggooien zodra die begint te verliezen. Meelijwekkend, vindt Rosanne Herzberger, maar zeker ook bedreigend. Tijd om een voorbeeld te nemen aan Australië.

Hier in de VS zijn de verschillen tussen arm en rijk astronomisch. Nederland moet daarvan leren

Als arbeid structureel zwaarder wordt belast dan vermogen, belandt er vanzelf teveel rijkdom en macht bij een kleine groep, ziet voormalig staatssecretaris Marnix van Rij. De Box-3-kwestie is een kans voor de Nederlandse politiek om daar iets aan te doen.

VK: Voorpagina

Volkskrant.nl biedt het laatste nieuws, opinie en achtergronden

Vooruitblik VN-top dag drie: Palestina, Israël en Nederland

Kan Nike met Die Mannschaft een comeback maken?

Trump negeert vonnis: journalisten van Politico, CNN en MS NOW toegang geweigerd tot Witte Huis

Stone fox at a shrine in Aomori

Sergiy Galyonkin has added a photo to the pool:

Stone fox at a shrine in Aomori

A stone fox with a red bib and traces of gold leaf at a shrine in Aomori, Japan.

_NZ71138

richtebw has added a photo to the pool:

_NZ71138

_NZ71112

richtebw has added a photo to the pool:

_NZ71112

Wel.nl

Minder lezen, Meer weten.

Alcaraz wil af van nachtelijke tenniswedstrijden op grandslams

LONDEN (ANP/AFP) - Als het aan Carlos Alcaraz ligt worden er geen nachtelijke tenniswedstrijden meer gespeeld op grandslamtoernooien. Dat zei de Spaanse toptennisser donderdag tegen verslaggevers in Londen in aanloop naar de strijd om de Laver Cup van komend weekend.

Alcaraz, die dit seizoen maanden aan de kant stond met een polsblessure, maakte enkele weken geleden op de US Open zijn rentree. De Spaanse titelverdediger verloor begin deze maand de kwartfinale in New York van de Amerikaan Ben Shelton na een nachtelijke vijfsetter. De wedstrijd was na ruim vier en een half uur om iets na 03.30 uur afgelopen.

"Voor een sporter die om 03.30 uur 's ochtends klaar is, betekent dit dat we om 04.30 uur de baan moeten verlaten en terug naar het hotel moeten," legde hij uit aan verslaggevers. "Je gaat pas om 06.30 of 07.00 uur 's ochtends naar bed. Zelfs een wedstrijd die om 00.00 uur eindigt, is al te laat."

Wimbledon hanteert een eindtijd van 23.00 uur, maar de US Open, Roland Garros en de Australian Open kennen geen vastgestelde tijd waarop wedstrijden moeten worden gestaakt.


De Speld

Uw vaste prik voor betrouwbaar nieuws.

Duizenden mensen doen maar één onderdeel van Hyrox

​Elk weekend is het weer raak: duizenden mensen die te beroerd zijn om een volledige Hyrox-race te doen, en slechts één onderdeel van de fitnesswedstrijd uitvoeren. Sterker nog: dat hardlopen doen ze ook nog eens helemaal verkeerd, want ze lopen vaak veel te ver door. Afgelopen zondag stond Amsterdam nog bol van de mensen die de Hyrox-reglementen niet leken te begrijpen, dit weekend worden er in Groningen nog meer misverstanden verwacht.

“Geen Sandbag Lunges, geen Burpee Broad Jumps, zelfs geen Sled Pull”, zegt Hyrox-fanaat Jayro (33) hoofdschuddend. Hij kijkt naar een groep mensen die al kilometers achter elkaar aan het rennen is. “Dat is dus niét de bedoeling. Na de eerste kilometer hadden ze meteen stoppen voor de SkiErg. Het is toch geen hogere wiskunde?”

“Het begint al bij de faciliteiten”, vervolgt Jayro kritisch. “Ze rennen allemaal buiten. Waarom? Zie maar eens een Concept2 roeimachine te vinden op een rotonde in Spijkenisse of Den Haag, dat is vragen om problemen. Het lijkt wel alsof ze het niet wíllen snappen. Zonde hoor, want ze hebben allemaal een prima conditie. Die mensen zijn allemaal hartstikke tevreden als ze snel die kilometers gerend hebben, maar volgens mij weten ze niet dat zo’n tijd helemaal niet telt bij Hyrox.”

​

&


Behance Featured Projects

The latest projects featured on the Behance

Drawing 9.21.2026