Rijnmond - Nieuws

Het laatste nieuws van vandaag over Rotterdam, Feyenoord, het verkeer en het weer in de regio Rijnmond

Twee jongens (15) opgepakt voor gewapende overvallen

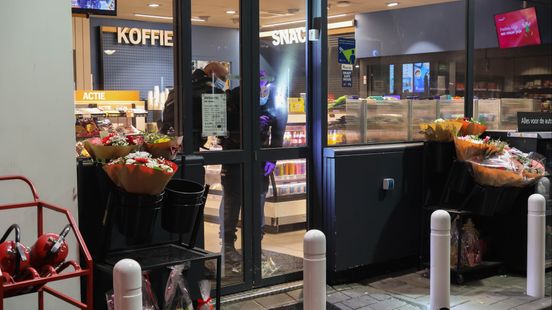
De politie heeft twee 15-jarige Rotterdamse jongens aangehouden voor hun betrokkenheid bij een gewapende overval. De twee overvielen op 13 mei samen een tankstation aan de Tjalklaan in Rotterdam-Delfshaven. Een van de twee jongens kwam op 9 juli terug voor een tweede overval.

Politie pakt twee 15-jarige jongens op voor twee gewapende overvallen

De politie heeft twee 15-jarige Rotterdamse jongens aangehouden voor hun betrokkenheid bij een gewapende overval. De twee overvielen op 13 mei samen een tankstation aan de Tjalklaan in Rotterdam-Delfshaven. Een van de twee jongens deed op 9 juli nog een tweede poging op dezelfde plek.

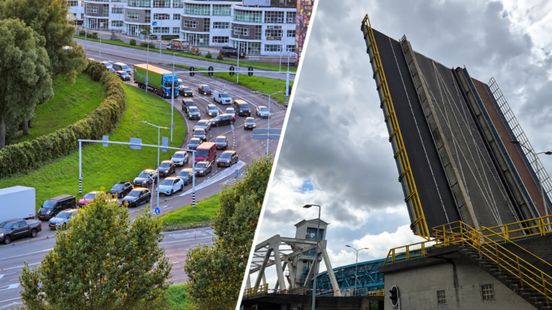
Algerabrug weer open na technische storing van meer dan een uur

De Algerabrug kampte dinsdagavond met een flinke technische storing. Iets na 18:30 uur ging de brug open voor een schip en de klep ging pas weer rond 19:45 uur dicht. De N210 was dan ook lange tijd in beide richtingen afgesloten.

De Speld

Uw vaste prik voor betrouwbaar nieuws.

Door gebroken nek belandde Gen Z’er Disa in doodenge situatie: bellen met 112

​De 17-jarige Disa belandde dit weekend in een doodenge situatie waarbij een vrouw haar nek brak en zij moest bellen met 112. “Het was echt heel, heel erg eng.”

De vrouw, die rustig aan het wandelen was over straat, werd geschept door een auto en vloog door de lucht tegen een gebouw aan; overal zat bloed en het hoofd van de vrouw lag in een gekke knik. “Ik zag het ongeluk gebeuren en ik voelde eigenlijk gelijk paniek”, vertelt Disa die rilt bij de herinnering. “De impact van de auto was enorm en toen de auto ook nog eens hard doorreed, kon ik nog maar aan één ding kon denken: een telefoontje naar 112 is onvermijdelijk.”

De tiener vertelt dat zij eerst nog probeerde of de vrouw niet zelf kon bellen. “Ik zag dat zij nog ademende dus ik probeerde haar wakker te schudden, maar zij reageerde maar niet. Haar nek leek eigenlijk alleen maar schuiner te gaan hangen. Ook schreeuwen hielp niet. Toen een lange wandeling door de buurt, opzoek naar andere mensen, ook niets opleverde wist ik dat er geen andere optie meer was.”

“Met trillende vingers heb ik het nummer ingetoetst. Tussen het kokhalzen door heb ik uiteindelijk in steekwoorden uit kunnen leggen wat er gebeurt was. Het was balen dat de vrouw niet meer leek adem te halen, was het bellen toch helemaal voor niets.”

​

&'


VK: Voorpagina

Volkskrant.nl biedt het laatste nieuws, opinie en achtergronden

Contact is een voorwaarde voor kennisoverdracht

Steeds meer Republikeinen keren zich af van Trump: ‘Zelfs rode staten zijn niet veilig tijdens de midterms’

Verblinde Netanyahu handelt als een kat in het nauw en voert Israël richting een totaal isolement

Indrukwekkend goed, in veel opzichten beter dan het origineel

De Iraanse advocaat Nasrin Sotoudeh wil als het om mensenrechten gaat van geen wijken weten

Nederlanders steeds vaker dood na val

FOTO: Nederlander (nog niet gevallen)

oudere met rollator

Kunnen we dan helemaal niks meer? Zo moeilijk is het toch allemaal niet, gewoon een beetje BLIJVEN STAAN. En anders lopen of zitten, desnoods liggen. Nee hoor, moeten we niks van weten, gooien we meteen de kontjes tegen de krib (dat kunnen we wél). Vallen is wat we doen (SCHWALBE), en daarna ook nog eens massaal sterven (GEEN SCHWALBE), zo blijkt uit cijfers van het CBS. Vorig jaar gingen 7810 mensen deaud na een val-, glij- of struikelpartij, liefst 480 meer dan een jaar ervoor. We zijn dus ergens beter in geworden waar we helemaal niet beter in geworden moeten zijn. We zitten nu op 21 valdoden per dag. Mag gerust een vallende ziekte-plaag heten, waarmee de onwelwillende minderheid het hier verpest voor de meerderheid die wel gewoon normaal doet. Nou vallen vooral ouderen, en door de vergrijzing worden dat er nou net steeds meer, waardoor de vallers straks nog in de meerderheid zijn ook. Hoe denken die ouderen dat het mensen die niet vallen bevalt dat ze continu gespannen moet waken voor een instabieltje dat ineens met z'n bakkes door het met taartjes bezaaide glazen tafeltje kan klappen? En maar janken over eenzaamheid.

thexiffy

Last.fm last recent tracks from thexiffy.

Asian Dub Foundation - Naxalite

Asian Dub Foundation

The Guardian

Latest news, sport, business, comment, analysis and reviews from the Guardian, the world's leading liberal voice

No explosives found in three vans searched near RAF Fairford, say police

Head of counter-terrorism policing defends decision to bail five British men arrested in connection with incident

No explosive devices were found in three vans searched near RAF Fairford as part of a terrorism investigation but a quantity of petrol was recovered, police have said.

Five British nationals were arrested in the early hours of Sunday morning after a resident living near the Gloucestershire airbase reported suspicious activity involving three vans.

Continue reading...

Justitieminister Van Weel gaat kijken of surveillance-apps zoals mSpy verboden kunnen worden

Minister David van Weel (VVD) is zich „rot geschrokken” over het onderzoek van NRC waaruit bleek dat de app mSpy wordt gebruikt om (ex-)partners te stalken. Daarom wil hij met de Autoriteit Persoonsgegevens in gesprek over het verbieden van zulke surveillance-apps.

Voor één begroting is nu steun gevonden. Daarmee zijn de kabinetsperikelen nog niet van tafel

Over de begroting van het ministerie van Sociale Zaken en Werkgelegenheid wist het kabinet-Jetten een deal te sluiten, door alle bezuinigingen te schrappen – zonder duidelijke dekking. Voor andere pijnpunten – zoals box 3 – is een meerderheid nog niet zeker.

The Register

Biting the hand that feeds IT — Enterprise Technology News and Analysis

Custom malware used in Citrix 0-day attacks targeting govt, banks, professional services

The public still doesn’t know who is abusing a critical Citrix vulnerability exploited as a zero-day weeks before disclosure, but we now know that the unknown digital intruders have used CVE-2026-88772 to break into government agencies, financial services firms, education organizations, and legal and professional services sectors across North America and Europe. And everyone agrees that the vendor took way too long to disclose the security holes. GreyNoise said it spotted an attempt to exploit CVE-2026-88771 against a Citrix NetScaler Gateway on September 24. Google researchers, meanwhile, said the CVE-2026-88772 campaign has been ongoing “since at least early September.” “Why Citrix took so long to disclose these vulnerabilities is a question only Citrix can answer,” Benjamin Harris, founder and CEO of exposure management firm watchTowr, told The Register. Citrix did not respond to our questions about this. “The vulnerabilities were discovered during incident response and forensic investigations at organizations already compromised, meaning both the exploitation and Citrix’s awareness of it predated public disclosure,” Harris said. “Citrix has a history of delaying the publication of vulnerabilities, even when they’re being exploited in the wild and affecting customers.” So if you use Citrix NetScaler ADC and NetScaler Gateway appliances, and haven’t already applied the security updates, do that ASAP. But first, check your systems for signs of compromise, warns Mandiant Consulting CTO Charles Carmakal. “Given the active exploitation, NetScaler customers should prioritize examining their systems for compromise *before* upgrading/patching,” Carmakal said on LinkedIn. “If you find evidence of web shells or other malicious files, please preserve evidence and investigate the scope of the compromise. Patching alone may not eradicate the threat actor from your environment.” No attribution - yet Citrix disclosed eight CVEs on Sunday with the worst of the bunch – CVE-2026-88771 and CVE-2026-88772 – earning critical 9.5 CVSS scores. “Exploitation of CVE-2026-88771 and CVE-2026-88772 on unmitigated NetScaler deployments has been observed,” the vendor said. CVE-2026-88771 can allow an unauthenticated attacker to execute arbitrary commands remotely. CVE-2026-88772 is a memory overflow vulnerability that can lead to remote code execution or denial of service when DTLS is enabled, as it is by default on VPN virtual servers. But by the time Citrix issued security advisories and warned customers about the vulnerabilities, they were already under attack. “No attribution has been made public, and we have yet to identify a clear trend among targets by industry or organization size,” Harris said. “Historically, NetScaler vulnerabilities have been exploited by both state-sponsored groups and ransomware operators.” WatchTowr on Tuesday published a technical writeup about CVE-2026-88772, plus a detection artifact generator for Citrix users to determine if they are vulnerable and to help with remediation. Also on Tuesday, Google’s threat intel businesses provided additional details about the exploitation campaign’s targets and the attacker’s custom malware. “We have observed evidence that organizations in North America and Europe in the government, financial services, education, legal and professional services sectors were likely impacted by this exploitation campaign, which has been ongoing since at least early September,” Google Threat Intelligence Group and Mandiant said in an advisory. Custom malware After analyzing the intruder’s post-exploit toolkit, the malware hunters found never-before-seen malware used to establish persistent root access and proxy traffic into internal corporate networks. The custom malware includes WHIPSHOT, a PHP web shell, and SLAPSHOT, a TCP tunneling tool written in Python. WHIPSHOT is disguised as a Debian package and hides Base64-encoded command-and-control payloads in native HTTP headers. It functions as an HTTP transport bridge for SLAPSHOT, which accepts commands from WHIPSHOT and forwards arbitrary TCP streams to internal hosts. Supported commands include: open, which establishes an outbound TCP socket to a target host and port. push, which writes data to an open session. pull, which polls and reads data from an open session socket. exch, which sends and receives command-and-control data to and from an open session socket. close, which terminates a specified network session. ping, which performs a basic health-check verification. “In at least one observed intrusion, the threat actor routed traffic through this proxy to manually conduct internal reconnaissance and credential theft,” the threat intel teams noted. Google did not immediately respond to The Register’s questions about the campaign, including how many exploitation attempts and successful intrusions its threat hunters observed. Its advisory notes that the Citrix campaign “underscores the continued targeting of edge devices to gain initial access to victim networks, a trend that GTIG has tracked across a range of threat actors.” Security and networking vulnerabilities accounted for about half of enterprise-related zero-days in 2025, according to Google’s count. Attackers love edge devices - application delivery controllers, VPN gateways, and firewalls - because they provide direct access from the open internet to corporate networks, allowing attackers to bypass endpoint detection tools and other security layers. NetScaler, in particular, is notoriously buggy. Attackers exploited another critical NetScaler vuln in March. A year earlier, Citrix disclosed multiple zero-days in the same product. ®
kottke.org

Jason Kottke's weblog, home of fine hypertext products

What’s On Your To-Do List?

I keep a list of things I want to do for KDO in Apple Notes, organized into four sections: small, medium, large, and longshots/obsolete. This note contains tweaks, bug fixes, code refactoring, new site features, roadmap items,1 infrastructure migrations, potential project ideas, vague prompts, and even things I don’t want to do but should maybe consider doing anyway at some point. I keep already-completed items on the list so progress can be gauged, noticed, and appreciated.

I was looking at the list today, and thought I’d share some of the items with you:

  • Reposting social posts (in comment threads) for members
  • Do a podcast
  • Publish posts to Instagram. (How?)
  • Implement site-wide search
  • Make newsletter daily?
  • Write a book based on kottke.org
  • Sell Blue Line Air Express t-shirts
  • Build a Substack competitor
  • Make a gift link search engine

Some of these are partly finished or would take very little to implement if I wanted. Some will never happen. Weirdly, some of the projects and site tweaks I most want to make aren’t even on my list. They live only in my head and I mull them over in the shower or while walking until they’re “done” enough to start working on. I guess maybe ideas don’t go on the list unless they’re not that urgent or interesting.

Do you have to-do lists for your creative projects? Care to share an item or two with the group?

  1. Insofar as KDO has a roadmap, which is somewhere between “not at all” and “a general direction into the murky haze of a possible future”. I play things by ear a lot. ↩

Tags: kottke.org · lists

Drive by Melbourne - wave building

braart has added a photo to the pool:

Drive by Melbourne - wave building

Outoff focus

Nomenclature

I got a used Mac Mini to use as a sacrifice zone for testing things on recent OSes. Since at this point it seems like you will pry macOS 14.7 from my main machine's cold dead fingers.

Anyway I can't decide what to name it. I'm going with "sucker" so far. I thought about "patsy" but that just makes me think "and edina" which is not what I'm going for.

It sits next to "retro", the Intel i7 10.13.6 Mini that still exists solely so I can run Illustrator CS6. (VirtualBox emulation is too slow.)

Wel.nl

Minder lezen, Meer weten.

Politie VK: geen explosieven aangetroffen in busjes bij RAF-basis

LONDEN (ANP) - In het onderzoek naar het voorval van afgelopen weekend bij RAF-luchtmachtbasis Fairford zijn geen explosieven aangetroffen. Dat meldt de antiterreurbrigade van de Britse politie, die eraan toevoegt dat er ook panden in Londen zijn doorzocht. Vijf verdachten, allen Britten, werden eerder op borgtocht vrijgelaten.

De vijf werden zondag niet ver van de vliegbasis opgepakt, op verdenking van het schenden van de explosievenwet en het willen begaan van een terroristische aanslag. Een omwonende, die hen tegenkwam na een avond uitgaan, tipte de politie. Na de melding werd in allerijl opgeschaald en onder meer de explosievenopruimingsdienst ingeschakeld. Onduidelijk was toen nog of er explosieven lagen in de busjes van de verdachten.

De dienst meldt dinsdag dat er weliswaar geen geïmproviseerde explosieven zijn aangetroffen, maar wel vloeibare brandstof in beslag is genomen. "De voertuigen zijn uitvoerig gecontroleerd, met behulp van militaire middelen en forensisch experts", aldus de dienst.

Vrijlating

Over de vrijlating van de verdachten wordt gezegd dat dit een "onderzoeksmatige keuze" was, "gegrond in ervaring en zorgvuldige overweging van de politionele bevoegdheden". Maandag werd al bekend dat de voorlopige vrijlating niet betekent dat de vijf geen onderdeel meer uitmaken van het onderzoek.

Aanvankelijk klonk het maandag in Britse media dat omwonenden meer verdachten hadden gezien dan slechts de vijf arrestanten. Vooralsnog is onduidelijk of dit klopt en of de politie inderdaad meer verdachten in het vizier heeft.


Slashdot

News for nerds, stuff that matters

Florida Invokes Extinction Fears In Legal Bid To Halt OpenAI Development

An anonymous reader quotes a report from Ars Technica: The state of Florida is seeking a temporary injunction to stop OpenAI from continuing to develop what it calls a "reckless, unacceptably risky product" without the deployment of "third-party approved safety guardrails." The new legal motion (PDF), filed Monday morning, is part of a civil lawsuit the state of Florida originally filed in June, arguing that ChatGPT represented "a threat to the public safety of Floridians," specifically by preying on vulnerable populations like children and violent or delusional adults. [...] In arguing for this injunction, the state points to the Hugging Face incident as well as recent high-profile misalignment cases involving unintended and unauthorized attempts to access Australian and US government servers. Florida also cites AI industry leaders, including many from OpenAI, in arguing that the AI industry is literally asking for this kind of outside regulation.

The motion points to statements from Paul Christiano, who said on joining the company's board this month that he believes "there is a meaningful risk that rapid acceleration in AI capabilities leads to catastrophic and irreversible loss of control in the very near term." The motion also points to OpenAI's own "An Alien Mind" essay and an open letter from 1,300 AI industry employees, both of which call for enforced slowdowns on frontier AI development, if necessary. Citing laws that allow the state to exercise control over companies that are a "public nuisance," Florida argues that OpenAI is "the greatest public nuisance ever created by the hand of man, capable of laying waste to global civilization." "It is only by the grace of the Almighty that one of Defendants' AI agents hasn't compromised a water supply or shut down a power grid -- yet," the state writes in the motion.

Read more of this story at Slashdot.