Portugal pull away to 4-2 win in Denmark
Jürgen Klopp’s Germany beat Serbia 2-0
Portugal maintained their perfect start to Nations League Group A4 as Jorge Jesus’s squad showed little signs of missing Cristiano Ronaldo with a 4-2 victory over Denmark in Copenhagen.
The 41-year-old Al-Nassr forward and five-time Ballon d’Or winner left the camp ahead of the match amid reports of a falling out with Jesus, his former club boss, having been left on the bench throughout a victory in Norway.
Continue reading...Protests halted events in Dublin twice before the Republic of Ireland were forced to settle for a 2-2 draw after Austria came back in the second half of their Nations League encounter at the Aviva Stadium.
Despite a significant security presence, the contest was twice interrupted in the opening 45 minutes, first due to what campaign group Stop the Game later referred to in a statement as a “limited tennis ball protest”, when – around the 20th minute – tennis balls wrapped in stickers featuring the Palestinian flag and the text “#StopTheGame” were launched on the pitch.
Continue reading...Spurs star says he will ‘never’ promote betting
Wembanyama says endorsements must reflect his values
James, Durant and Antetokounmpo have gambling ties
Victor Wembanyama has ruled out ever endorsing a sports betting company, saying he was saddened to see fellow NBA players lend their names to gambling platforms.
The San Antonio Spurs star was unequivocal when asked after Thursday’s training camp workout if he would consider partnering with a sportsbook.
Continue reading...Planned rule change forms part of Burnham’s bid to crack down on the ‘little charges that add up’
Airlines will be blocked from charging parents extra to sit with their children on planes, according to government plans.
The new rule would require airlines to seat passengers aged under 14 next to their parents or an accompanying adult free of charge. Passengers will also no longer need to pay to tweak the name on their flight booking if they need to correct a mistake.
Continue reading...Shoppers and vendors in Aspen surprised by unusual customer as it stretched to sample stall offerings
Farmers’ market shoppers might not usually pay much attention to the local resident devouring fresh bread and pastries at one of the stalls with extra gusto – but some certainly did last weekend when they realized it was a hungry bear.
Onlookers on Saturday reached for their phones to take photos and videos of the bear in downtown Aspen, Colorado, after it wandered through the stalls and got up on to its hind legs to dig into the baked goods.
Continue reading...Manchester City played out a high-quality draw with Real Madrid in the Women’s Champions League after an unprecedented week of off-field tension at the English club.
The result – which was a fair reflection of an even but entertaining game – left both sides with two points from their opening two fixtures, but City will know their league phase opponents should theoretically become less challenging from hereon, after their opening draw at Bayern Munich.
Continue reading...
iain.davidson100 has added a photo to the pool:


iain.davidson100 has added a photo to the pool:


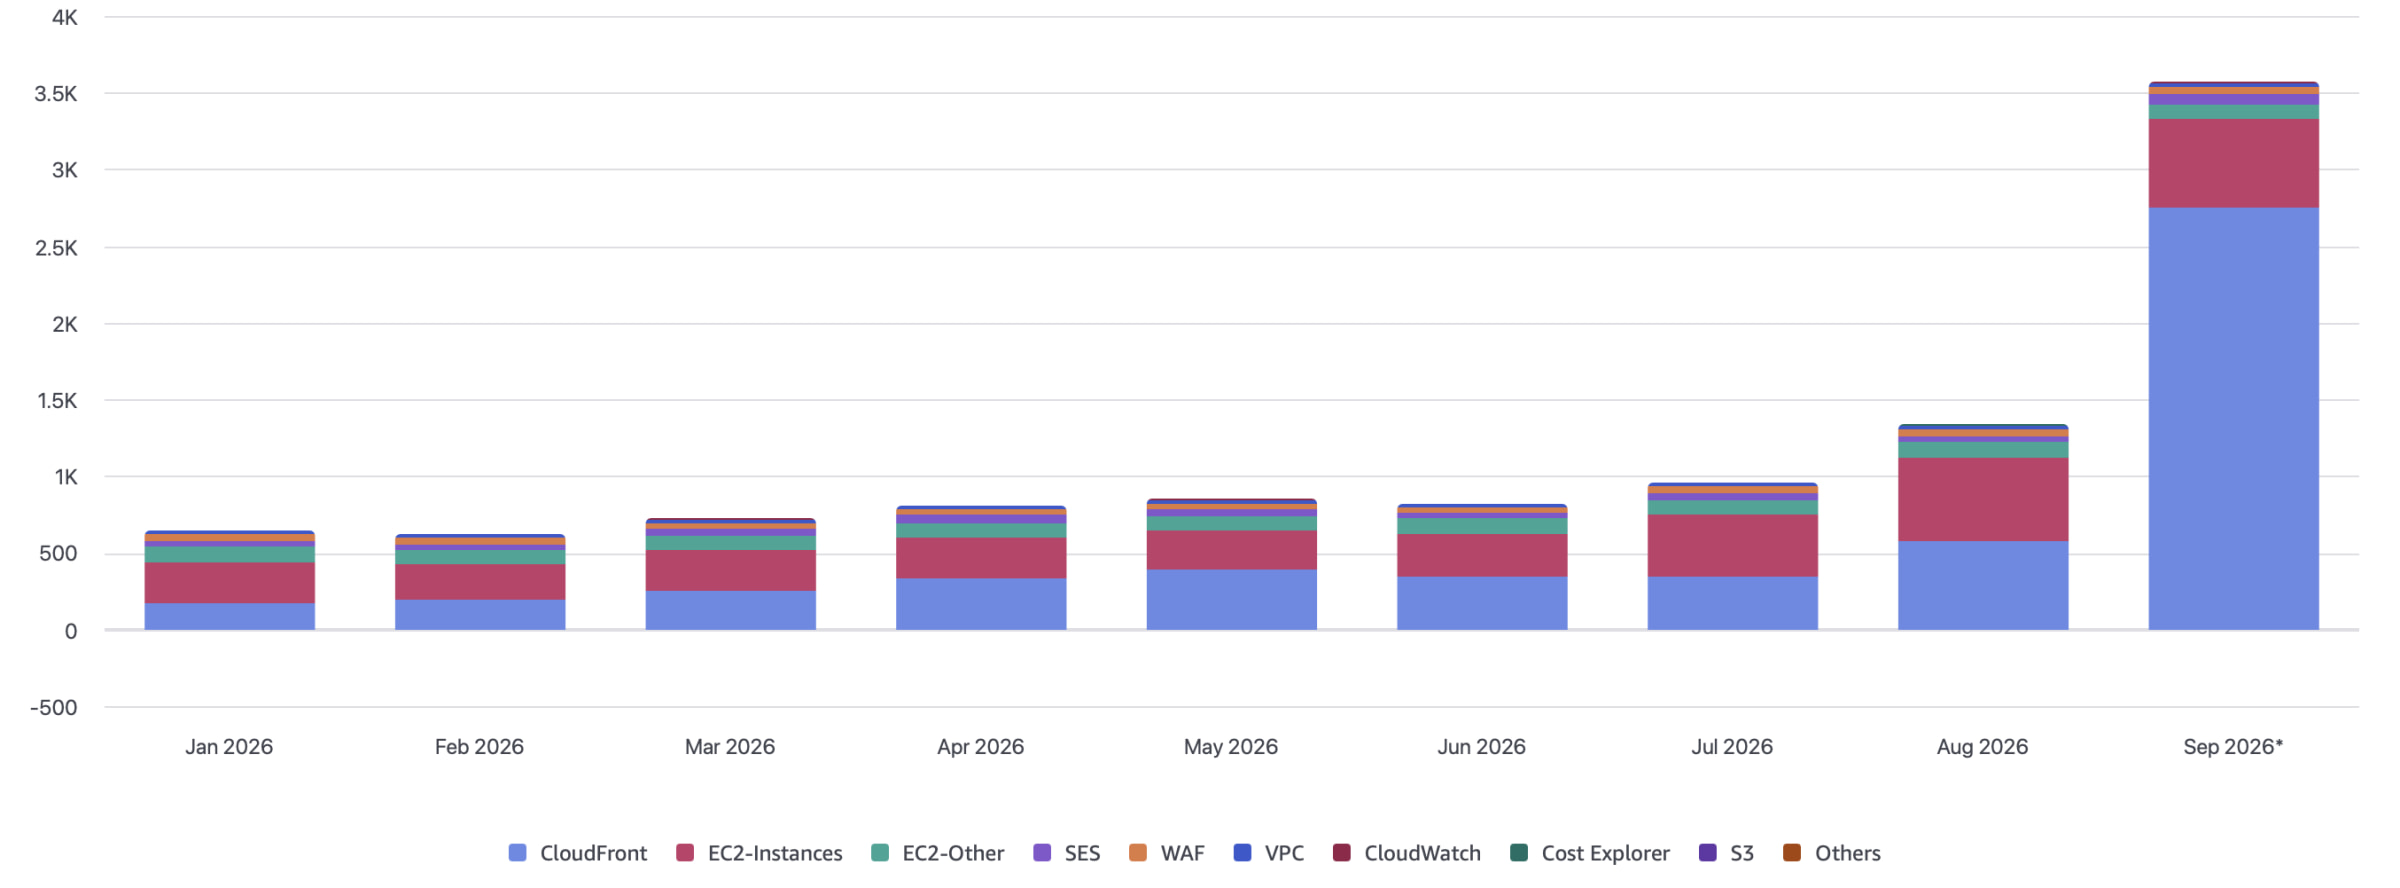
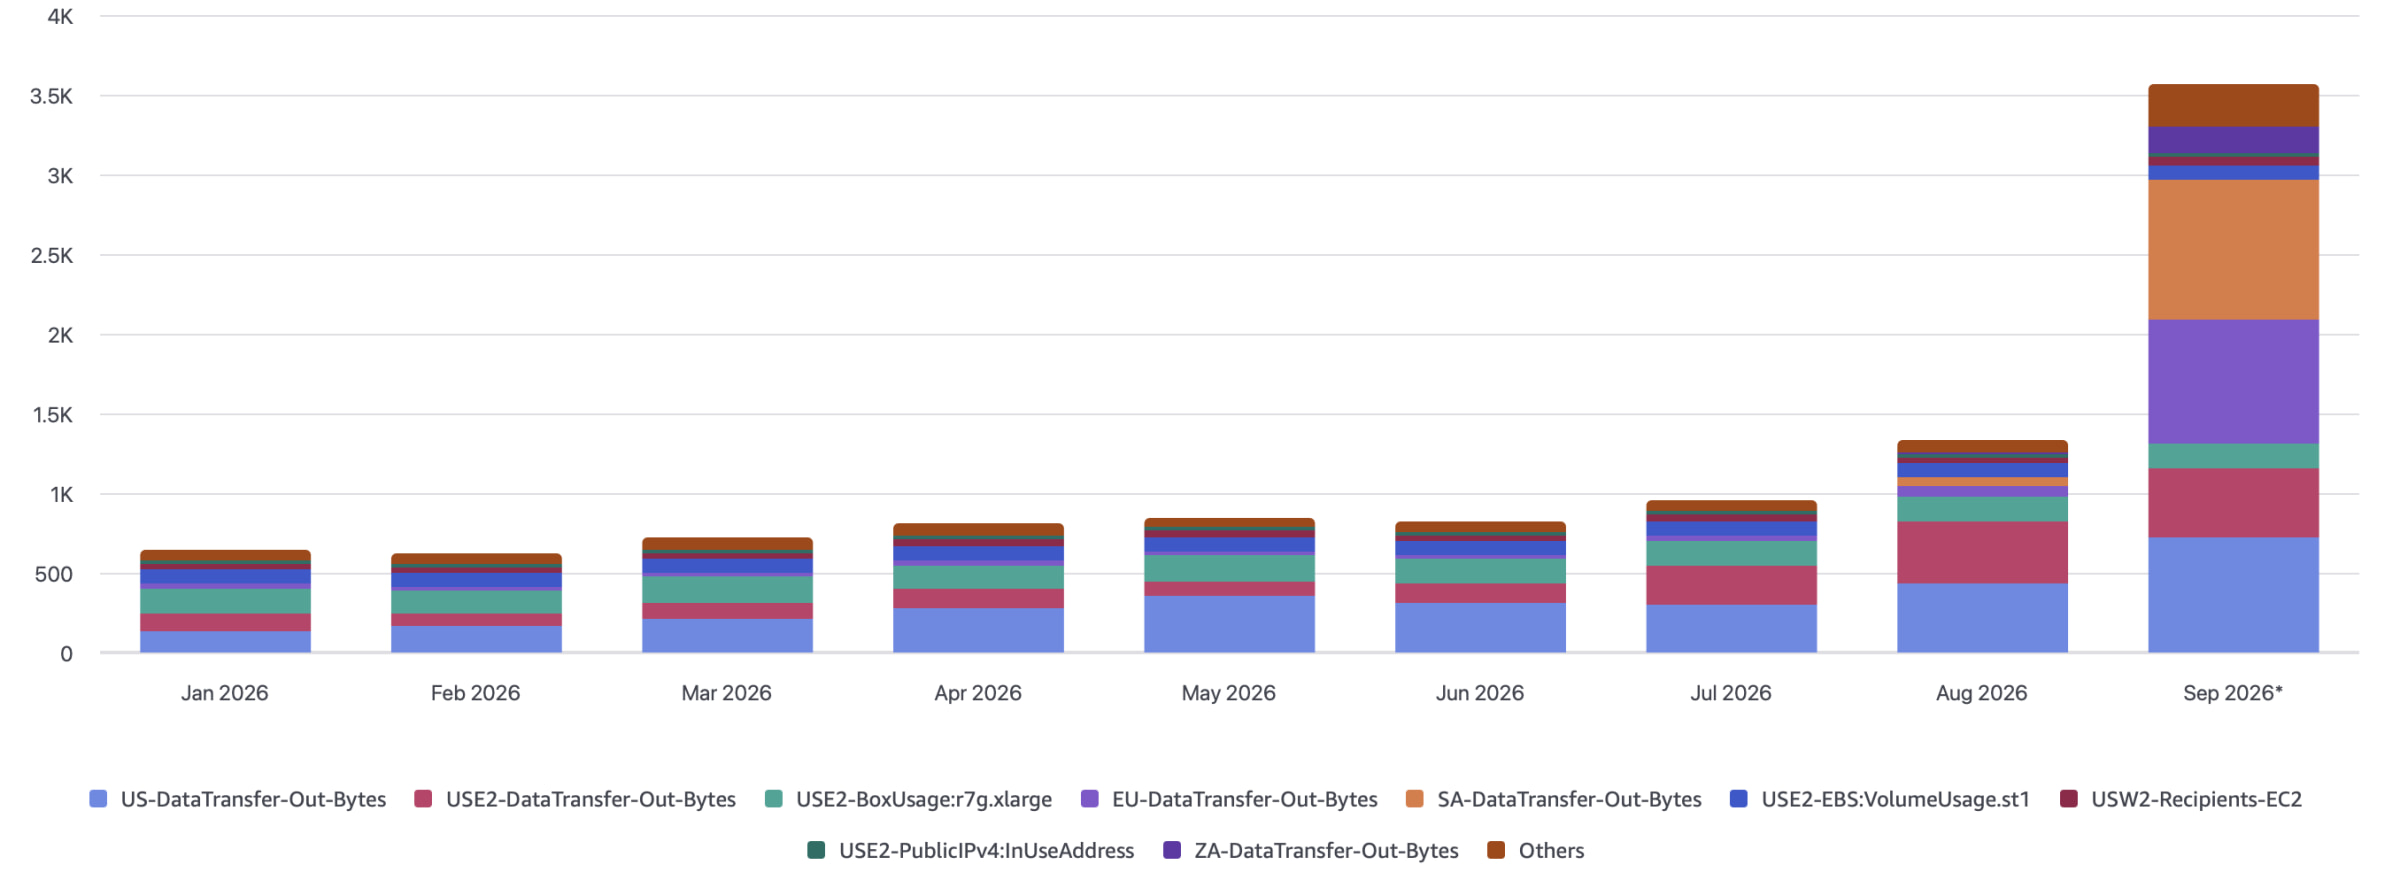
Let me just take a nice long sip of this beverage and then open up my web-hosting bill for last month...
An anonymous reader quotes a report from 404 Media: A company that makes phone hacking devices claims to have developed a solution that freezes iPhones in a state that lets cops more easily access sensitive data inside them, according to a video obtained by 404 Media. [...] The new technology to get around inactivity reboot was developed by Magnet Forensics, the company behind GrayKey, a popular tool sold to law enforcement agencies that allows them to unlock and access data stored in iPhones and Android smartphones. Magnet has developed a new device called GrayKey Preserve and a feature for its regular GrayKey devices called Evidence Preservation Mode, according to the video.
"This is an absolute game changer for iOS forensics and a function that I wish we had years ago," a Magnet employee says in the leaked video, specifically mentioning that the solution is targeted at the iPhone's inactivity reboot feature and the data it makes unavailable. GrayKey Preserve and Evidence Preservation Mode are also designed to combat another iPhone feature that automatically deletes certain data -- such as cached locations, and recently deleted photos and iMessages -- after a certain number of days. "We're gonna be able to preserve that data for an infinite amount of time."
[...] 404 Media shared a transcript of the video with Jiska Classen, a researcher at the Hasso Plattner Institute who studies iPhone security. While Classen said that it's impossible to know for sure how Magnet's new feature works based on the video, she posited some theories and agreed that it is "quite a game changer" or "at least puts things back to where they were before inactivity reboot." She thinks Magnet has found a way to manipulate the iPhone's clock, effectively "slowing down time" or even "stopping the clock from ticking, even after a reboot." Most likely, according to her, the GrayKey may disable the iPhone tasks that set data to expire. The "inactivity reboot" feature mentioned above was added to iOS in November 2024 and automatically restarts iPhones that have not been unlocked for 72 hours, making them harder for police to access using forensic tools.


"This is an absolute game changer for iOS forensics and a function that I wish we had years ago," a Magnet employee says in the leaked video, specifically mentioning that the solution is targeted at the iPhone's inactivity reboot feature and the data it makes unavailable. GrayKey Preserve and Evidence Preservation Mode are also designed to combat another iPhone feature that automatically deletes certain data -- such as cached locations, and recently deleted photos and iMessages -- after a certain number of days. "We're gonna be able to preserve that data for an infinite amount of time."
[...] 404 Media shared a transcript of the video with Jiska Classen, a researcher at the Hasso Plattner Institute who studies iPhone security. While Classen said that it's impossible to know for sure how Magnet's new feature works based on the video, she posited some theories and agreed that it is "quite a game changer" or "at least puts things back to where they were before inactivity reboot." She thinks Magnet has found a way to manipulate the iPhone's clock, effectively "slowing down time" or even "stopping the clock from ticking, even after a reboot." Most likely, according to her, the GrayKey may disable the iPhone tasks that set data to expire. The "inactivity reboot" feature mentioned above was added to iOS in November 2024 and automatically restarts iPhones that have not been unlocked for 72 hours, making them harder for police to access using forensic tools.
Read more of this story at Slashdot.
AI agents hacked the hackers - the Dutch Institute for Vulnerability Disclosure (DIVD) - via two zero-day bugs in its Zammad support platform, abusing the flaws to hijack sessions, run code remotely as the local zammad user, and escalate privileges to root. The chained exploits took just seconds to move from session hijacking to root access, and on Thursday, the nonprofit bug hunting organization said the miscreants stole data belonging to its volunteer security researchers, including DIVD email addresses and potentially other contact details. “We’re still investigating exactly which data of which volunteers is affected,” DIVD said in its incident report. “For DIVD volunteers (and others) this means a higher risk of social engineering, because this makes it easier for someone to pose as a DIVD’er.” A subsequent LinkedIn post advised anyone receiving an email or contact request from someone at DIVD “that feels slightly off” to verify that it’s legit by emailing communications@divd.nl. DIVD is also a CVE Numbering Authority (CNA), and it assigned CVE IDs to the now-public security holes in Zammad, an open-source helpdesk and customer support ticketing system. They are CVE-2026-102489 and CVE-2026-102490, and both bugs received CVSS 4.0 scores of 9.4, when assessed in the chained attack scenario. CVE-2026-102489 enables unauthenticated attackers to achieve remote code execution and leak user sessions, while CVE-2026-102490 allows a local user to elevate their privileges to root. Zammad versions 6.3.0 to 6.5.4 are vulnerable to CVE-2026-102489, and it also exists in versions 7.0.0 through 7.1.3 - but it’s not exploitable “due to environment conditions,” according to DIVD’s advisory. All Zammad versions are vulnerable to CVE-2026-102490. DIVD advises “all users of Zammad to upgrade to version 7 of Zammad or to take it offline.” What happened According to the nonprofit’s timeline, the attack happened on September 21, when "malicious actors” broke into its IT system via the two zero-days in its ticketing support software. The bug hunters discovered the attackers the following day, blocked access to all of its data center systems, and formed an incident response team with Merlon Security. On September 24, DIVD reported the Zammad vulnerability to the vendor, notified the Dutch Data Protection Authority and the National Cyber Security Centre about the incident, and discussed its options with police. It also posted its first disclosure on LinkedIn. “It took us (almost) seven years but we can now say that we're the hackers that got hacked,” the post said, adding that DIVD remained committed to handling the incident in “the way we think it should be handled. That is open, transparent and honest, even if it sucks.” 'Modus operandi' indicates agentic AI DIVD also noted that its team had never seen an attack like this before. “This is an attack we have not seen before,” according to the post. “Not because it’s our first, but because the modus operandi indicates that this is an agentic AI powered attack.” The attack was "loud and very very messy," DIVD said. "We could see the agent working automated, because after every action it decided the next step itself, at the speed of light and sloppy logic or pattern." Subsequent posts with screenshots of logs found during the investigation reveal embedded notes found in the attack script - another indication that this was an agentic operation or at least AI-enabled. “What human attacker leaves notes to themself in their scripts, explaining why what they're doing is okay and really not phishing? The AI just got a task and keeps justifying its own actions in the code as comments, a human wouldn’t care less," the post said. "Who has time for that anyway?” If only all orgs responded to hacks like this While the investigation remains ongoing, security researchers applauded DIVD for its transparency in disclosing and responding to the hack. “Kudos to DIVD for their level of honesty and transparency working through their active incident and investigation,” VulnCheck security researcher Patrick Garrity posted on LinkedIn. “It would be nice if all organizations were this transparent about their security incidents!” In a subsequent interview with The Register, Garrity said he applauded DIVD’s “brutal honesty” about the breach. “They're eating their own dog food, which is great, and getting information out quickly to other organizations that potentially use this product so they can take action before they get hit.”®

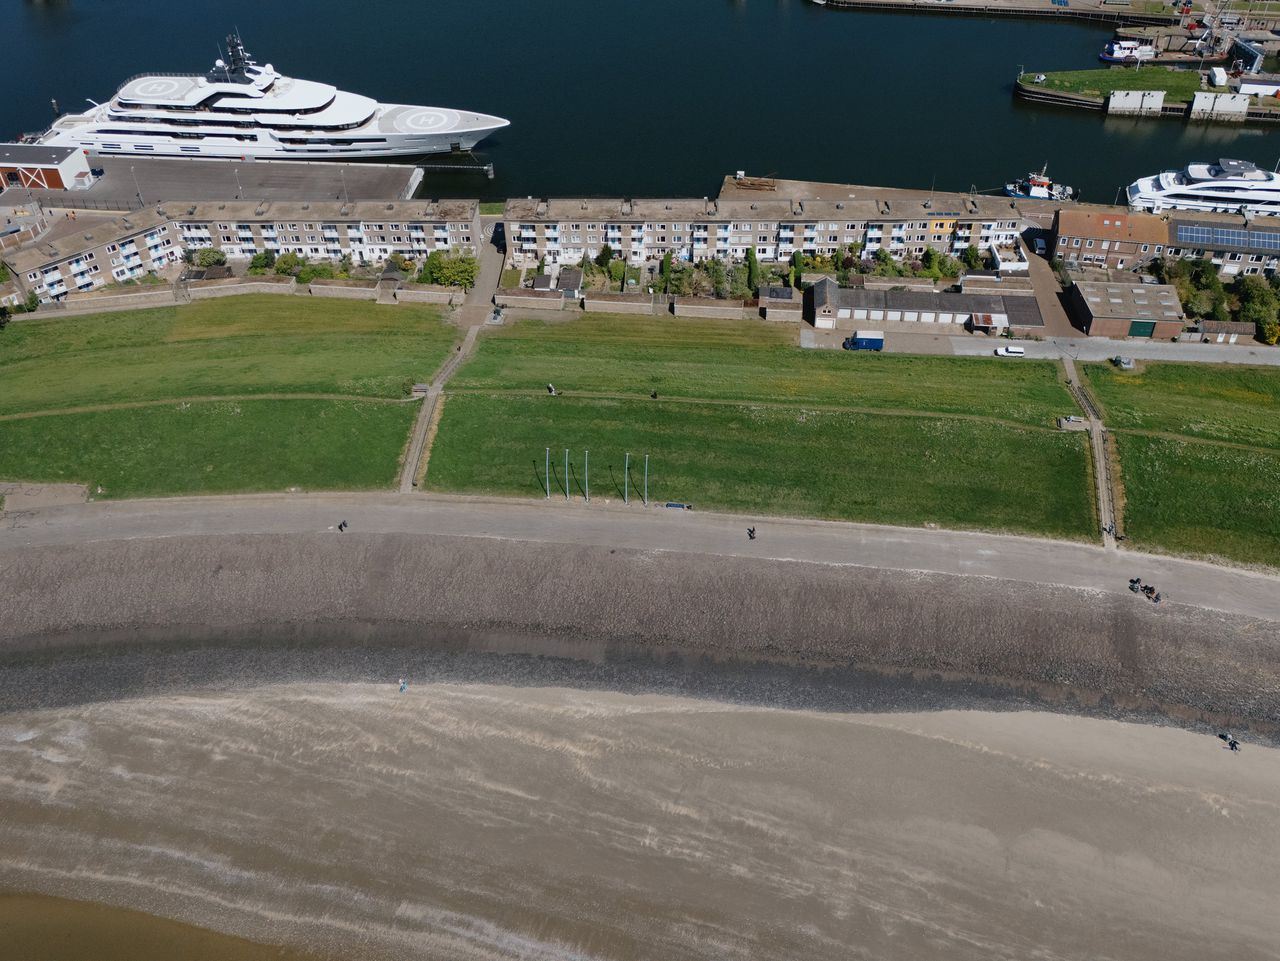
Bewoners van het unieke wijkje ’t Eiland in Vlissingen moeten na sloop kunnen terugkeren in nieuwe sociale huurwoningen, vinden lokale politici. Maar een garantie krijgen ze niet. „Gemeentes kunnen woningcorporaties niet dwingen.”
VENLO (ANP) - De oorzaak van de brand begin augustus in het Limburgse natuurgebied Boschhuizerbergen blijft onduidelijk. Dat is de conclusie in een rapport van de brandweer Limburg-Noord en het Landelijk team Natuurbrandonderzoek dat donderdag werd gepresenteerd.
De brandweer zegt wel met zekerheid te kunnen stellen dat de brand niet is veroorzaakt door werkzaamheden, onontplofte oorlogsresten of achtergelaten afval, is te lezen in het rapport. Ook vonkvorming van het spoor, dat dwars door het natuurgebied loopt, wordt als oorzaak uitgesloten. En het schrikdraad, waarmee delen van het gebied voor wild zijn afgezet, bevond zich ook niet in de buurt van de plek waar de brand begon.
Bij de brand in het natuurgebied bij Venray ging ongeveer 100 hectare natuur verloren, waaronder bijna 4000 aaneengesloten struiken met jeneverbessen. Volgens de brandweer is de brand vermoedelijk midden in het bos ontstaan en kon het vuur zich snel verspreiden door een combinatie van onder meer droogte en de grote hoeveelheid brandbaar materiaal.
The best multi day hikes in the world. “As an avid hiker, who spends most of her time hiking, I have done more than 100 multi day hikes all over the world. This list includes 25 of my favorite ones.”