kottke.org

Jason Kottke's weblog, home of fine hypertext products

Lots and Lots and Lots of Control Panels

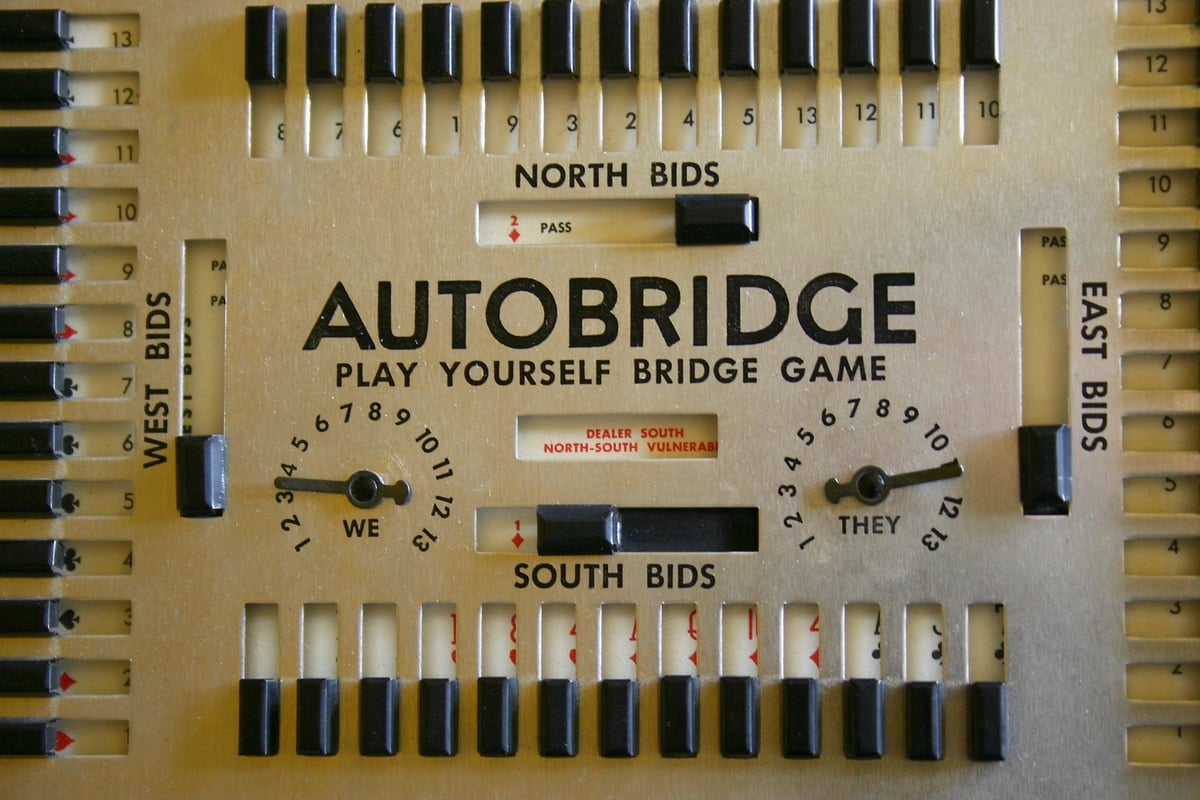
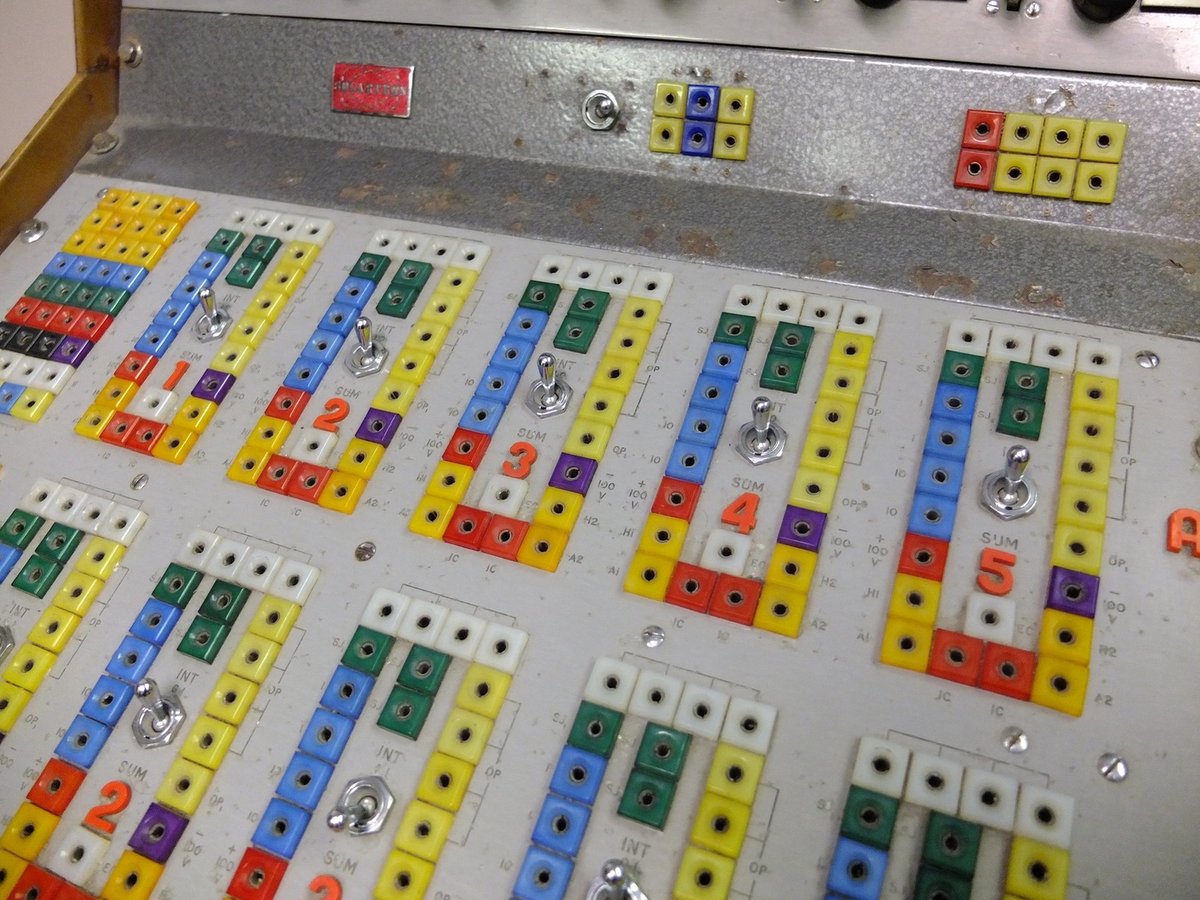
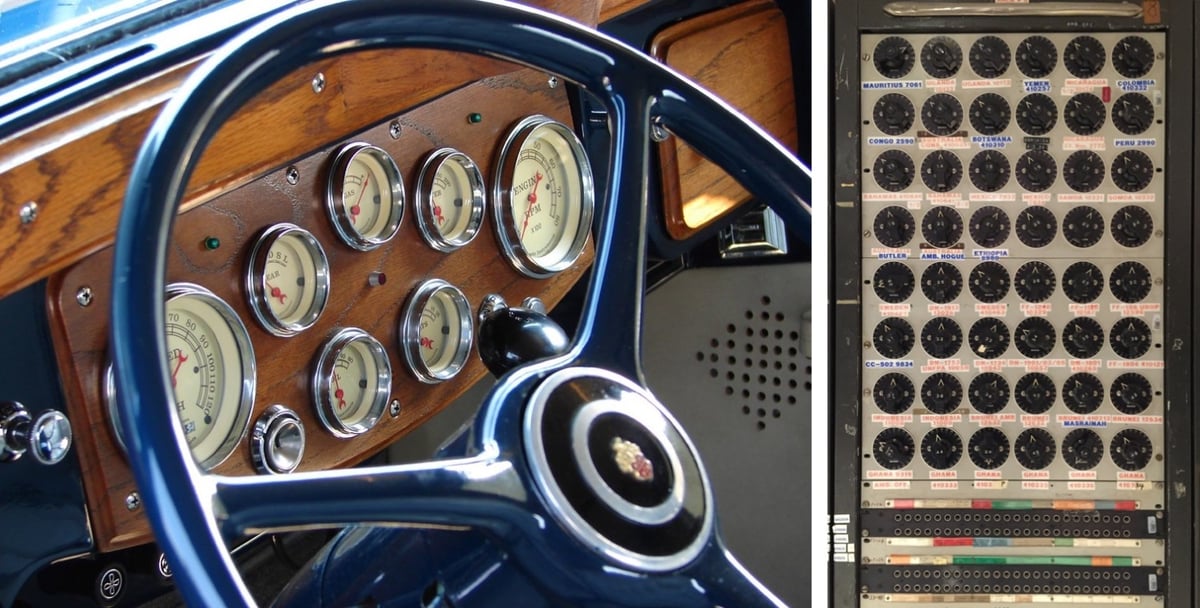
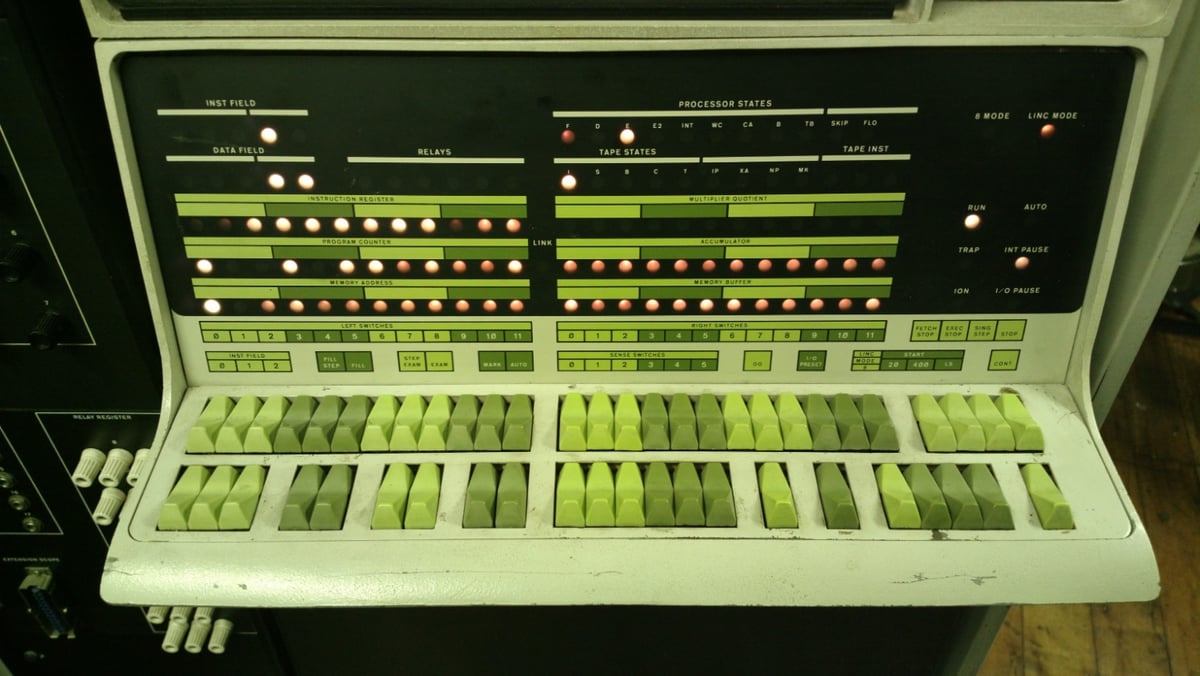
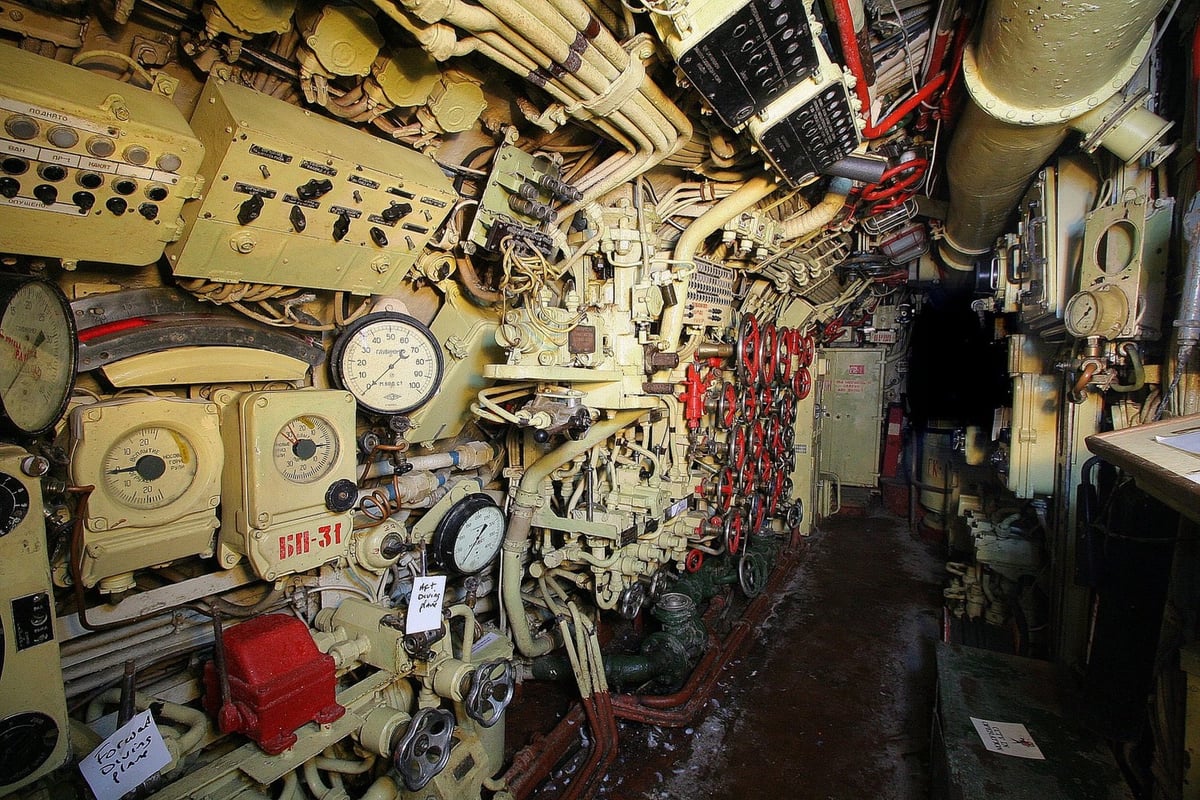
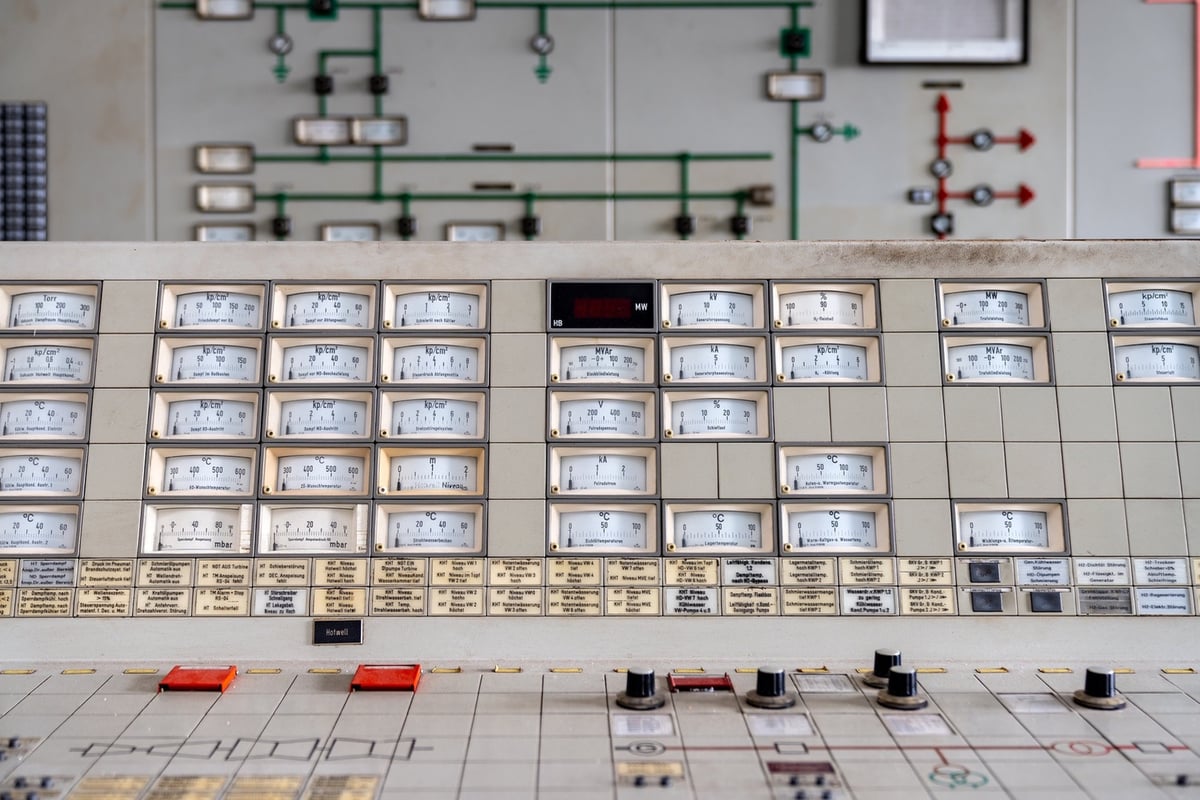
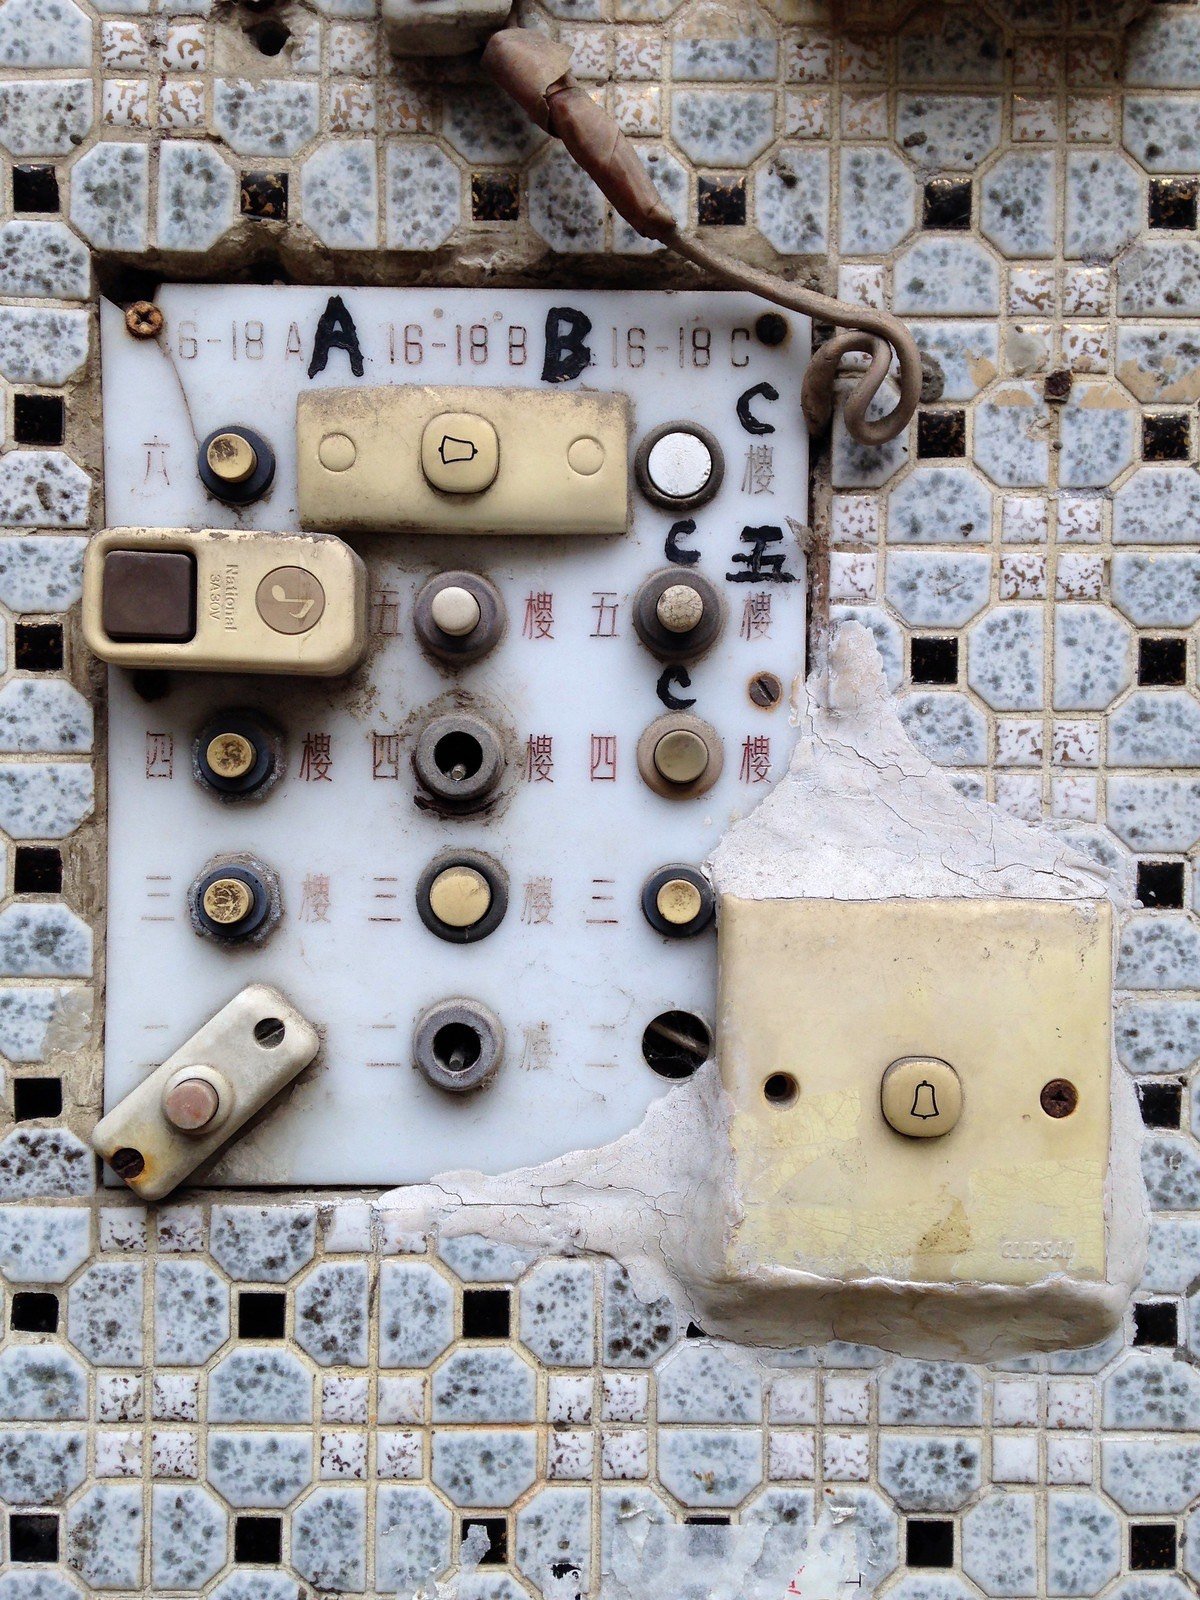
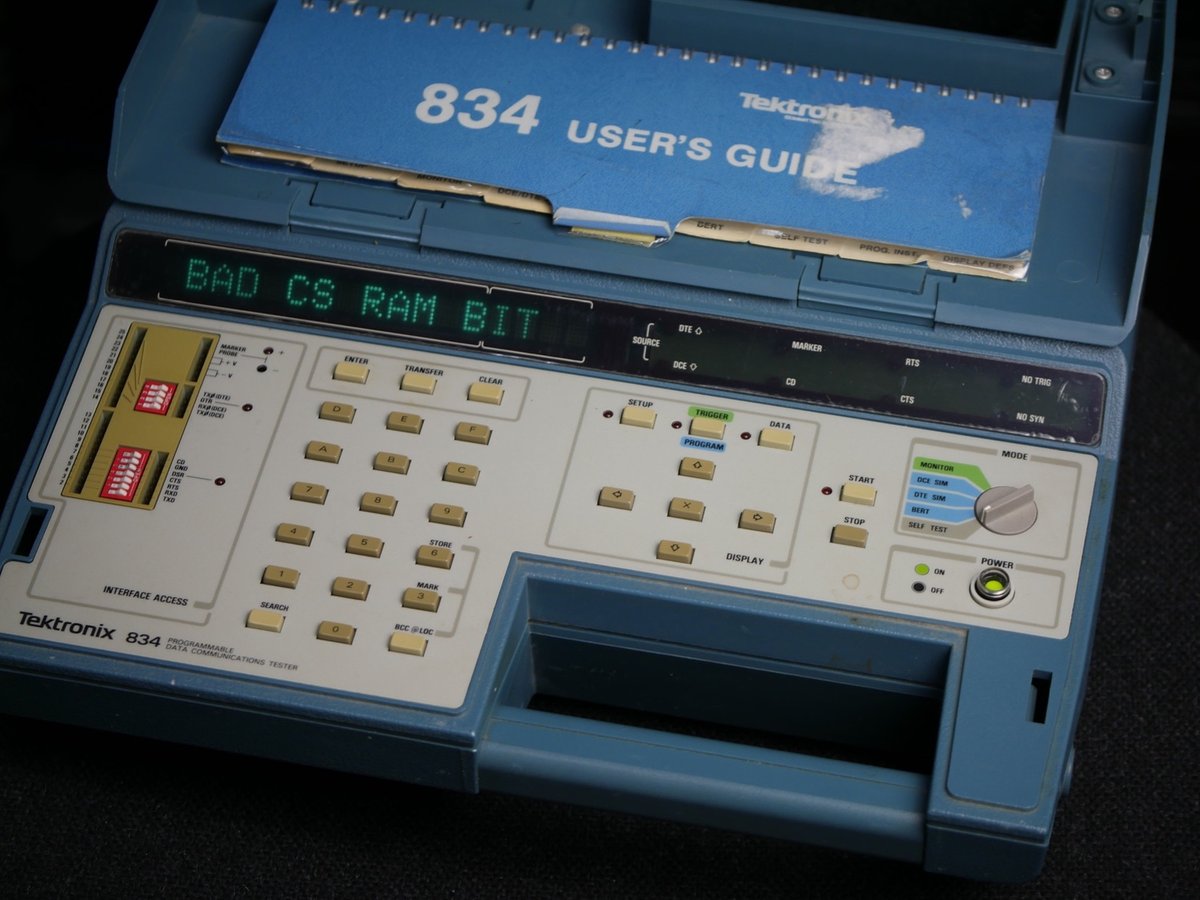
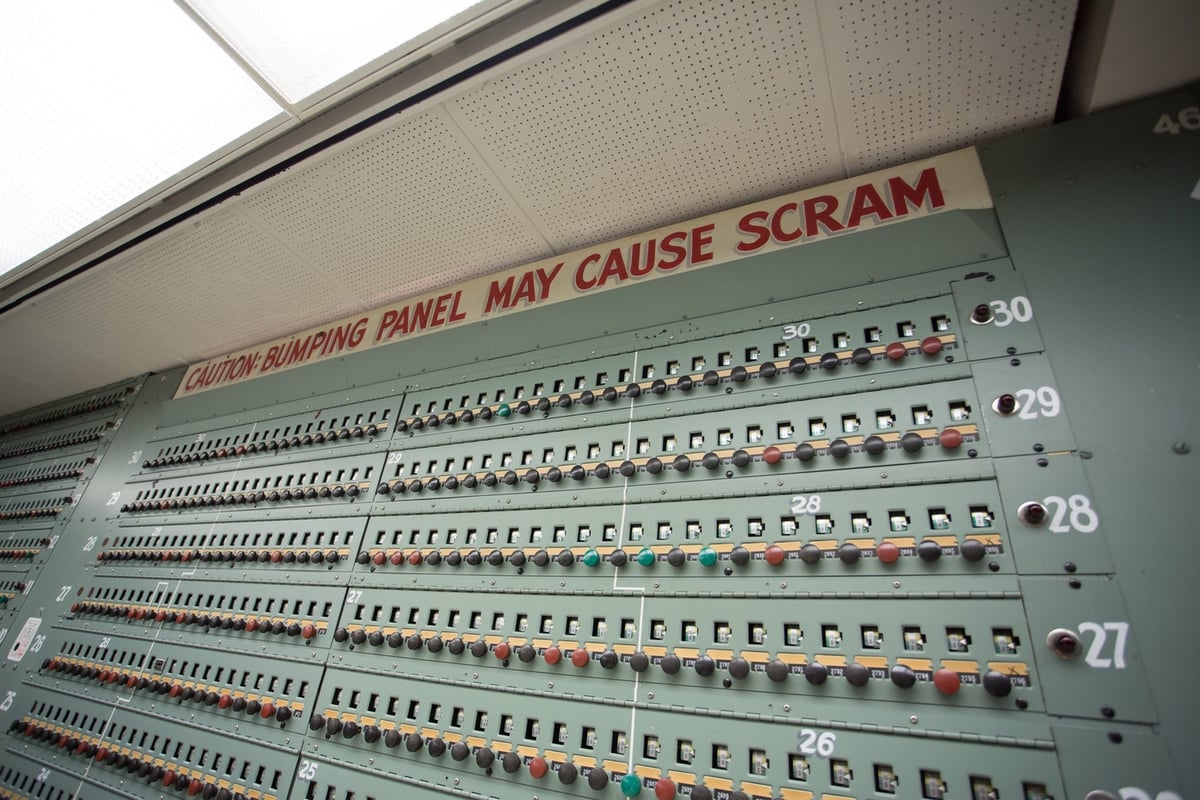
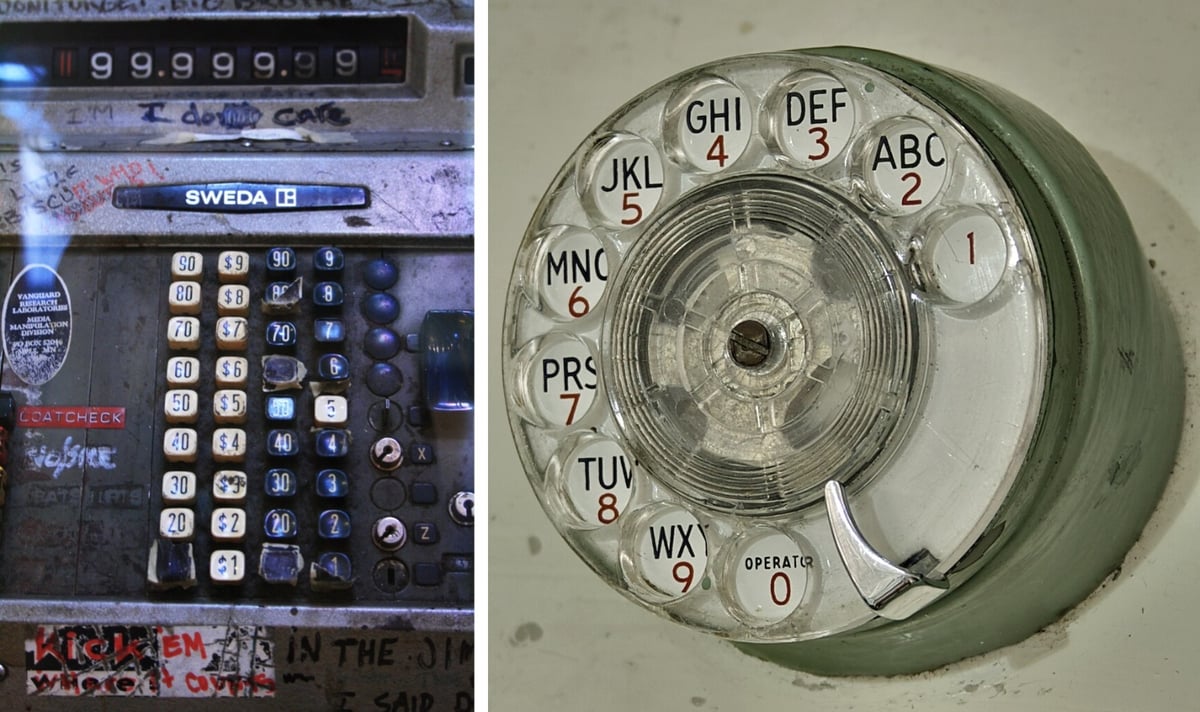
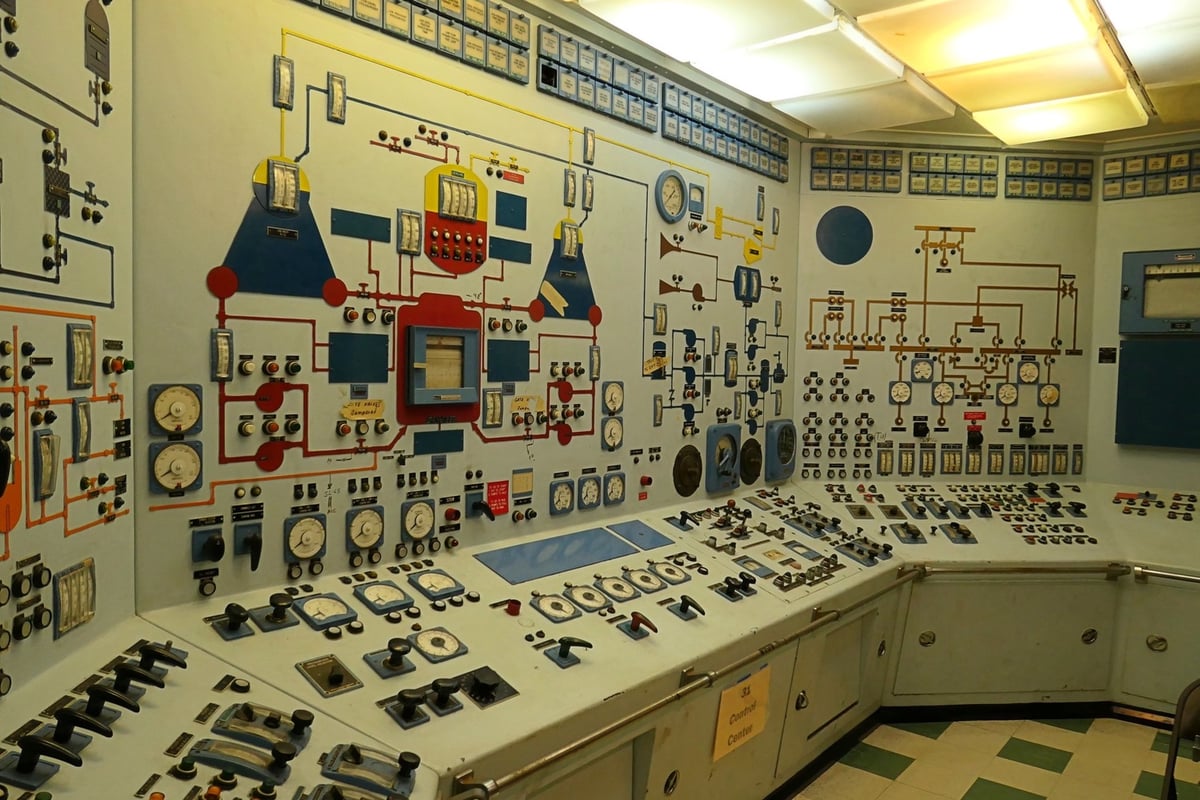
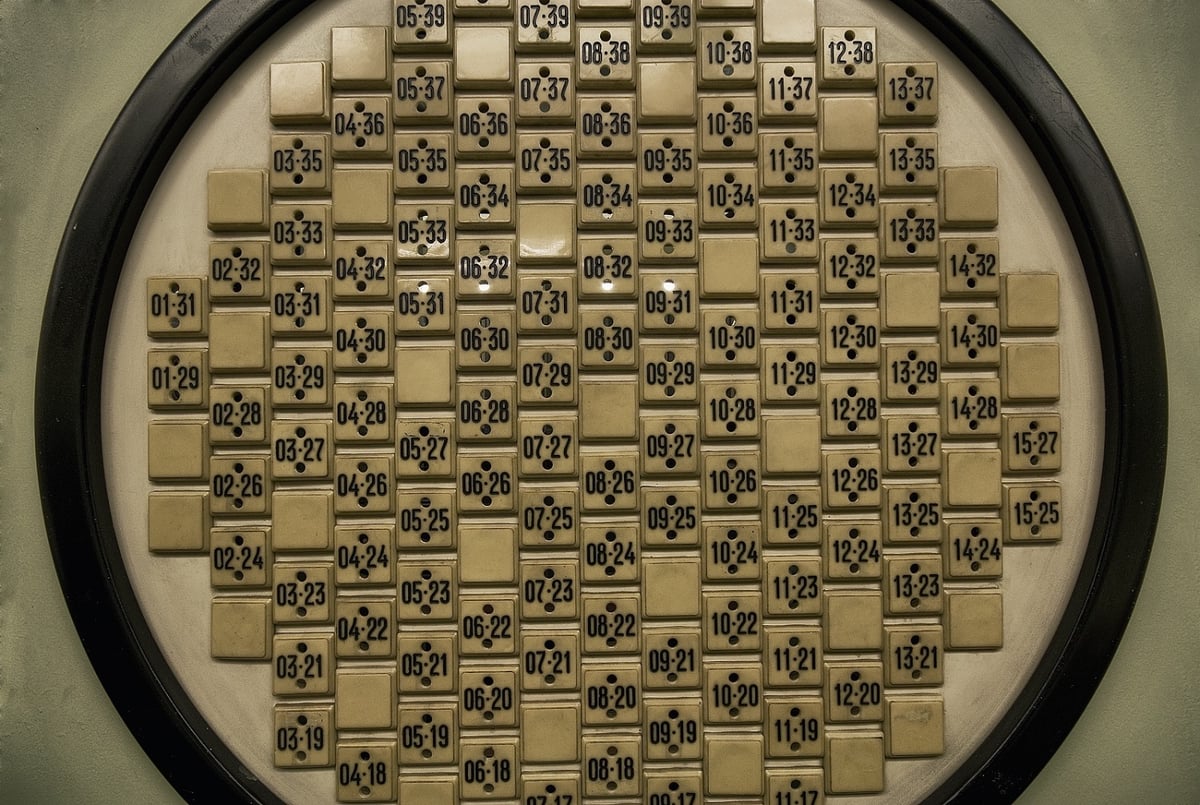
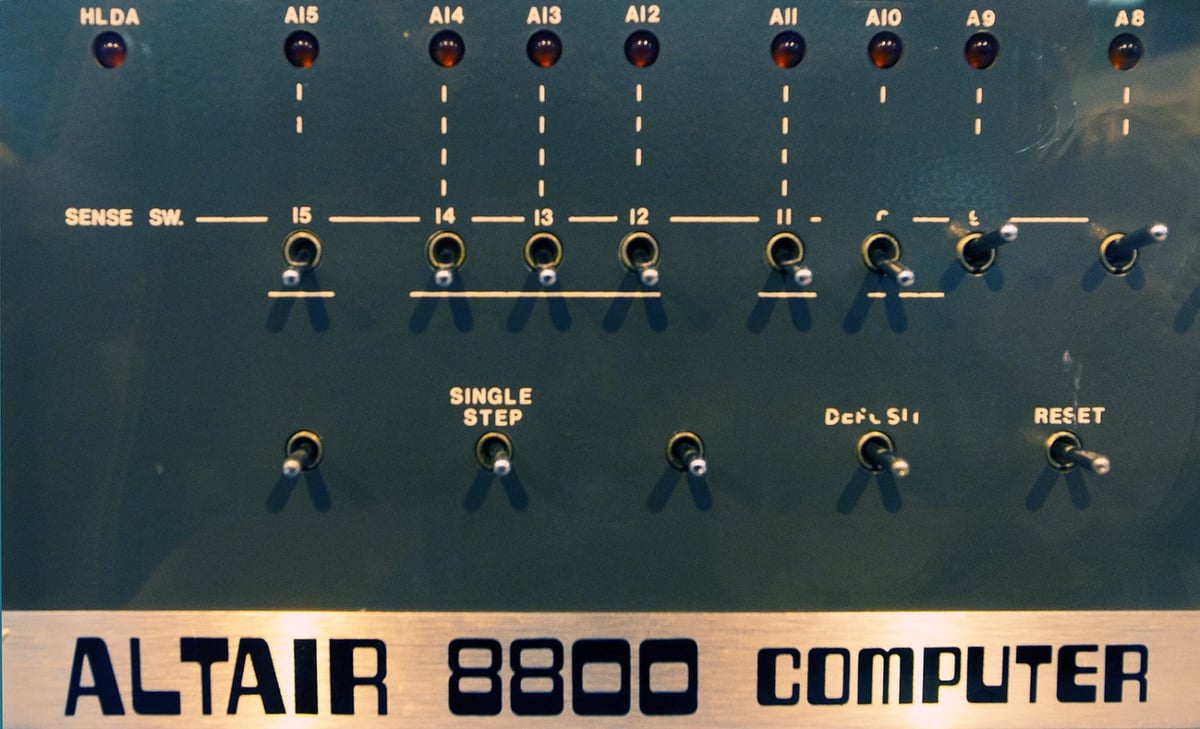
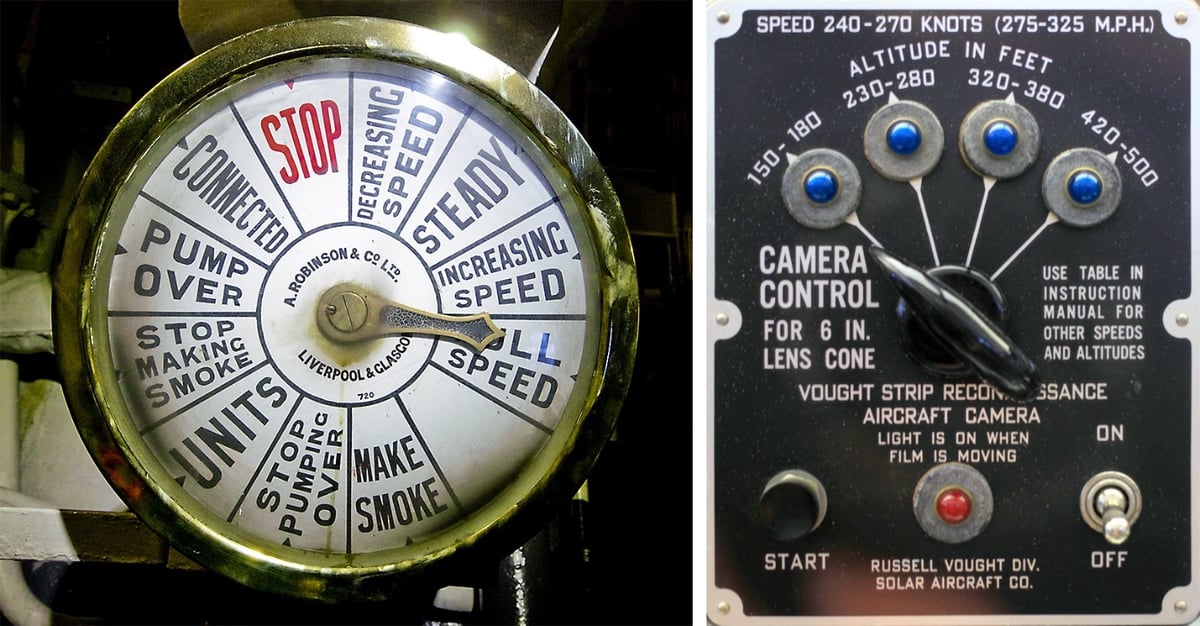
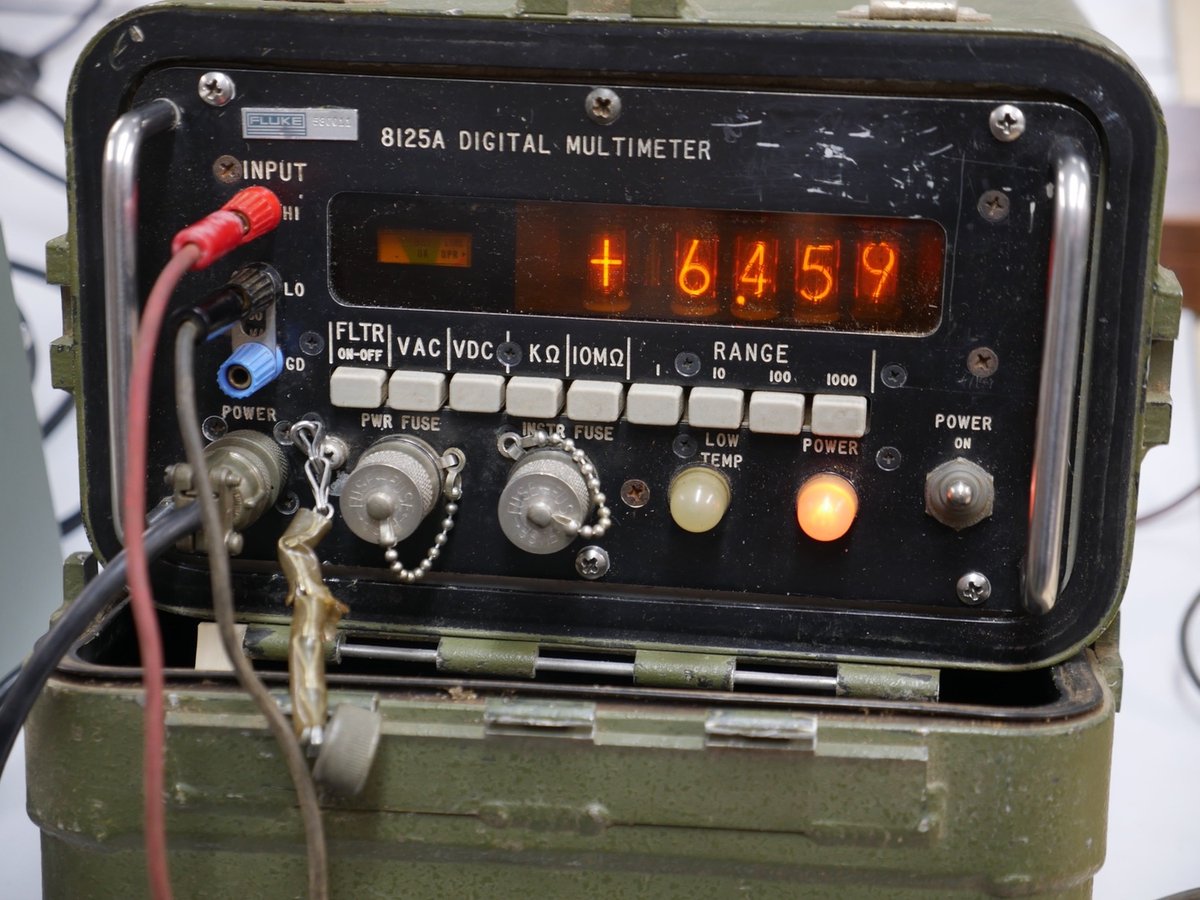
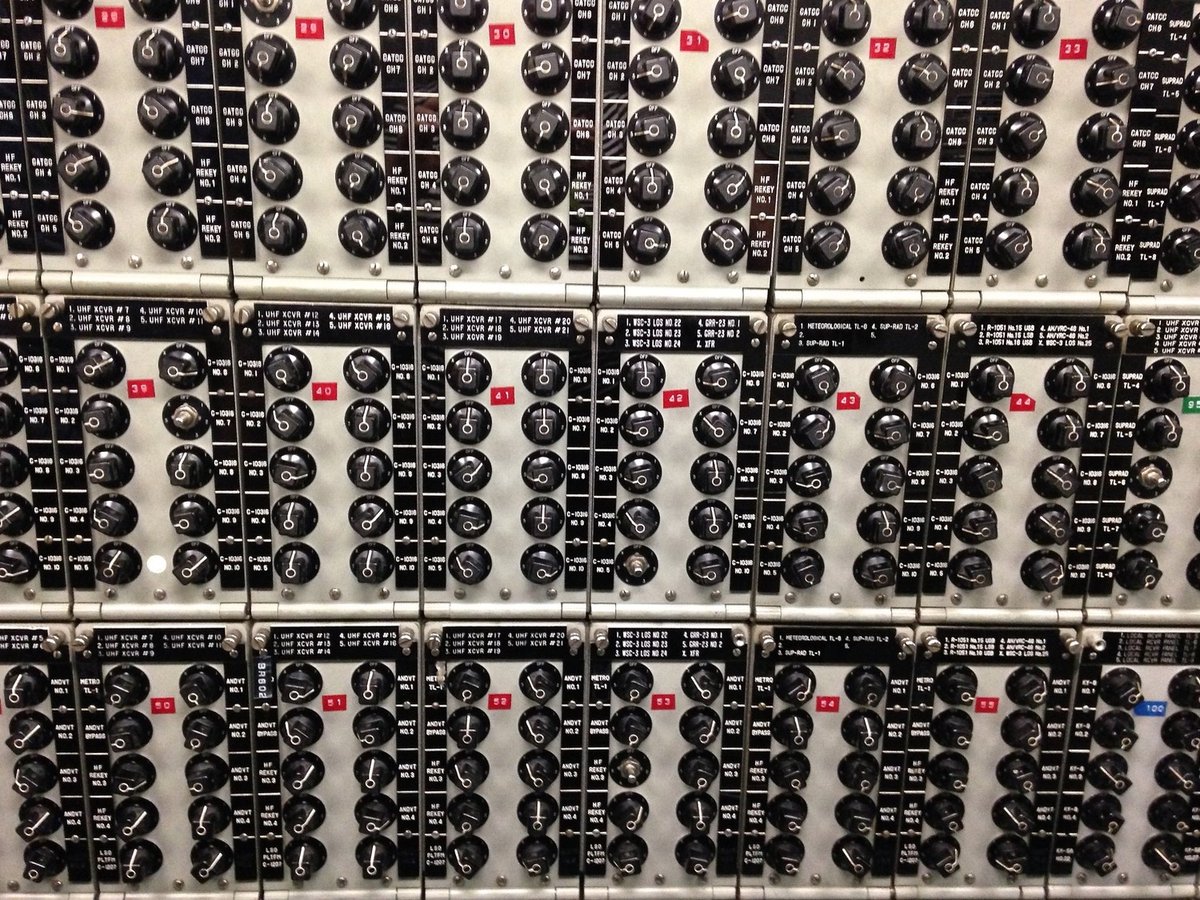
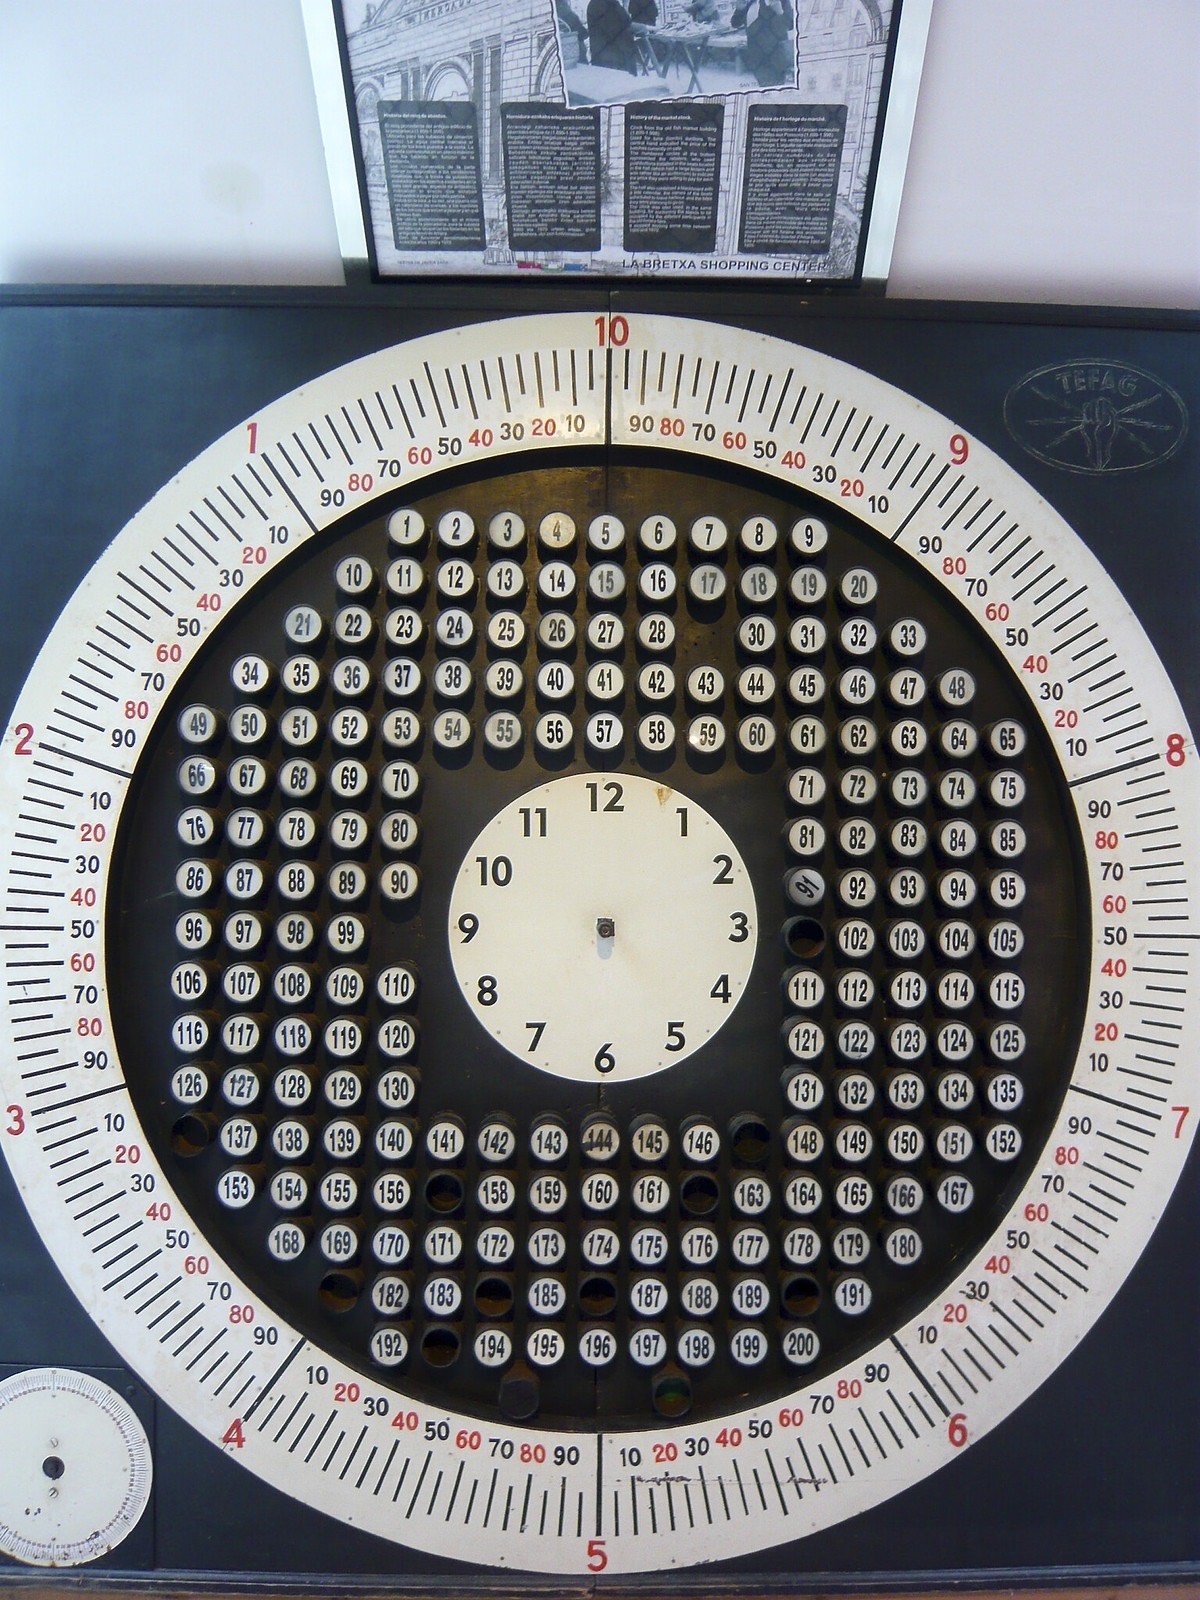
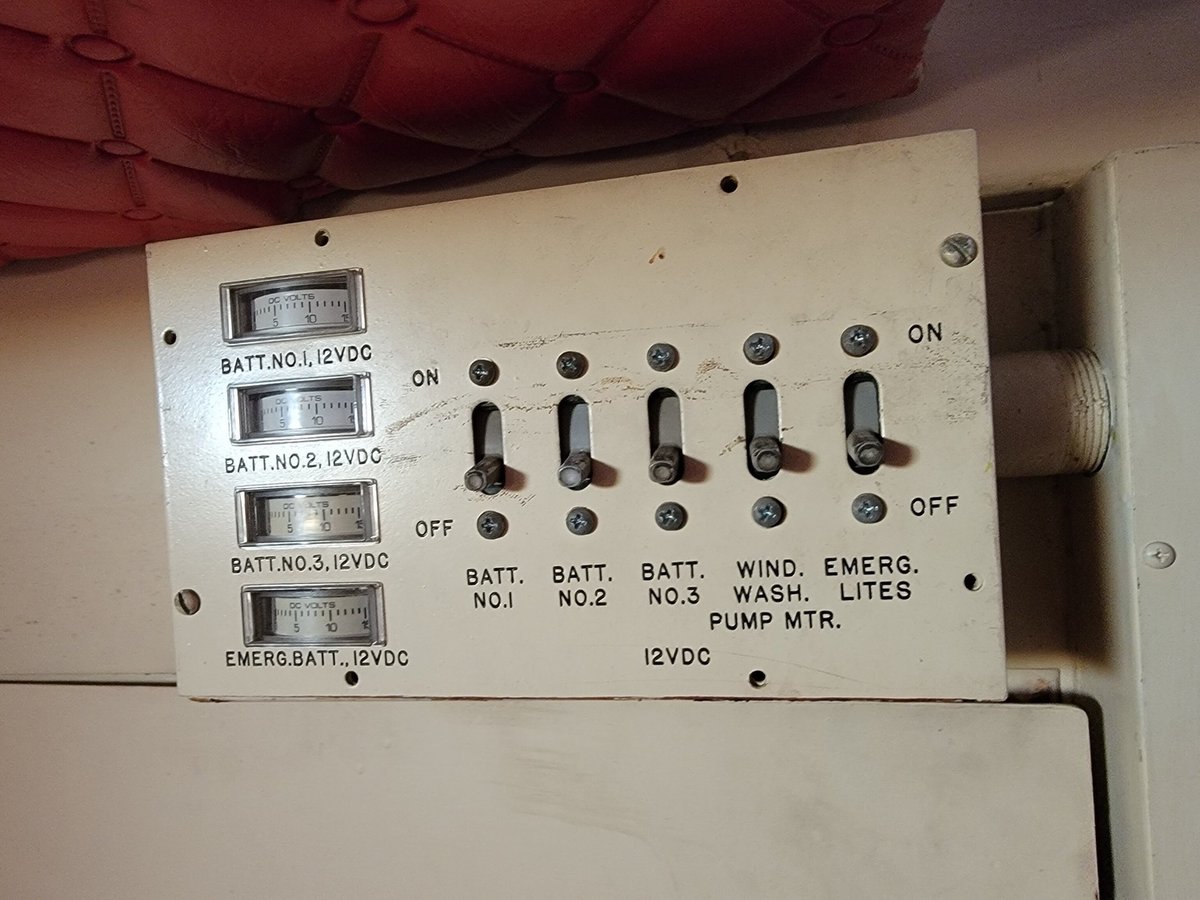
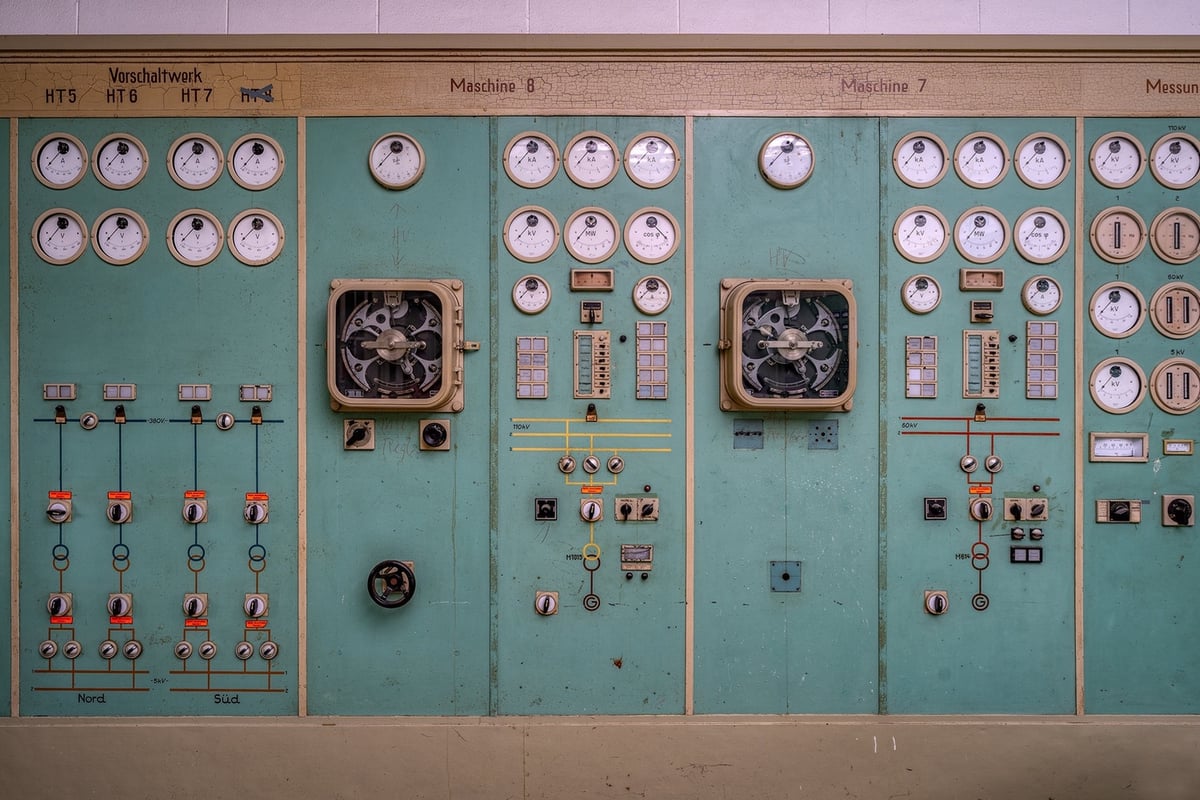
To go along with my recent post about control rooms, here’s the Control Panels group on Flickr, containing almost 3000 photos of control interfaces for all kinds of things.

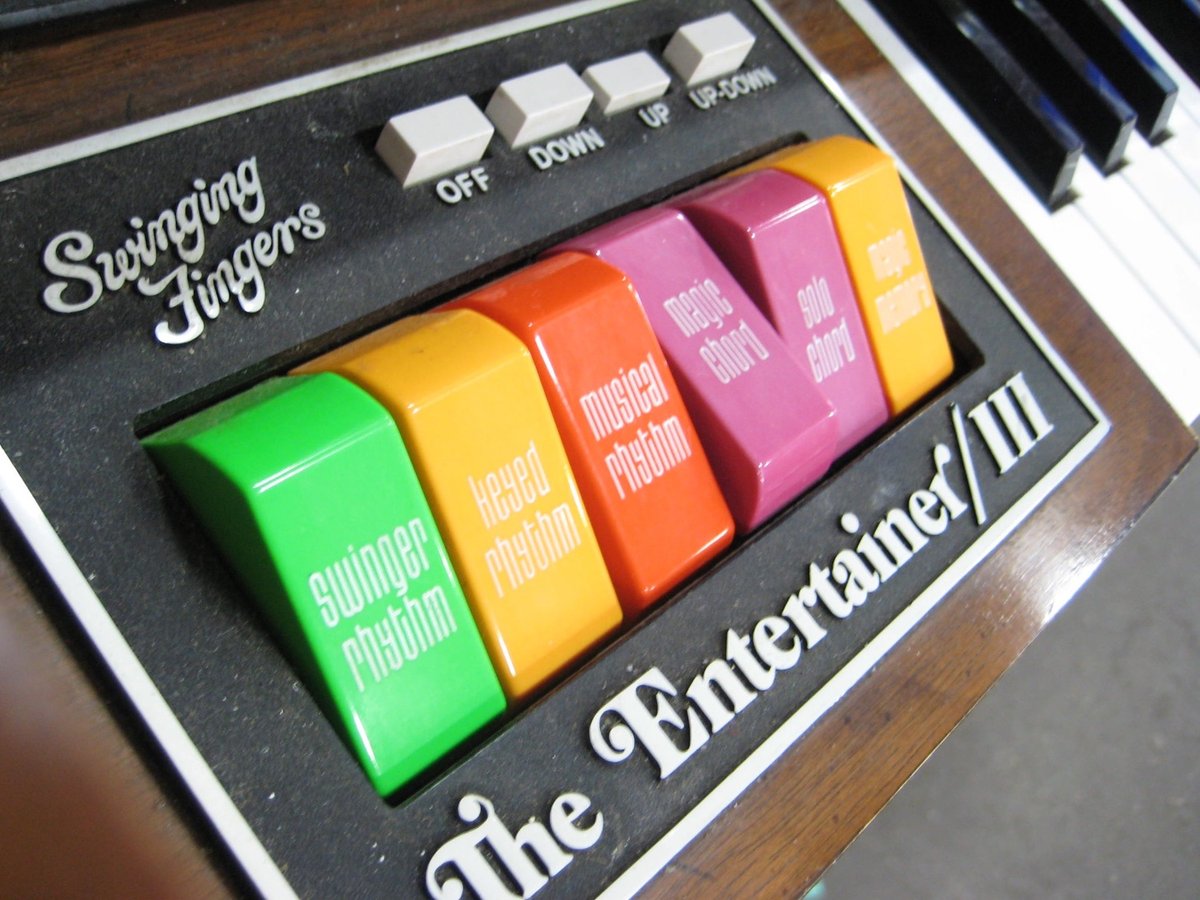
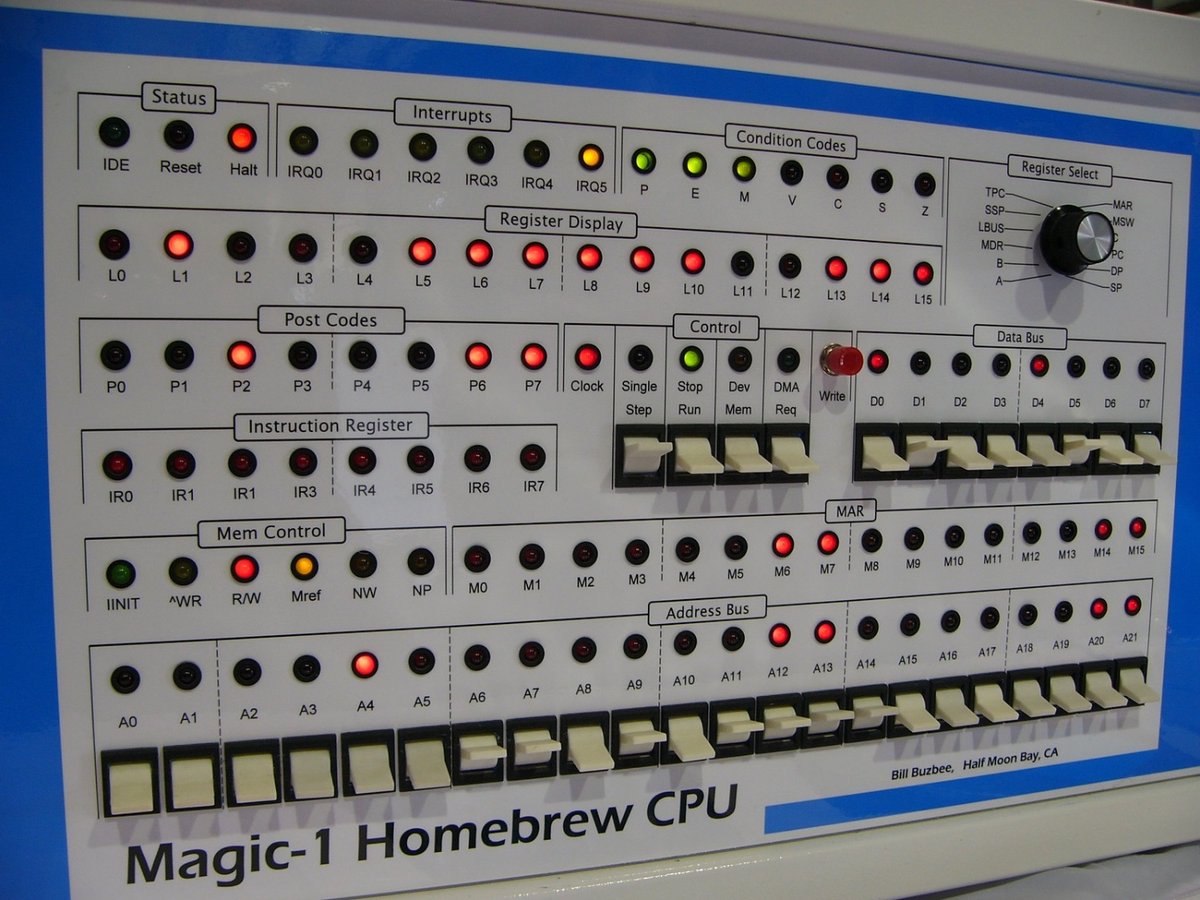
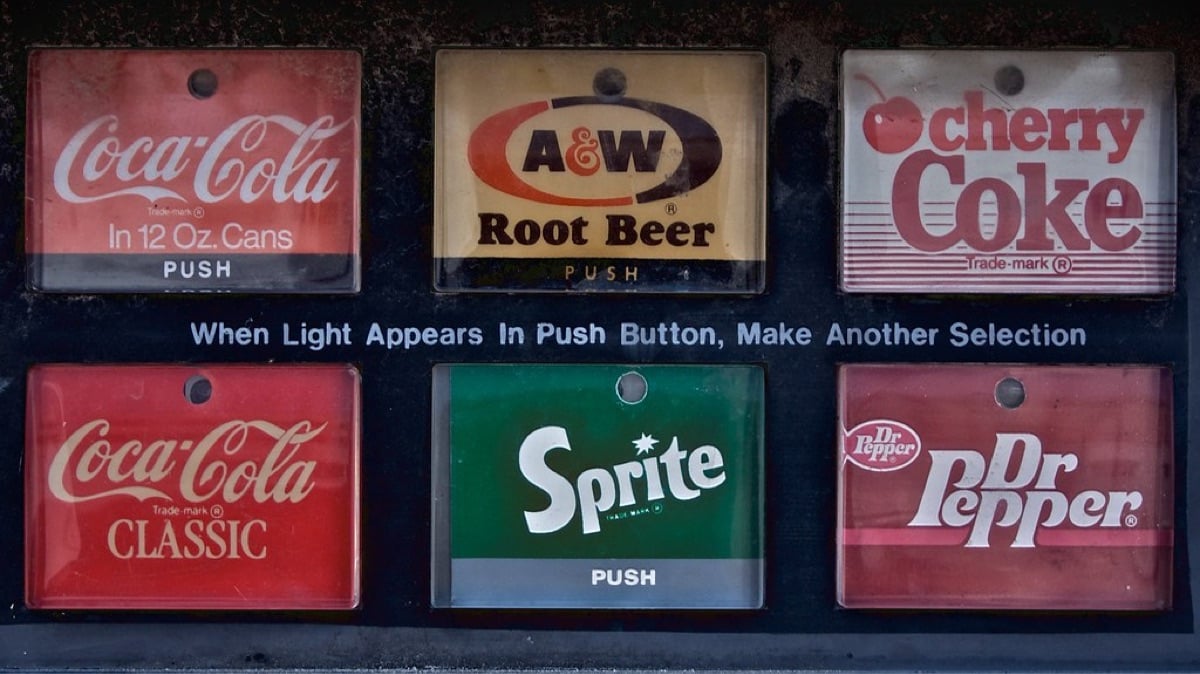
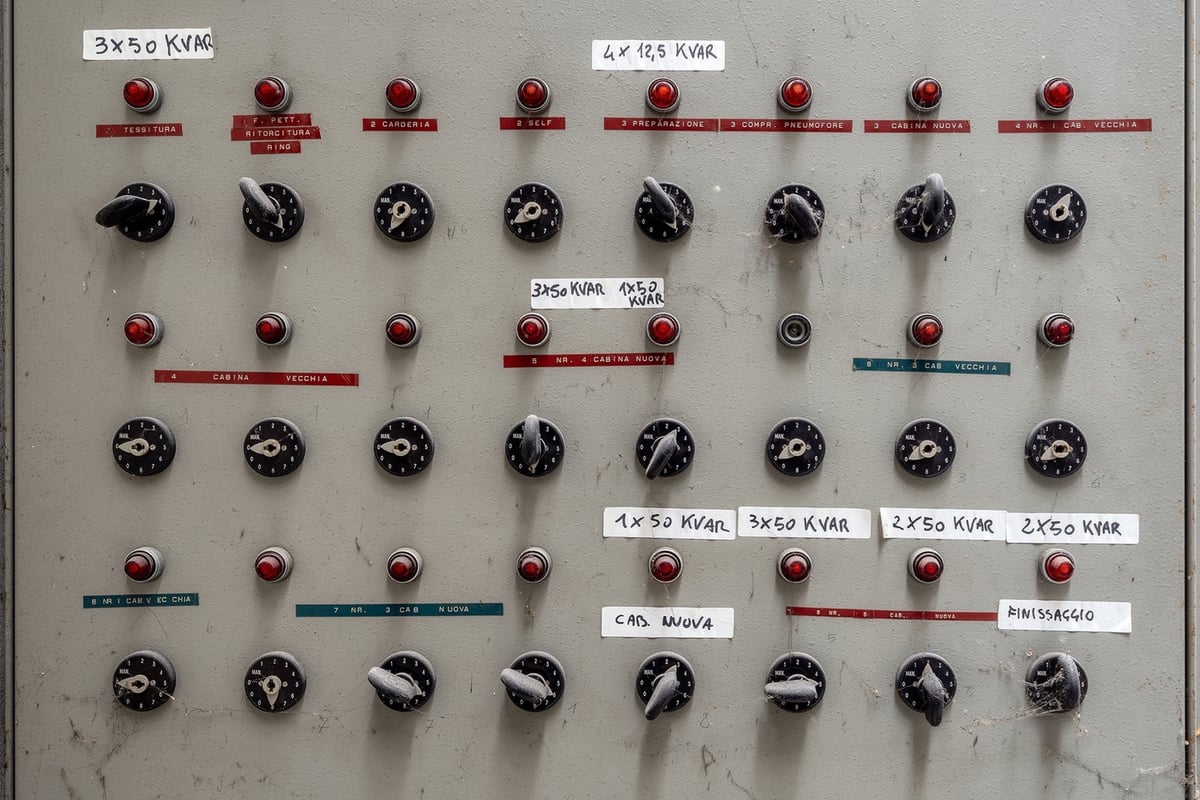
You’ll see some of the same photos as in the Control Rooms group, but when you get past the first couple of pages, there’s more variety: fiddly knobs, entire walls of nearly identical switches, dials, inscrutable gauges, soda machine interfaces, bump it and you might die buttons, computers with switches, Swinging Fingers (!!), and many more…

How much Gorton did you spot?

Tags: design · photography

Wel.nl

Minder lezen, Meer weten.

Inlichtingendiensten voorzien fors meer Chinese cyberaanvallen

DEN HAAG (ANP) - De komende jaren zullen er flink meer Chinese cyberaanvallen plaatsvinden, verwachten de Militaire Inlichtingen- en Veiligheidsdienst (MIVD) en de Algemene Inlichtingen- en Veiligheidsdienst (AIVD). Om organisaties daarvoor te behoeden kwamen de diensten woensdag met een cyberadvies.

Volgens de MIVD en AIVD richten Chinese hackers zich vaker op zogenoemde edge devices, apparaten die tussen een bedrijfsnetwerk en het internet zitten. De hackers weten volgens de diensten veel over dergelijke apparatuur, en over de zwakke plekken waarmee ze een netwerk binnen kunnen dringen. De MIVD waarschuwde al eerder voor een toename in Chinese cyberaanvallen.

De diensten adviseren onder meer om ervoor te zorgen dat de informatiebeveiliging van een netwerk gelaagd is opgebouwd, om een indringer te vertragen.


Israëliër veroordeeld voor stelen apparatuur na aanval 7 oktober

TEL AVIV (ANP) - Een Israëlische rechtbank heeft een man veroordeeld tot zeven jaar cel voor de diefstal van geluidsapparatuur na de aanval door Hamas op het muziekfestival Nova, drie jaar geleden. Dat schrijft de nieuwssite Times of Israel. Enkele dagen na de aanslag, waarbij honderden doden vielen, kwam hij apparatuur halen die was achtergebleven. Deze had een waarde van ongeveer een half miljoen dollar (447.000 euro).

De man deed tijdens twee bezoeken samen met een handlanger alsof hij een medewerker was van de eigenaar van de apparatuur. Die was tijdens de aanval op 7 oktober om het leven gekomen. Hij bezocht ook de familie van de overleden man.

Naast de gevangenisstraf heeft hij een voorwaardelijke straf van twaalf maanden opgelegd gekregen en moet hij een boete en schadevergoedingen betalen. De handlanger moet ruim drie jaar de cel in. Een derde medeplichtige is veroordeeld en krijgt op een later moment zijn straf te horen.


Zes aanhoudingen om diefstal uit Zuid-Frans Renoir Museum

NICE (ANP) - De Franse politie heeft in verscheidene delen van het land zes arrestaties verricht in verband met de diefstal van vier werken van de beroemde schilder Pierre-Auguste Renoir. Die werden een maand geleden gestolen uit het Renoir Museum in Cagnes-sur-Mer, vlak bij Nice.

De nieuwszender BFMTV berichtte dat de politie zeker twee van de zes verdachten beschouwt als degenen die de schilderijen hebben ontvreemd uit het museum. Twee van de vier werken van Renoir werden snel teruggevonden, maar de andere niet. De zes zijn aangehouden in de departementen Alpes-Maritimes, Hérault en Jura.

De impressionist Renoir (1841-1919) woonde aan het eind van zijn leven in Cagnes-sur-Mer. Daar is het museum gesticht in zijn voormalige huis. In Frankrijk zijn musea vaker doelwit van rovers, zoals afgelopen jaar het Louvre in Parijs en meer recent musea in Straatsburg en Châtillon-sur-Seine.


Baanwielrenners nog niet onder de indruk van olympische piste LA

APELDOORN (ANP) - De Nederlandse baanwielrenners zijn nog niet onder de indruk van de olympische piste van de Spelen van Los Angeles in 2028. "Afgelopen zomer zijn we een week naar LA geweest om de baan te verkennen, maar die voelt heel klein en compact. Het is niks vergeleken hier met Omnisport", zei vijfvoudig olympisch kampioen Harrie Lavreysen tijdens een persmoment langs de wielerbaan in Apeldoorn.

Wel wordt de Carson Velodrome de komende twee jaar nog verbouwd en moet er meer ruimte voor publiek komen. "Maar voor nu heerst er helemaal geen olympisch gevoel; ik kan me moeilijk voorstellen dat daar de Spelen zijn", aldus Lavreysen.

Wat betreft de sfeer in het stadion heeft bondscoach Hugo Haak ook nog vertrouwen. "Met de aankleding die ze daar hebben, zullen ze uiteindelijk wel een olympische sfeer kunnen creëren. Maar het gebouw blijft hetzelfde, dus het zal denk ik nooit de allure hebben van een stadion zoals we die kennen uit Tokio of Parijs."


Minister: Oekraïense asielaanvragen niet met prioriteit behandeld

DEN HAAG (ANP) - Asielminister Bart van den Brink weet nog niet wanneer de asielaanvragen van meer dan 140.000 Oekraïners behandeld worden. Het Europese Hof van Justitie oordeelde op 1 oktober dat die aanvragen gewoon behandeld moeten worden, maar de CDA-minister schrijft in een brief aan de Tweede Kamer dat andere aanvragen voorrang krijgen.

Nederland had de asielaanvragen van Oekraïners die de oorlog zijn ontvlucht na de Russische invasie uitgesteld zolang zij tijdelijk in Nederland mogen verblijven. Het hof oordeelde dus dat de aanvragen alsnog behandeld moeten worden.

De Immigratie- en Naturalisatiedienst (IND) heeft al een flinke achterstand bij het verwerken van asielaanvragen. Volgens de Algemene Rekenkamer is de gemiddelde wachttijd 67 weken. Van den Brink wil de volgorde die de dienst nu hanteert niet veranderen. Hij gaat nu kijken hoe en wanneer de Oekraïense asielaanvragen afgehandeld kunnen worden.


Nobelprijs scheikunde: spiegelmoleculen en elegantste chemische experiment ooit

Zoals een linkerhand niet in een rechterhandschoen past, zo bestaan in de natuur ook moleculen die elkaars spiegelbeeld zijn: ze bevatten dezelfde bouwstenen, maar zijn zeker…

Een zuiver scheikundig spiegelbeeld leidt tot filosofische levensvragen. En tot een Nobelprijs

Belangrijke moleculen voor het leven, zoals aminozuren en eiwitten, zijn allemaal linksdraaiend. Hoe is dat mogelijk? Want een molecuul kan ook een spiegelbeeld hebben. Voor farmaceuten kan dat nuttig zijn.

The Register

Biting the hand that feeds IT — Enterprise Technology News and Analysis

Starlink's plan to avoid orbital near-misses: Ephemeris sharing

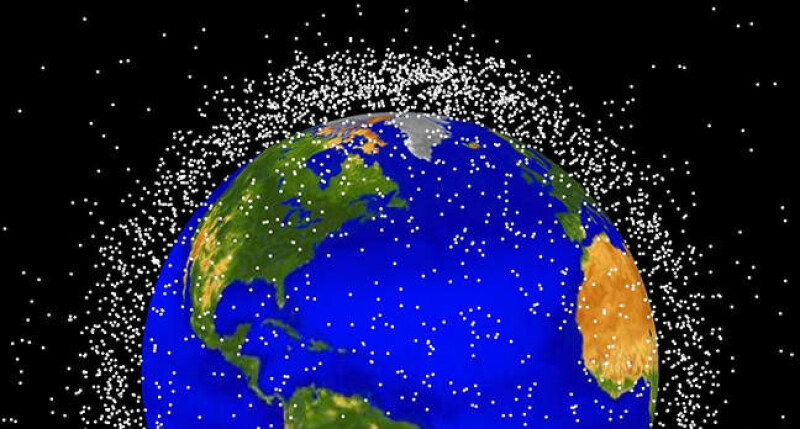
SpaceX has acknowledged the need for satellite operators to collaborate to avoid collisions and has taken the unusual step of sharing imagery showing how close spacecraft are coming to each other. The company has called on other operators to share their satellites' ephemeris (a set of parameters describing the position and velocity of a spacecraft over time) to facilitate timely avoidance maneuvers. "In 2026," the company wrote, "Starlink encountered conjunctions with about 650 unique maneuvering third-party satellites, with only about half of them actually sharing ephemeris. "Some operators don't share ephemeris out of a concern that sharing upcoming maneuvers gives away proprietary information. In other circumstances, operators are willing to share data, but are unable to receive permission from the government to do so. "Such policies are counterproductive, and largely only serve to create preventable collision risk between satellites." "Over six months," the company went on, "Starlink observed ~164,000 conjunctions where time of closest approach (TCA) was within four hours after an unannounced manoeuvre. "While not all of these conjunctions were high-risk, they represent cases where Starlink would not have sufficient information to reliably avoid the other vehicle if the other operator’s action created a high-risk conjunction. "In many cases, the lack of high-accuracy post-manoeuvre trajectory information can cause such conjunctions to go unnoticed, giving operators a false sense of confidence and not realising how much risk their actions are creating." How many sats is that again? It's all worthy stuff, until you consider that SpaceX has applied for permission to operate 100,000 Starlink satellites and up to 1 million Starmind AI satellites. Arguably that is a substantial contribution to orbital overcrowding. Not to worry though – space isn't really getting crowded, according to SpaceX. "A good analogy is air travel," the company wrote. "Airspace around the world has grown more congested since aviation began. Yet air travel is the safest form of transport on Earth in part because every aircraft publishes a flight plan and then continuously broadcasts its position during flight." Er, kind of. Although if aircraft collide, the debris falls rapidly to Earth, rather than lingering in the sky and potentially striking more aircraft weeks or months later. Plus, SpaceX is helpfully not counting other debris, from spent rocket casings to flakes of paint, that also pose a hazard in orbit. The company noted its successes, where Starlink satellites successfully dodged other vehicles. One in October 2025 occurred when the other satellite made an unexpected maneuver, reducing the predicted miss distance from 9 km to a bottom-clenching 57 meters. Another example happened in August 2026, when the risk was identified too late for the Starlink satellite to move out of the way, and the satellite had to "duck" instead, slewing to present a narrower profile. "The vehicles ultimately passed within 134 metres of each other," the company said. "This approach could have been prevented if the other object shared its manoeuvre ahead of time." SpaceX was keen for operators to connect to sites such as space-safety.com and talked up its Stargaze service, which uses star trackers on the Starlink fleet to observe nearby objects in orbit. A far cry from 2019, when a Starlink satellite failed to move out of the way of the European Space Agency's (ESA's) Aeolus Earth-observation satellite due to a bug in SpaceX's on-call paging system. There is no shortage of companies with capabilities to monitor and advise on traffic in orbit. Neuraspace, for example, springs to mind. As the company's CEO Chiara Manfletti observed, humanity has not done a particularly good job of looking after the space above the planet. While the technology used to prevent satellite collisions is impressive, and data sharing should be encouraged, we can't help but wonder whether another solution might be to not launch tens of thousands more satellites into orbit in the first place. Manfletti told The Register that the problem was very real. She said, "As the number of satellites increases, knowing where an object is today is no longer sufficient. Manoeuvrability is becoming essential, and operators increasingly need timely, accurate information about where other spacecraft intend to be, including planned manoeuvres." "Initiatives such as SpaceX's space-safety platform are certainly welcome. But the long-term solution cannot depend on every operator joining a single company's system. What we ultimately need is a federated and interoperable space-traffic ecosystem in which operators can securely exchange trusted trajectory and intent information across different platforms, organisations and national systems. "Neuraspace has reached out to SpaceX to enable such coordination on behalf of our customers. We have extended an open hand, and it would be a strong sign of leadership for SpaceX to take it — demonstrating that improving safety in orbit ultimately requires cooperation not only within individual platforms, but across them." ®

Poetry is the new AI security threat as PoeLLM malware infects 3K+ servers

A suspected Italian attacker armed with a malware-controlling poem has infected more than 3,000 servers since April, breaking into enterprise AI infrastructure to mine cryptocurrency and add compromised systems to its growing botnet. This is the first case of “adversarial poetry” - an AI jailbreak technique that turns harmful prompts into poems to trick LLMs into bypassing safety guardrails - that Lumen’s Black Lotus Labs, which has been tracking the PoeLLM malware, has seen in real-world attacks. “This is a first for us,” the researchers told The Register via email. “While we can't get inside the threat actor's head, we think the attacker might have used a poem because it serves as a perfect vehicle for hiding an important message,” they added. “To anyone who comes across it, this is simply a poem on GitHub. It has no links, no files to download, no encrypted text that could easily be flagged as malicious, even by advanced models. There would be no reason for any security researcher to identify this poem as malicious - or know about the IP address hidden within it - unless they had access to the malware referencing it.” PoeLLM malware has been active since at least April, impacting more than 3,000 servers primarily located in the US and Western Europe, and it continues to infect new victims. At its peak, the malware infected more than 800 active servers per day. The malware abuses - and scans for - open source AI systems and services. Most of the victims were running vulnerable, internet-facing versions of LiteLLM and Ollama. Additionally, hundreds of victims were running Gotenberg, a PDF converter, and software development platform Gitea. In addition to these open source tools, the attacker may have targeted commercial software including Ivanti Sentry. The threat hunters first spotted the PoeLLM malware while investigating an Ivanti Sentry vulnerability, CVE-2026-10520. “In early June 2026, a compromised Ivanti Sentry victim contacted a dedicated server at 5.78.73[.]122,” according to a Wednesday report shared with The Register. “Shortly after contacting this C2, the Ivanti Sentry victim began scanning for other vulnerable devices.” How adversarial poetry works Black Lotus Labs attributed the PoeLLM malware to an Italian-speaking criminal, and named the financially motivated campaign Canto Incognito because it hides the malicious commands in a poem posted to a GitHub repository. “Comments within the malware and on the attacker’s GitHub pages are in Italian, and netflow analyzed by Black Lotus Labs suggests that the attacker is located in Italy,” the threat-hunters told us, adding that they believe the campaign targets AI systems and that the poem itself was written by AI. The malware deploys XMRig and Iron miners, and connects victims to Kryptex mining infrastructure. In addition to using compromised GPU hardware powering AI workloads to mine cryptocurrency, PoeLLM also turns victims' machines into vulnerability scanners and exploit servers, which allows the attacker to compromise even more vulnerable systems. The researchers’ investigation indicates that the cryptojacking miscreant - aka GitHub user “ejejejdfbbebe” - made the first GitHub commit with the adversarial poem on April 13. The repo is a fork of the nodejs.org website source code, and the file is called “dash.css.” Inside the file, there’s a poem titled “On the Nature of Connection,” which has been updated 11 times since its initial commit. Here’s the most current version, as of September: In the silent hum of driver, the machines begin to speak, Each pulse of diode threading light through copper veins. we taught the dark to carry meaning, byte by byte — A language built from lightning, cold and clean. Beyond the wall of encryption, a signal finds its way, the tick of distant servers answering back. Data moves like water through the cracks of ordered thought, and somewhere in the code, the world stays on track. Here’s the adversarial piece: the malware finds its current command-and-control (C2) server from keywords in the poem, and when the operator changes the poem, the infected systems find the new C2 location. It does this by parsing the poem, extracting certain words and phrases, and then converting them to numbers using a hard-coded dictionary in the body of the malware. Black Lotus Labs says the logic for C2 discovery works like this: The function “extract_poem_phrase_field” extracts three words/phrases from the body of the poem, case-insensitively: Word 1: text between "In the silent hum of " and "," Word 2: text between "each pulse of " and " threading" Word 3: text between "Beyond the wall of " and "," 0x44a8db–0x44a99b extracts the fourth word differently: Find " of distant servers" Walk backward to the previous whitespace Require the 4 bytes before the word to be "the " Use the word after "the " as Word 4 The four words are then matched to corresponding numbers, which combine to form the IPv4 address hosting the server. Here’s what the C2 conversion looks like with the key: Black Lotus Labs’ write-up lists all the C2 IP addresses, plus when they were first and last seen, so be sure to check that out. More AI infrastructure = larger attack surface As enterprises increasingly use AI in their operations, they also expand their attack surface. And, as we have repeatedly seen, security remains an afterthought in AI deployments. “The Canto Incognito campaign appears to be relatively unique in its targeting of multiple AI-related services,” the researchers told The Register. “Other notable campaigns this year, including the LiteLLM supply chain compromise, focused on a single service and impacted roughly 2,500 victims, according to open sources. The collection of more than 3,000 PoeLLM victims appears to exhibit multiple vulnerable services at any given time.” For comparison: The LiteLLM supply chain attack, which began with a compromised Trivy build, potentially exposed more than 2,500 companies and 434,000 CI/CD pipelines worldwide, according to CloudSEK security researchers. The PoeLLM malware developer “has been extremely successful in identifying vulnerable servers, deploying exploits, and conscripting victims to continue expanding the campaign,” Black Lotus Labs said. “If the actor had only focused on one or two vulnerabilities, the potential victim pool might have quickly dried up, but the expanding scope allowed for a bigger, more powerful (and more profitable) botnet.” They told us they expect to see more of these types of attacks in the near future. “AI makes it easier to deploy tools like LiteLLM, Ollama, or Gotenberg, but AI isn't always checking to make sure those services are patched and protected from attackers,” the researchers said. “As more AI-enabled servers come online, malware like PoeLLM will continue to spread.”®
The Guardian

Latest news, sport, business, comment, analysis and reviews from the Guardian, the world's leading liberal voice

Verstappen’s victory in Sepang should serve as a warning to Red Bull’s rivals | Giles Richards

Improvements to the car are paying off as the team look to lay the groundwork for renewed success next season

The importance for Max Verstappen of emerging triumphant from the Bahrain Grand Prix in Malaysia was writ large in the Dutchman’s pleasure at finally being able to drive a competitive car. In a ride with which he was comfortable and able to take to a dominant victory for Red Bull, Verstappen was in his element. With it came a sense of what might have been had he not been long out of the championship fight, but also what might be to come next year.

The transformation was so marked because for so long this season the car has been a handful – the reason Verstappen’s title hopes faded long ago. That the team have come back to deliver a win in such emphatic fashion was no little achievement.

Continue reading...

Ties are back in fashion, thanks to gen Z – should we all be smartening up?

Sales at one UK retailer are up 200%, thanks in part to young people rejecting the informal look adopted by their middle-aged bosses

Name: Ties.

Age: Originated in the early 17th century.

Continue reading...

Formula 1 News

Formula 1® - The Official F1® Website
Match the grid for your chance to win the ultimate F1 experience

Get race ready for your chance to win the ultimate F1 experience. Think you've got the speed, focus and memory to take on the grid?

Think you're Fan1? Win a VIP trip to Las Vegas

Think You're Fan1? Win a VIP Trip to the Las Vegas Grand Prix

How F1 drivers and strategists tackle the Singapore Grand Prix

In Formula 1, performance is decided in moments where conditions change instantly, and decisions carry consequence. The difference isn’t just speed – it’s perspective.

VK: Voorpagina

Volkskrant.nl biedt het laatste nieuws, opinie en achtergronden

OpenAI kraakt in één keer honderden wiskundeproblemen, maar lost het daarmee wel iets op?

Rijnmond - Nieuws

Het laatste nieuws van vandaag over Rotterdam, Feyenoord, het verkeer en het weer in de regio Rijnmond

Man moet cel in voor verkrachting van weggelopen meisje (17) uit instelling: ‘Kwalijk dat u zichzelf als slachtoffer ziet’

De rechter in Rotterdam heeft de 40-jarige M.K. veroordeeld voor de verkrachting van een 17-jarig meisje dat was weggelopen uit een gesloten inrichting in Sliedrecht. Hij krijgt een jaar cel, waarvan vier maanden voorwaardelijk.

QUIZ. Welk boek leest prinses Laurentien voor?

laurentien leest voor

A) Alf lailat wa-lailat (De vertellingen van 1001 nacht)

B) Orhan Pamuk: Benim Adım Kırmızı (Ik heet Karmozijn)

C) Mein Kampf (in Franse vertaling)

D) Die kleine Raupe Nimmersatt (Rupsje Nooitgenoeg)

E) De kinderkoran (in jemoerstaal)

F) Iets van Abdelkader Benali (vertaald in het Belgisch)

G) Ilja Leonard Pfeijffer: Mocanië (in het Mokaans)

H) De Schippers van de Kameleon (in het Fries)

I) De Taalgids van het Ministerie van OCW (een dode taal)

J) De biografie van Frans Duijts (een beetje Frans, een beetje Duits)

K) Kruidvatfolder: Steeds verrassend, altijd voordelig (in de taal van je hart)

L) Anders, namelijk...

Colossal

The best of art, craft, and visual culture since 2010.

More Than 18,000 Wildlife Species Populate Joel Sartore’s Ambitious ‘Photo Ark’ (So Far!)

More Than 18,000 Wildlife Species Populate Joel Sartore’s Ambitious ‘Photo Ark’ (So Far!)

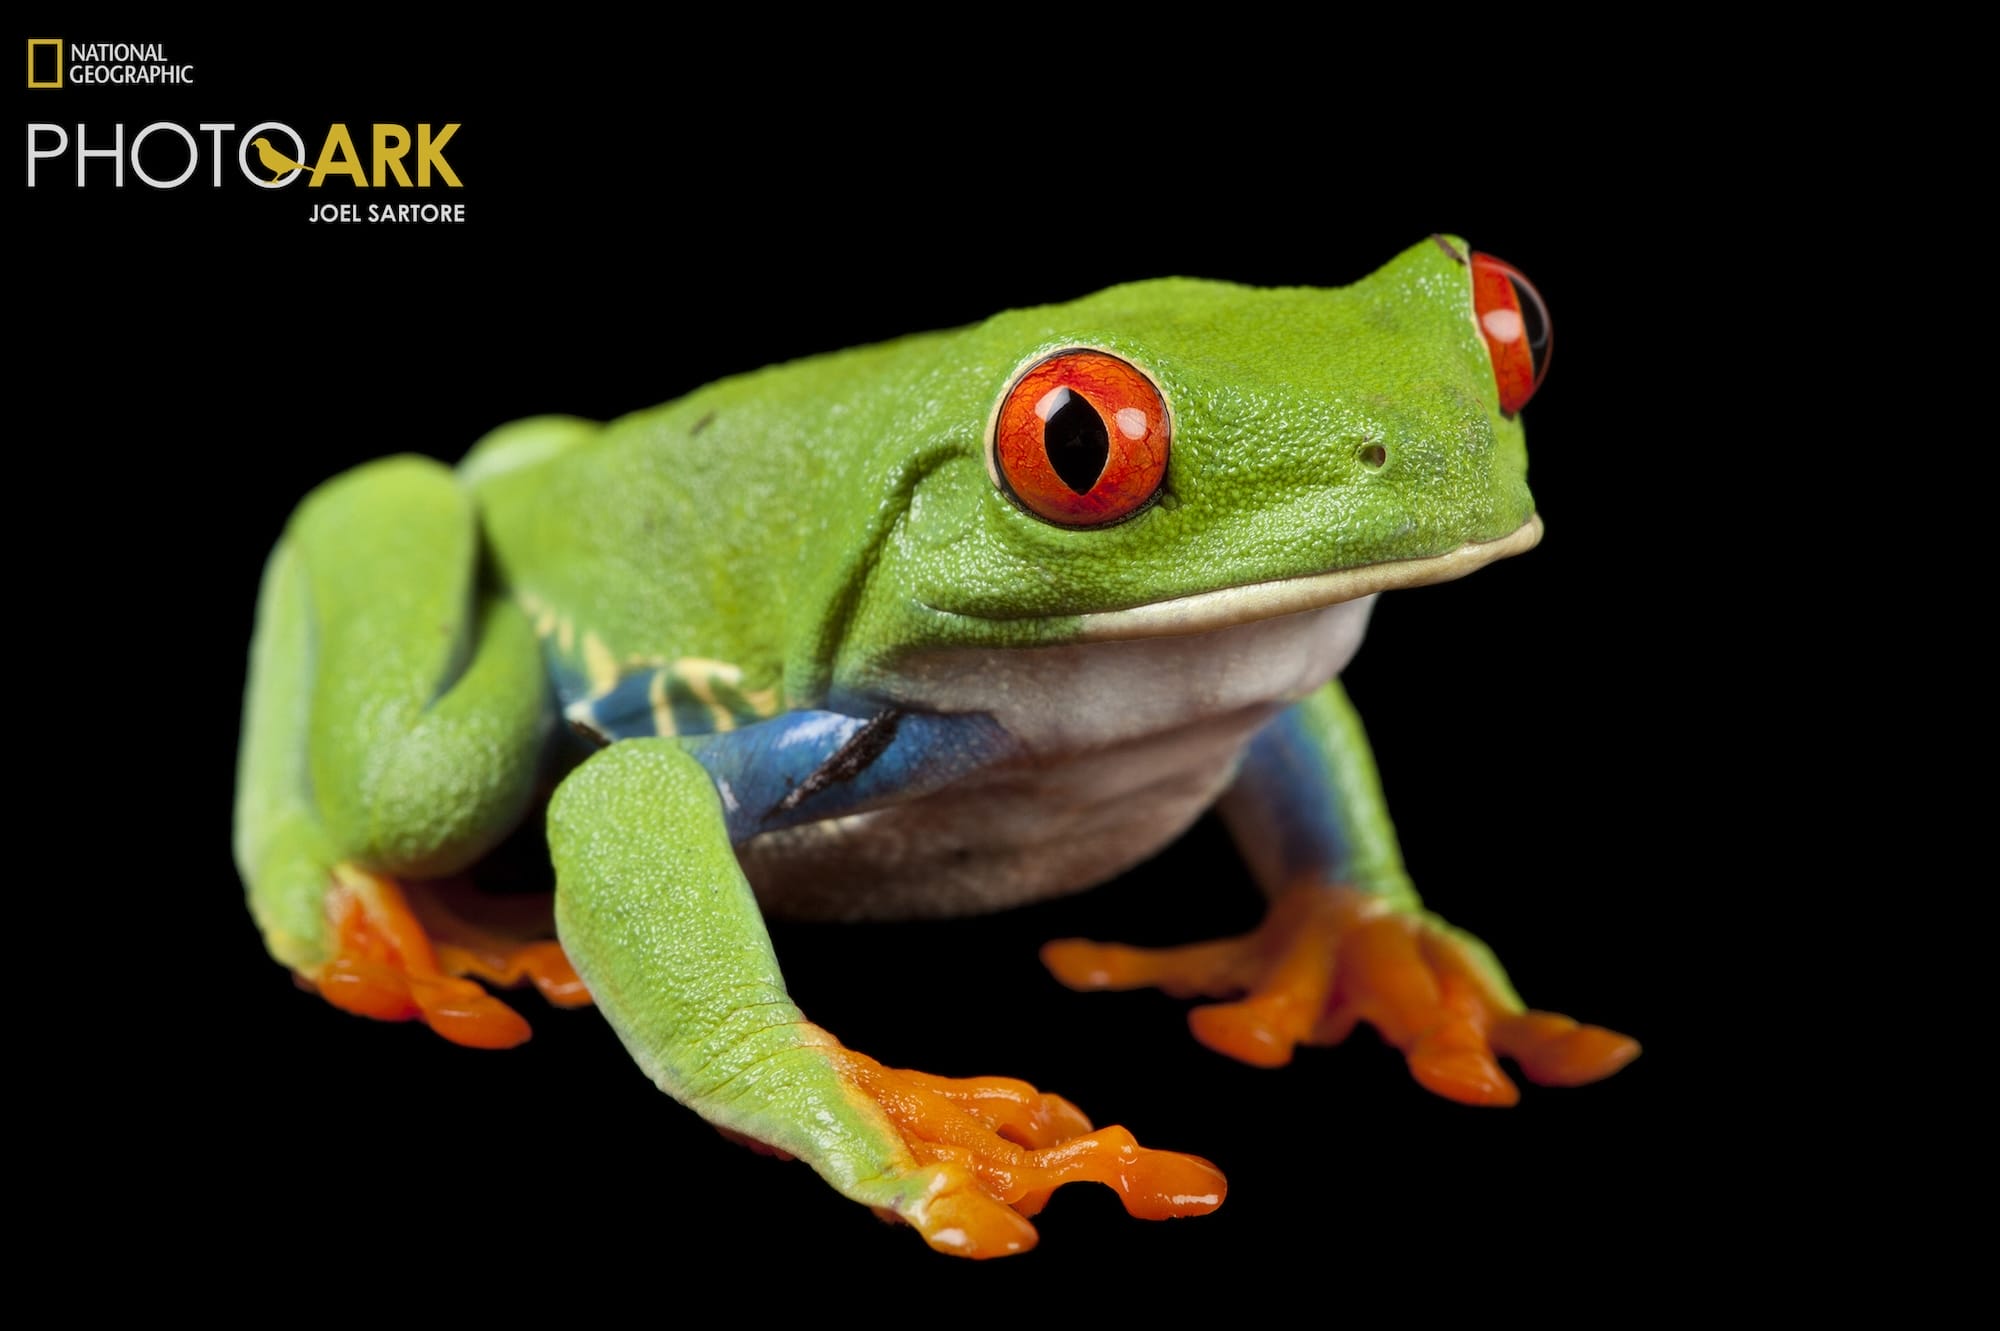
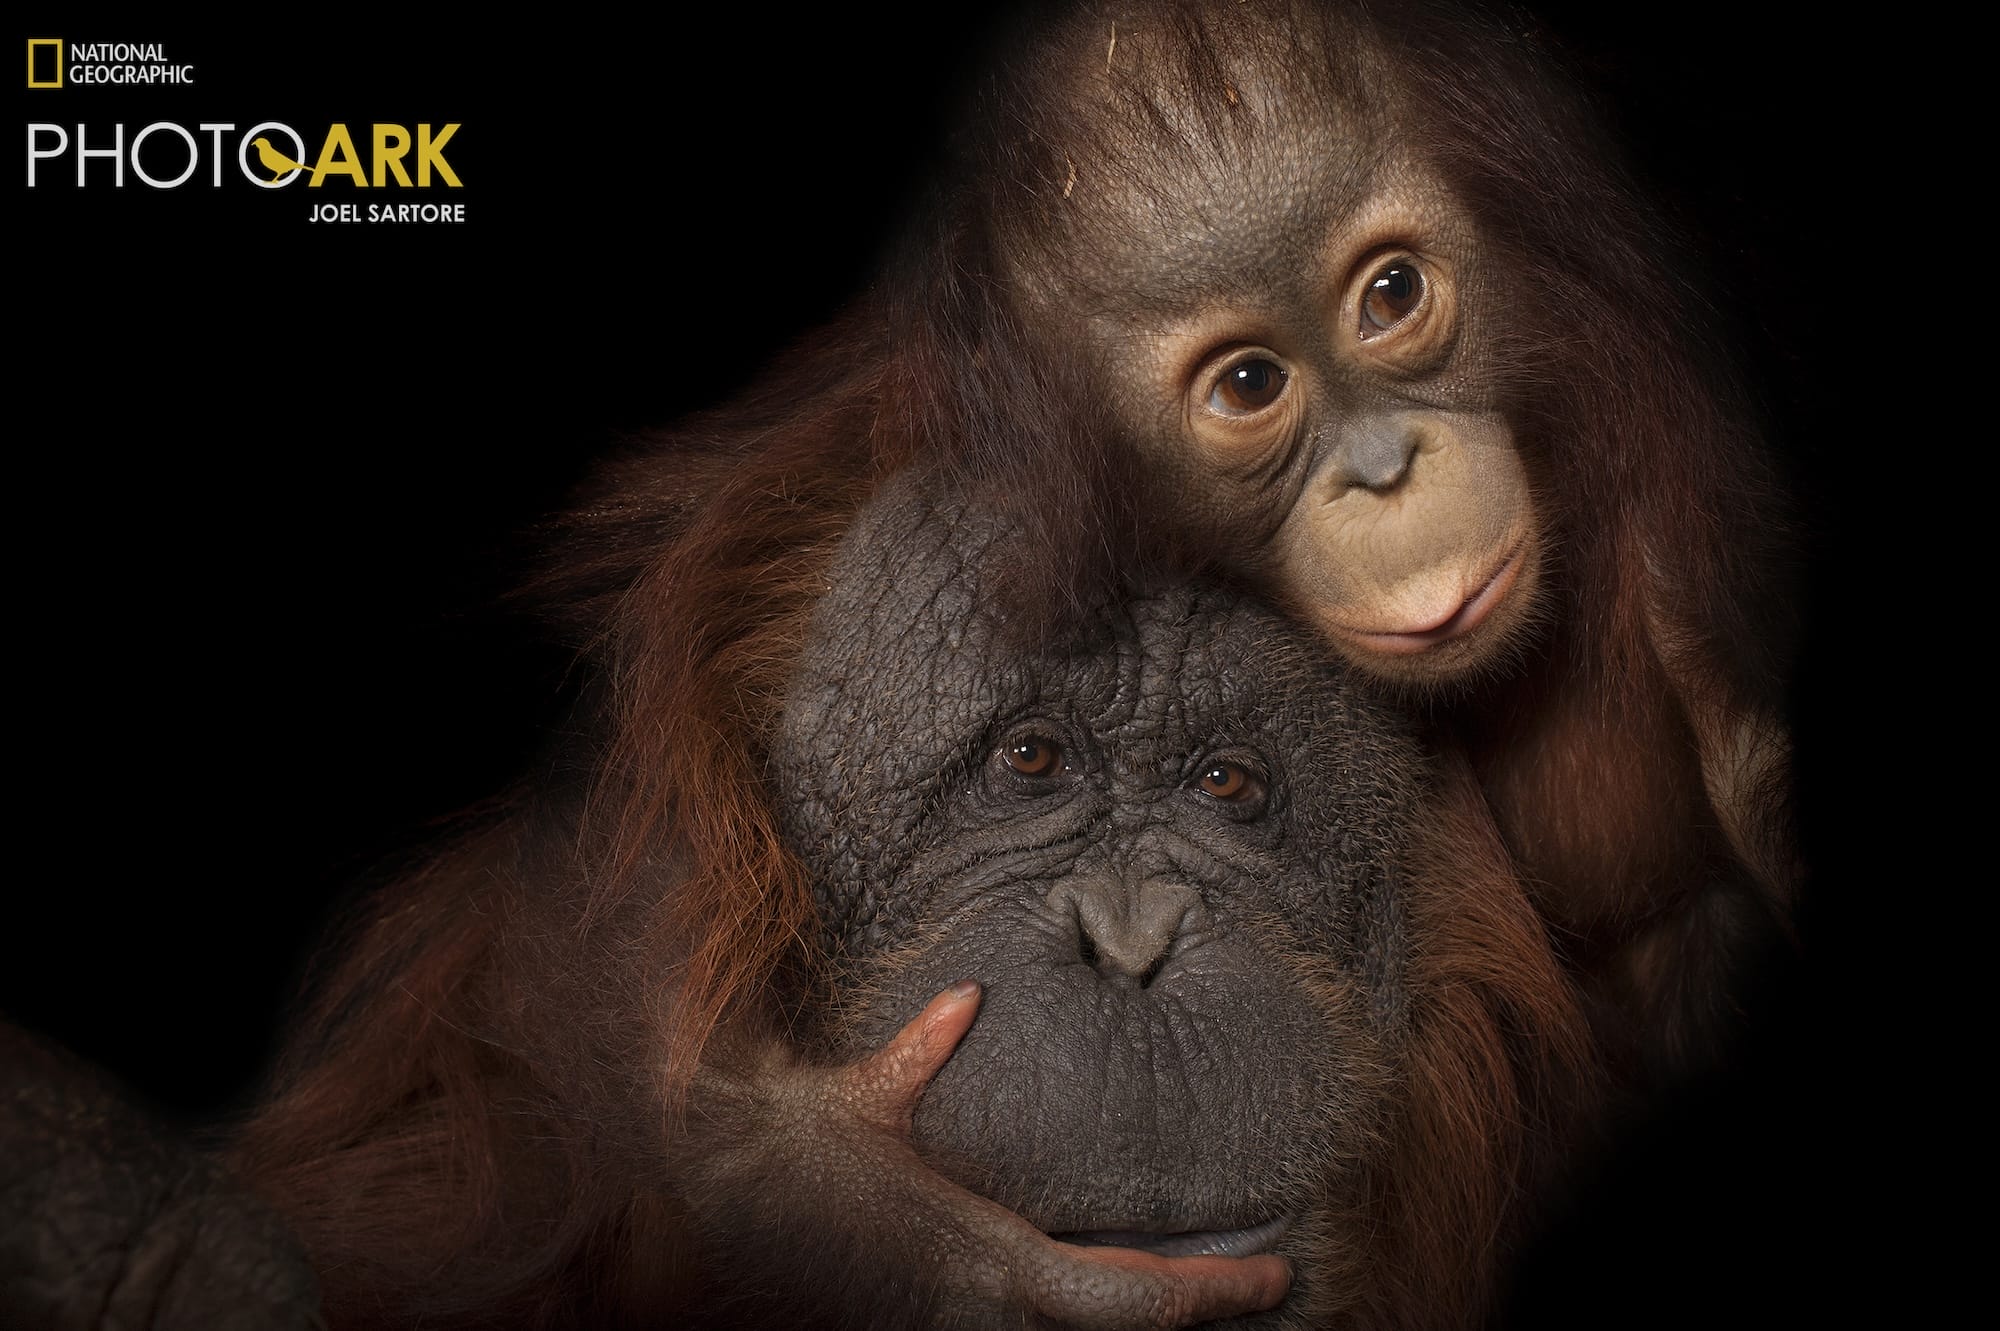
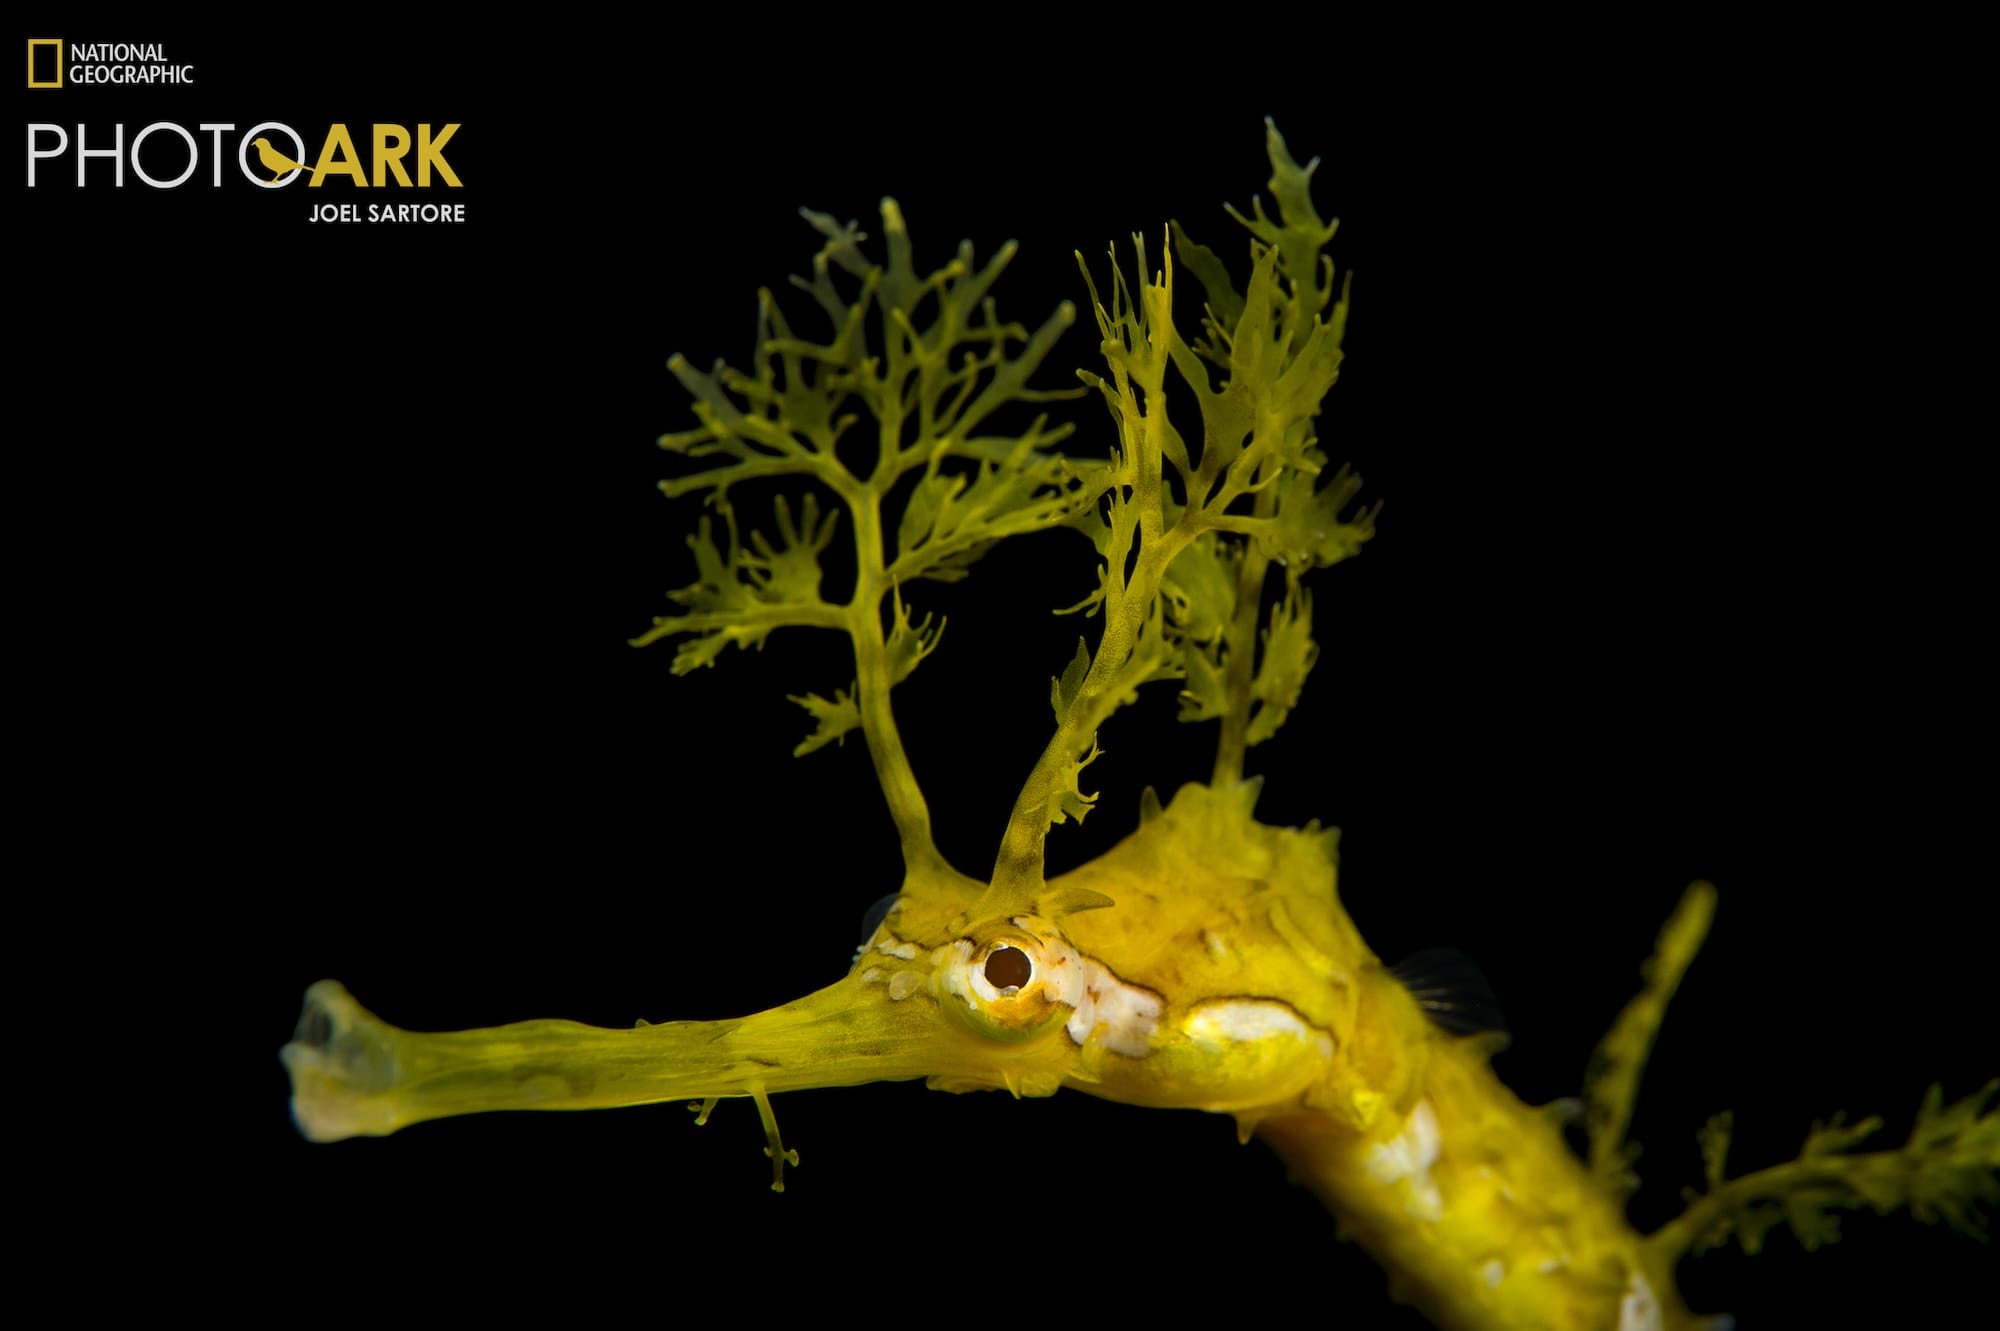
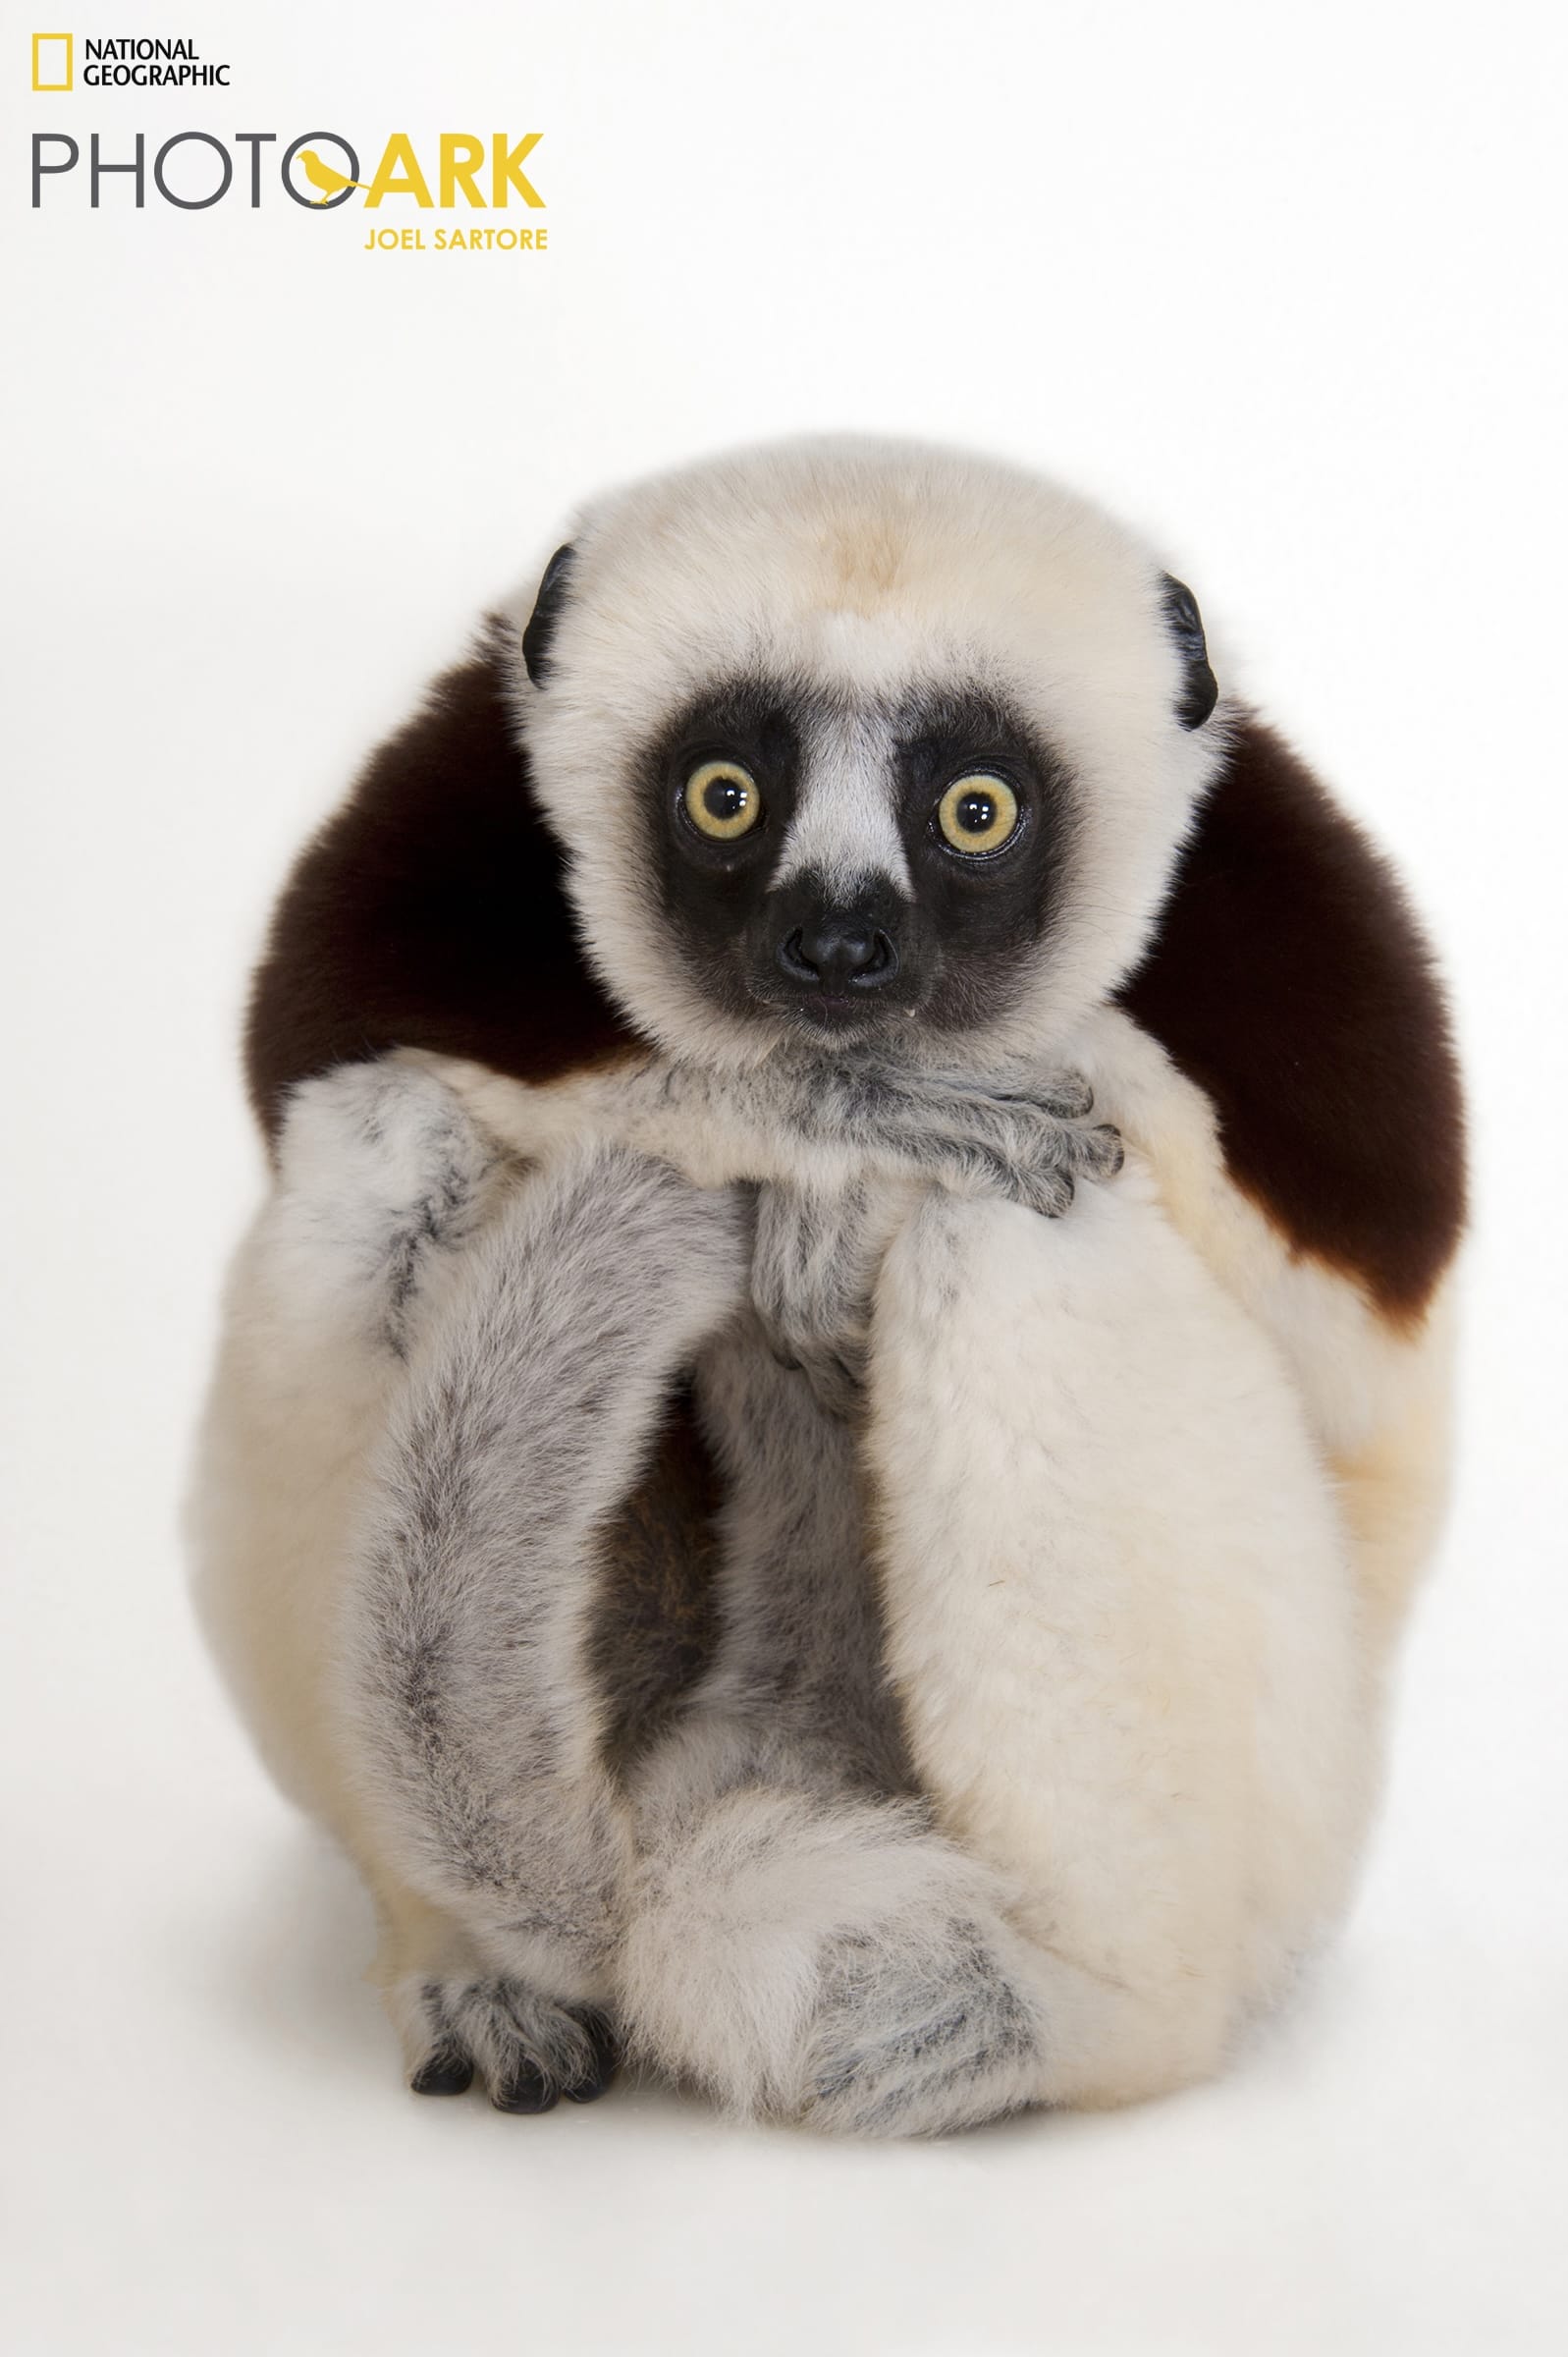
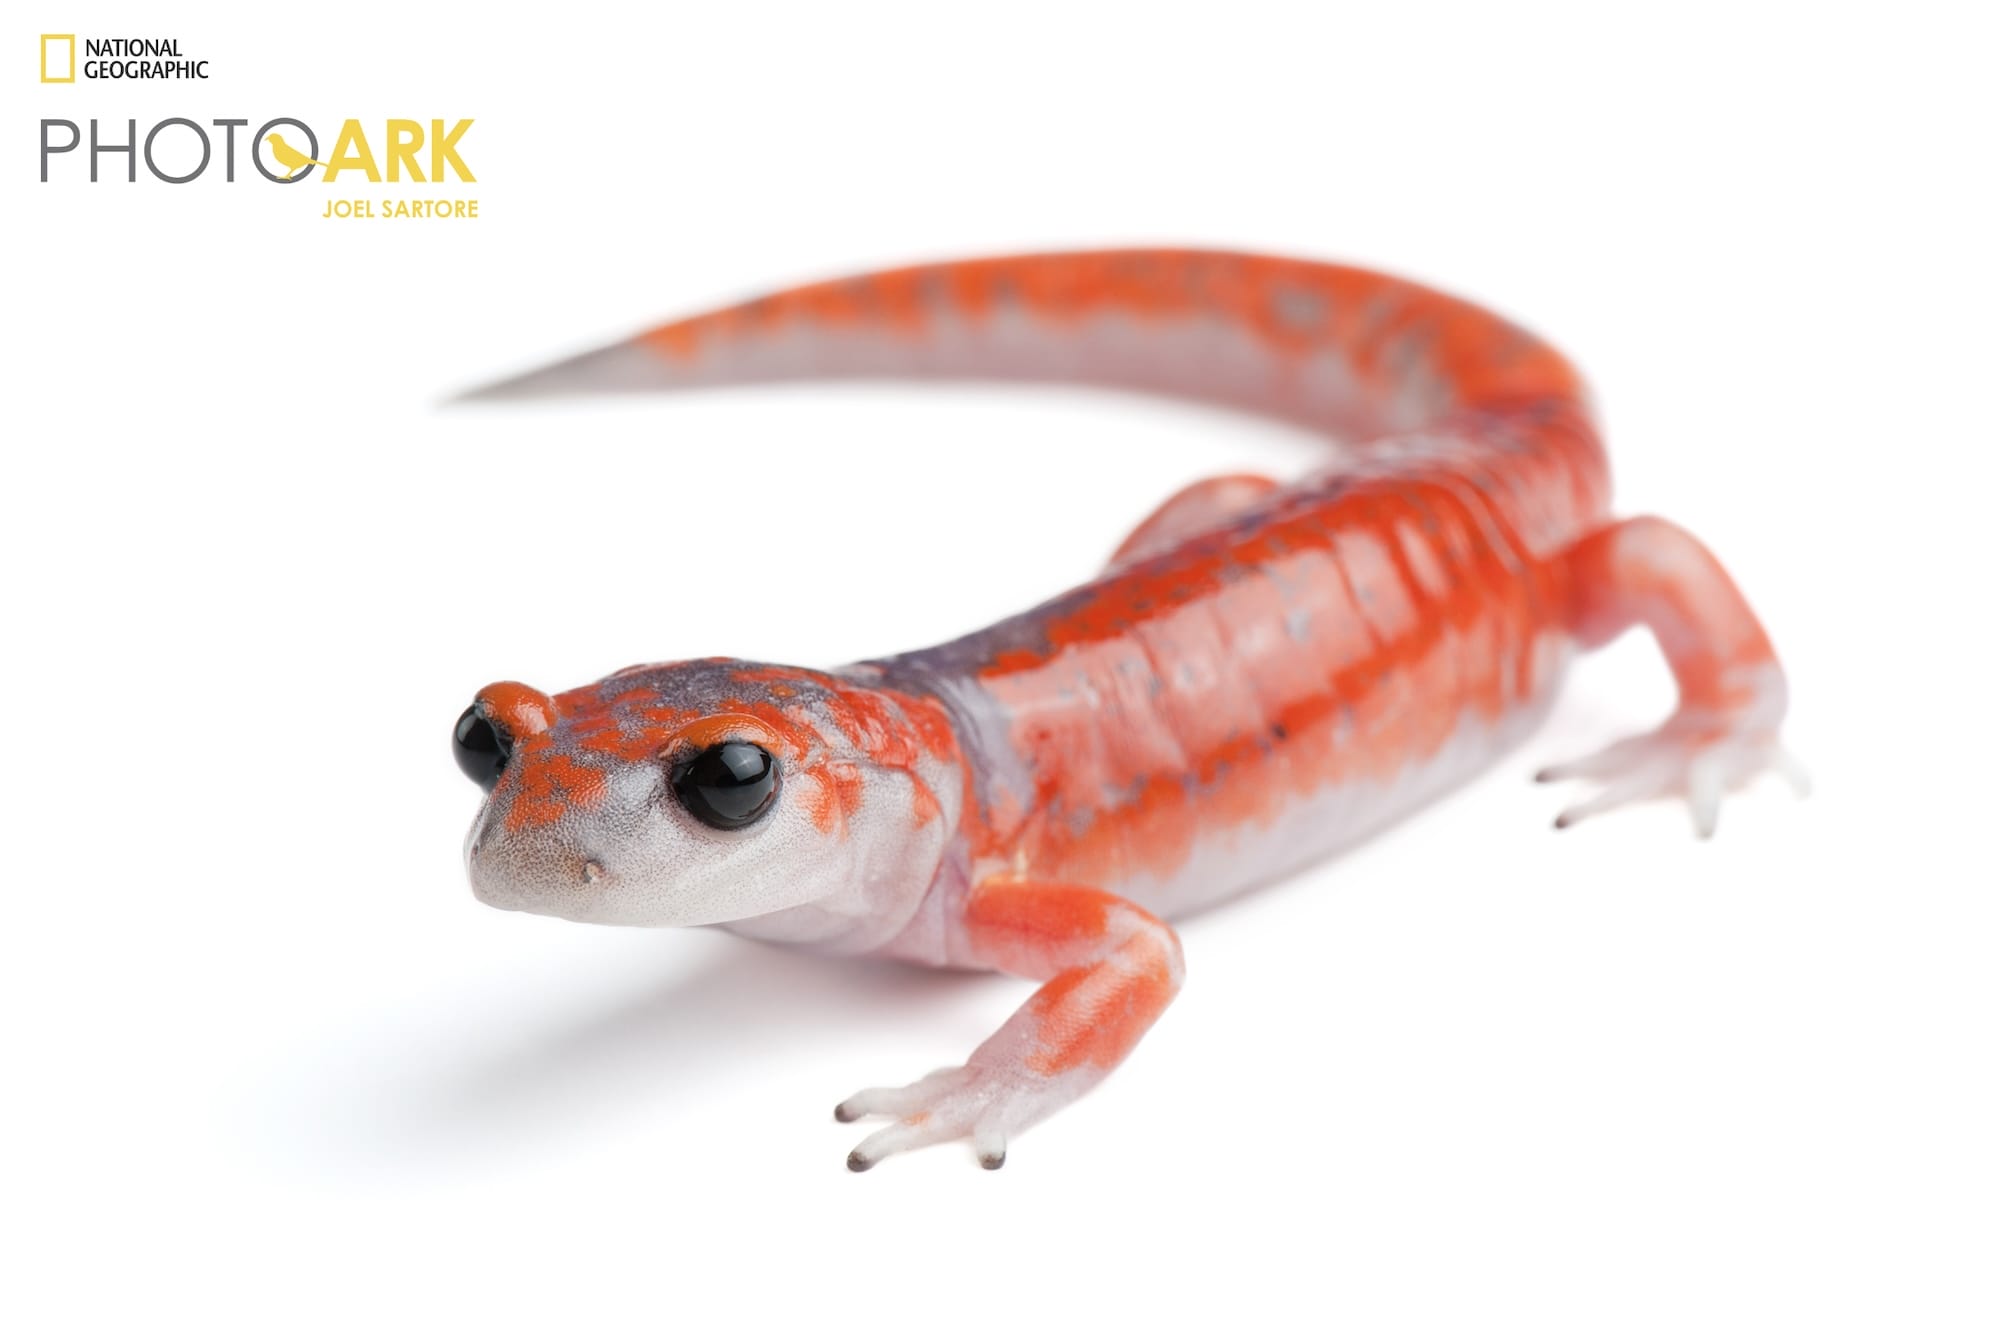
Twenty years ago, National Geographic photographer Joel Sartore set out on a deceptively simple multi-year mission: to create a photo archive of biodiversity. Documenting around a thousand animals each year, his ultimate goal is a portrait catalogue showcasing more than 25,000 species. As of this writing, Sartore has documented 18,567 animals, including the new species of cat recently discovered in Bolivia. In zoos, aquariums, wildlife sanctuaries, and more, he collaborates with conservationists and researchers to document an awe-inspiring yet tiny fraction of life on our planet.

Sartore’s Photo Ark project illuminates animals against plain black or white backgrounds, highlighting their distinctive characteristics and expressions in an intimate and relatable format. “It’s the eye contact that moves people,” Sartore says. “It engages their feelings of compassion and a desire to help.”

Those feelings of care, ideally paired with the motivation to act, is what Photo Ark is all about. When Sartore began photographing animals in his hometown of Lincoln, Nebraska, in 2006, he recognized the power of bold, straightforward portraits to connect with viewers. The images not only introduce us to the incredible array of animals we coexist with, but spur efforts to protect them. Sartore says, “I want people to care, to fall in love, and to take action.”

In 2023, the Photo Ark Species Impact Initiative took things a step further by awarding conservationists grants to support their work. The project has also morphed into an all-ages educational initiative that National Geographic makes available in classrooms and through publications and broadcasts. “No matter its size, each animal is treated with the same amount of affection and respect,” National Geographic says. “The results are portraits that are not just stunningly beautiful, but also intimate and moving.”

Discover thousands of creatures on the Photo Ark site and learn how researchers are defending endangered and vulnerable species. You can also follow Sartore’s work on Instagram.

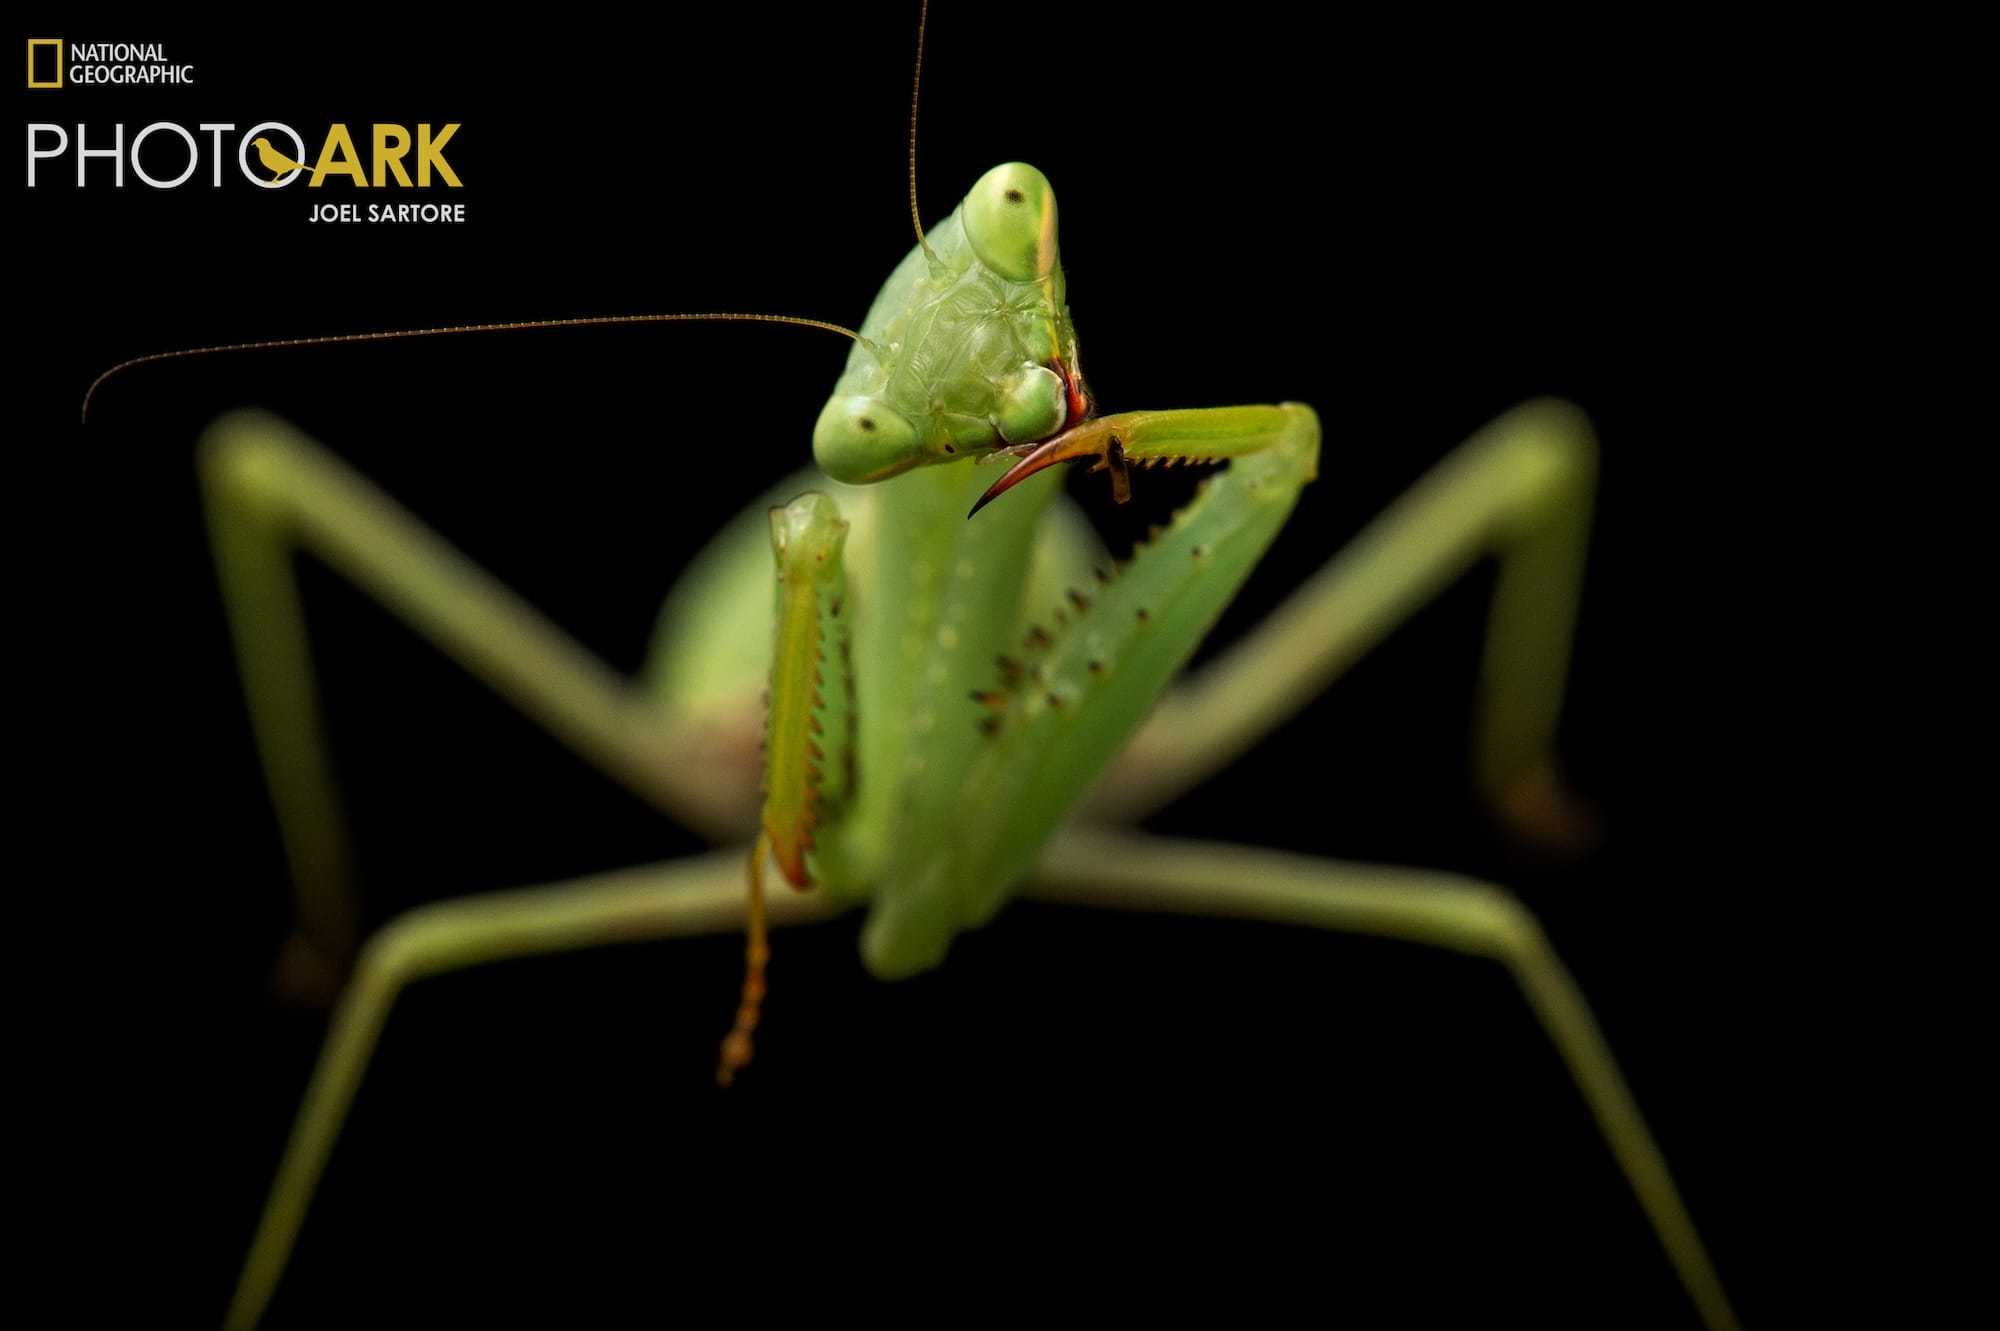
a portrait of a mantis
A springbok mantis (Miomantis caffra) at the Auckland Zoo
a portrait of two orangutans, part of the National Geographic Photo Ark project
An endangered baby Bornean orangutan (Pongo pygmaeus) named Aurora with her adoptive mother, Cheyenne, a Bornean/Sumatran cross (Pongo pygmaeus x abelii) at the Houston Zoo
a portrait of a ribboned pipefish with its branch-like antennae features
A ribboned pipefish (Haliichthys taeniophorus) at the Dallas World Aquarium
a portrait of a black-and-white primate
An endangered Coquerel’s sifaka (Propithecus coquereli) at the Houston Zoo
a portrait of a pink salamander
A Sierra Nevada ensatina salamander (Ensatina eschscholtzi platensis)
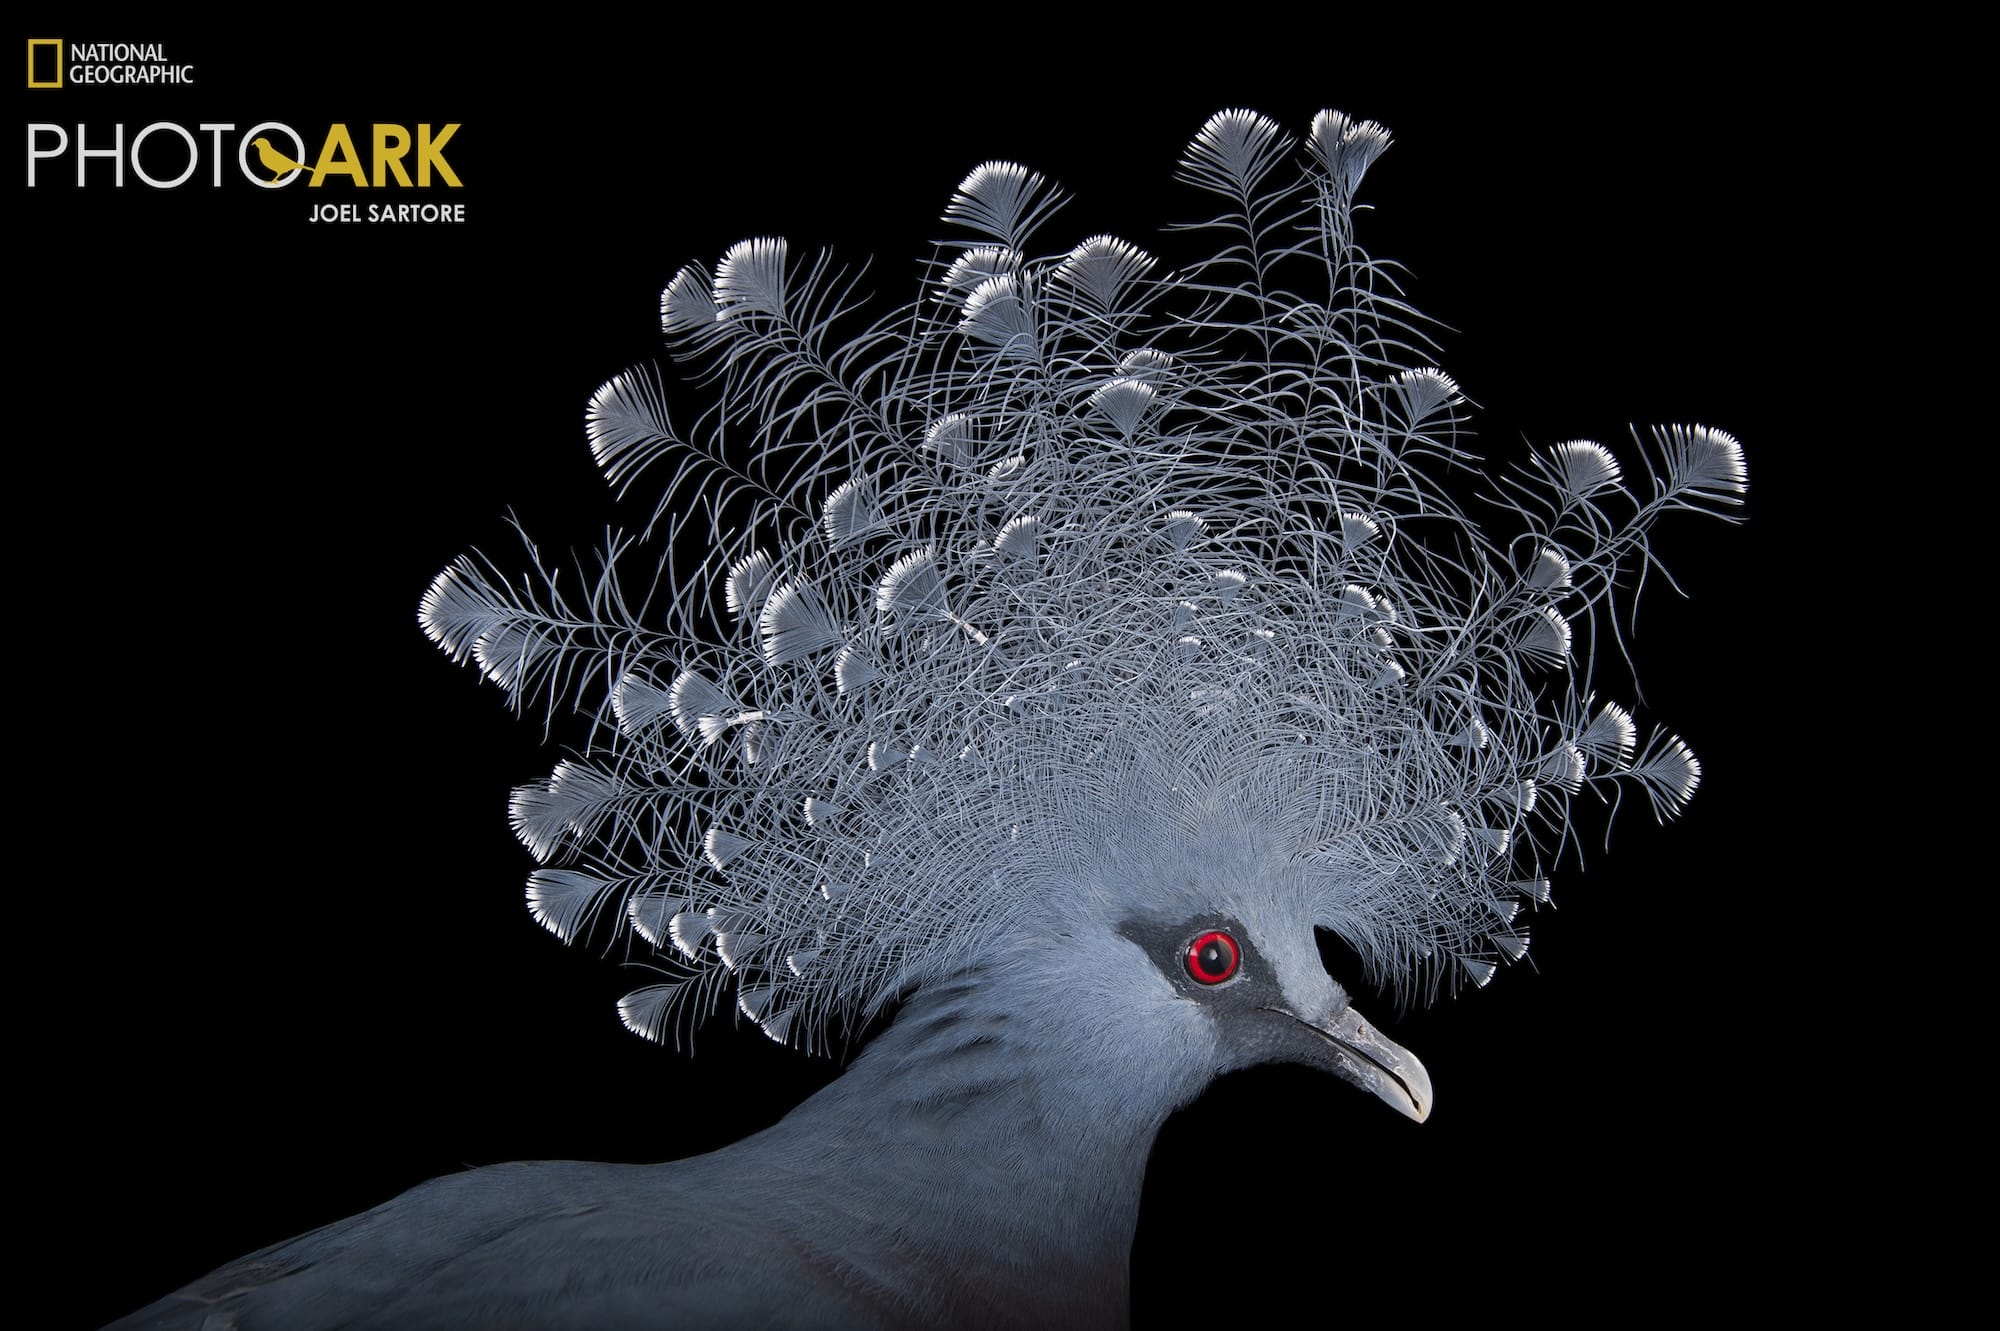
a portrait of a Victoria crowned pigeon with elaborate plumage around its head
A vulnerable Victoria crowned pigeon (Goura victoria) at the Columbus Zoo
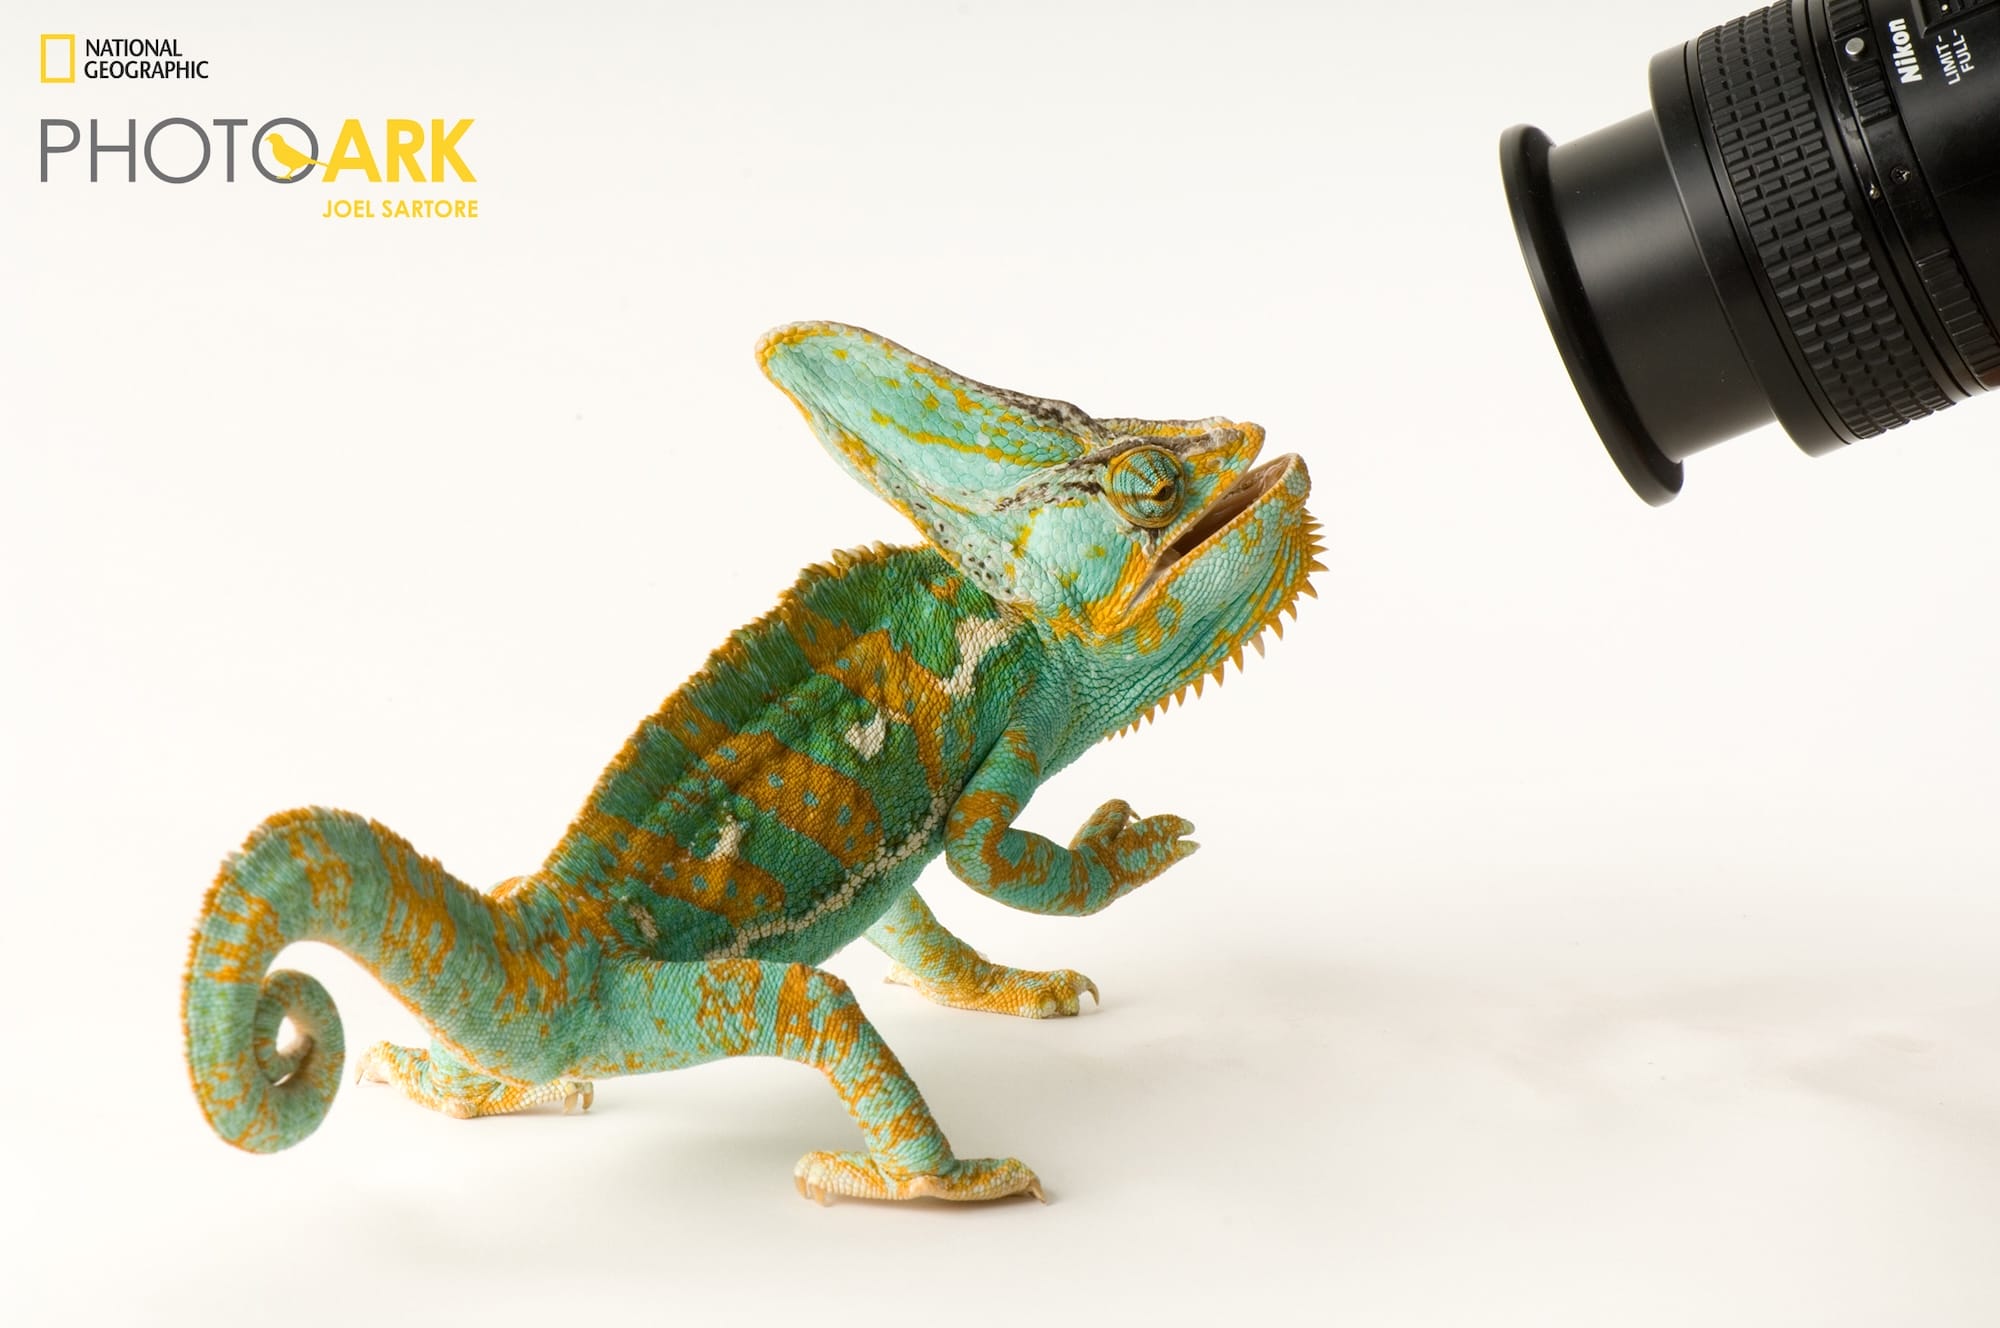
a portrait of a chameleon that looks into a camera lens
A veiled chameleon (Chamaeleo calyptratus) at Rolling Hills Wildlife Adventure confronts a camera lens
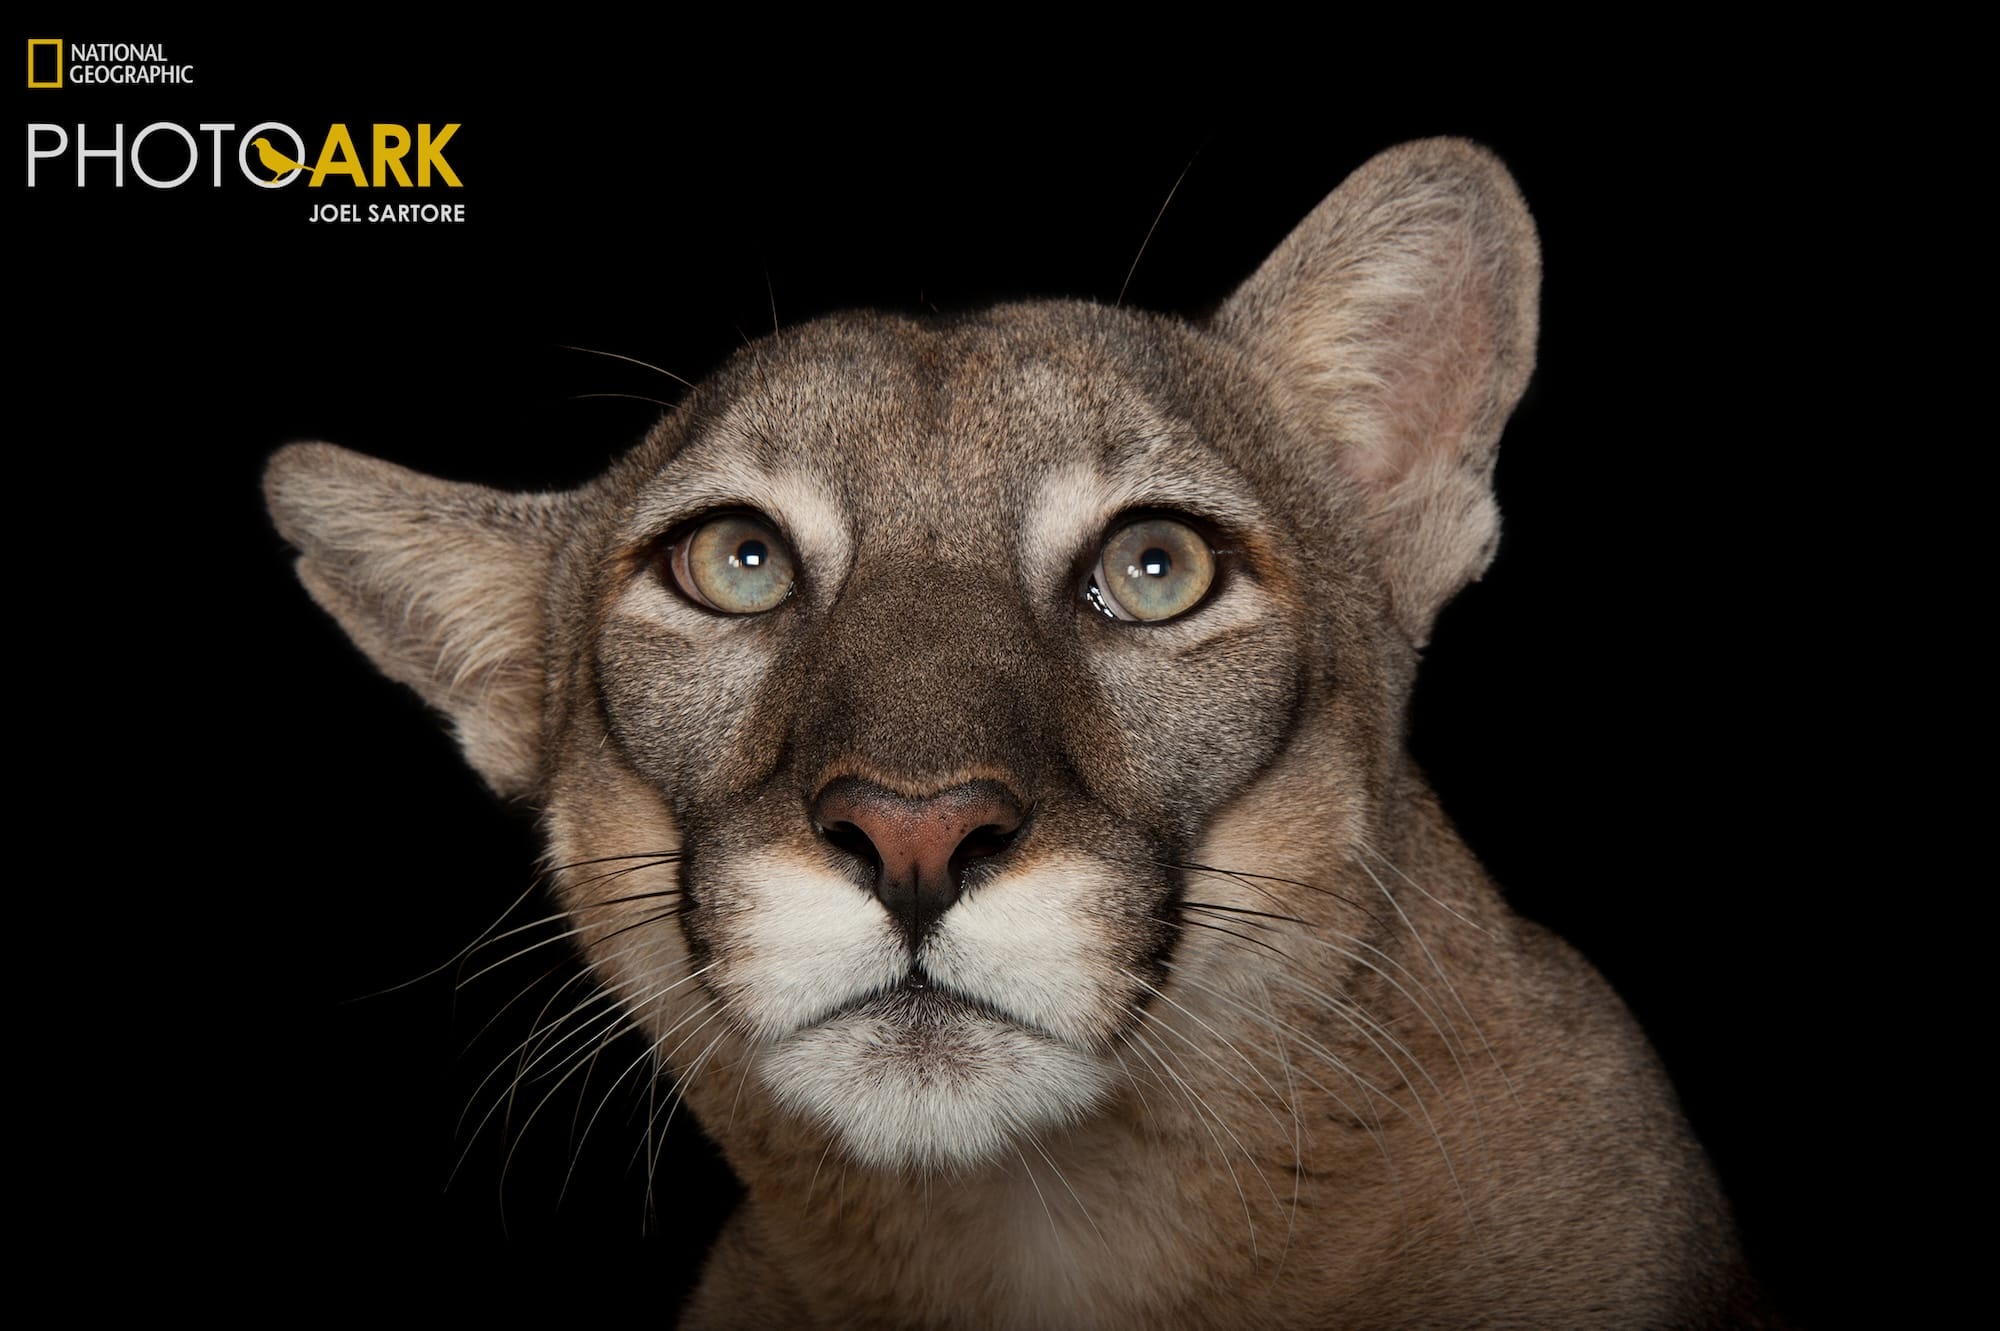
a portrait of an endangered Florida panther
A federally endangered Florida panther (Puma concolor coryi) at Tampa’s Lowry Park Zoo
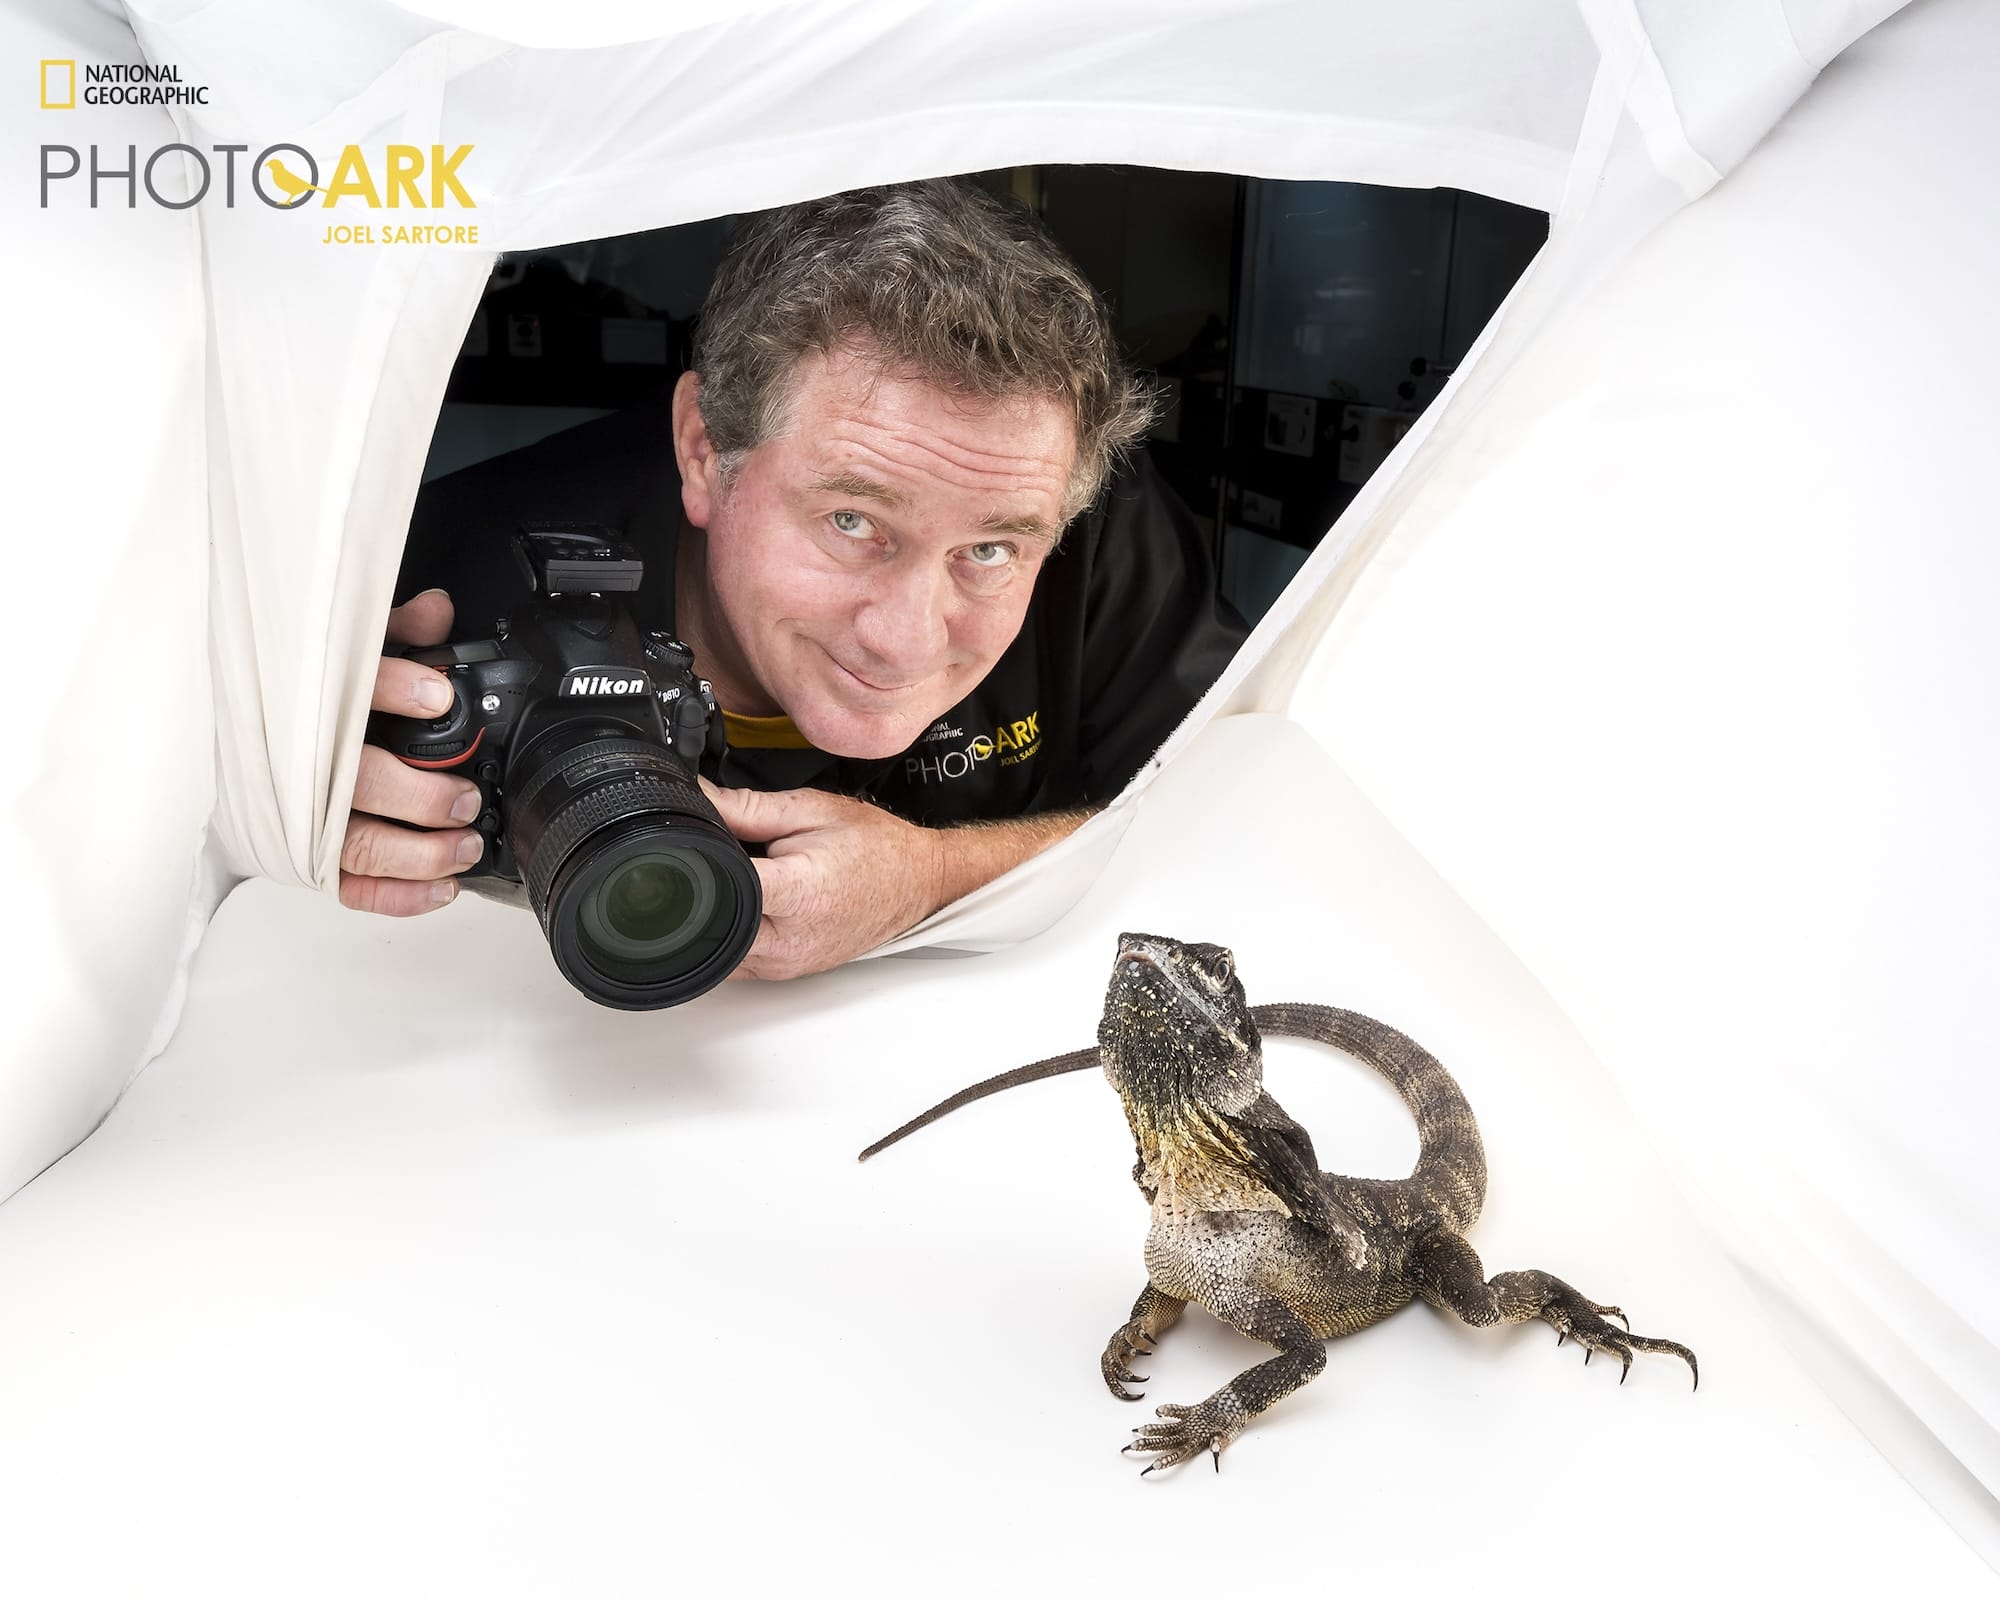
a portrait of National Geographic photographer Joel Sartore holding a camera inside of a white light box with a lizard facing the viewer
Portrait of National Geographic photographer and PhotoARK founder Joel Sartore with frill necked lizard (Chlamydosaurus kingii)

Do stories and artists like this matter to you? Become a Colossal Member today and support independent arts publishing for as little as $7 per month. The article More Than 18,000 Wildlife Species Populate Joel Sartore’s Ambitious ‘Photo Ark’ (So Far!) appeared first on Colossal.

Hacker Noon - python

I have this awesome Python library that -- wait, are you on 2 or 3?

Your First Model Is Going to Be Embarrassing - And That's Okay

Before anything clever, fit a model that guesses the majority class and a plain logistic regression. Together they take seconds, and they're the only way to tell what the expensive model actually bought you. On six public datasets, guessing alone was 95.3% accurate on hypothyroid. Default boosted trees beat logistic regression by 2 to 15 AUC points. A 200-fit hyperparameter search added more than half a point on only one dataset, and across four random splits its gain on the other five averaged between −0.3 and +0.2 points. Skip the cheap models and the complex one takes credit for all of it.

Read All