Group’s fighters hit key airport in Aden with explosive moments before plane from Cairo was due to land
Houthi forces appeared to be making slow advances on Wednesday in south-west Yemen, approaching the city of Taiz and firing a missile and an explosive towards the airport in Aden, the chief international hub of the Saudi-backed government.
The explosive hit the key airport moments before a plane was due to land. The British ambassador to Yemen, Abda Sharif, said the attack could have endangered thousands of people. It forced the flight – from Cairo – to be diverted to Jeddah and led to a review about the safety of flights in Aden.
Continue reading...Lithuania and Canada were also pressured to withdraw, and days before #Disinfo2026, logos were wiped off website
The Trump administration pressured multiple countries to withdraw their sponsorship of a leading European conference on disinformation, with Canada, Lithuania and the EU’s diplomatic service subsequently agreeing to do so, the Guardian understands.
The conference, #Disinfo2026, taking place Wednesday and Thursday, is the annual meetup of Europe’s counter-disinformation community and has drawn hundreds of researchers, journalists, technologists and policymakers to a hotel in Vilnius, Lithuania. It is run by an independent Brussels non-profit, EU Disinfo Lab.
Continue reading...Judge tells Tennessee officials all items in execution room must be saved as Pike remains restrained in hospital bed
A judge ordered Tennessee officials on Wednesday to preserve all evidence related to the botched execution attempt on convicted murderer Christa Pike, as it emerged that the state has refused pleas from medical staff to allow her to be unshackled from her hospital bed.
At a hearing in Nashville on Wednesday, judge I’Ashea Myles said: “Anything that was in the actual room” during the attempted execution a week ago must be preserved by the state, including all drugs, intravenous lines and tubing used in the death chamber.
Continue reading...Convicted pair, plus third man released in August, have IPPs replaced after serving much longer than minimum terms
Two men jailed with indefinite sentences for public protection (IPPs) have been freed after each serving about two decades in custody despite receiving minimum terms of two years or less.
A high court judge and a magistrate hearing an appeal after a review by the Criminal Cases Review Commission (CCRC) told Luke Ings and Liam Bennett they would be freed, and also replaced an indeterminate sentence given to a third man, James Ward.
Continue reading... Lots of stupid shit going on lately, but let me try to talk about some good stuff for a change... It's October, and that means that Ribley the Skeleton is back up, and we have a full month of Halloween goodies for you. Let's do this kind-of out of order to hit the big ones first:
 All Hallow's Eve, Sat Oct 31
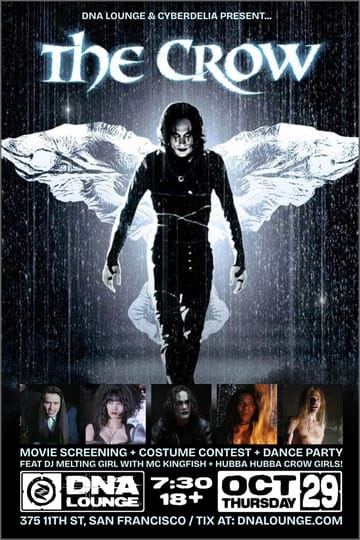 The Crow, Thu Oct 29
 Why 2K, Fri Oct 30
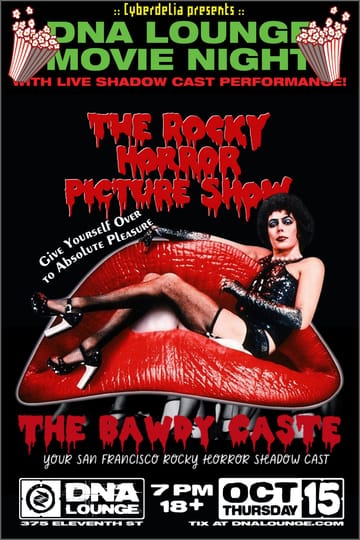 Rocky Horror, Thu Oct 15
 Project X, Sat Oct 17
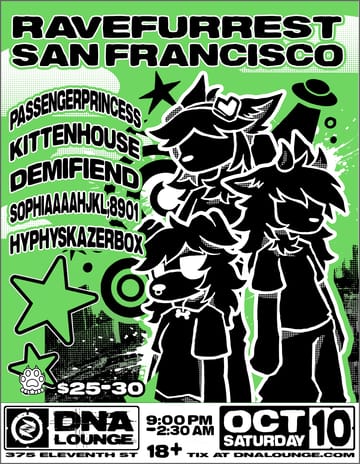 Ravefurrest, Sat Oct 10
 Gotham City Follies, Mon Oct 12
 From Dusk `Til Dawn, Sun Oct 18
 Hazbin Hell-Tel, Sat Oct 24
Halloween Week:
- Thursday October 29, Devil's Night Eve: an encore screening of the 1994 Brandon Lee classic, The Crow, followed by a costume contest and a dance party featuring and inspired by the movie's epic soundtrack.
- Friday October 30: Why 2K, our 90s/2000s throwback night, also featuring a costume contest with Dr. Kingfish.
- Saturday October 31st is the big event, our 25th annual All Hallow's Eve, four rooms of music, and consistently the best costume contest you're gonna see in San Francisco!
October Pre-gaming:
- Next Thursday, October 15: The Rocky Horror Picture Show -- a live screening featuring a live performance by The Bawdy Caste. This is the full audience participation experience! (If you don't know what that means, ask your grandparents.)
- Next Friday, October 17: Project X: Haunted House Party with 2010s hiphop.
- And I guess a furry hyperpop dance party is Halloween-adjacent? That's this Saturday, October 10: Ravefurrest.
We also have burlesque, of course:
- Monday October 12: Hubba Hubba Revue's Gotham City Follies;
- Sunday October 18: Hubba Hubba Revue's From Dusk 'til Dawn;
- Saturday October 24: Hazbin Hell-Tel, a Hazbin Hotel-themed burlesque / drag show.
"...and, Frog."

Not a bug.
Het bericht Hallucination is a feature… verscheen eerst op ICT en Onderwijs BLOG.
Imagine going to a Google website at its correct URL, only to be redirected to a crim's illegitimate copy. Attackers hijacked top-level domains, allowing them to alter DNS records and mint fraudulent HTTPS certificates for several Google domains, and those belonging to other organizations. Google said it became aware of the series of attacks last week in the .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa) country-code top-level namespaces (ccTLDs). “During these hijacks, attackers modified authoritative DNS records and obtained unauthorized HTTPS certificates covering several Google domains, as well as domains belonging to other organizations,” Google security warned on Tuesday. Google did not say which specific domains or organizations were affected. The attacks did not compromise Google’s systems, and Chrome quickly blocked suspected counterfeit certificates across the affected ccTLDs - meaning Chrome browser users are already protected - according to the Chocolate Factory. “Due to the nature of the attacks, we have no reason to believe the Certification Authorities (CAs) that issued the impacted certificates did anything wrong,” the alert said. These types of attacks allow criminals to impersonate legitimate organizations and websites without triggering any browser security alerts. The attacker controls the traffic routing (via DNS) and the private key associated with the unauthorized certificate, which means they can potentially intercept or modify data sent by users to the impersonated site - and abuse the trusted organization's brand to distribute malware or conduct phishing attacks. “While Chrome took steps during these incidents to identify and block suspected unauthorized certificates across the affected ccTLDs, browser-side intervention should not be relied on to protect your users,” Google warned domain owners. “Due to the complexity of DNS hijacks, we cannot guarantee that our analysis identified every affected domain, nor do Chrome interventions reliably protect non-Chrome users.” To ensure that their domains and users are protected, Google recommends ongoing monitoring of Certificate Transparency (CT) logs across all of an organization’s domains, including parked or regional ccTLD properties. This provides near real-time alerts whenever someone obtains a certificate for one of your domains. And if you operate a domain in .gh, .sl, or .as, definitely review recent CT log entries for unexpected certificates. Organizations can also publish restrictive Certification Authority Authorization (CAA) DNS records, which allow domain owners to specify which CAs are permitted to issue certificates for their domains. While this won’t stop certificates from being issued during a DNS hijacking attack, it helps safeguard domains after DNS control is restored. Google recommends CAA policies that restrict issuance to specific authorized accounts and validation methods and prevent attackers from using cached validation state to mint new certificates after a hijacking ends.®
A phishing campaign targeting advertising managers by impersonating Gemini, Claude, ChatGPT, Perplexity, and Manus to steal credentials and multi-factor authentication (MFA) codes has added a fake Muse Ads product to its lure lineup – just eight days after Meta launched its personal AI agent. Meta announced Muse on September 8, and by September 17, a very convincing website – museads.ai – for a product called Muse Ads that promised to help advertisers reach buyers and run sponsored placements popped up online. “The operators already had the platform, so adapting it to a new brand can take minutes,” Oleg Zaytsev, lead security researcher at Island, told The Register. “The striking part is how quickly they turned a timely announcement into a credible reason for someone to act. The same platform could then be repackaged around other familiar tasks, from connecting a business tool to claiming a refund or applying for a job.” The security startup spotted the Muse Ads webpage, and upon digging into the scam uncovered that just the page was new. “Its code, from the sign-in forms to the fake browser window, came from a wider operation that had already run fake ad products for Gemini, Claude, ChatGPT, Perplexity, and Manus,” Zaytsev and fellow Island researcher Ofek Ronen wrote in a blog post published Tuesday. All of these products served as lures for browser-in-the-browner (BitB) attacks designed to trick agency staff, media buyers, and manager-account administrators into handing over their advertising account credentials – along with stored payment methods and client accounts – to digital thieves. “For victims, the potential cost is loss of access to an advertising account, unauthorized ad spend, and exposure of linked client accounts,” Zaytsev told The Register. How the scam works BitB is a clever phishing technique originally detailed by a researcher called mr.d0x in 2022. It involves building a fake login window directly inside a legitimate one. The fake window looks like the real thing, featuring an address bar, title, and URL, but it's just an overlay to steal users’ credentials. According to Zaytsev, this one has likely proved very lucrative for its criminal operators, with hundreds of victim submissions to the platform, and activity still ongoing. “From one frontend alone, we observed submissions involving roughly 200 distinct email addresses over about a month,” he told us. “The operators used the same platform across many similar sites, so we estimate the campaign-wide volume is substantially higher.” Each phony ad product has its own page, with ChatGPT promising users a Monday Google Ads brief, Gemini offering manager account and linked-client support, Claude an advertising portal, Perplexity pitching campaign planning and spend audits, and Manus providing a private Meta integration. Each fake product page also has a “connect” button. When the victim clicks “connect,” it opens the browser-in-browser overlay, with a fake address bar showing accounts.google.com, or an Okta tenant to gain the victim’s trust. The real browser, however, stays on the phishing domain and steals credentials when the victim types them in. A human operator running the campaign sees each submission and chooses what the victim sees and is prompted to do. This includes asking for another password, requesting an SMS or Okta authenticator code to bypass MFA, showing a Google approval code or Okta push request, or displaying a QR code. The platform supports Google, Meta, TikTok, and Okta workflows, and the browser overlay adapts to whatever the victim runs: Window, macOS, iOS, ot Android, and even mimics Safari’s URL pill, Chrome’s custom tabs, and a dark mode. And while the researchers told us they haven’t identified the people operating the kit or found a name under which it’s sold, the operators did expose older source code through misconfigured public GitHub repositories that connected this to a campaign to a larger operation. In addition to the AI ad pages, this operation also used fake refund claims and job recruitment sites as lures with separate builds for Adidas, Google Careers, Robert Half, Tesla, and Louis Vuitton. All of these pages run on one Next.js and Socket.IO stack. Many of the pages also used Vercel frontends with Railway or Render services behind them for state and commands. “A new brand or polished page doesn’t necessarily mean a new attack. Operators can change the lure quickly, but the workflow still has to move someone onto a site they control, collect credentials, and steer them through authentication,” Zaytsev said. “Security teams should maintain a continuous baseline of trusted domains, check the real browser address, and connect similar behavior across different sites,” he added. “Attackers can generate a convincing website quickly; building the domain history and reputation of a legitimate service is much harder. AI can help defenders keep pace with AI-generated websites, especially as they become more convincing and appear more quickly.”. ®




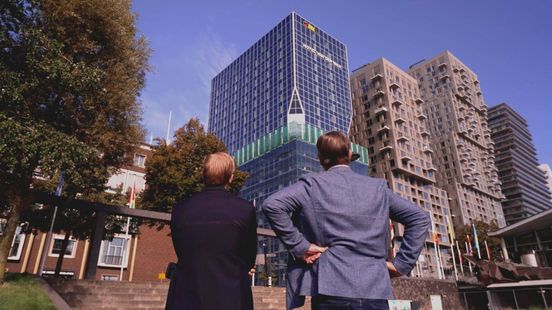
Het voormalige kantoorgebouw van Rijkswaterstaat aan de Maasboulevard in Rotterdam staat een nieuwe toekomst te wachten. Het pand uit 1988 wordt omgebouwd tot modern Van der Valk-hotel. De werkzaamheden zijn in volle gang en op de buitenkant is al een halve toekan te zien. Hoe gaat het hotel er uiteindelijk uitzien?
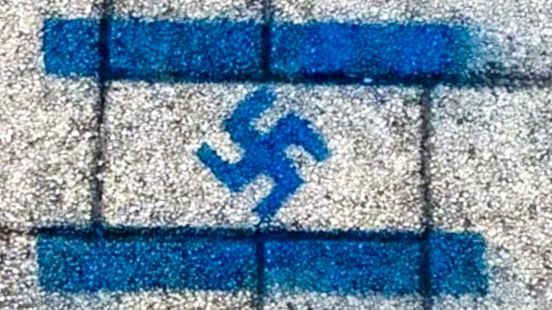
Op meerdere plekken in Nieuw-Lekkerland zijn woensdag bekladdingen van Israëlische vlaggen met hakenkruizen aangetroffen. De gemeente Molenlanden heeft aangifte gedaan.

Woensdag werd de terreuraanslag van Hamas in Israël van 7 oktober 2023 herdacht. In de Amsterdamse modern-orthodoxe sjoel hadden aanwezigen het onder meer over het ‘collectieve trauma’ door de aanvallen.
