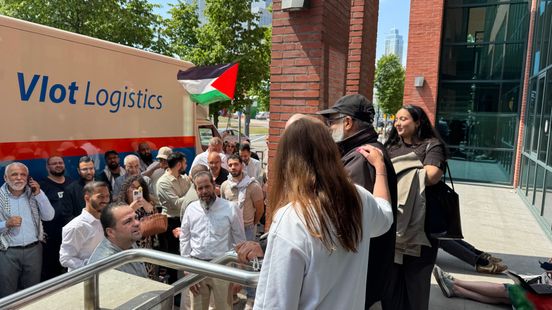
WUT. Chinezen verdrijven ONS FREGAT Zr. Ms. De Ruyter uit Paraceleilanden

Schandalige actie van DE CHINEZEN, sowieso nogal een kwaadaardig regime dat hier illegale politiebureaus runt, journalisten intimideert, banden heeft met een (toegegeven: hele vette) politieke partij, een grote bek opzet over cartoons en, misschien nog wel het ergst van allemaal: advertenties plaatst in NRC Handelsblad. Nu zeggen ze dat ze ONS FREGAT Zr. Ms. De Ruyter (niet te verwarren met de Zr. Ms. Willemstad die naar de Straat van Hormuz gaat), het beste fregat ter wereld van de beste marine ter wereld van het beste land ter wereld, hebben verdreven uit het water rond de Paracel-eilanden. 

"De Chinese strijdkrachten zeggen een Nederlands fregat te hebben verdreven dat ‘illegaal’ de betwiste Paraceleilanden in de Zuid-Chinese Zee zou zijn ‘binnengedrongen’. Het zou gaan om de Zr.Ms. De Ruyter. Volgens China heeft De Ruyter ook helikopters laten opstijgen in het Chinese luchtruim. China heeft marine- en luchtmachteenheden ingezet om het fregat te verdrijven. 'Wij verzetten ons hier ten stelligste tegen en dringen er bij de Nederlandse zijde op aan om onmiddellijk een einde te maken aan deze inbreukmakende en provocerende acties', zegt een woordvoerder van de krijgsmacht in een verklaring."

This will not stand China, als dat fregat daar was dan zal dat fregat daar wel een hele goede reden voor gehad hebben ja. Het is daar om handelsroutes veilig te houden en samen te werken met bondgenoten. Belangrijk voor onze veiligheid en economie. Trots op deze inzet.

Toen alles nog pais en vree was

Social

FBI’s 2025 Internet Crime Report

The 2025 Internet Crime Report was published a few weeks ago, but I only just saw it.
Lots of interesting statistics.

Press release. News articles.

Hacker Noon - python

I have this awesome Python library that -- wait, are you on 2 or 3?

Why Your Python Functions Are Secretly Changing Data You Never Passed to Them

You defined a function with a list as a default argument. Now, it's accumulating data across calls you never connected.

Read All

The Guardian

Latest news, sport, business, comment, analysis and reviews from the Guardian, the world's leading liberal voice

Ribbit is the new Wordle, and I’m here to share it with you

A gentle daily puzzle is quietly becoming the most joyful part of my morning routine​ and reminds me that not every win needs to be epic

There’s been some pretty big news in the last couple of weeks in video game world: the long-running space shooter Destiny 2 is winding up after almost nine years, PlayStation appears to have decided to stop releasing its flagship single-player games on PC, and Microsoft wants us to look like we’re shouting every time we type XBOX. But the biggest news for me is that I have found my new favourite word game. I am going to be so bold as to call it the new Wordle.

Ribbit is one of the varied suite of daily games on Puzzmo, an online puzzle platform. It launched at the beginning of January, but I only recently discovered it because I have been unwell, bored, and spending too much time on my phone. Puzzmo’s daily hits include a satisfying shape-arranging game, variations on chess that make me feel extremely stupid, and pleasing word games, which are my favourites. Circuits has you making connections between the beginnings and ends of phrases (eg “stone cold > cold medicine > medicine cabinet”) as fast as you can. Bongo gives you a bunch of letter tiles and asks you to arrange them for a maximum score.

Continue reading...

Two Venezuelan boys in a forest full of vultures: Silvana Trevale’s best photograph

‘I left Venezuela after someone held a gun to my head. But I returned to show what beauty it has – like these two boys coming back from a fishing trip at an amazing beach’

My parents encouraged me to leave Venezuela. The situation in the country at that time, the mid 2010s, had started to get really hard, with food and medicine shortages – and violent robberies were becoming a regular thing. A lot of people had started to leave and my parents were worried that if I stayed something bad would happen. I had already seen my mum robbed and I’d had a gun held to my head, but that was normal. I was lucky enough to be able to go to England. But when I arrived, to study at Huddersfield University, I had the feeling many immigrants have – of not belonging, questioning who I was and where I was from. I understood what I was losing, too, and it hurt.

I remain deeply connected to Venezuela and whenever I go back to visit my parents we always go to the beach. My whole family loves the ocean: it’s how I spent a lot of my childhood. I started shooting there, too, hanging out with kids, spending time with young people and seeing what they were going through, but I also felt I could give something back. The kids had so much fun during those shoots.

Continue reading...

VK: Voorpagina

Volkskrant.nl biedt het laatste nieuws, opinie en achtergronden

Een Europees-Joodse identiteit? Die bestaat al eeuwen

Rijnmond - Nieuws

Het laatste nieuws van vandaag over Rotterdam, Feyenoord, het verkeer en het weer in de regio Rijnmond

Amin Abou R. vrijgesproken van financiering Hamas: ‘We gaan mensen niet veroordelen op wat er in de krant staat’

Amin Abou R. is door de Rotterdamse rechtbank vrijgesproken van het financieren van Hamas. Volgens de rechtbank is er geen bewijs dat geld voor weeskinderen bij de terroristische organisatie belandde.

De hoop op schone lucht is terug: groene waterstof komt eraan

Vliegen zonder kerosine. Een staalfabriek zonder kolen. Waterstof is dé belofte van een CO2-vrije toekomst. Maar de praktijk bleek de afgelopen jaren weerbarstig.

The Register

Biting the hand that feeds IT — Enterprise Technology News and Analysis

India's cyber agency sets clock at 12 hours to tackle exploited bugs as AI turns up the heat

India's Computer Emergency Response Team (CERT-In) says defenders should endevor to patch or mitigate exploited n-day vulnerabilities within 12 hours as the cybercrime landscape continues its AI-ification. The organization's recommended half-day window applies only to bugs that affect internet-facing or "crown jewel" systems and are known to be exploited. In these cases, CERT-In told defenders to "patch, mitigate, or remove exposure within 12 hours where feasible." For other flaws, such as a standard critical vulnerability (CVSS 9.0 or higher) affecting an internal system, or a known exploited bug affecting an internal system, defenders can enjoy a much more leisurely 24-hour window. The revised suggestions come as part of a new guide released by CERT-In this week to help infosec pros better protect against AI-assisted cyberattacks. "AI-assisted cyber exploitation reduces the time required for adversaries to identify, weaponize, and exploit vulnerabilities, exposed services, weak identities, insecure APIs, and misconfigured systems," CERT-In's report reads. "As organizations become increasingly dependent on interconnected digital infrastructure, cloud ecosystems, software supply chains, operational technologies, and AI-enabled platforms, the potential impact of AI-enabled cyber threats continues to increase across sectors." CERT-In's report follows a trail of news stories in 2026 that all suggest AI is becoming an increasingly important part of cybersecurity for both attackers and defenders. The field of agentic AI has especially matured rapidly in the past year. Consumer-grade tools like OpenClaw have made it easier for non-technical users to experiment with autonomous tech, raising its profile and awareness of its capabilities. Agents are equipped with all the necessary permissions to make significant system changes, but as global intelligence agencies recently highlighted, their behavior can at times be unexpected, and they're also prone to mischief. Security pros are starting to see the potential for AI agents in their workflows, but for attackers, the technology represents an opportunity to hasten all parts of their process, from recon and exploitation to privilege escalation and data theft. CERT-In cited agentic AI as one of the core concerns behind the report's recommendations, and because of the disparate supply chains on which organizations are increasingly reliant, any vulnerability can lead to cascading damage on interconnected systems. Beyond agentic AI, the launches of frontier models such as Anthropic's Mythos and OpenAI's GPT-5.5, two certified cyber workhorses, threaten to empower attackers further with capabilities to uncover and exploit critical vulnerabilities at pace. A 12-hour window: Is it feasible? Any cybersecurity practitioner will attest to the onerous nature of the patching process, and how it's not as easy as clicking "Update," which is why a 12-hour patch window might seem initially unrealistic to some. Urgent warnings and demands for immediate patching are routinely delivered alongside critical vulnerability disclosures, but these fail to account for the downtime required to apply patches, or the testing required to prove that by applying them, everything else won't break. Microsoft has had its fair share of these cases, for example, and many readers will have borne the brunt. CISA's Known Exploited Vulnerabilities catalog is another prominent resource that sets patching deadlines, albeit only for federal agencies, but these are typically set at two to three weeks, or a number of days for the most serious vulnerabilities. The cybersecurity pros who spoke to The Register, weighing in on the CERT-In recommendations, agreed that 12 hours is far too short a window to properly test and deploy a patch, although they said the organization was on to something with its approach. Dray Agha, senior manager of security operations at Huntress, said that CERT-In’s recommendation to "patch, mitigate, or remove exposure within 12 hours where feasible" was solid advice, largely because of the caveat that it doesn’t necessitate a full patch within that time. "By explicitly encouraging temporary mitigations, such as isolation, access restriction, or disablement until a patch is ready, this turns the patching deadline into a highly feasible and necessary containment strategy," Agha told The Register. "And this corroborates the guidance we dispense at Huntress for critical threats: we often advise our community to deploy temporary mitigations to 'get them out of trouble' as soon as humanly possible, and then come up with a more coordinated strategy for patching that respects the business's need to function in its enterprises." Agha added that AI-assisted cyberattacks are seen every day in the wild, compressing the time taken to exploit vulnerabilities, meaning defenders must adapt to this new reality. In the pre-AI days, a 12-hour window to mitigate or patch a known exploited vulnerability was seen as excessively tight, but increased availability of advanced tooling and automation is reshaping the demands of vulnerability management. "Defenders must fundamentally reshape their operations to focus on quicker mitigations – prior to AI, at Huntress, we have seen vulnerabilities exploited within a handful of hours, let alone a full 12 hours," said Agha. He said the 12-hour guideline is less about an arbitrary clock, more about "forcing a necessary readjustment in how organizations drive their security approaches to be beyond compliance and move to a continuous defensive posture. "And this will involve the enterprise functions of the business being a part of the security posture – not just IT, thank you very much – as the consequences of AI-driven exploitation mean faster, higher impact cascading negatives on a targeted business; much better to proactively defend than reactively recover." ®
The Moscow Times - Independent News From Russia

The Moscow Times offers everything you need to know about Russia: Breaking news, top stories, business, analysis, opinion, multimedia

Russian Fuel Tanker Fails to Reach Cuba, Changes Course After Weeks at Sea

The Insider said this suggested U.S. authorities had not permitted the sanctioned tanker to proceed to Cuba.