404 Media

404 Media is an independent media company founded by technology journalists Jason Koebler, Emanuel Maiberg, Samantha Cole, and Joseph Cox.

How a Massive Chinese Crime Ring Hacked Staples to Steal Millions

How a Massive Chinese Crime Ring Hacked Staples to Steal Millions

A Chinese organized crime hacked into retail giant Staples, used that access to fraudulently issue millions of dollars worth of gift cards for stores like Target and Sephora, then went on a nationwide shopping spree, shipping many of the stolen electronics and other products back to China as part of a massive retail theft operation, 404 Media has learned.

The finding, based on a review of court records, reveals the scale at which some organized crime groups are fleecing U.S. retailers, with entire warehouses dedicated to housing the merchandise. The hack of Staples, which has not been previously reported, signals just how sophisticated some of these operations have become.

💡
Do you know anything else about this case? I would love to hear from you. Using a non-work device, you can message me securely on Signal at joseph.404 or send me an email at joseph@404media.co.

In October 2023, Homeland Security Investigations (HSI) received information from an office supply company, saying that hackers had targeted the company and issued more than 15,000 gift cards worth over $5 million, according to a search warrant application unsealed last week. The document does not name the company, but 404 Media determined it was Staples based on various clues: the document says the victim company is headquartered in Massachusetts; uses a company called Blackhawk Network to fulfill its giftcard orders; and the hacked company has an internal customer support system called Nexus. All of those identifying features match Staples, and 404 Media found a reference to Nexus on a former Staple’s executive’s LinkedIn profile.

Staples did not respond to requests for comment.
The document says Staples believed Nexus was only accessible to the company’s internal computers, but that the hackers found a way to access it from the outside. The hackers performed multiple heap dump requests, which is a way to capture all of the data held in an app’s memory at a particular point in time, according to the document. Using the returned information, the hackers were then able to hijack the sessions of logged in Staples customer service representatives to then issue the massive wave of gift cards, it adds. 

The hackers sent the giftcards to various email accounts they controlled. After this, members of the gang went and spent many of the gift cards on electronics at stores like Target. In one example, Target found 35 of the gift cards sourced from the Staples hack were used at a Target in New Hampshire for Apple, Bose, and Powerbeats products in just one hour. Those purchases included gift cards from the hack and other sources too, according to the document. Surveillance footage showed four men “appearing one after another, occasionally interacting with one another and the cashiers.”
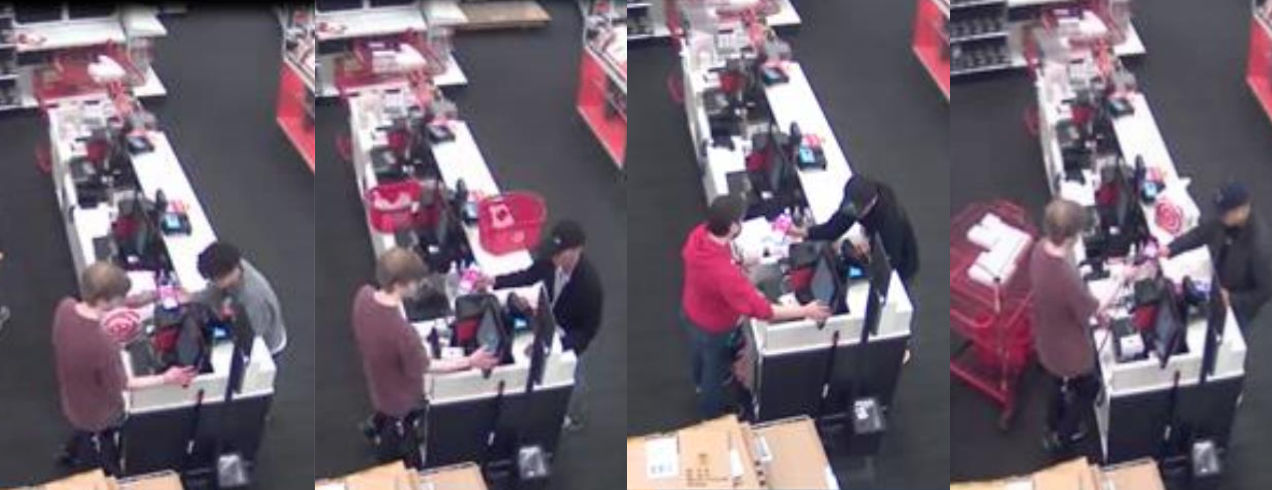
How a Massive Chinese Crime Ring Hacked Staples to Steal Millions
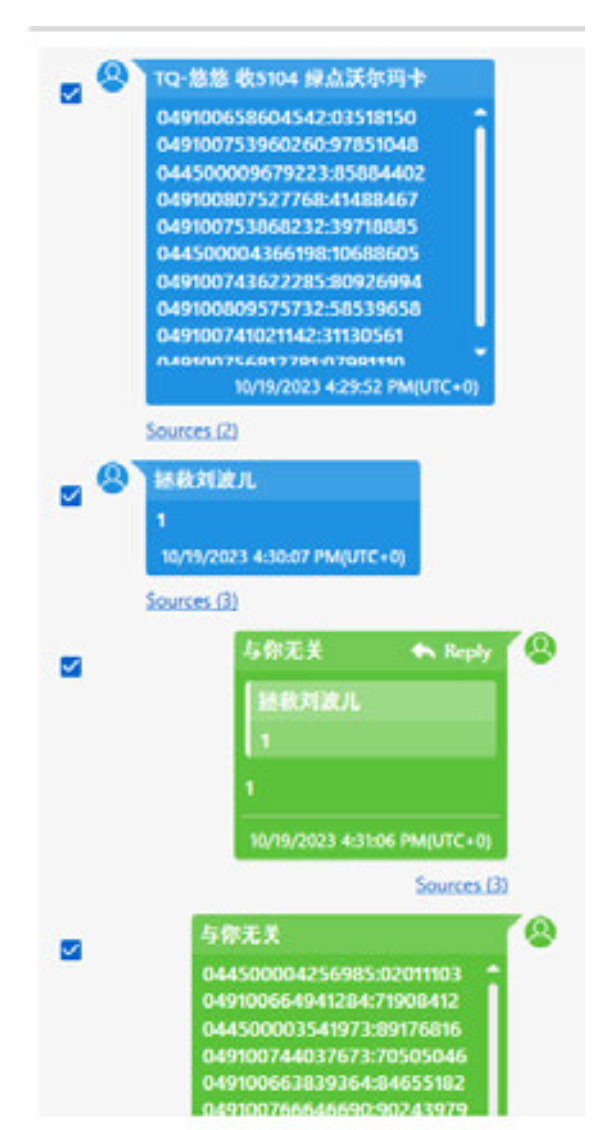
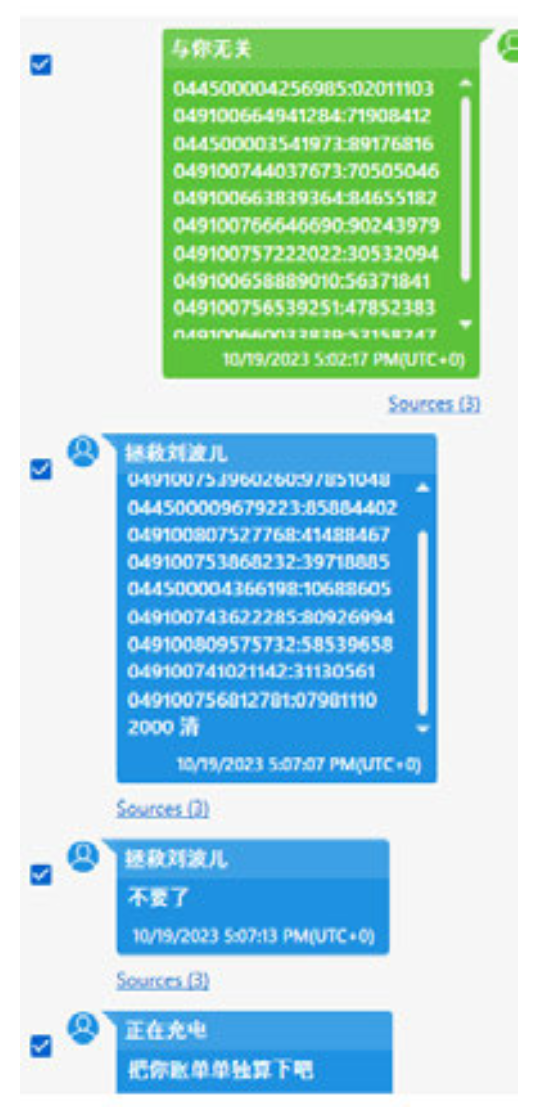
A screenshot from the search warrant application.

“M. CHEN, X. CHEN, JIANG, and the UAM each presented their cell phones to the Target cashier allowing the cashier to scan the electronic Target gift card displayed on their respective cell phones. After an electronic gift card was scanned, all four would use their phone, appearing to access another electronic gift card and presenting it to the cashier to be scanned,” the document says. The men did this until they had “exhausted” all of the gift cards available on their phones, and Target employees later said the four men were well known to staff at the store. They “came into the store almost every day to make numerous large purchases of Apple products using gift cards,” the document says.

Target gave data to investigators showing, for example, the crooks used 3,850 giftcards, worth around $141,000, at 85 different Target stores in 18 states across two days. That encompassed 300 individual transactions, according to the document. Sephora told investigators the gang redeemed around 330 giftcards, worth $58,600, online across 1,500 transactions. Lowe’s, meanwhile, had 450 giftcards, totalling $226,000, redeemed in person and online at more than 22 Lowe’s locations.

Ultimately, the gang was able to use 4,630 of the hacked giftcards, totalling to around $425,000.

The hack is related to a previously announced prosecution of a retail theft ring. Last April, the Department of Justice announced three Chinese nationals were sentenced for their roles in the gift card fraud conspiracy. While the newly unsealed document reveals the hack of Staples, the ring was even bigger in scope than the document suggests. The group acquired more than $100 million worth of gift cards, according to the press release.

That press release mentioned the hacking of U.S. companies, but did not name Staples. “The defendants acted as an integral cog of this international scheme by monetizing the ill-gotten gains obtained by Chinese hackers and scammers that victimized U.S. businesses and the citizens of the United States. IRS-CI is committed to our continued collaboration with our law enforcement partners, both at home and abroad, to stop and deter anyone who seeks to profit off the hard work of U.S. citizens,” Thomas Demeo, Acting Special Agent in Charge of the Internal Revenue Service Criminal Investigation, Boston Field Office, said at the time.

Wel.nl

Minder lezen, Meer weten.

Zo maak je het inbrekers wel heel gemakkelijk, maak deze fout met je sleutel nooit meer

Je legt even een reservesleutel in de brievenbus, zodat de kinderen of de huishoudelijke hulp erin kunnen. In Den Haag maakte een inbreker daar zijn werk van: hij hengelde minstens zestien sleutels uit brievenbussen van appartementencomplexen.

Met die sleutels liep hij tussen april en september 2025 woningen binnen zonder iets te forceren, meldde Omroep West. Hij nam onder meer sieraden en horloges mee. In juli 2026 kreeg de man 2,5 jaar cel, waarvan tien maanden voorwaardelijk, voor tien bewezen inbraken.

Waar hang je je huissleutel dan wel op?

Dicht bij de voordeur, vindt Brandweer Nederland. Bij brand heb je “maar enkele minuten om heelhuids buiten te komen”, zegt woordvoerster Jet Vroege-Gerth tegen verzekeraar Interpolis. Dan wil je niet eerst je sleutel zoeken.

Haar advies: een vaste plek aan een haakje of spijkertje naast de deur, uit het zicht en minstens een meter van de brievenbus. “Zo kunnen inbrekers er niet bij, ook niet met een kleerhanger.” Neem hem ’s avonds ook niet mee naar boven.

De politie is het daarmee eens, maar liever niet in een rommelig sleutelkastje, zegt een woordvoerster. “Want je moet ’m altijd meteen kunnen vinden.”

Mag de sleutel dan in het slot blijven zitten?

Liever niet. Inbrekers hengelen met een kleerhanger of een magneet door de brievenbus, schrijft Interpolis, en een sleutel aan de binnenkant van het slot maakt hun werk makkelijker. “Met een sleutel in je slot, ben je kwetsbaarder voor inbraken,” zegt Vroege-Gerth.

De politie adviseert je deur op slot te draaien en de sleutel eruit te halen, ook als je thuis bent. Monteer ook een kap aan de binnenkant van je brievenbus. “Dat maakt het hengelen nog moeilijker en dus minder aantrekkelijk,” zegt de woordvoerster.

Zo kunnen inbrekers er niet bij, ook niet met een kleerhanger.

Waar laat je een reservesleutel voor de kinderen?

Niet in de brievenbus, en ook niet onder de mat of in de bloempot. Dat zijn de verstopplekken waar inbrekers eerst zoeken.

Een sleutelkluisje aan de buitenmuur is beter, mits het stevig is. Panorama wijst op het advies van het Politiekeurmerk Veilig Wonen: een gecertificeerd kluisje met minstens twee SKG-sterren, het Nederlandse keurmerk voor sloten en beslag.

Hoort je autosleutel in het schaaltje in de hal?

Niet als je auto keyless entry heeft, waarbij de deur opengaat zodra de sleutel in de buurt is. Dieven vangen het signaal van de sleutel op en versterken het, legt de Consumentenbond uit. Eén dief staat bij je voordeur, een tweede bij de auto. Die gaat dan open alsof de sleutel ernaast ligt.

De Duitse automobilistenclub ADAC controleerde 850 auto’s. Bij ongeveer 30 procent is de beveiliging nog niet op orde. Auto’s met ultra-wideband, een techniek die de afstand tot de sleutel meet, krijgen dieven met de gebruikelijke apparatuur niet open.

Leg de sleutel daarom niet bij de voordeur, een raam of een buitenmuur, adviseren ADAC en de Consumentenbond. Een hoesje dat het signaal afschermt of een metalen blik helpt, maar alleen als alle signalen worden tegengehouden. Test het: loop met de sleutel in de hoes naar je auto en kijk of de deur opengaat.

Loop vanavond je hal even na

  • Haal een reservesleutel uit of achter de brievenbus weg.
  • Hang je huissleutel op een vaste plek, uit het zicht en minstens een meter van de brievenbus.
  • Leg een keyless autosleutel verder het huis in, eventueel in een geteste hoes.
  • Laat niemand binnen die onaangekondigd je sloten komt controleren, ook niet namens de politie. Zo kwam een bende nepagenten 26 keer binnen.
  • Draai de voordeur op slot, ook als je maar even weggaat.
Meer weten?

Bronnen: Panorama, Interpolis, ADAC


Duidelijkheid over infrastructuur was broodnodig, maar meer geld blijft dat ook

Karremans’ nadruk op “extra geld” is misleidend. Wat de bewindslieden doen, is schuiven met projecten.

The Moscow Times - Independent News From Russia

The Moscow Times offers everything you need to know about Russia: Breaking news, top stories, business, analysis, opinion, multimedia

Putin, Trump and Xi Could Hold Trilateral Meeting on Ukraine War Next Month, Kremlin Says

Officials in Kyiv have criticized the idea of holding talks that do not include Ukraine, saying they would only “encourage” Putin to continue the war.

The Guardian

Latest news, sport, business, comment, analysis and reviews from the Guardian, the world's leading liberal voice

Life Out of Order by Audrey Niffenegger review – does this sequel measure up to The Time Traveler’s Wife?

More than two decades on, the passion that ignited Niffenegger’s debut has all but evaporated from this confused follow-up

I run a reading workshop which begins with a little shelf assessment. Participants bring a stack of books that have shaped who they are: childhood treasures; new revelations; comfort reads. Books they once cherished but have now outgrown. The usual suspect in that category is Audrey Niffenegger’s 2003 novel The Time Traveler’s Wife. Once smitten, readers now find that time-warped romance cruel. What felt like destiny now feels like a cage. As they explain, I’m always struck by the same thought: Wasn’t it always cruel? Wasn’t that the point?

Henry DeTamble and Clare Abshire are a couple caught in a causal loop. The irresolvable question is where that loop starts: does a bright young art student fall in love with a junior librarian, or does a time-travelling man groom a child to become his future wife? If the answer is both – and it has to be – what are we to make of their marriage? Can you truly choose someone if you believe the choice is already made?

Continue reading...

A composite of eight Euclid VIS exposures of Comet C/2026 S1 (Euclid).

europeanspaceagency posted a photo:

A composite of eight Euclid VIS exposures of Comet C/2026 S1 (Euclid).

A composite of eight Euclid VIS exposures of Comet C/2026 S1 (Euclid).

It was observed by the spacecraft between 16 and 24 September 2026, during the Euclid Deep Field North survey. To create this ‘clean’ image, eight 89.5 second exposures were aligned on the moving comet and combined. Contaminated regions were masked, and background objects were removed, leaving only the comet and its fuzzy cloud of dust and gas (known as a ‘coma’ in cometary terms) visible.

The shorter exposure time of these images (compared with the other images in this release) means that the comet travelled a shorter distance during the exposure, so it appears less like a streak.

Comet C/2026 S1 (Euclid) is the first previously unknown comet to be discovered by ESA’s Euclid space telescope.

Read more

[Image description: A black-and-white close-up view of comet C/2026 S1 (Euclid). The comet appears as a bright central core surrounded by a large, diffuse cloud of dust that gradually fades into the dark background. Faint points of light are scattered across the image. The view focuses on the comet’s glowing coma, which fills much of the frame.]

Credits: ESA/Euclid/Euclid Consortium/NASA, M. Pöntinen et al. 2026; CC BY-SA 3.0 IGO

Sentinel-3C captures Hurricane Rachel

europeanspaceagency posted a photo:

Sentinel-3C captures Hurricane Rachel

Demonstrating that the visible channels of Sentinel-3C’s sea and land surface temperature radiometer are working as expected, on 2 October the instrument captured this image of Hurricane Rachel over the eastern Pacific Ocean, off the coast of Mexico and the Baja California Peninsula. The image marks another important milestone in the commissioning of Europe’s newest Copernicus Sentinel-3 satellite, offering an early glimpse of the instrument’s capabilities as it is being prepared to deliver valuable observations of Earth’s surface.

Sentinel-3C, the third in the series of Copernicus Sentinel-3 satellites, was launched on 15 September. The European Space Agency is, therefore, still in the early stages of commissioning this new satellite for service.

Identical to its older siblings, Sentinel-3C carries a suite of instruments to systematically measure Earth’s oceans, land, cryosphere and atmosphere. The satellite’s ocean and land colour instrument and its synthetic aperture radar altimeter have already returned their first images. Now, as this image of Hurricane Rachel shows, its sea and land surface temperature radiometer is also offering a glimpse of what’s in store.

The instrument observes Earth across nine spectral bands spanning the visible, shortwave infrared and thermal infrared parts of the electromagnetic spectrum, as well as two dedicated channels for fire detection. Its primary role is to measure sea- and land-surface temperatures using thermal its thermal infrared channels.

The visible channels support this process by detecting clouds to prevent contamination of temperature measurements. They also support aerosol retrieval and atmospheric correction, contributing to the quality and accuracy of the instrument's data products. Since this is a false-colour image, vegetation on land appears red.

This image offers a first glimpse from the instrument’s visible channels only – images using its thermal channels are still to come – stay tuned.

Credits: contains modified Copernicus Sentinel data (2026), processed by ESA; CC BY-SA 3.0 IGO

Comet C/2026 S1 (Euclid) observations in context

europeanspaceagency posted a photo:

Comet C/2026 S1 (Euclid) observations in context

Comet C/2026 S1 (Euclid) seen in a wide VIS image for context (left), with a zoom in (right).

The image was captured on 20 September 2026, during the Euclid Deep Field North survey. It is a 560.52 second exposure, so the comet appears like a streak because it moves across the sky during the long exposure. A fuzzy cloud of dust and gas, known as a ‘coma’ in cometary terms, is seen around the object.

Comet C/2026 S1 (Euclid) is the first previously unknown comet to be discovered by ESA’s Euclid space telescope.

Read more

[Image description: A black-and-white Euclid image shows a sky field filled with bright points and faint fuzzy light sources on a dark background. A boxed region is enlarged in an inset, where comet C/2026 S1 (Euclid) is marked by an arrow. The comet appears as a bright elongated streak surrounded by a diffuse cloud of light. Lines connect the inset to the comet’s location in the wider image.]

Credits: ESA/Euclid/Euclid Consortium/NASA, M. Pöntinen et al. 2026; CC BY-SA 3.0 IGO

A House By The Sea

Darren Schiller has added a photo to the pool:

A House By The Sea

1915 bungalow very close to Henley Square, Henley Beach, South Australia

Henley History

Darren Schiller has added a photo to the pool:

Henley History

1915 bungalow very close to Henley Square, Henley Beach, South Australia