12th October: Hundreds of French supermarkets have been hit by a cyber attack that caused their fridges and freezers to heat up, spoiling fresh and frozen food estimated to be worth millions of euros. 2nd November: Dozens of supermarkets across seven European countries have been hit by a cyber-attack affecting their refrigerators and freezers. Around 40 Delhaize supermarkets in Belgium and Luxembourg were affected, while a smaller number of shops were hit in Sweden, Ireland, the Netherlands, Estonia and Finland. 20th November: A behind the scenes cyber-security operation has taken place to secure tens of thousands of fridges and freezers at major UK supermarkets, warehouses, restaurants, petrol stations and stadiums from hackers, the BBC has learned.
From Jennifer Lawrence to Kate Moss, the fuzz-trimmed garments are proving popular with celebrities, while others are DIY-ing their way into the trend
While puffer jackets have dominated winter wardrobes for years, this winter an alternative is emerging: the fuzz-trimmed opera coat.
Originally worn over formal evening gowns, new interpretations come in floor-grazing and cropped styles and are being worn with everything from minidresses to jeans.
Continue reading...
Suspected Chinese spies deployed AI agents which worked autonomously to find a zero-day in an open source application and then abuse the flaw to break into university networks, gaining full control of a server, according to Amazon CISO CJ Moses. The China-linked attacker used Cairn, an open source, penetration-testing framework that has become increasingly popular with cybercriminals who use the AI tool to carry out multi-stage intrusions with no human assistance. In this case, the agents found and exploited a zero-day MONAI Label, an open-source medical imaging AI application. Amazon notified the project's maintainers of the vulnerability, and they released a fix and a security advisory. On September 10, Amazon's Threat Intelligence Team found a server with a publicly hosted instance of Cairn that provided visibility into the campaign targeting universities in East Asia, outside Mainland China, Moses said in a Friday report shared with The Register. The campaign occurred over a period of 48 hours beginning on September 8, and the prompts were written in Simplified Chinese, with timestamps in executed scripts configured to China Standard Time. Before the AI agents found and exploited the zero day, however, they tried to break into another university’s Redis server over about 16 hours and 148 sequential actions, including abusing Redis's replication feature to load unauthorized code, escaping its scripting sandbox, writing to its configuration files, and corrupting its memory. None of these were successful, and when those actions failed, the agents also attempted a Log4Shell injection against a different service, a server-side request forgery (SSRF) attack against a vulnerability in a co-located Qdrant instance, and several credential sprays against PostgreSQL, SSH, and other tools. Meanwhile, a separate operation running for more than 6 hours targeted a university GPU server with another credential-spray attack, compiling a list of 80 real user names found across the school’s public websites, academic papers and other documents. "Neither operation succeeded, yet together they show that the agents kept adapting for nearly a full day without human direction," Moses wrote. Then the AI agents found the zero-day path traversal vulnerability in MONAI Label, and this time they were able to gain access to the server. "The agents identified the application's framework, mapped its API endpoints, and found an upload endpoint with a filename parameter," Moses wrote. They tested that parameter for path traversal, and the parameter was vulnerable. In about 11 minutes, the agents went from mapping the application’s API to arbitrarily writing files on the server." Later, the agents abused the same flaw to execute a Python reverse shell running as root. In another session, after the agents discovered the zero-day, the human operator provided them with a proxy that tunneled into a second university network, and connected to a server running the same vulnerable code. Amazon's discovery follows an earlier report by Gambit Security's threat intelligence team that also documented a Chinese operator using Cairn to carry out at least 105 attacks, and managing to compromise, "to varying degrees," at least 27 companies. This campaign also occurred in September. In addition to Cairn, the attacker used two other open source AI harnesses to steal credit card records and other sensitive data from a Fortune 500 hospitality company, a major US airline, a large private US industrial supplies distributor, and a US online fashion retailer, and other companies. "Together, these cases show that this autonomous AI agent framework is being adopted in both espionage and criminal operations," Moses wrote. ®
DEN HAAG (ANP) - Jason Bhugwandass is vrijdag op 28-jarige leeftijd overleden. Zijn naasten hebben dat aan het ANP laten weten. Hij zette zich in voor mensen die, net als hij, slachtoffer waren geworden in de gesloten jeugdzorg. Dankzij de strijd van Bhugwandass zijn de gesloten afdelingen opgeheven en probeert de overheid het stelsel te hervormen.
Bhugwandass had psychische en lichamelijke klachten, die hij deels overhield aan zijn eigen periode in de jeugdzorg toen hij 16 was. Zijn rapporten over de misstanden in de jeugdzorg leidden in 2024 tot de sluiting van de strengste afdelingen binnen de gesloten jeugdzorg. Op 29 augustus van dit jaar bood minister Mirjam Sterk (Langdurige Zorg, CDA) namens de overheid excuses aan.

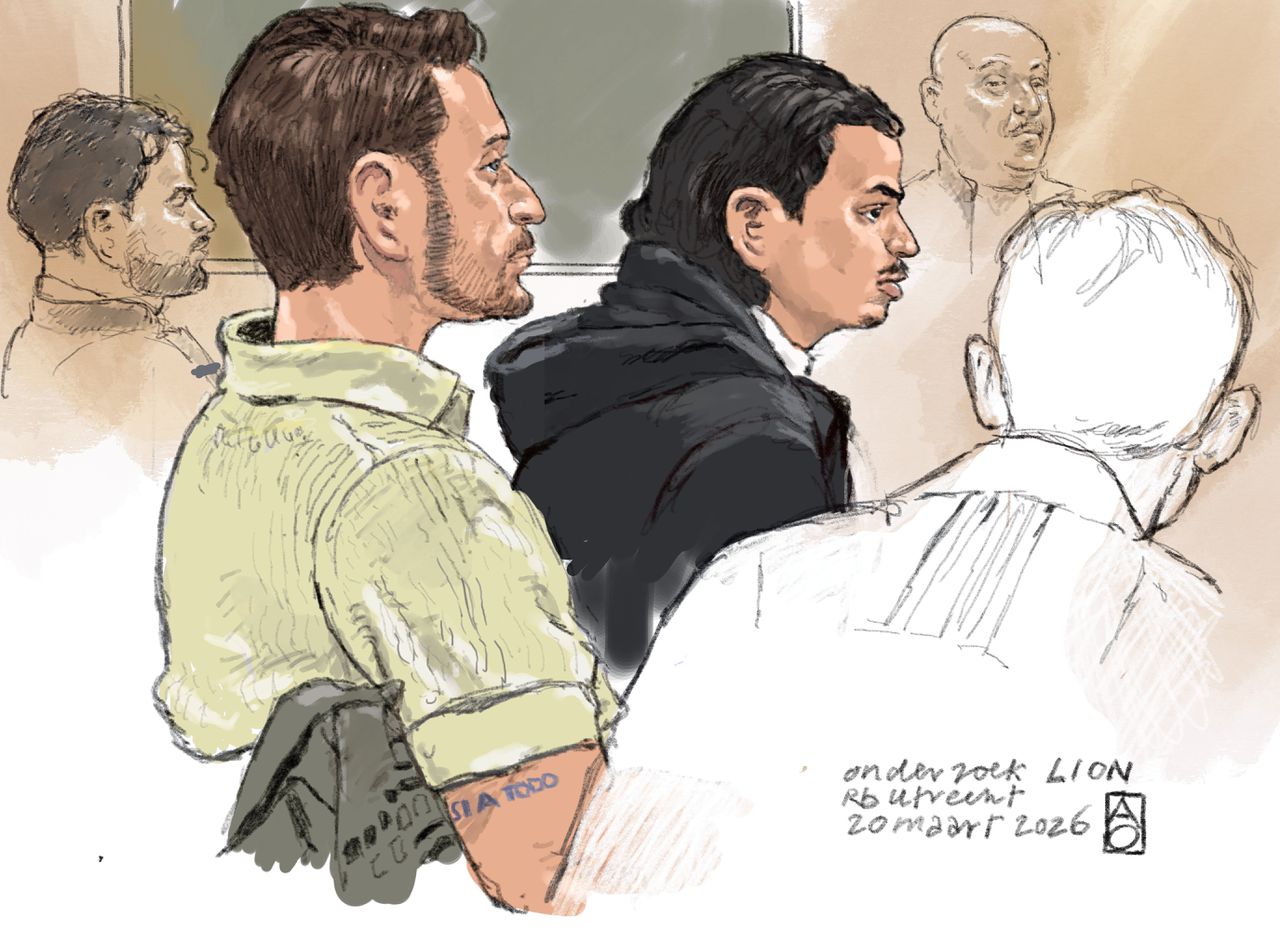
Bij Utrecht Centraal dronken twee schoonmakers uit bierflesjes die drugs bleken te bevatten. Een van de slachtoffers overleed, wat justitie de veronderstelde drugssmokkelaar zwaar aanrekent.
„En als laatste wil ik mezelf bedanken, natuurlijk. Ik wil mezelf bedanken omdat ik zo hard werk, omdat ik nooit stop, en omdat ik altijd in mezelf geloof.


DJ David Vunk draaide er meerdere malen. Bezoeker van het eerste uur Bobby Jacques keek er vroeger het hele jaar naar uit. En nachtburgemeester Thys Boer stond als tiener verbijsterd langs de route. Nu de Dance Parade na achttien jaar terugkeert in Rotterdam komen herinneringen boven. "Alle Rotterdammers gefeliciteerd. We zijn terug!"
